
spring-webmvc5
 jaloon/spring-webmvc5
Fork spring-webmvc 5.3.39 to fix CVE-2024-38816, CVE-2024-38819
code-analysisdevsecopssupply-chain-security+2
jaloon/spring-webmvc5Fork spring-webmvc 5.3.39 to fix CVE-2024-38816, CVE-2024-38819
 arnaudluti/ps-cve-2021-44228
Static detection of vulnerable log4j librairies on Windows servers, members of an AD domain.
 gina-alaska/bash-cve-2014-7169-cookbook
Chef cookbook to detect and patch the Shellshock (CVE-2014-7169) bash vulnerability across servers using automated configuration management.
 meganekos/secure-by-default-rce-demo
Secure-by-default demo lab showing how container hardening (distroless images, non-root, read-only filesystem, runtime-injected secrets) can…
 jblaine/cookbook-bash-cve-2014-6271
Chef cookbook that will fail if bash vulnerability found per CVE-2014-6271
 murataydemir/aws-sam-cli-vulnerabilities
Issue with AWS SAM CLI (CVE-2025-3047, CVE-2025-3048)
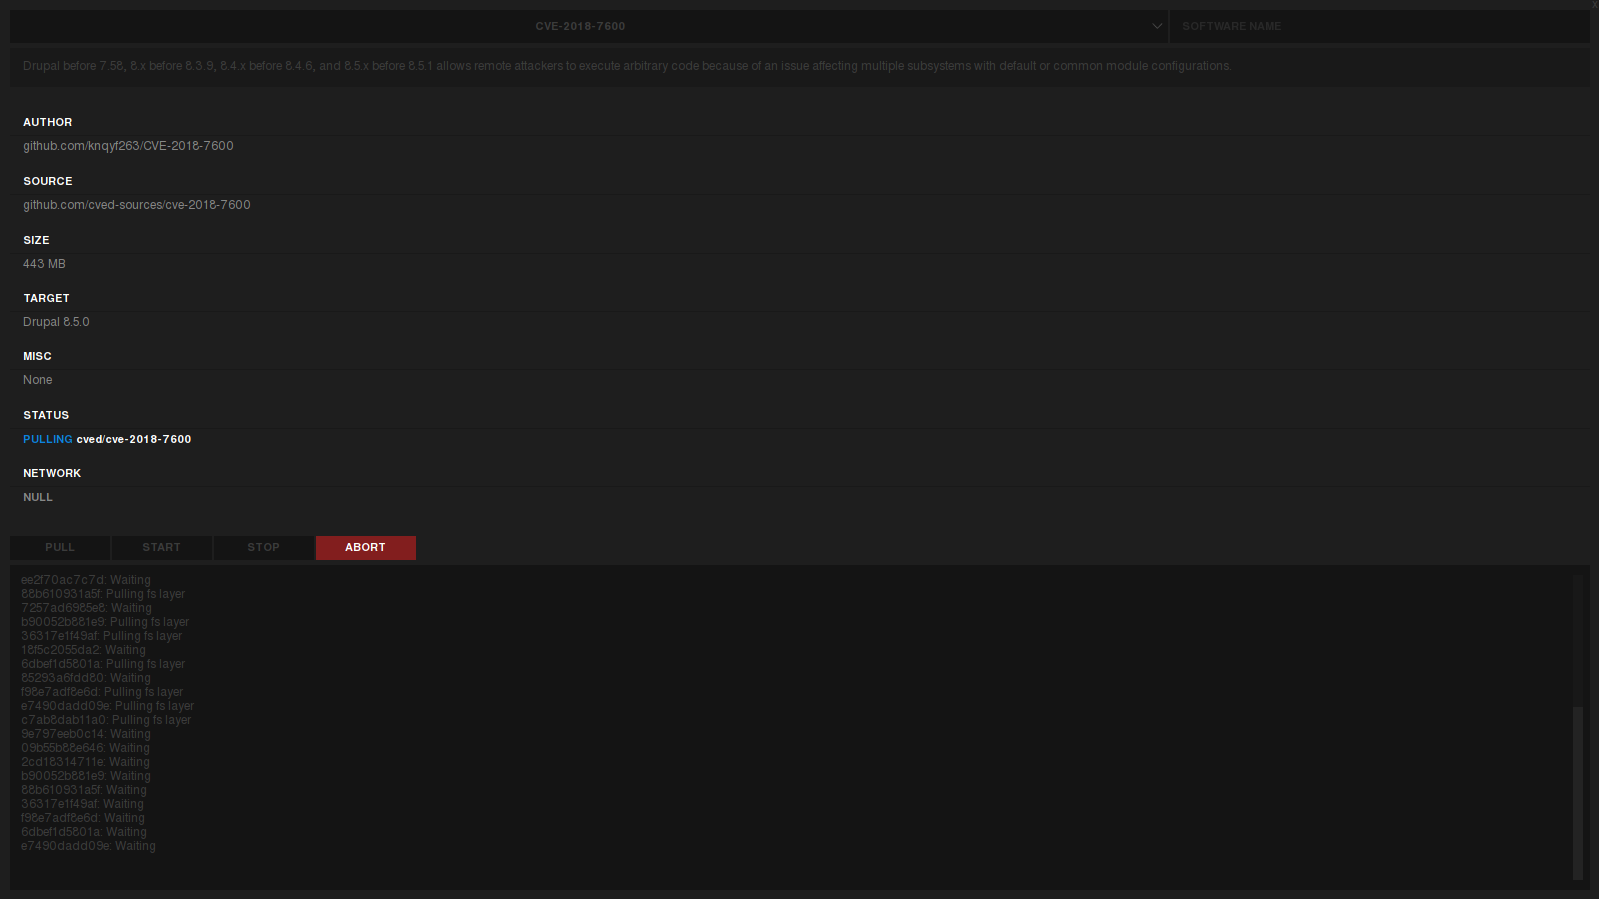 git-rep-src/cved
A tool to manage vulnerable docker containers
 mebibite/log4jhound
Created after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…
 daniel-odrinski/cve-2024-6387-mitigation-ansible-playbook
An Ansible Playbook to mitigate the risk of RCE (CVE-2024-6387) until platforms update OpenSSH to a non-vulnerable version.
 alebedev87/gatekeeper-cve-2020-8554
OPA Gatekeeper constraint policy that detects and prevents Kubernetes clusters from being vulnerable to CVE-2020-8554, enforcing secure configuration.
 ziadsaleemi/polkit_cve-2021-4034
Ansible role to patch RHSB-2022-001 Polkit Privilege Escalation - (CVE-2021-4034)
 almogopp/openssh-cve-2024-6387-fix
A Bash script to mitigate the CVE-2024-6387 vulnerability in OpenSSH by providing an option to upgrade to a secure version or apply a temporary…
 didoatanasov/cve-2021-44228
Ansible playbook that applies a global JVM environment variable to mitigate the Log4j CVE-2021-44228 remote code execution vulnerability across all…
 axisops/cve-2021-44228
log4j mitigation work
 teedeedubya/bash-fix-exploit
Ansible role to check the CVE-2014-6271 vulnerability
 markuman/aws-log4j-mitigations
CVE-2021-44228 log4j mitigation using aws wafv2 with ansible
 atilacastro/update-apt-package
Playbook update APT package because CVE-2019-3462
 dgourillon/mitigate-cve-2024-6387
Shell script to detect and mitigate CVE-2024-6387 vulnerability by auditing system configurations and applying recommended fixes.