
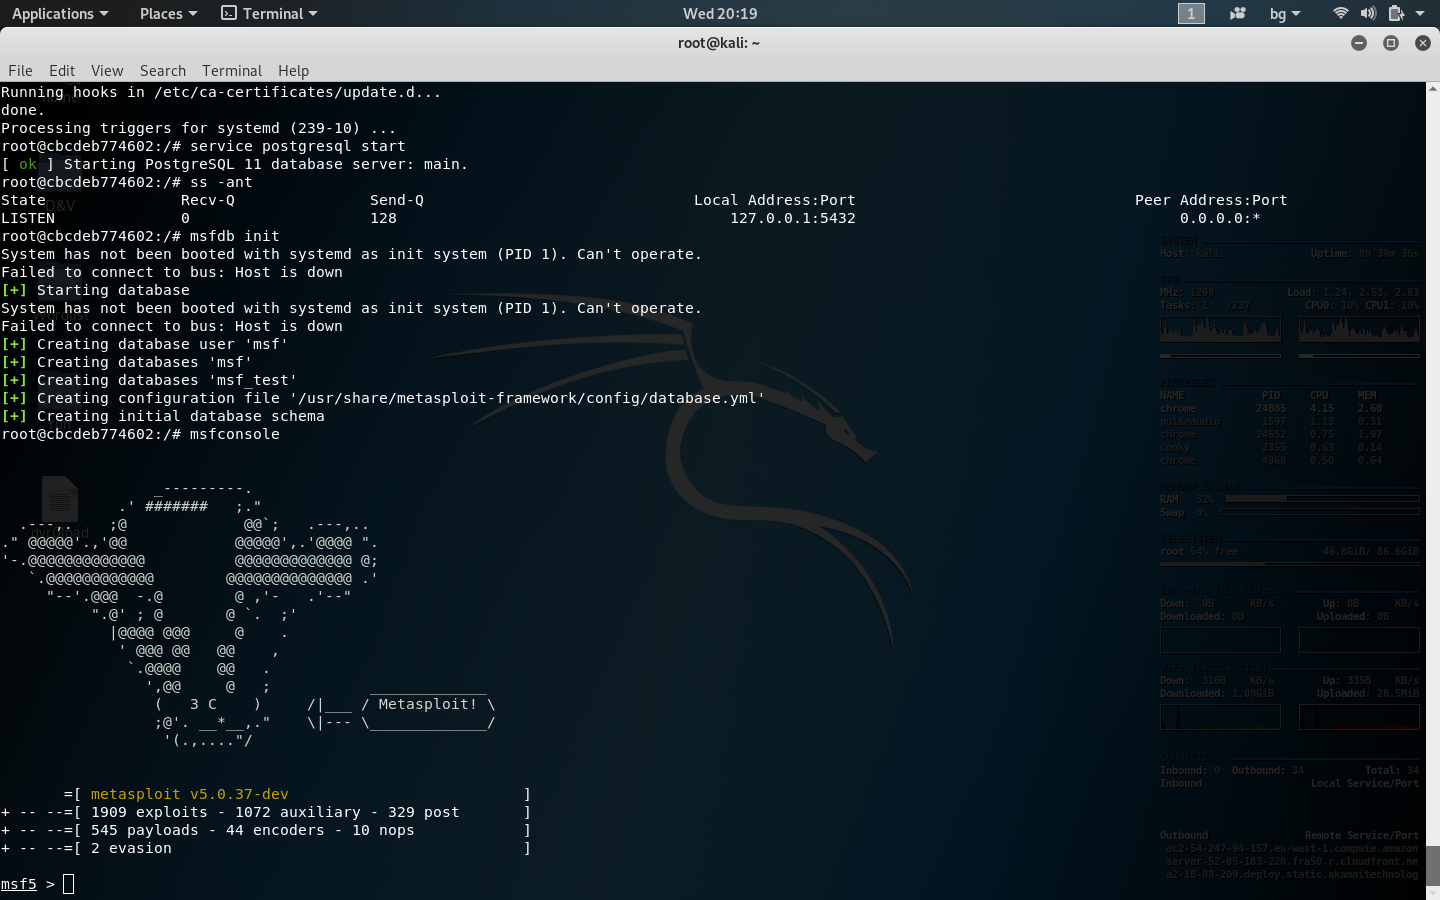
kali-linux-docker
 nu11secur1ty/kali-linux-docker
kali-linux-docker
cloud-securitycontainer-securitydevsecops+8
nu11secur1ty/kali-linux-dockerkali-linux-docker
 danielxavierjob/-cve-2025-55182
Browser-based scanner that audits GitHub repositories for known vulnerabilities in React and Next.js dependencies, checking all branches and…
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
 perplexityai/bumblebee
Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
 dnscontrol/dnscontrol
Infrastructure as code for DNS!
 anshumanbh/git-all-secrets
A tool to capture all the git secrets by leveraging multiple open source git searching tools
 mukul975/cve-mcp-server
Production-grade MCP server giving Claude 27 security intelligence tools across 21 APIs — CVE lookup, EPSS scoring, CISA KEV, MITRE ATT&CK, Shodan,…
 raskrebs/sonar
CLI tool for inspecting and managing services listening on localhost ports
 david-a-wheeler/flawfinder
a static analysis tool for finding vulnerabilities in C/C++ source code
 cycodelabs/raven
Scans GitHub Actions CI/CD workflows for security vulnerabilities, indexes findings into a Neo4j graph database, and provides a query library for…
 jsdelivr/globalping-probe
The globalping probe code that runs on your hardware and connects to the global community network of probes
 dionach/reposcanner
Python script to scan Git repos for interesting strings
 xddxdd/nixos-config
Lan Tian's NixOS Configuration
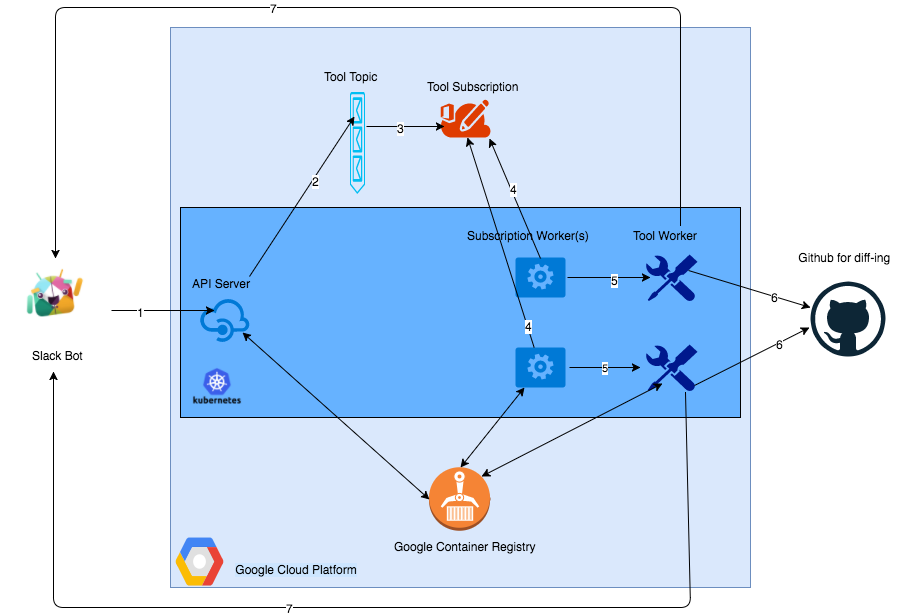 anshumanbh/kubebot
A security testing Slackbot built with a Kubernetes backend on the Google Cloud Platform
 papermtn/gitlab-watchman
Finding exposed secrets and personal data in GitLab
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)