protocol-fuzzer-ce
This is the community edition of GitLab's protocol fuzzing framework. This framework is based on Peach Fuzzer Professional with some features removed.

This is the community edition of GitLab's protocol fuzzing framework. This framework is based on Peach Fuzzer Professional with some features removed.

Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…

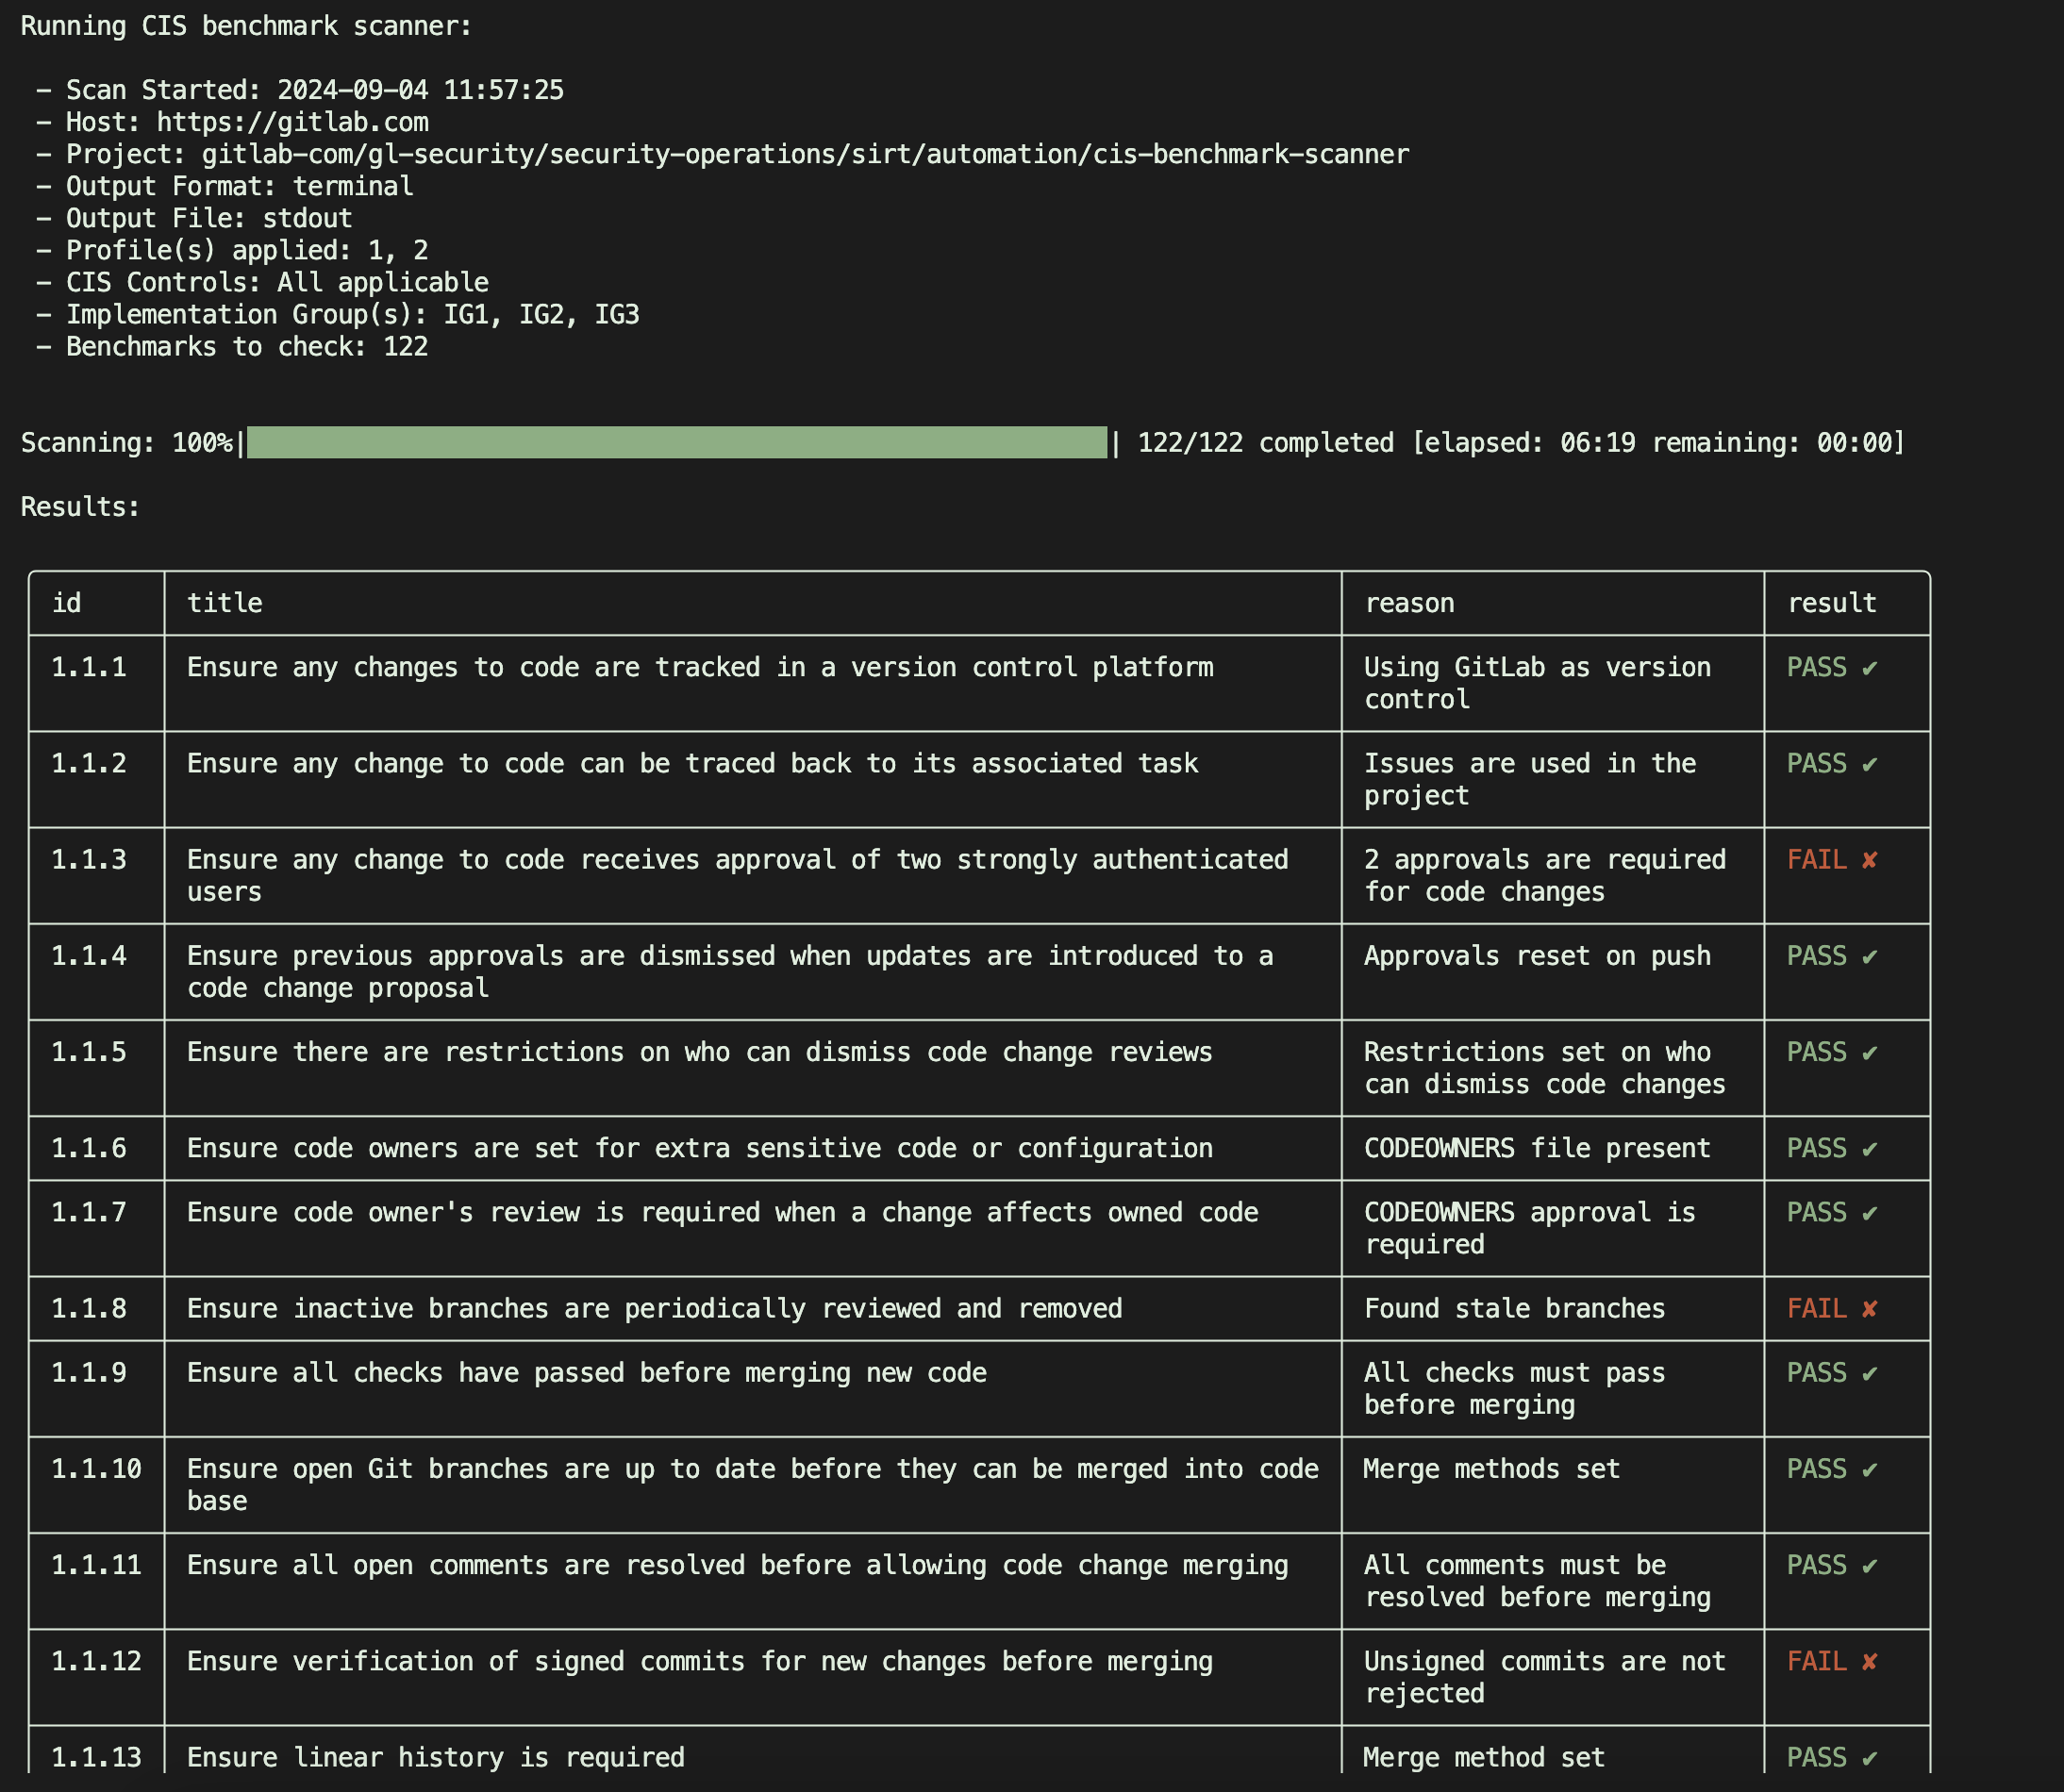
Audits GitLab projects against the CIS GitLab Benchmark via read-only API checks, generating JSON reports on compliance and hardening recommendations.

Checklist and tools for increasing security of Apache Airflow

Async API security scanner in Rust for CORS, CSP, GraphQL, JWT, OpenAPI, and active API posture checks.

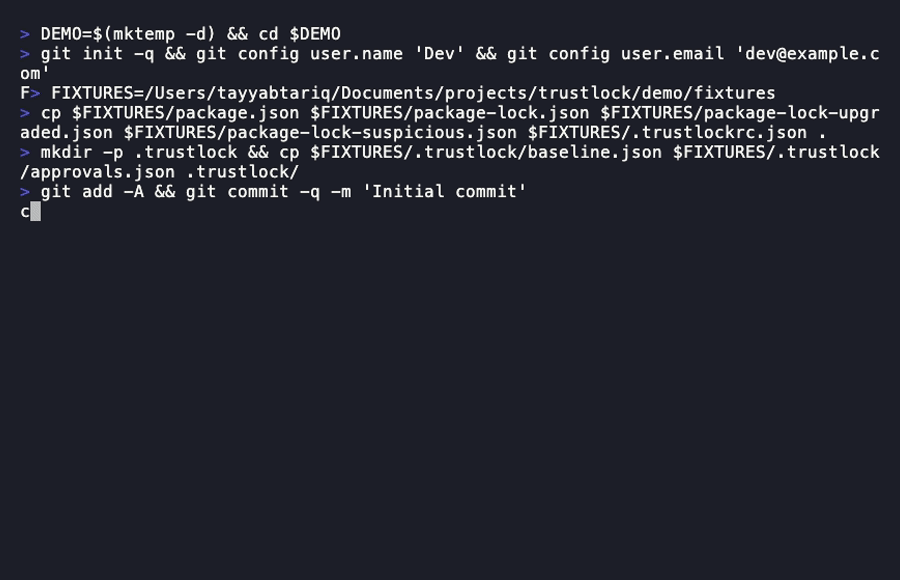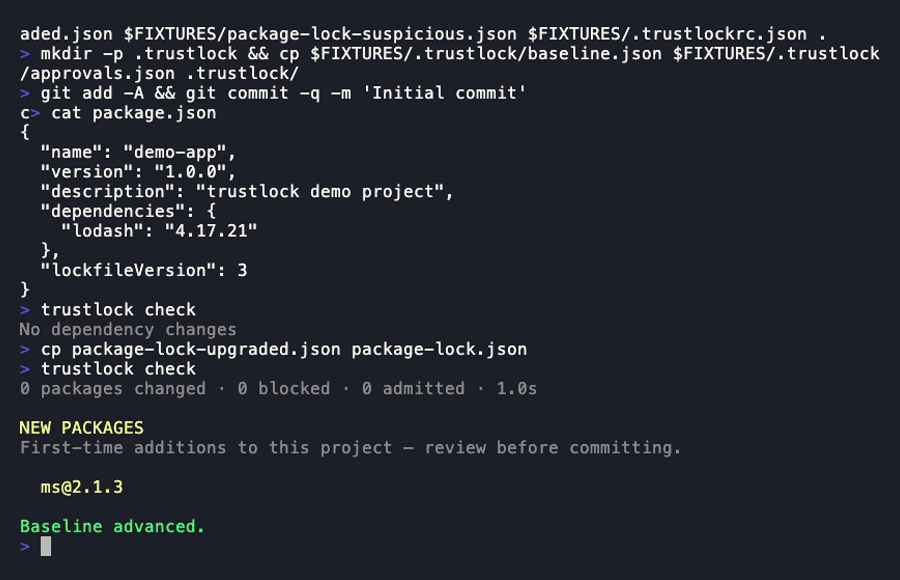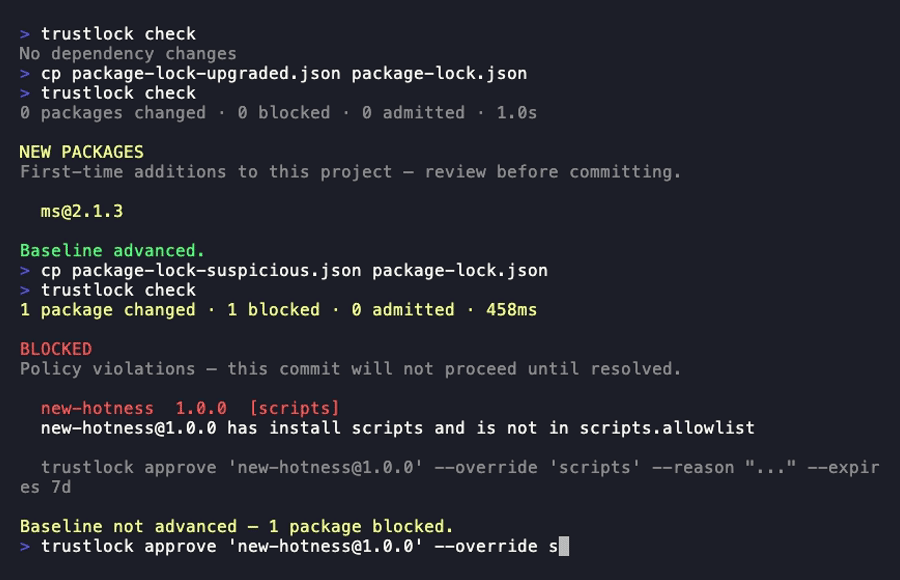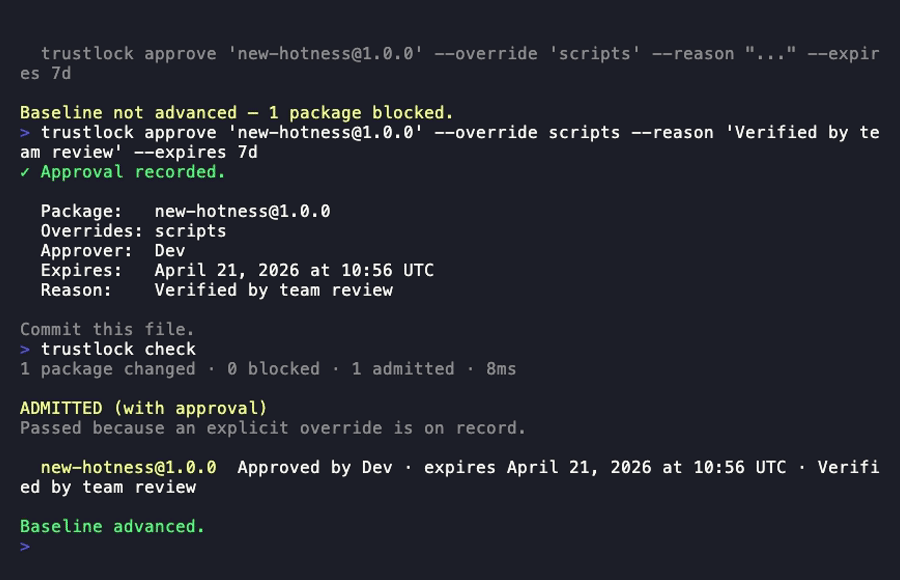
A Git-native dependency admission controller. Evaluates trust signals on every dependency change and blocks commits or builds when packages fail your…

provides a Firewall Manager API designed to centralize and streamline the management of firewall configurations

Security-research lab reproducing CVE-2021-4281 (GHSA-3796-3f93-cfvx): shell command injection via PR head-branch name in…

Security-research lab: reproduction of CVE-2026-41249 (GHSA-q58j-g3f4-h26h) — pull_request_target pwn request in .github/workflows/static.yml,…

Security-research lab: CVE-2026-47172 (workflow_run pwn request in deploy.yaml) — flattened snapshot of duck-organization/questbot at 1903b2f

Security-research lab: controlled reproduction of CVE-2024-4254 (GHSA-fc78-c36r-cc59) — deploy-website.yml fork checkout/code execution in…

Security-research lab: reproduction of CVE-2026-29075 (GHSA-3j55-5q6x-2h48) in mesa/mesa benchmarks.yml pull_request_target workflow — single-commit…

Authorized security-research reproduction lab for CVE-2025-54415 (GHSA-g5hx-xv45-9whg): astronomer/dag-factory snapshot at 464c75a —…

Authorized lab reproduction of CVE-2025-47928 (spotipy-dev/spotipy pull_request_target secrets exfiltration) — snapshot at vulnerable commit 4f5759d

Authorized security-research lab reproducing CVE-2026-45131 (pwn request in .github/workflows/pull-request.yaml) — snapshot of…

Apache Struts version analyzer (Ansible) based on CVE-2017-5638

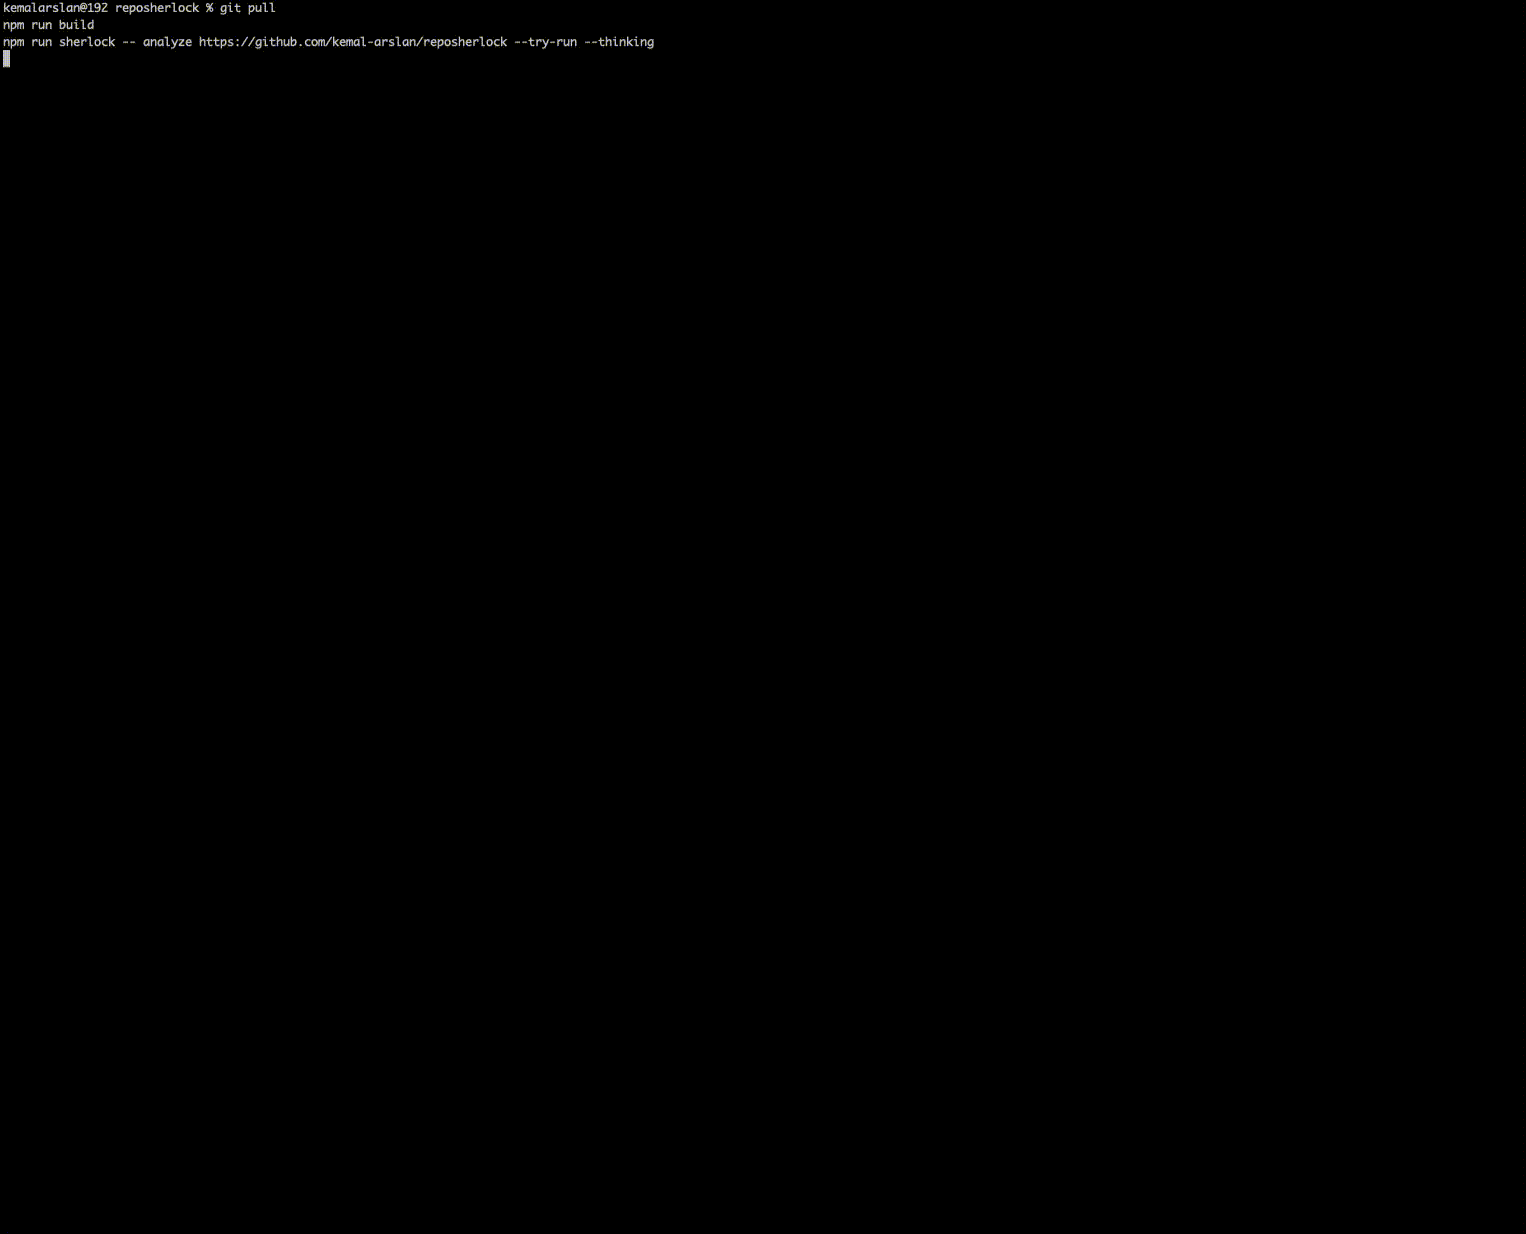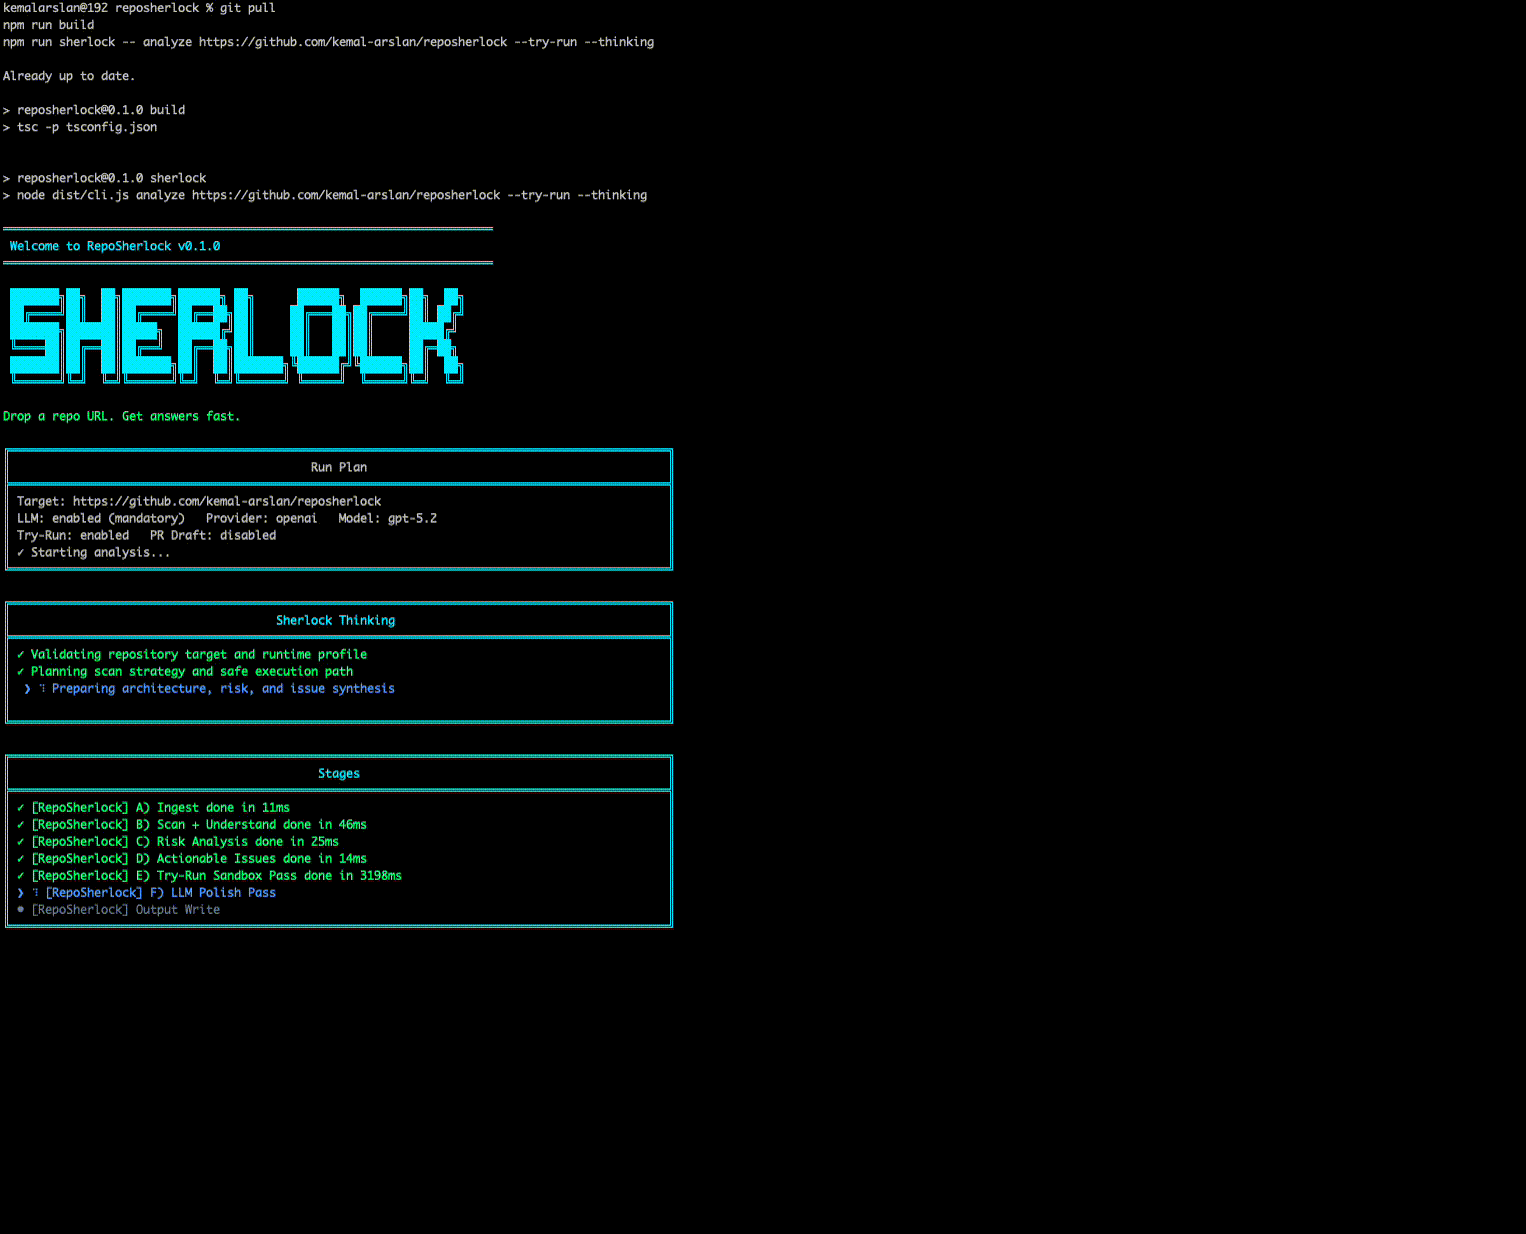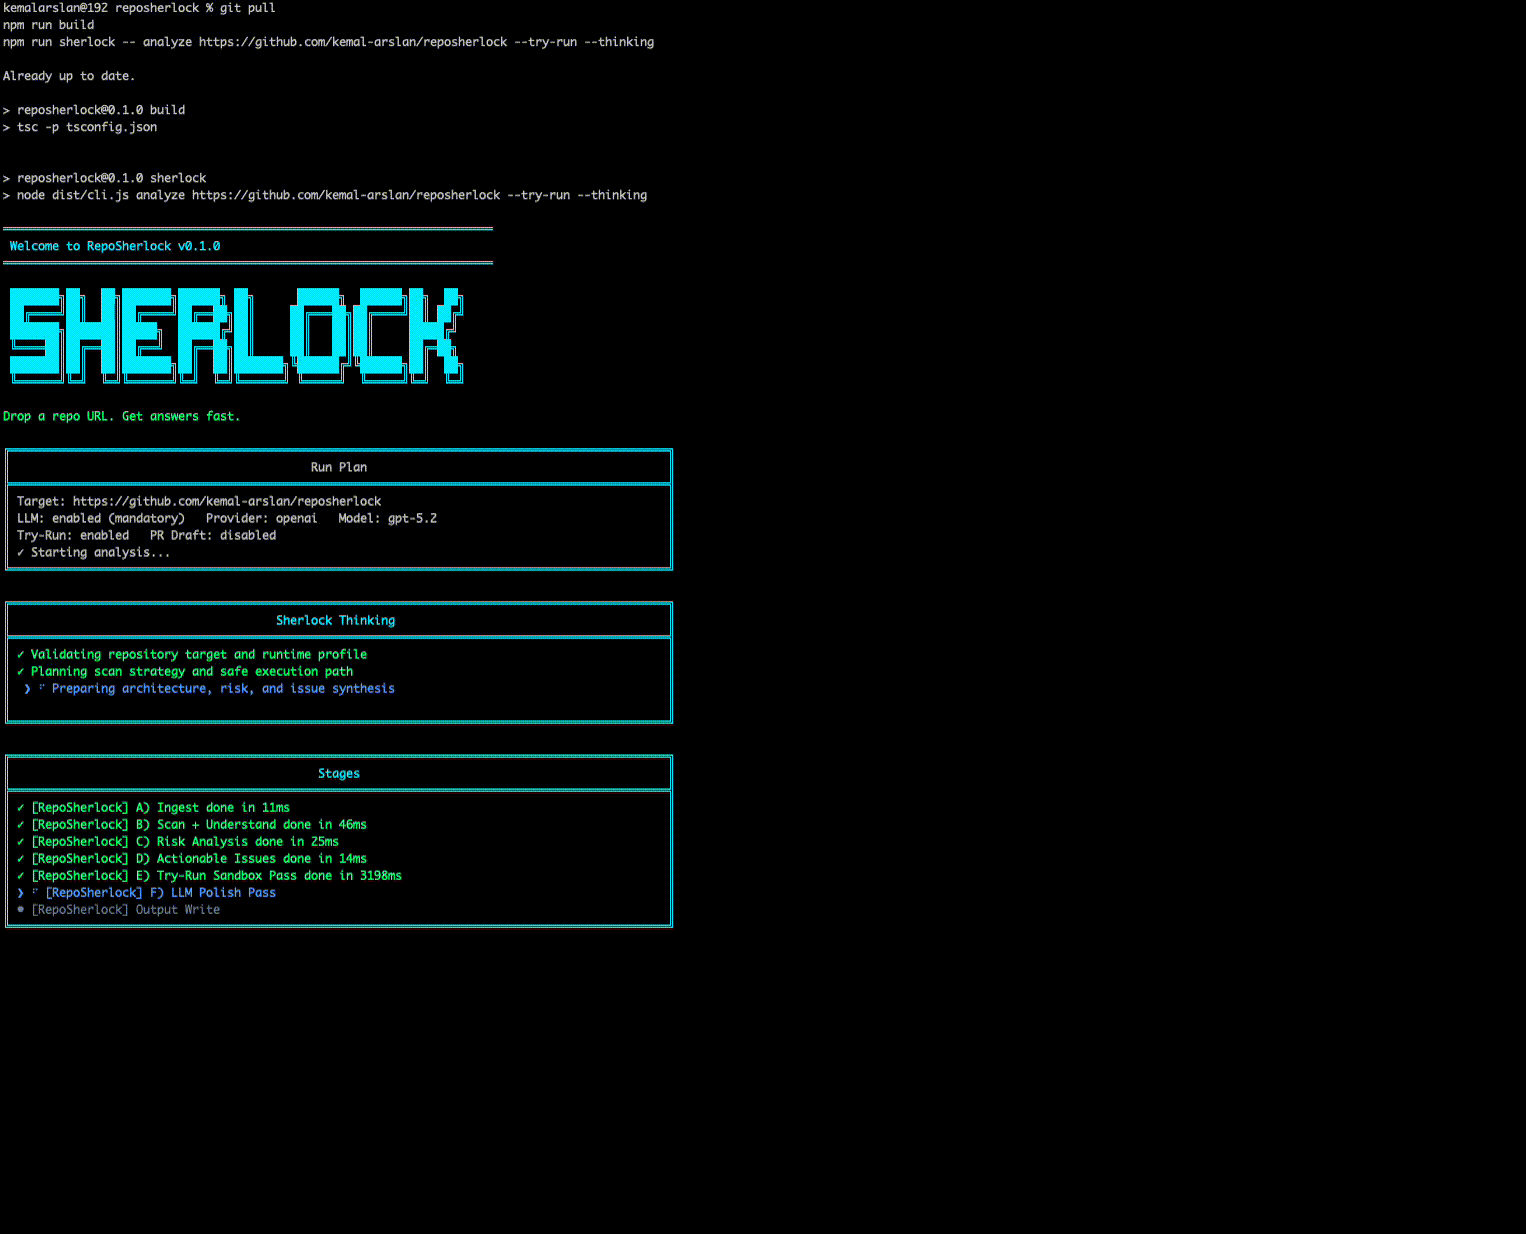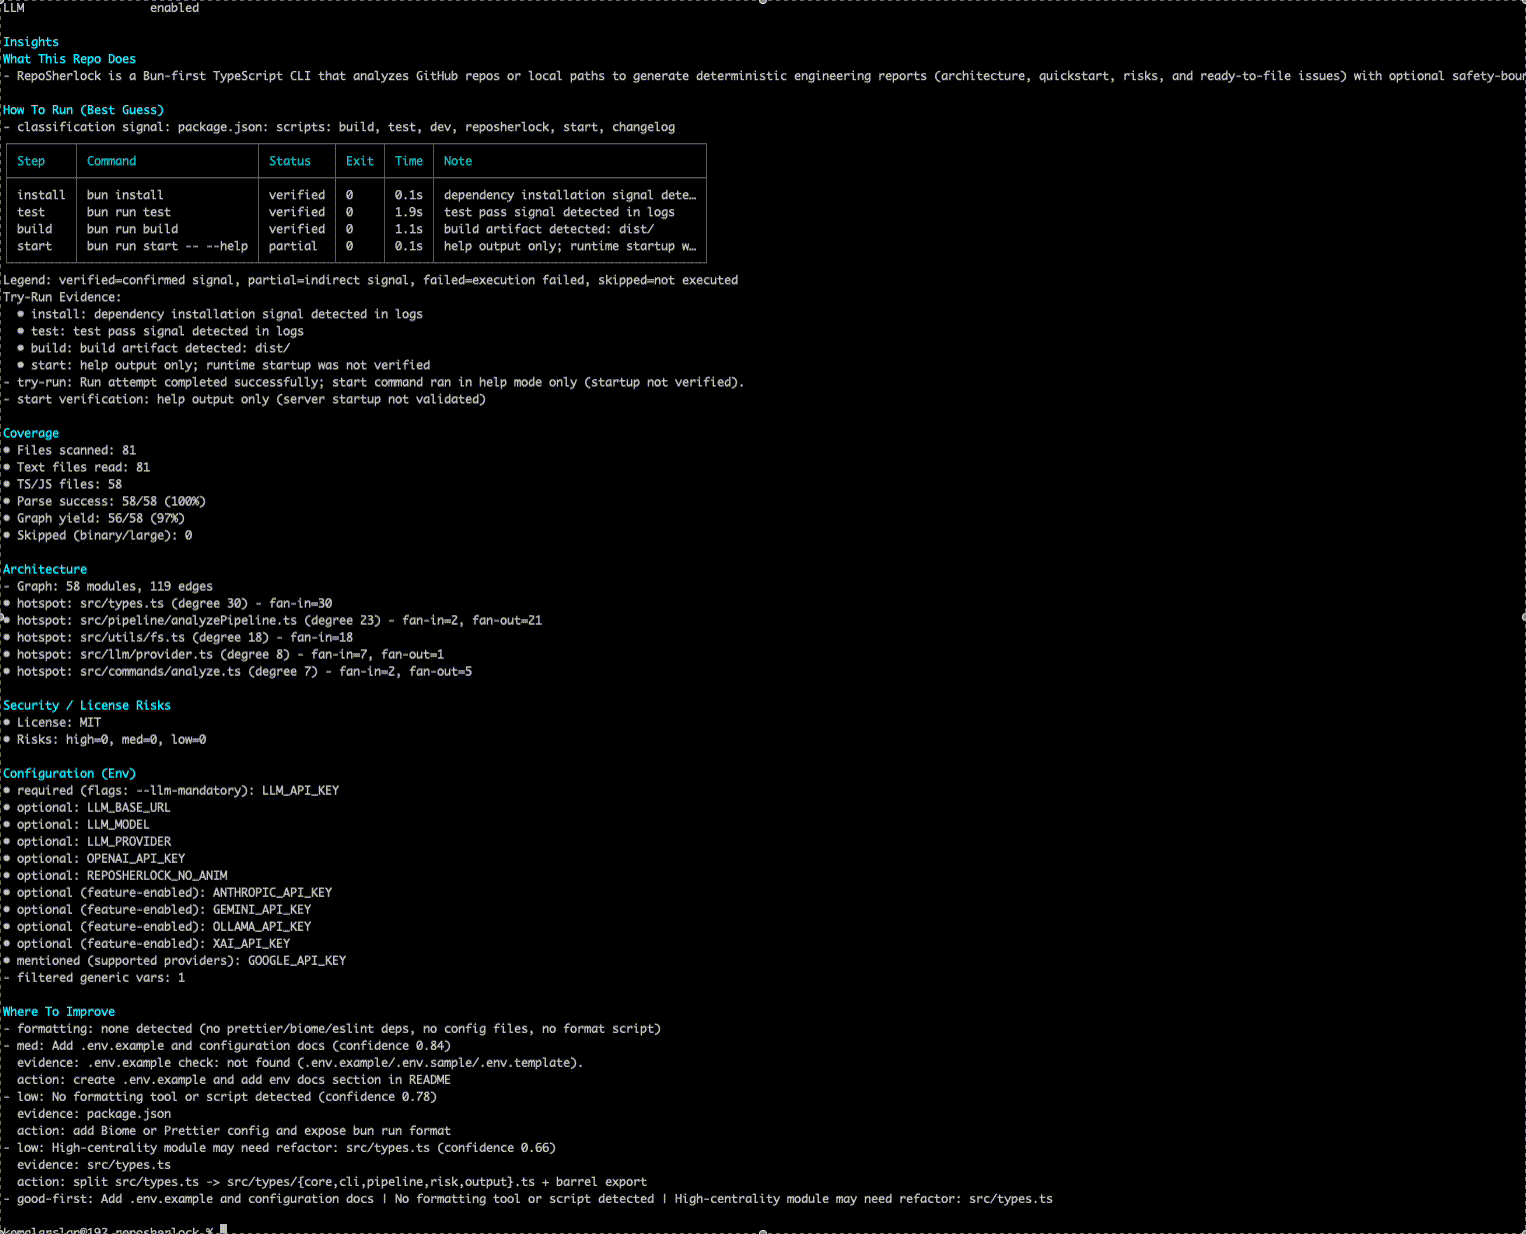
Analyze any GitHub repo (URL or local path) → architecture map, verified run commands, risks, and actionable issues - in minutes.

OPA Gatekeeper-based policy templates to mitigate CVE-2020-8554 by restricting Kubernetes Service external IPs to an allow list, preventing traffic…