

DakshSCRA
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
code-analysisdevsecopseducation+7
45
coffeeandsecurity/dakshscraFramework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
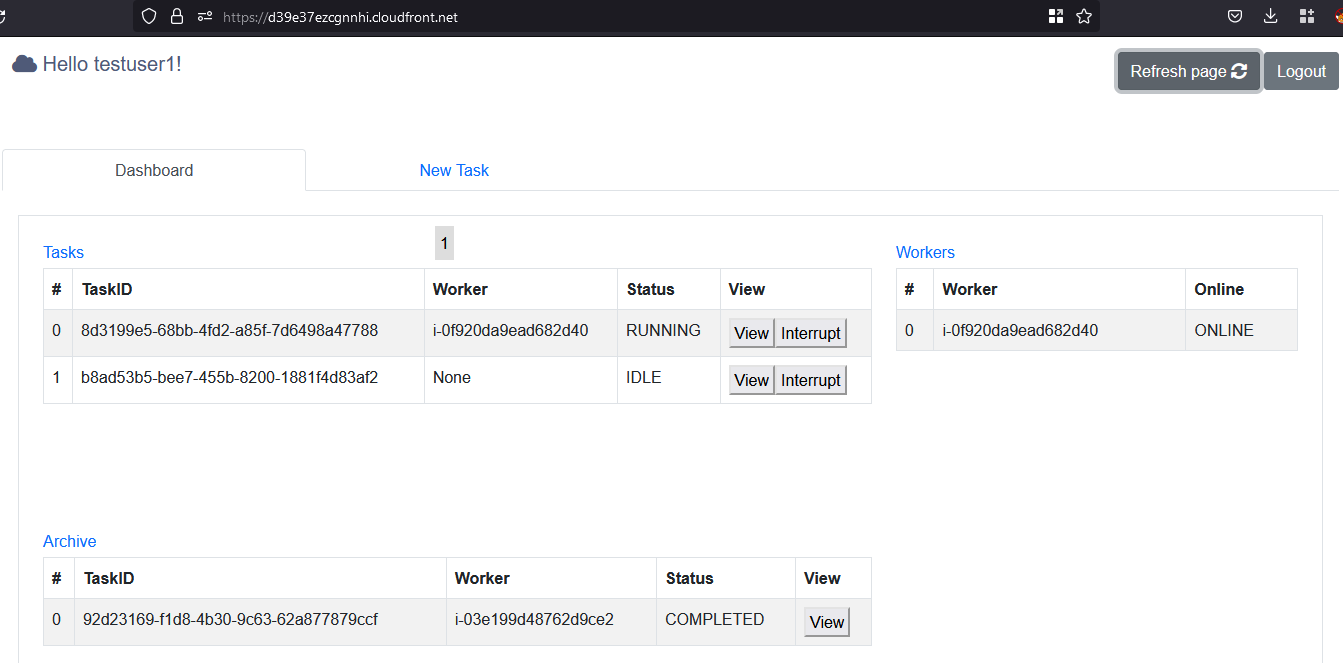 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
 teycir/apihunter
Async API security scanner in Rust for CORS, CSP, GraphQL, JWT, OpenAPI, and active API posture checks.
 projectdiscovery/naabu-action
A fast port scanner written in go with a focus on reliability and simplicity.
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker
 kamalsrini/sentinel-cve
CLI tool that explains CVEs in plain English and scans repos for impact. Powered by Claude.
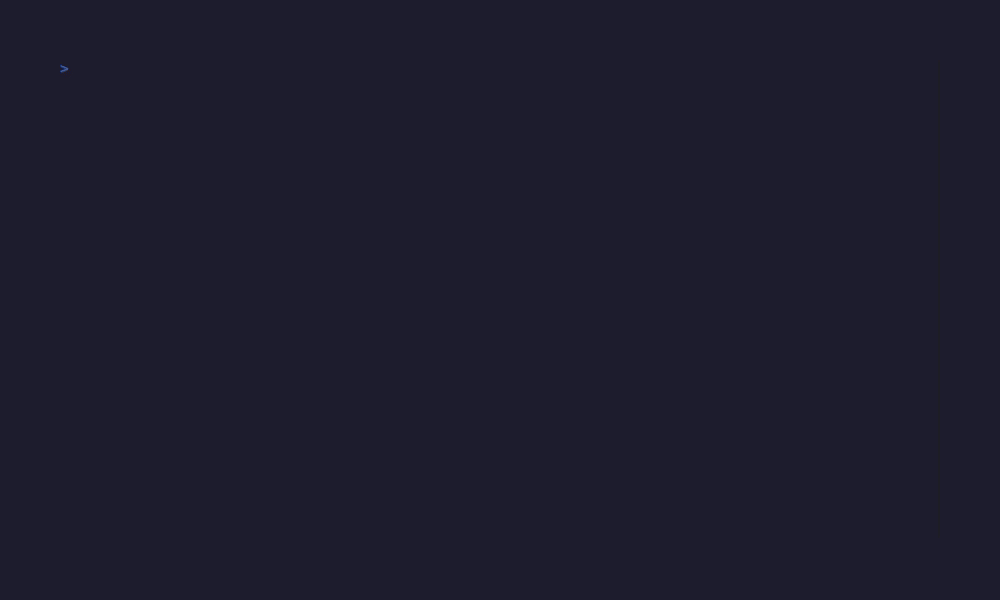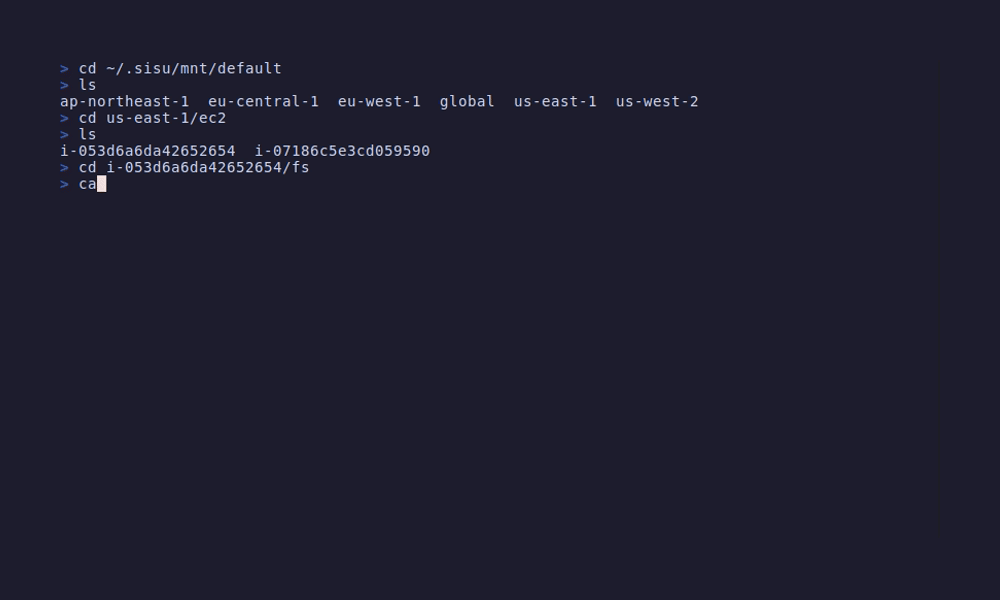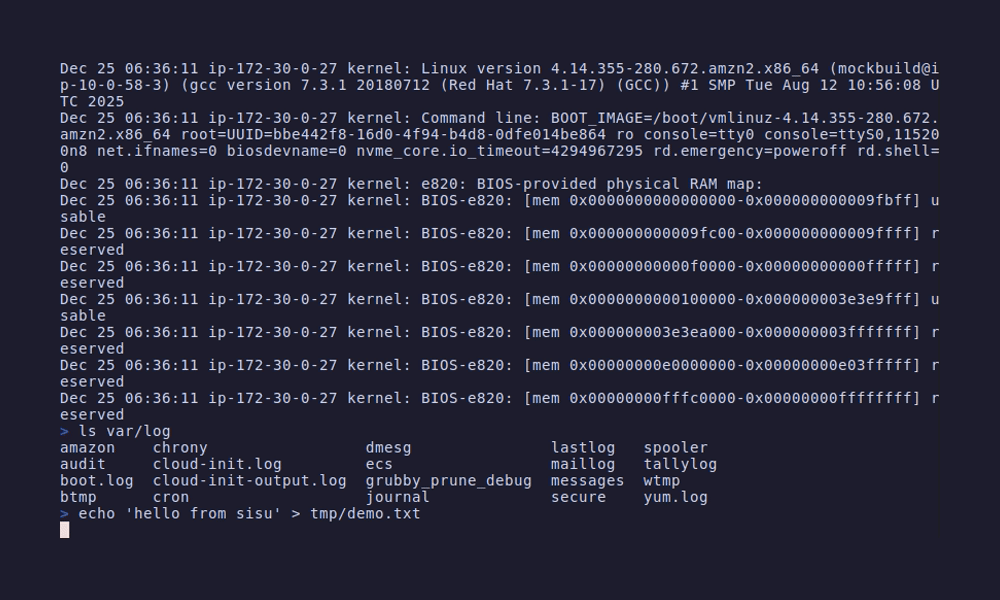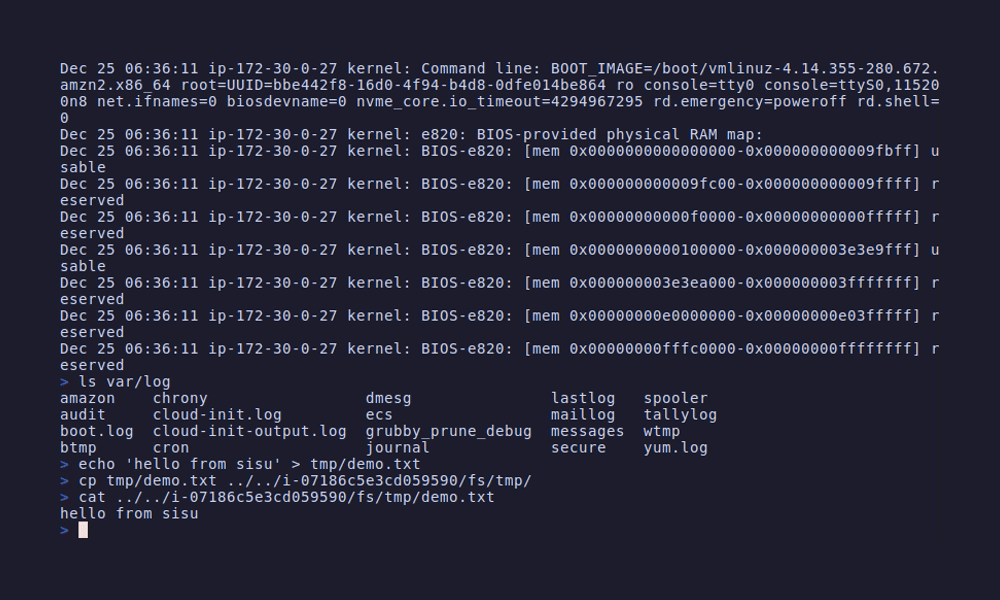 semonte/sisu
Mounts AWS resources as a local filesystem for infrastructure exploration, security auditing, and configuration analysis using standard Unix tools…
 projectdiscovery/httpx-action
HTTP Web Server probing
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 rapticore/ore-mal-pkg-inspector
Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
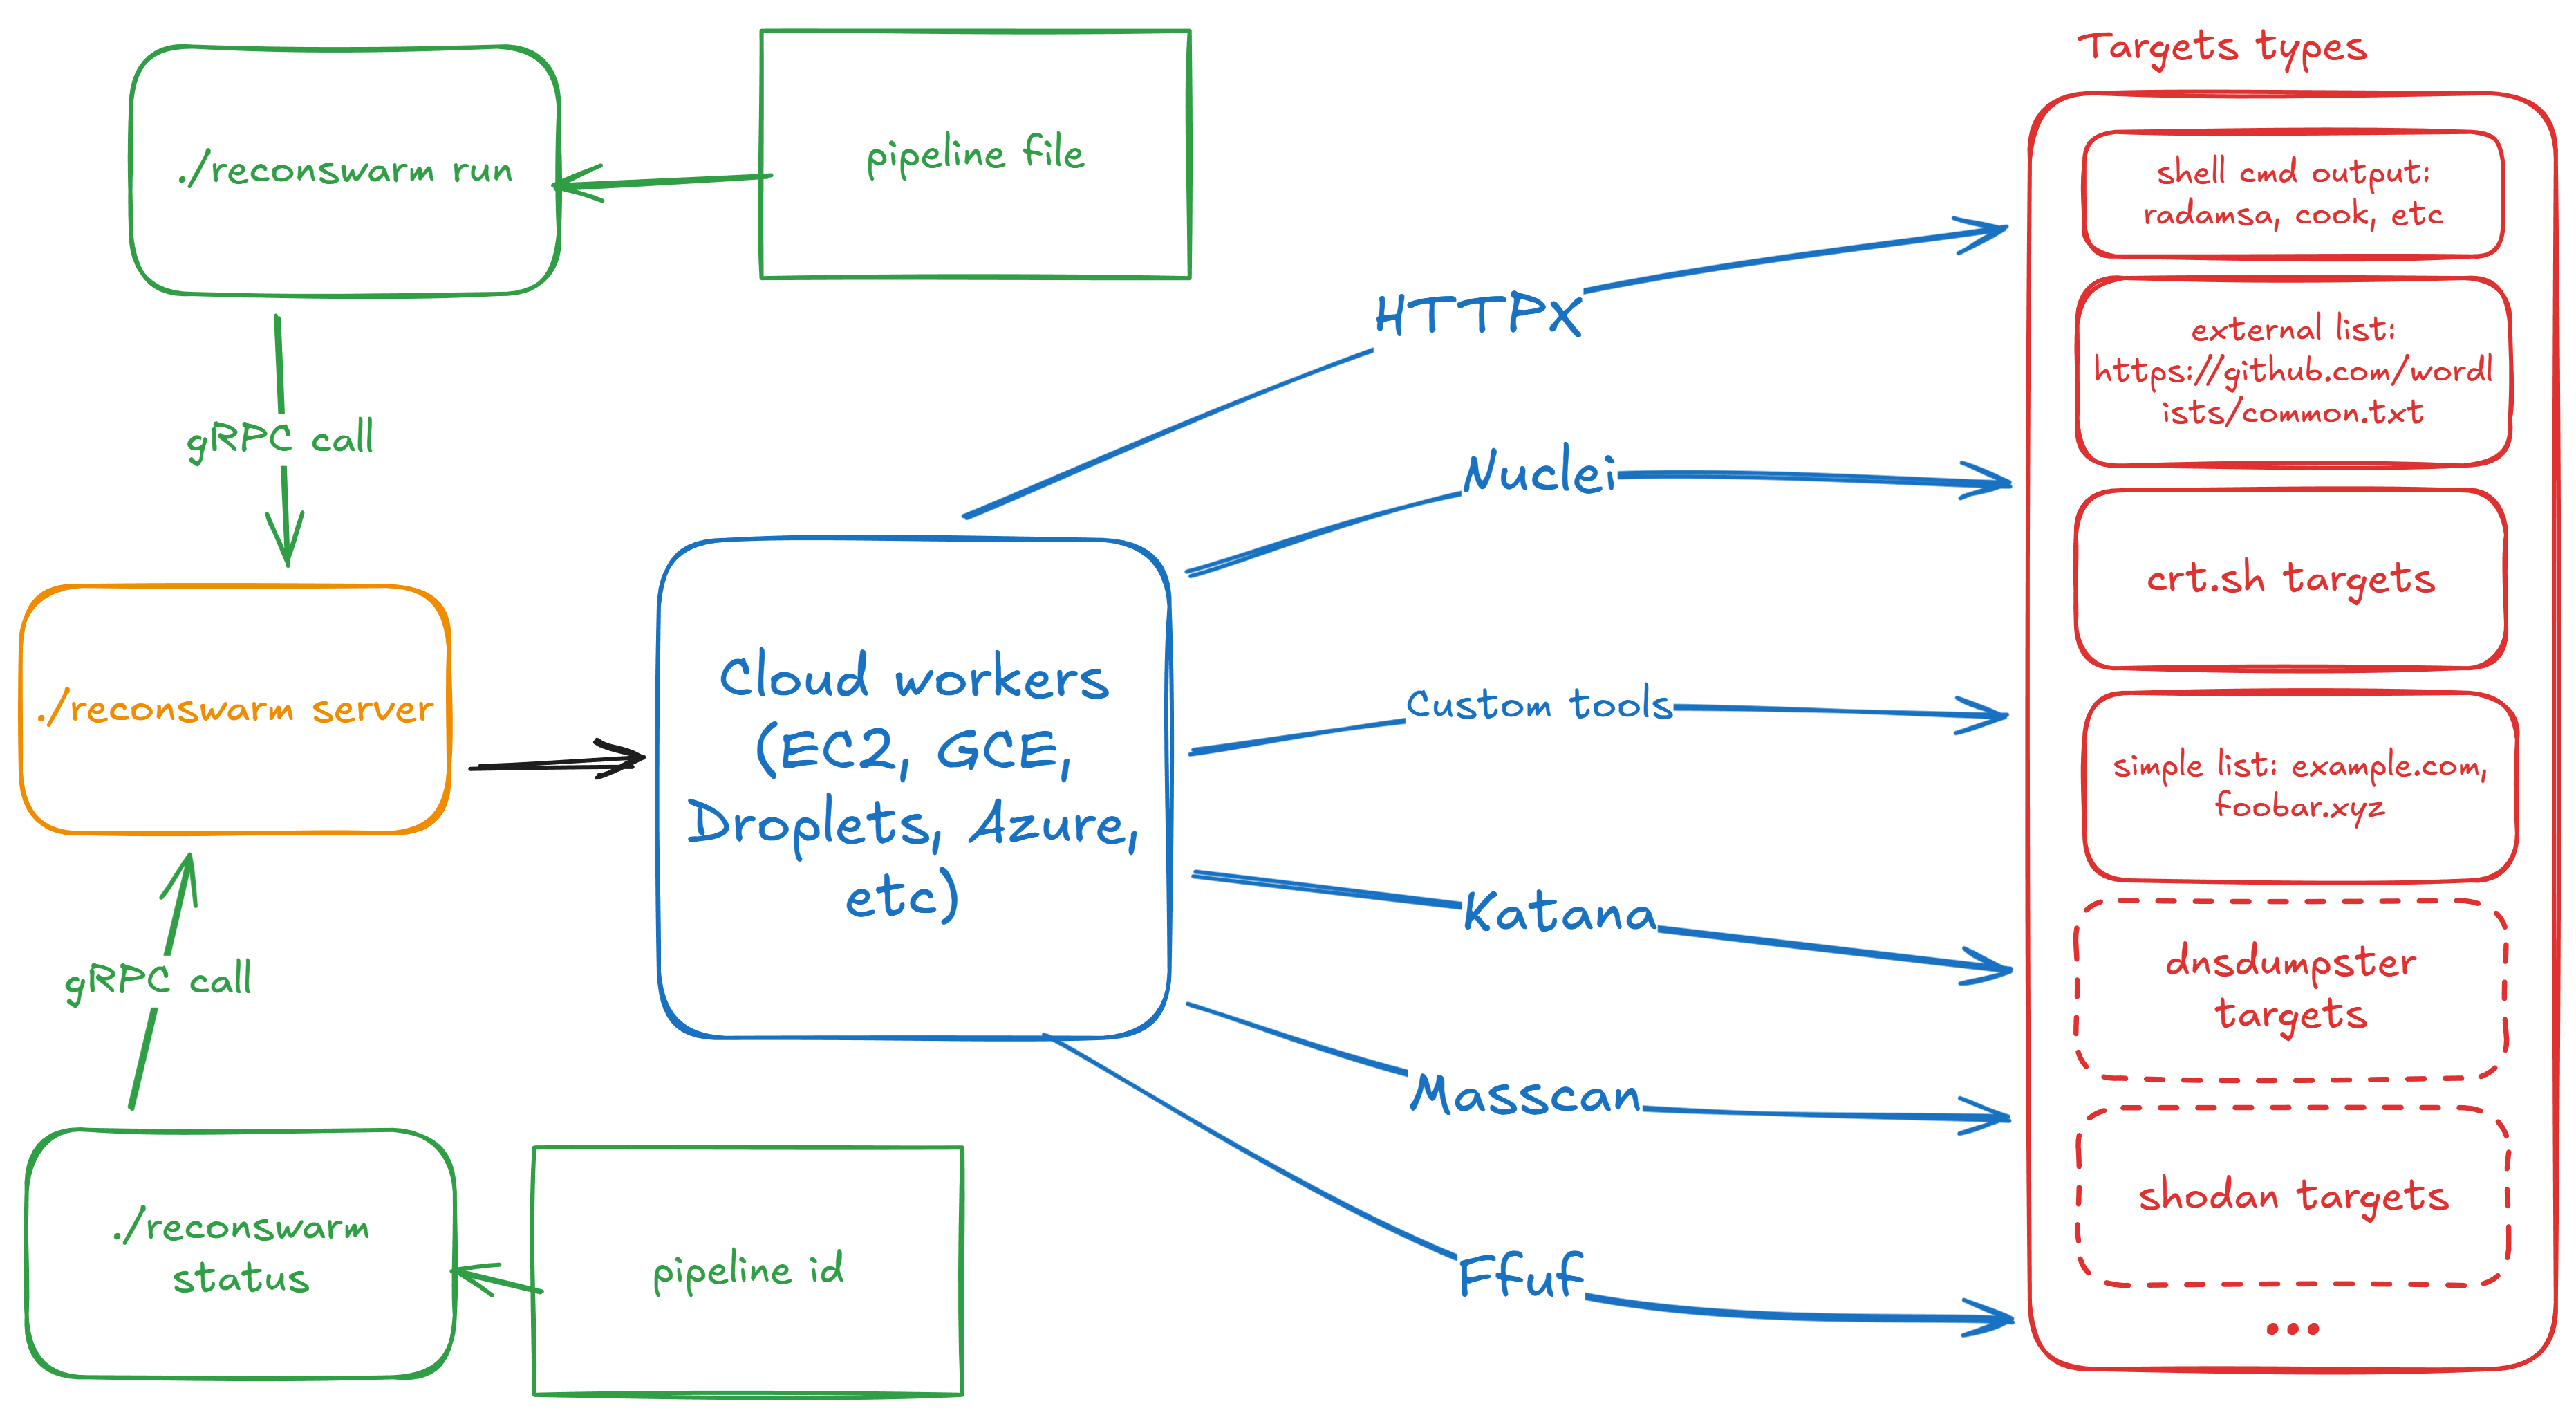 renatus-cartesius/reconswarm
Extend your recon with cloud power
 the-infra-company/kcatcher
Catch what's lurking in your Kafka clusters.
 adimahluf/rapidwebrecon
A high-performance automation tool designed to bridge the gap between technical web reconnaissance and executive reporting. Developed by **Adi…
 schroeder-sys/pantheon-souverainete
Infrastructure cloud modulaire, redondante et 100% souveraine pour s'affranchir des GAFAM. Guides techniques, architecture Zero-Trust et chiffrement…
 h4wkst3r/dop2mop
OpenGraph collector for BloodHound that maps attack paths from DevOps to MLOps infrastructure, collecting CI/CD pipeline, service principal, and ML…