
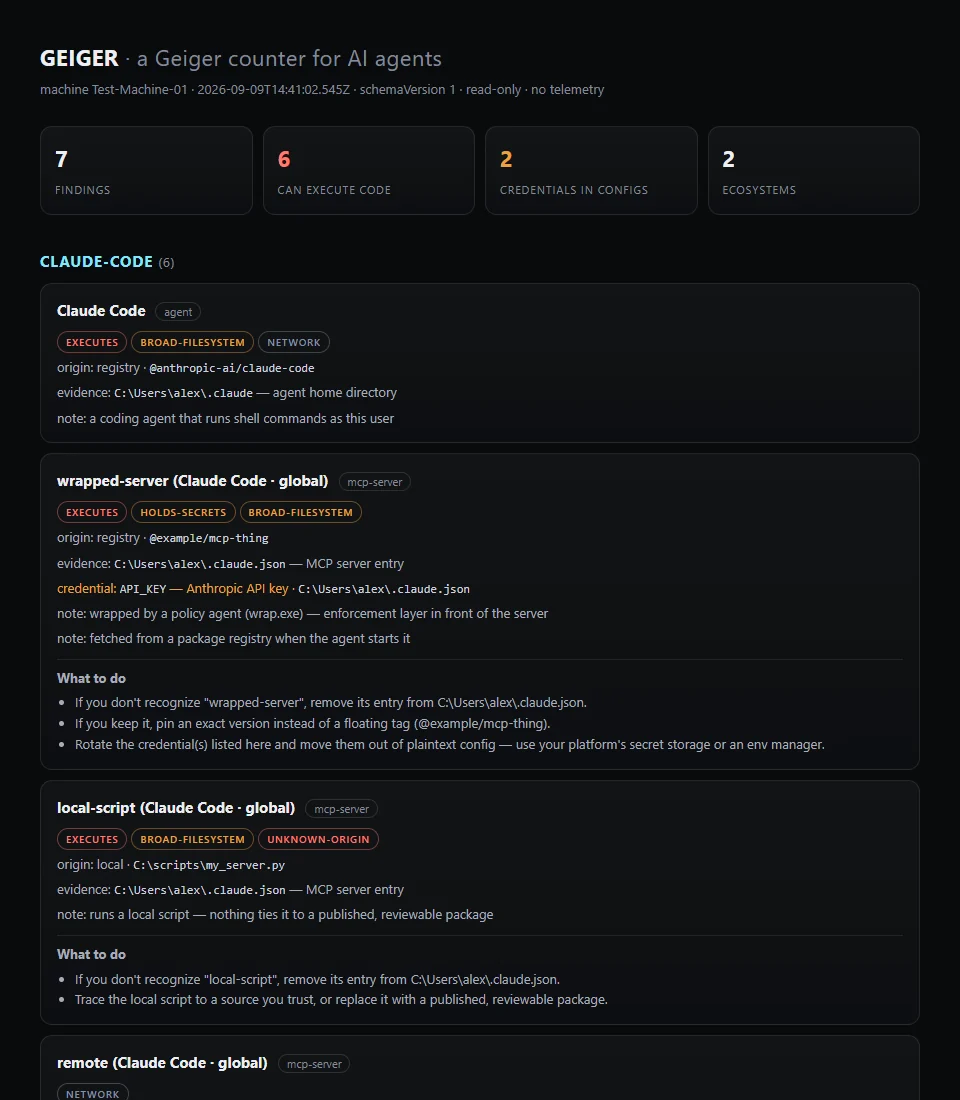
geiger
 atomburstofficial/geiger
Read-only CLI that inventories AI agents, MCP servers, plugins, and extensions on a machine, reporting their capabilities and exposure with…
ai-securitycloud-securityconfiguration-auditing+2
170
atomburstofficial/geigerRead-only CLI that inventories AI agents, MCP servers, plugins, and extensions on a machine, reporting their capabilities and exposure with…
 trailofbits/gosentry
Security-oriented Go toolchain, focused on state-of-the-art fuzzing capabilities.
 andreicscs/honeywire
Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…
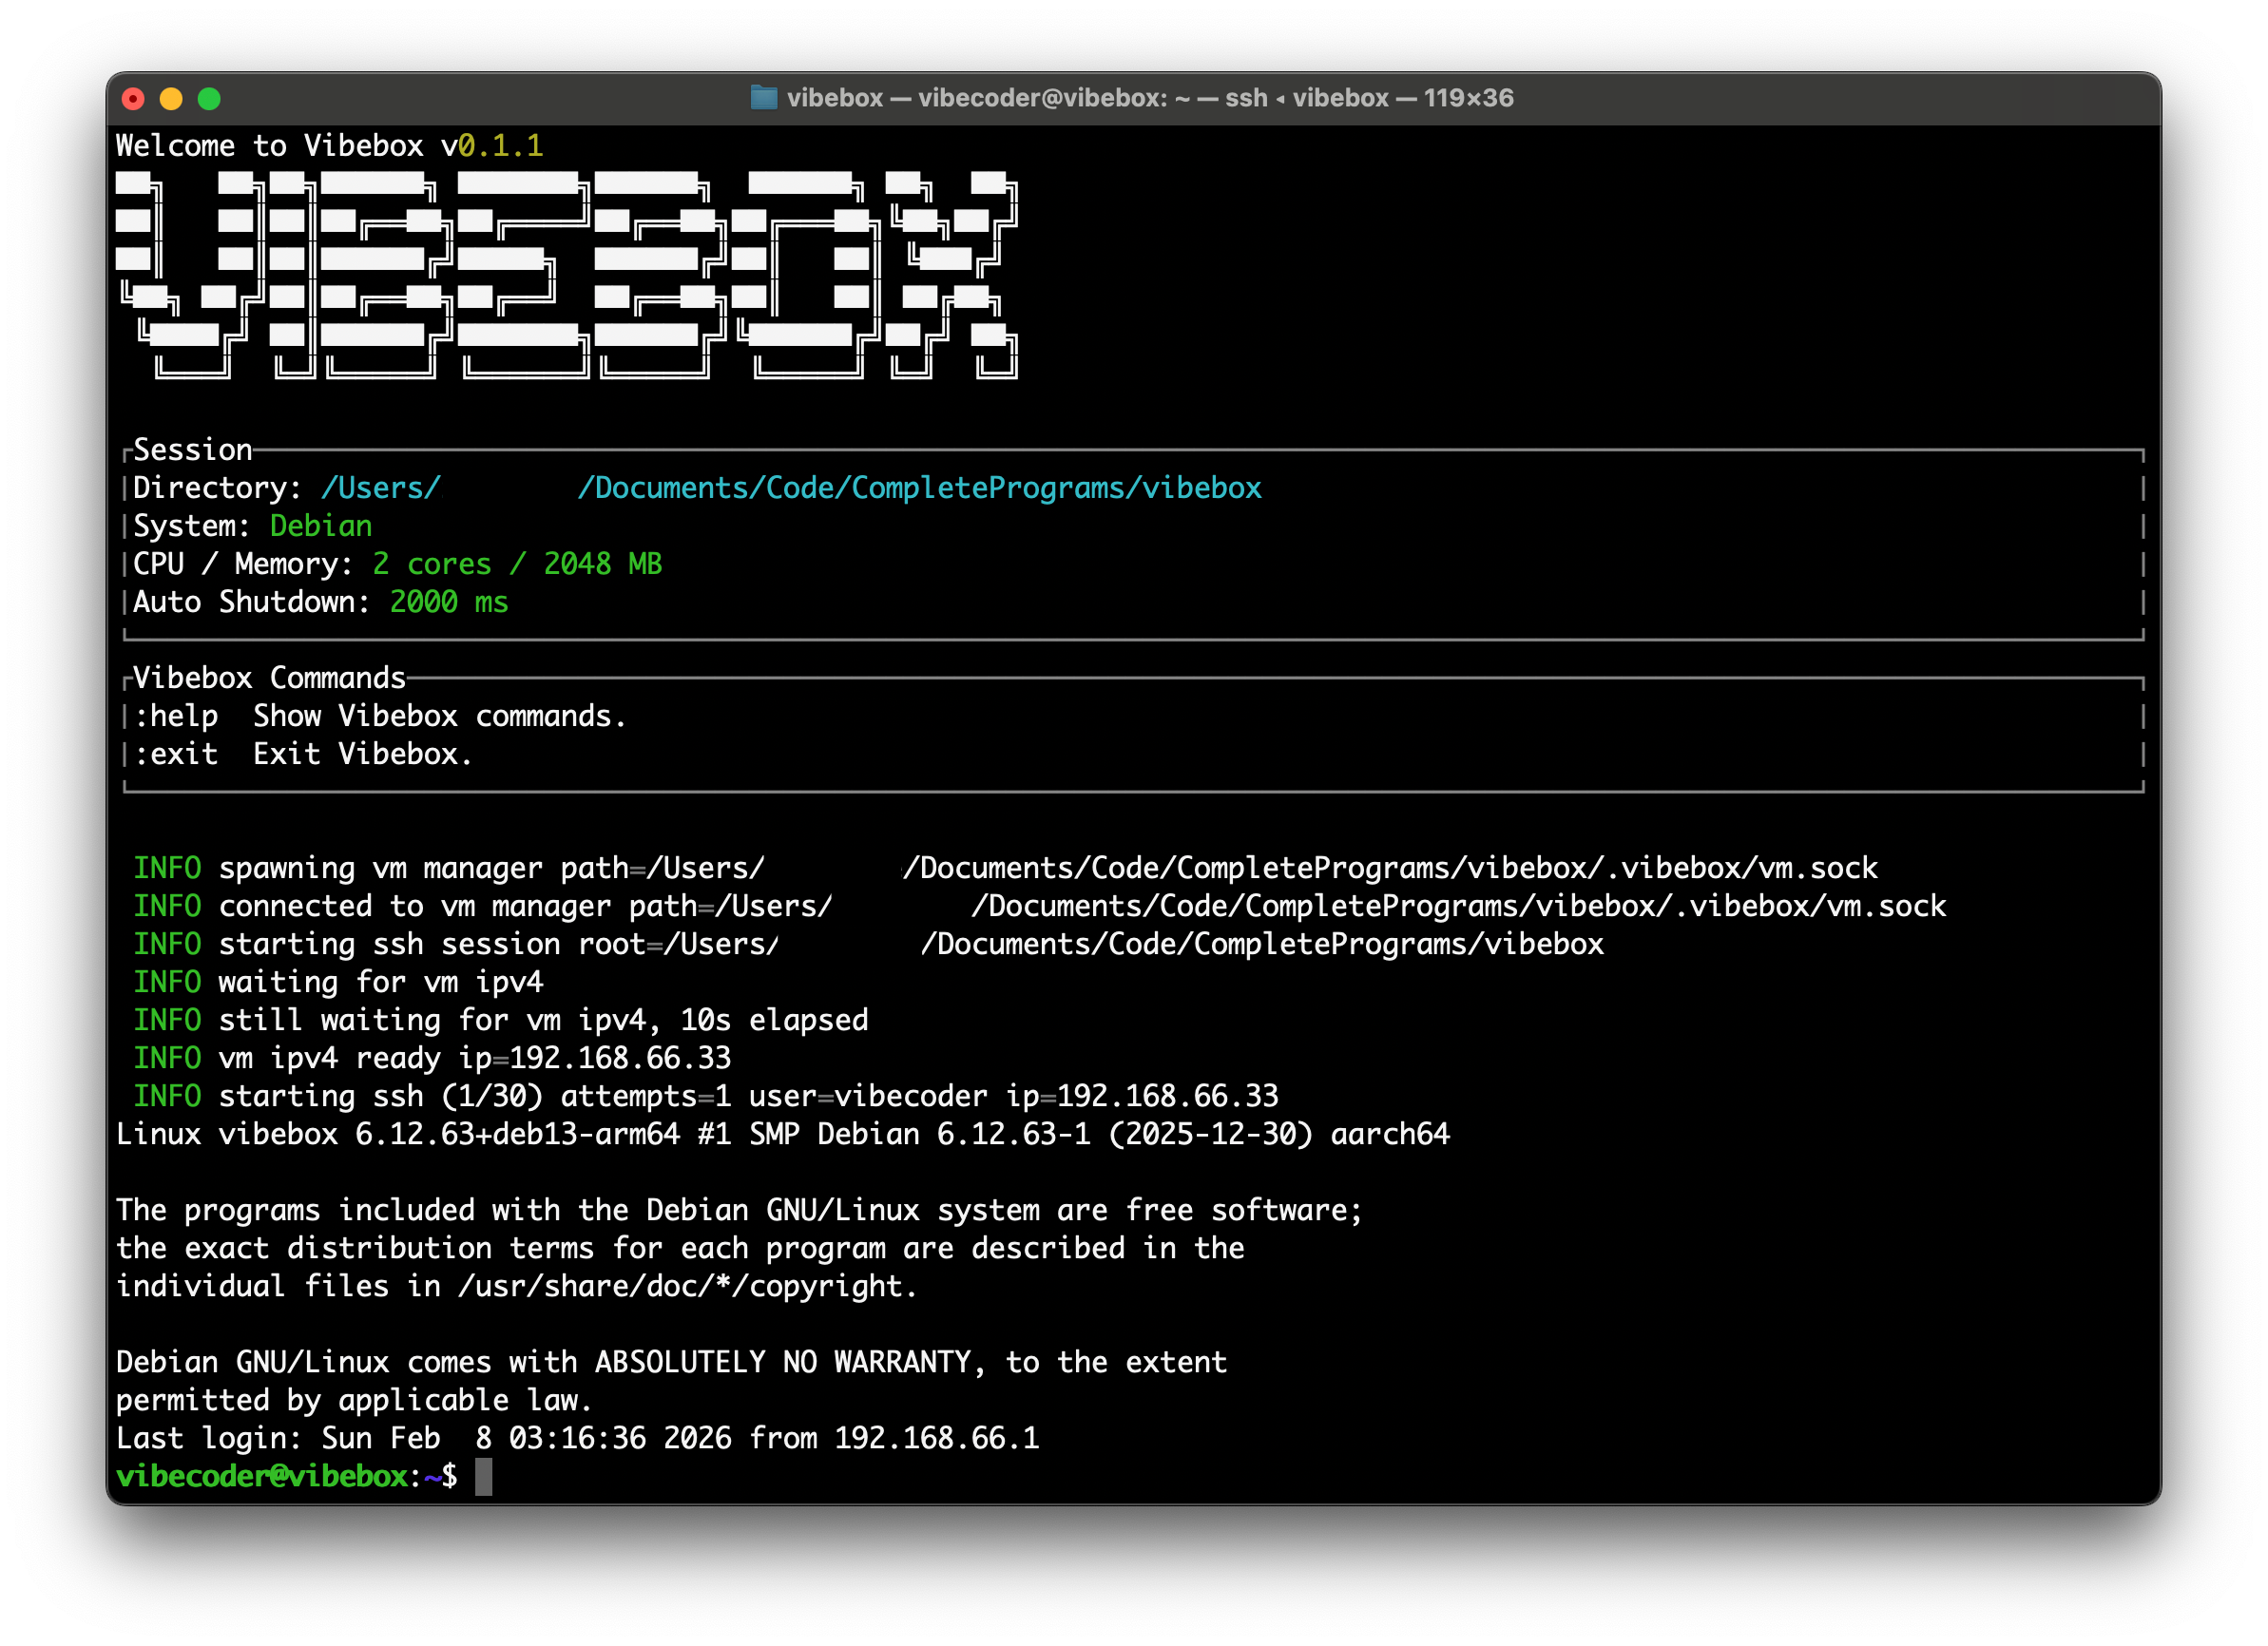 robcholz/vibebox
Ultrafast CLI on Apple Silicon macOS for fast, sandboxed development and LLM agents.
 aaaguirrep/offensive-docker-vps
Create a VPS on Google Cloud Platform or Digital Ocean easily with Offensive Docker included to launch assessment to the targets.

 gitlab-org/security-products/protocol-fuzzer-ce
This is the community edition of GitLab's protocol fuzzing framework. This framework is based on Peach Fuzzer Professional with some features removed.
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 offseq/threat-finder
Runtime vulnerability scanner: finds CVEs in the services actually running on a host and ranks them by network exposure.
 tinfoilsh/cvmimage
Builds a hermetic, reproducible confidential VM image for secure inference and custom compute on AMD SEV-SNP and Intel TDX, with auditable…
 chen-keinan/kube-beacon
Open Source runtime scanner for k8s cluster and perform security audit checks based on CIS Kubernetes Benchmark specification
 bugbounty-site/gitsecure
Detect exposed API keys on GitHub commits.
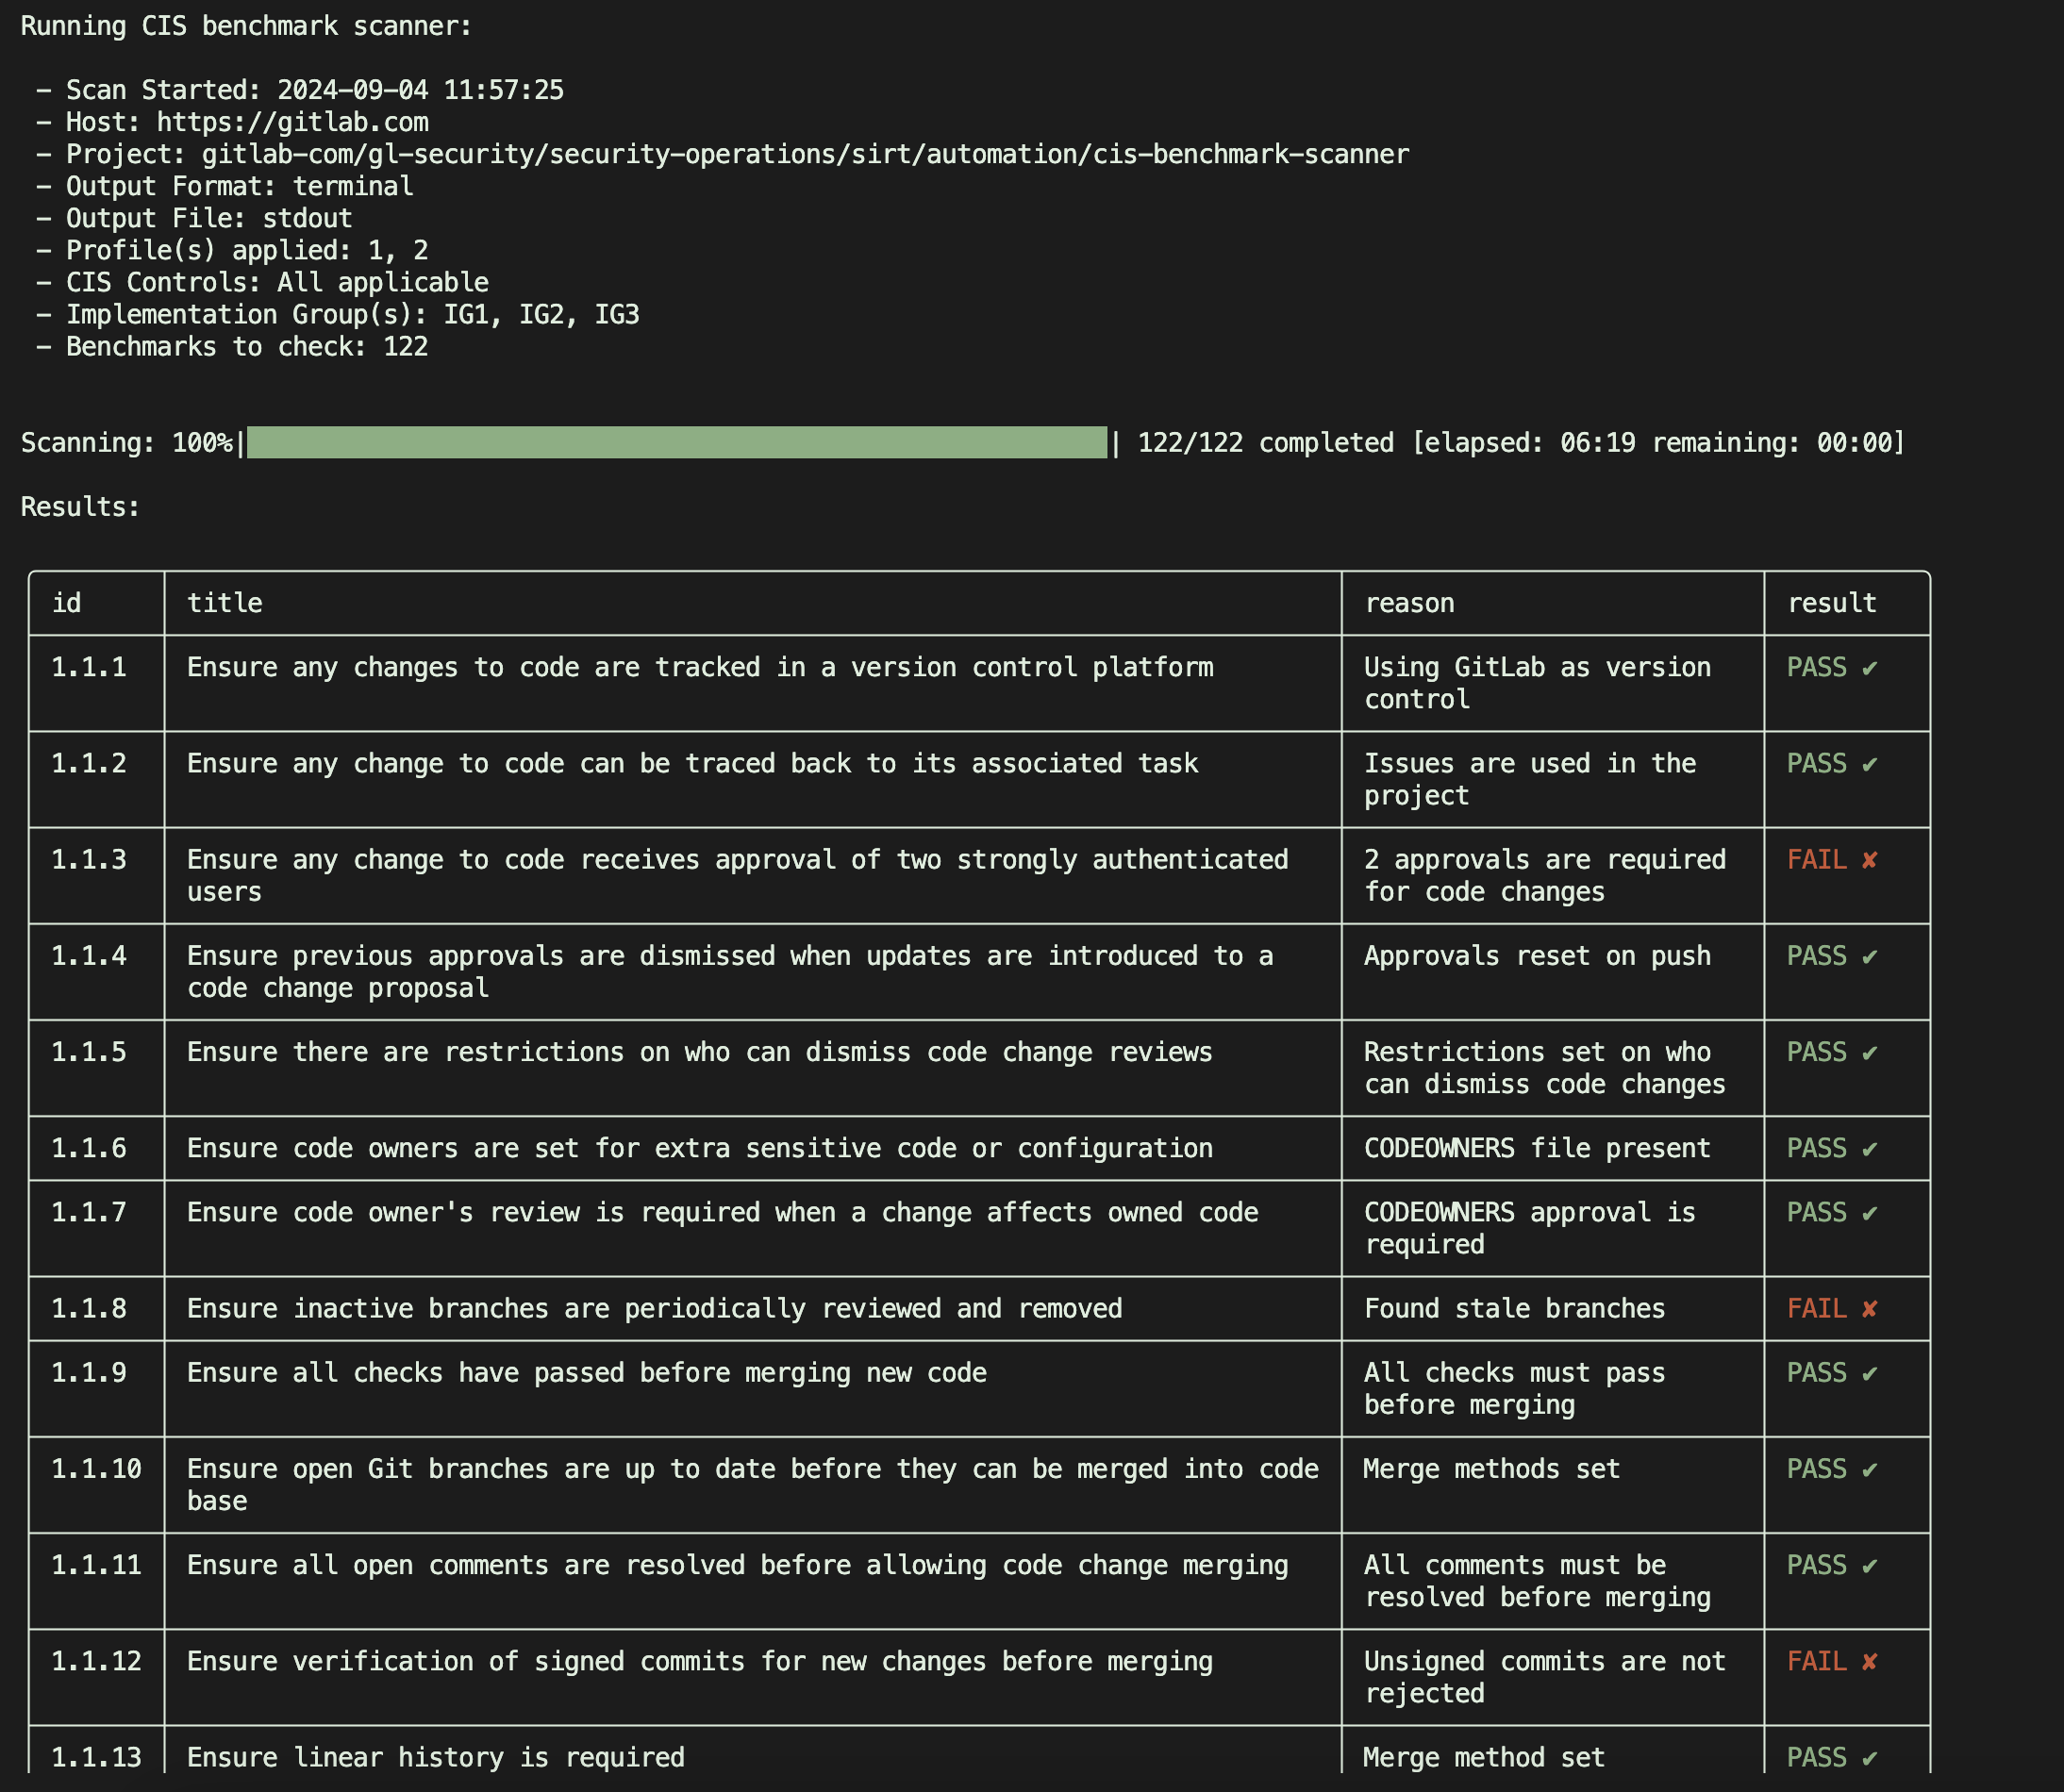 gitlab-security-oss/cis/gitlabcis
Audits GitLab projects against the CIS GitLab Benchmark via read-only API checks, generating JSON reports on compliance and hardening recommendations.
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
 projectdiscovery/naabu-action
A fast port scanner written in go with a focus on reliability and simplicity.
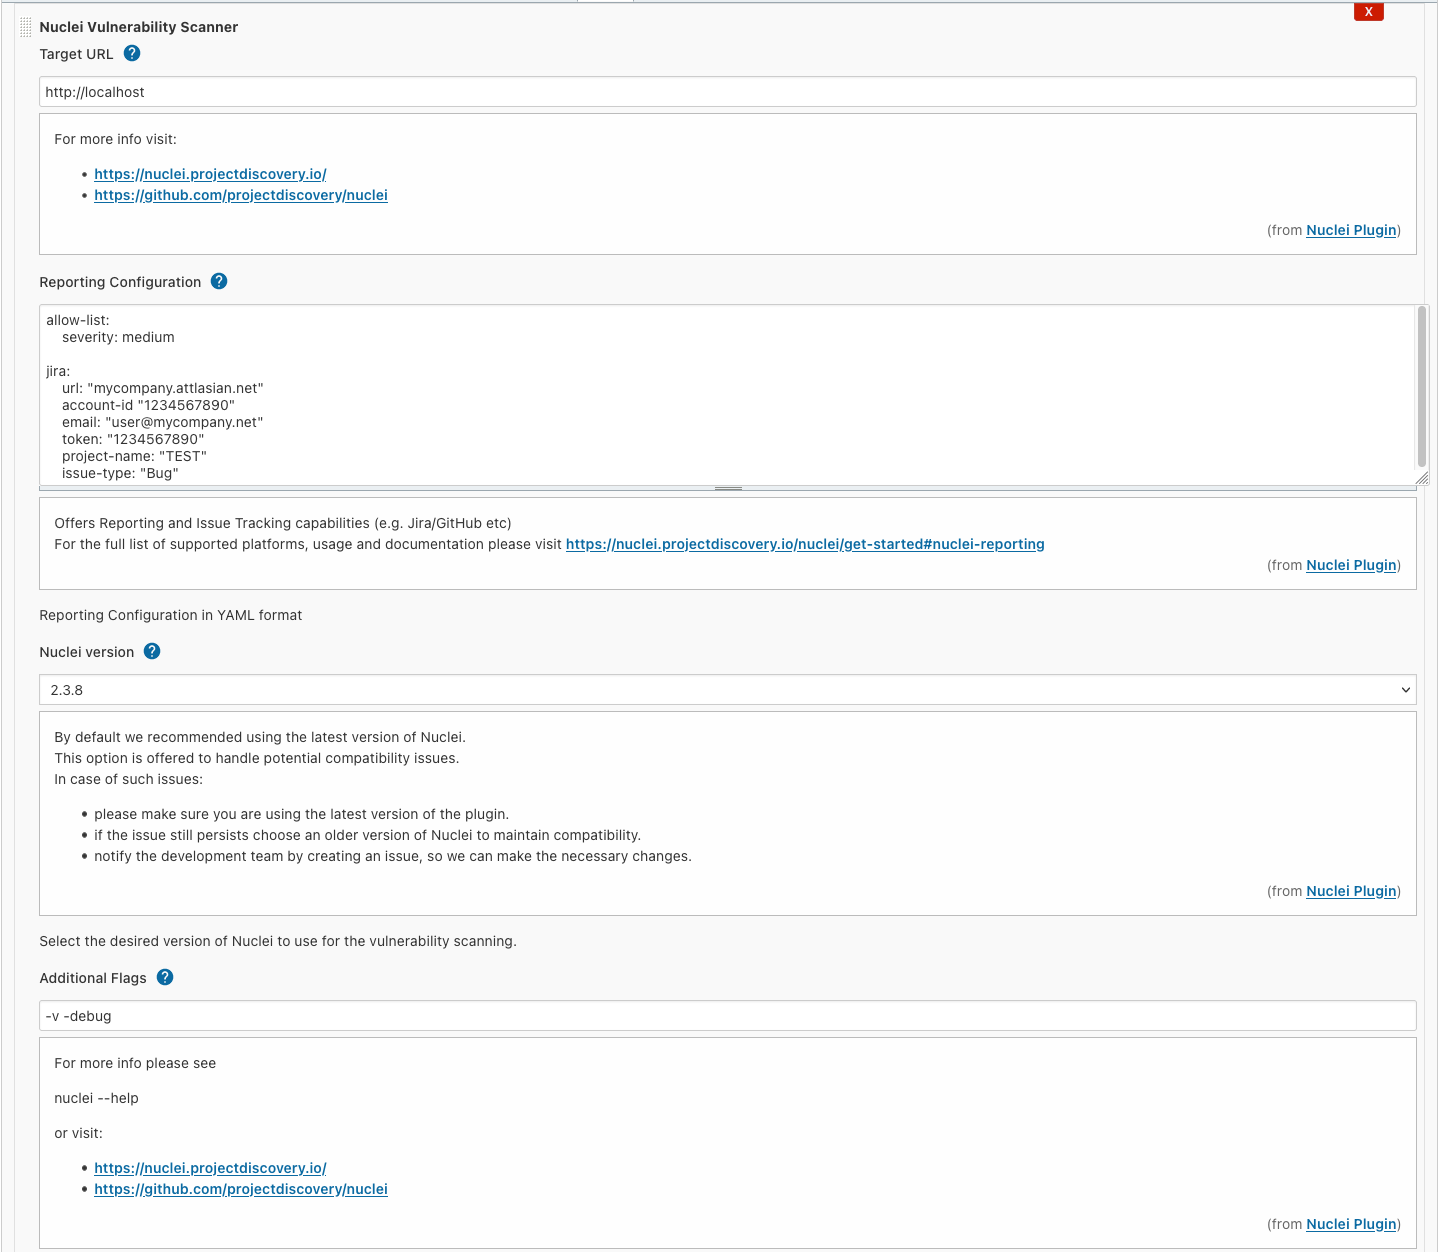 jenkinsci/nuclei-plugin
Nuclei is a fast tool for configurable targeted vulnerability scanning based on templates offering massive extensibility and ease of use.
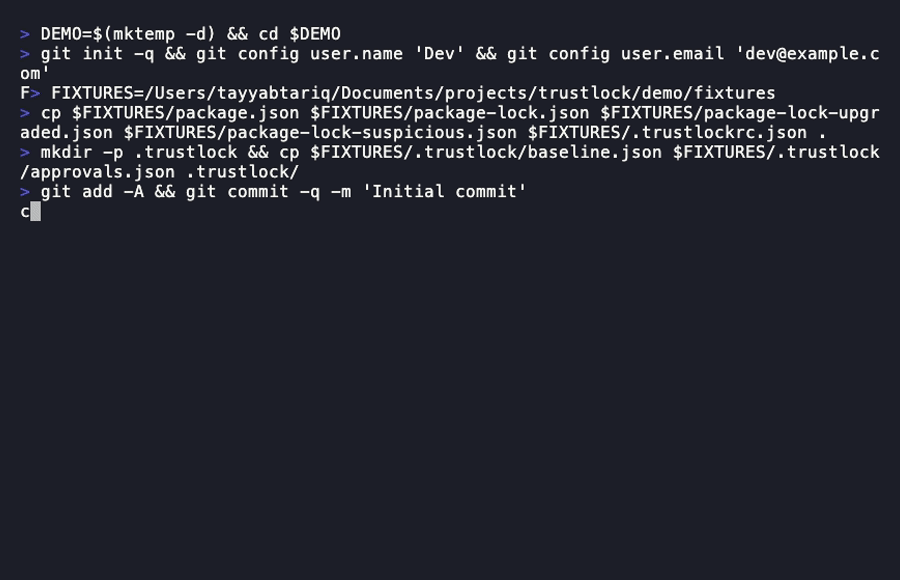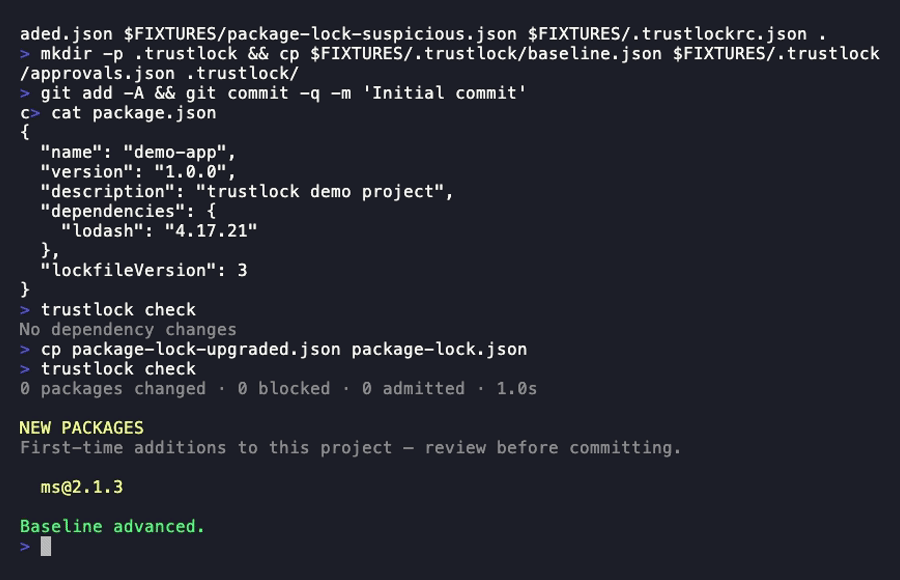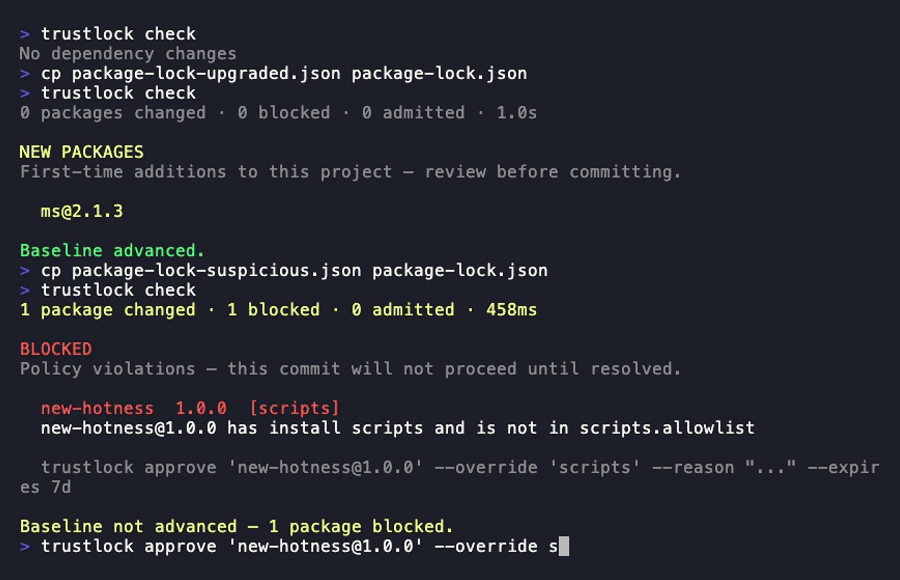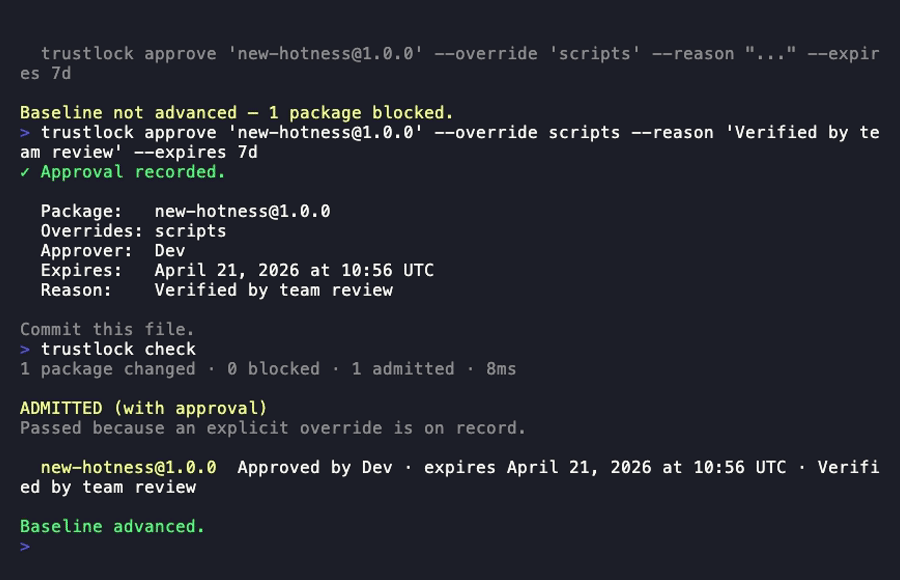 tayyabt/trustlock
A Git-native dependency admission controller. Evaluates trust signals on every dependency change and blocks commits or builds when packages fail your…
 giovannigatti/cve-bench
A benchmark for evaluating AI agents on fixing real-world security vulnerabilities.