
FIASSE
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
code-analysiscurated-resourcesdevsecops+7
141 day ago
owasp/fiasseA Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 owasp/owasp-ctf
Self-hosted CTF control plane for security-learning events: team registration, live leaderboard, and patch-to-score, quiz, jeopardy, and AI challenge…
 owasp/riskassessmentframework
The Secure Coding Framework
 owasp/rbac
PHP-RBAC is an authorization library for PHP. It provides developers with NIST Level 2 Standard Role Based Access Control and more, in the fastest…
 owasp/user-security-stories
Repo to hold mapping of user-security-stories
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 owasp/threat-modeling-playbook
Structured playbook for integrating threat modeling into product security, covering stakeholder buy-in, organizational embedding, training, process…
 owasp/application-security-curriculum
Structured curriculum for learning application security, covering secure coding, threat modeling, and DevSecOps practices. Designed for self-paced…
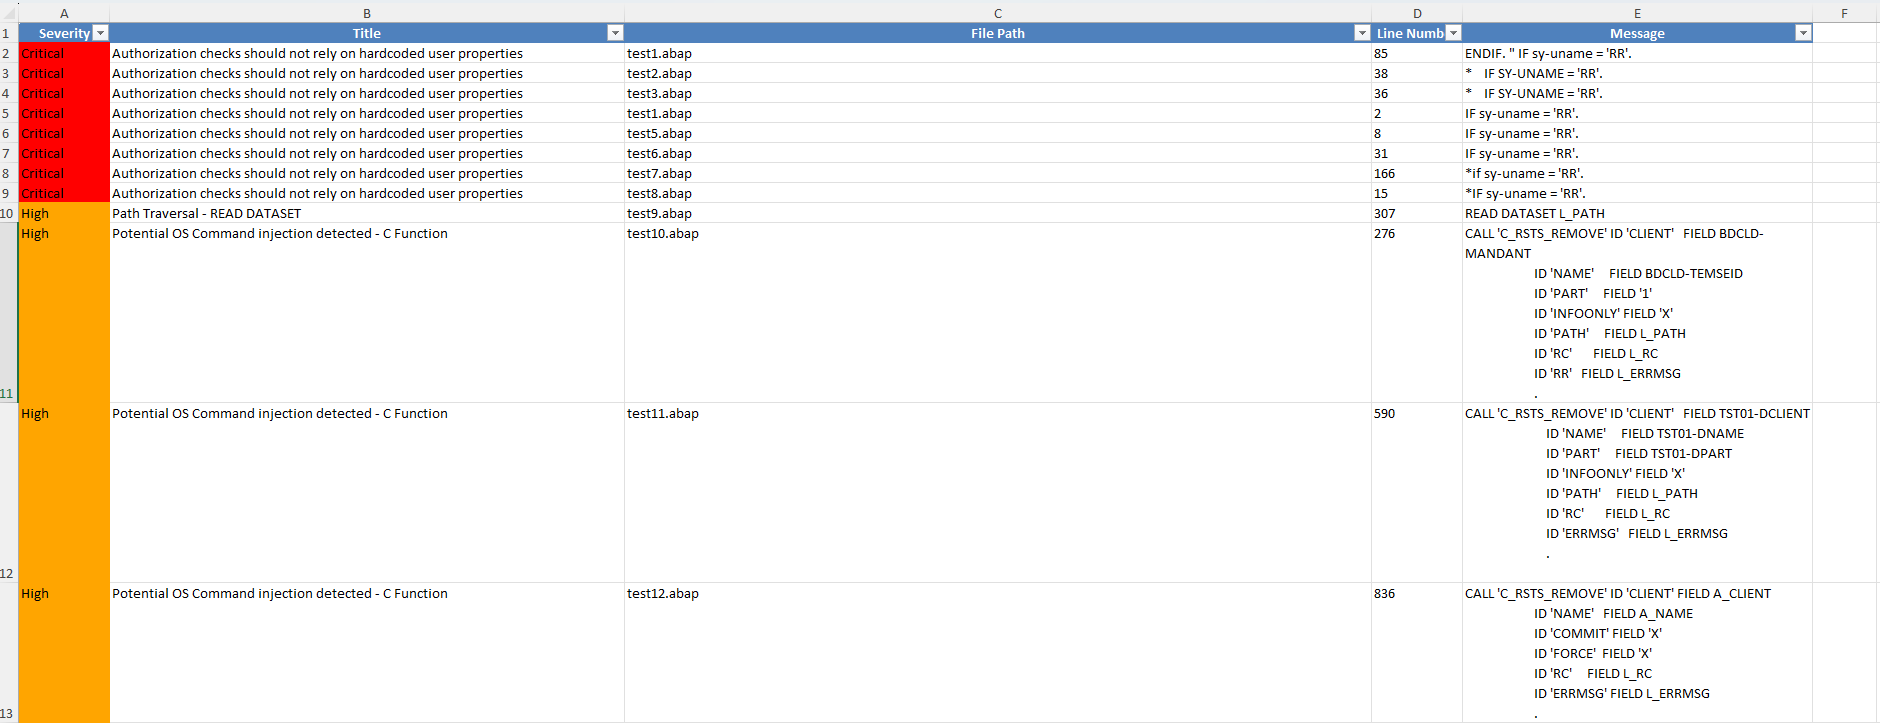
 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 owasp/secureml
SecureML - Securing and Watermarking AL models
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 nexaiceo/nexus-os
The Governed Agentic AI Operating System — Rust + Tauri 2.0 | 65 crates, 658 commands, 84 pages, 5,029 tests, 10/10 OWASP
 domain-protect/domain-protect
OWASP Domain Protect - prevent subdomain takeover
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
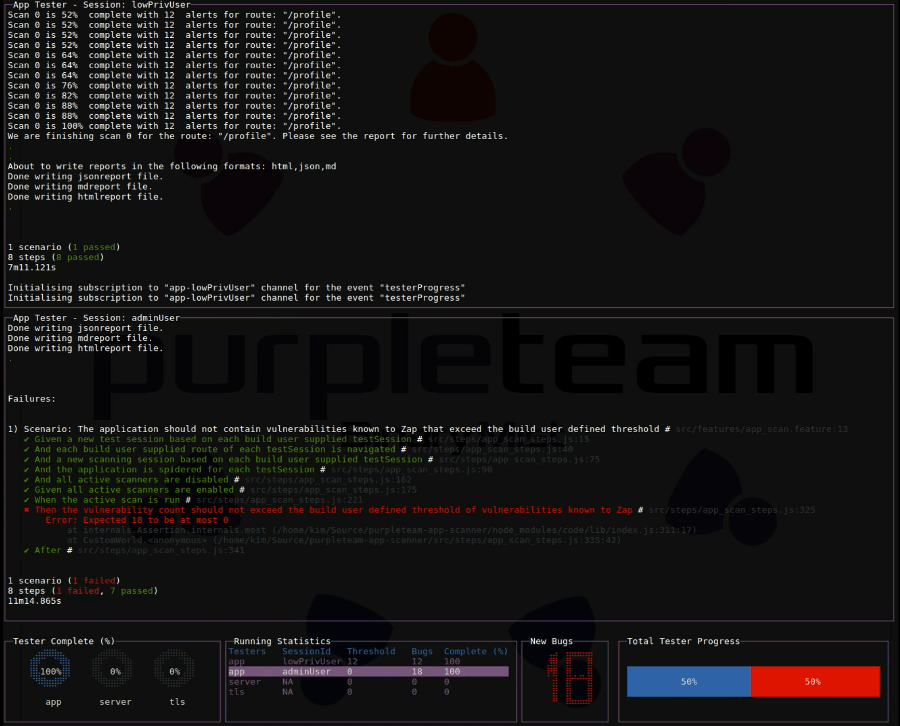 purpleteam-labs/purpleteam
CLI component of purpleteam