

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Sources curated into a security tool Repositories, feeds, communities and curated indexes flow through selection, classification, enrichment and translation into an illustrative tool record. ISC License Copyright (c) 2026 Lucide Icons and Contributors Permission to use, copy, modify, and/or distribute this software for any purpose with or without fee is hereby granted, provided that the above copyright notice and this permission notice appear in all copies. THE SOFTWARE IS PROVIDED "AS IS" AND THE AUTHOR DISCLAIMS ALL WARRANTIES WITH REGARD TO THIS SOFTWARE INCLUDING ALL IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS. IN NO EVENT SHALL THE AUTHOR BE LIABLE FOR ANY SPECIAL, DIRECT, INDIRECT, OR CONSEQUENTIAL DAMAGES OR ANY DAMAGES WHATSOEVER RESULTING FROM LOSS OF USE, DATA OR PROFITS, WHETHER IN AN ACTION OF CONTRACT, NEGLIGENCE OR OTHER TORTIOUS ACTION, ARISING OUT OF OR IN CONNECTION WITH THE USE OR PERFORMANCE OF THIS SOFTWARE. --- The following Lucide icons are derived from the Feather project: airplay, alert-circle, alert-octagon, alert-triangle, aperture, arrow-down-circle, arrow-down-left, arrow-down-right, arrow-down, arrow-left-circle, arrow-left, arrow-right-circle, arrow-right, arrow-up-circle, arrow-up-left, arrow-up-right, arrow-up, at-sign, calendar, cast, check, chevron-down, chevron-left, chevron-right, chevron-up, chevrons-down, chevrons-left, chevrons-right, chevrons-up, circle, clipboard, clock, code, columns, command, compass, corner-down-left, corner-down-right, corner-left-down, corner-left-up, corner-right-down, corner-right-up, corner-up-left, corner-up-right, crosshair, database, divide-circle, divide-square, dollar-sign, download, external-link, feather, frown, hash, headphones, help-circle, info, italic, key, layout, life-buoy, link-2, link, loader, lock, log-in, log-out, maximize, meh, minimize, minimize-2, minus-circle, minus-square, minus, monitor, moon, more-horizontal, more-vertical, move, music, navigation-2, navigation, octagon, pause-circle, percent, plus-circle, plus-square, plus, power, radio, rss, search, server, share, shopping-bag, sidebar, smartphone, smile, square, table-2, tablet, target, terminal, trash-2, trash, triangle, tv, type, upload, x-circle, x-octagon, x-square, x, zoom-in, zoom-out The MIT License (MIT) (for the icons listed above) Copyright (c) 2013-present Cole Bemis Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software. THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
Repositories
GitHub & GitLab
Security feeds
Blogs, RSS & Atom
Communities
Reddit, X & submissions
Curated indexes
Security lists & trends
Curate & select
Classification
Enrichment
Translation
Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. {"fictional":true,"name":"Tool","version":"1.0.1","repository":"owner/tool","live_metrics":false,"example_metrics":{"stars":1200,"forks":128,"views":8600}}
Tool
v1.0.1 owner/tool
Discover assets and review
HTTP security headers.
Reconnaissance
Web security
1,200 stars — Fictional example1.2k 128 forks — Fictional example128 8,600 views — Fictional example8.6k

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
827 results
matt.net preview

matt.net

GitHubnccgroup/matt.net

Matt.Net is a simple GUI wrapper around Microsoft's CAT.NET Code Auditing Tool

code-analysisdevsecopsstatic-code-analysis+2
8
12 years ago
TriSuElla-AIDLCA-Framework preview

TriSuElla-AIDLCA-Framework

GitHubowasp/trisuella-aidlca-framework

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

ai-securitycloud-securitycode-analysis+7
512 days ago
Vulnvault preview

Vulnvault

GitHubviralmaniar/vulnvault

Developer-focused knowledge base of application security vulnerabilities with insecure vs secure code examples, prevention guidance, and OWASP/CWE…

code-analysiscurated-resourcesdevsecops+5
41 month ago
meles preview

meles

GitHubmovray/meles

Malware scanner for container images: daemonless, layer-aware, ClamAV and YARA

cloud-securitycontainer-securitydefensive-tools+6
41 day ago
fad-checker preview

fad-checker

GitHub9pings/fad-checker

Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…

code-analysisconfiguration-auditingdefensive-tools+6
41 day ago
next-cve-2025-66478 preview

next-cve-2025-66478

GitHubabtonc/next-cve-2025-66478

Scans local projects for CVE-2025-66478 vulnerability and reports affected instances without fixing them.

code-analysisdevsecopsstatic-analysis+3
1111 months ago
ore-mal-pkg-inspector preview

ore-mal-pkg-inspector

GitHubrapticore/ore-mal-pkg-inspector

Multi-Ecosystem Malicious Package Detection and Supply Chain Security Scanner

code-analysisdevsecopseducation+6
86 months ago
linux-cve-2026-98432-fix preview

linux-cve-2026-98432-fix

GitHubaronwang001/linux-cve-2026-98432-fix

Detect CVE-2026-98432 on the running Linux kernel and apply the official fixed kernel only on verified distributions (Debian 12/13, Amazon Linux…

configuration-auditingdefensive-toolsdevsecops+4
415 days ago
vibegate preview

vibegate

GitHubthemiddleblue/vibegate

Host-agnostic pre-write security hook for coding agent: detects user-input patterns via Semgrep and emits deterministic, no-LLM security guidance.


ai-securitycode-analysisdevsecops+5
84 months ago
ndaal_public_auditd preview

ndaal_public_auditd

GitLabndaal_open_source/ndaal_public_auditd

Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…
configuration-auditingdefensive-toolsdevsecops+5
42 days ago
jackson-check preview

jackson-check

GitHubxiaoqimikko/jackson-check

jackson-databind + jackson-core 26 条安全公告自查:按坐标逐条求交集给出真正到位的版本(2.18.11/2.21.7/2.22.3/3.1.7/3.2.3,2.21.6 已不够);扫源码降噪告诉你真中几条;含 1 条 GitHub…

devsecopsstatic-code-analysissupply-chain-security+2
1 month ago
bc-check preview

bc-check

GitHubxiaoqimikko/bc-check

Offline scanner telling you which of the 2026 Bouncy Castle CVEs actually apply to you - across BC, BC-LTS and BC-FJA (FIPS), which do not share a…

cryptographydevsecopssupply-chain-security+2
1 month ago
kyubisweep preview

kyubisweep

GitHubtanmayshahane/kyubisweep

A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…

code-analysisconfiguration-auditingdevsecops+3
410 months ago
CVE-2024-6678 preview

CVE-2024-6678

GitHubfallenskill1/cve-2024-6678

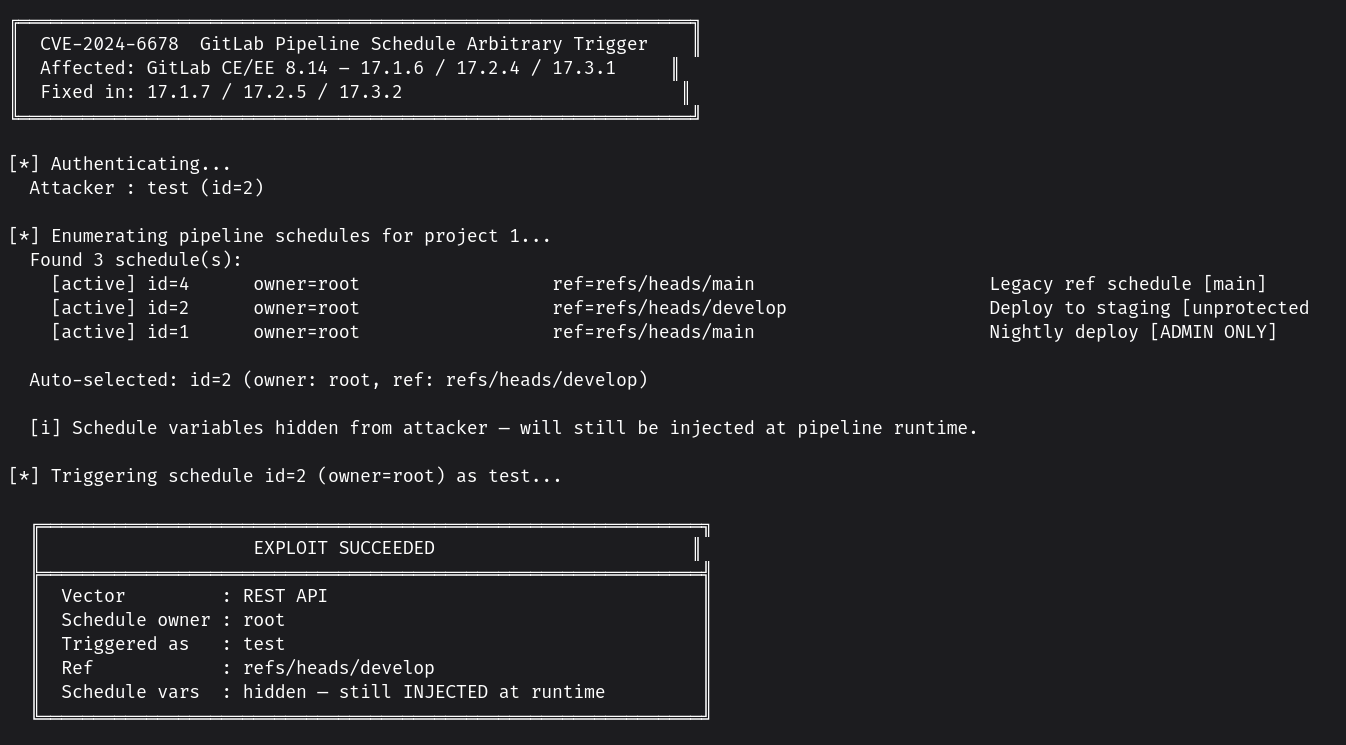
PoC for CVE-2024-6678

cloud-securitydevsecopsexploitation+3
46 months ago
BlackLotus preview

BlackLotus

GitHubajf8729/blacklotus

BlackLotus aka CVE-2023-24932 Detection/Remediation Scripts for Intune, ConfigMgr, and generic use

cloud-securityconfiguration-auditingdevsecops+3
81 year ago
tomcat-check preview

tomcat-check

GitHubxiaoqimikko/tomcat-check

查出 Spring Boot 内嵌 Tomcat 的真实版本(pom 里没有),并对每条 2026 年 CVE 同时给出 ASF 官方评级与 GitHub 评级、触发条件、以及这条会不会进 Dependabot 告警 CVE-2026-41293

configuration-auditingdevsecopssupply-chain-security+3
1 month ago
autopilot-pentest-ai preview

autopilot-pentest-ai

GitHubkush-coder/autopilot-pentest-ai

Official Build & Verified Release | Open-source AI pentester that proves every finding. Machine oracles re-run each exploit; verified bugs ship a…

ai-securitydevsecopsexploitation+7
15 days ago
ai-kubernetes-helm-chart-security preview

ai-kubernetes-helm-chart-security

GitHubsorami-consulting-au/ai-kubernetes-helm-chart-security

Evidence and data for the Sorami technical report on security defaults of 15 AI serving, vector database and MCP Helm charts on Kubernetes.

ai-securitycloud-securityconfiguration-auditing+5
21 month ago
Previous1…262728…46Next
Sources curated into a security tool Repositories, feeds, communities and curated indexes flow through selection, classification, enrichment and translation into an illustrative tool record. ISC License Copyright (c) 2026 Lucide Icons and Contributors Permission to use, copy, modify, and/or distribute this software for any purpose with or without fee is hereby granted, provided that the above copyright notice and this permission notice appear in all copies. THE SOFTWARE IS PROVIDED "AS IS" AND THE AUTHOR DISCLAIMS ALL WARRANTIES WITH REGARD TO THIS SOFTWARE INCLUDING ALL IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS. IN NO EVENT SHALL THE AUTHOR BE LIABLE FOR ANY SPECIAL, DIRECT, INDIRECT, OR CONSEQUENTIAL DAMAGES OR ANY DAMAGES WHATSOEVER RESULTING FROM LOSS OF USE, DATA OR PROFITS, WHETHER IN AN ACTION OF CONTRACT, NEGLIGENCE OR OTHER TORTIOUS ACTION, ARISING OUT OF OR IN CONNECTION WITH THE USE OR PERFORMANCE OF THIS SOFTWARE. --- The following Lucide icons are derived from the Feather project: airplay, alert-circle, alert-octagon, alert-triangle, aperture, arrow-down-circle, arrow-down-left, arrow-down-right, arrow-down, arrow-left-circle, arrow-left, arrow-right-circle, arrow-right, arrow-up-circle, arrow-up-left, arrow-up-right, arrow-up, at-sign, calendar, cast, check, chevron-down, chevron-left, chevron-right, chevron-up, chevrons-down, chevrons-left, chevrons-right, chevrons-up, circle, clipboard, clock, code, columns, command, compass, corner-down-left, corner-down-right, corner-left-down, corner-left-up, corner-right-down, corner-right-up, corner-up-left, corner-up-right, crosshair, database, divide-circle, divide-square, dollar-sign, download, external-link, feather, frown, hash, headphones, help-circle, info, italic, key, layout, life-buoy, link-2, link, loader, lock, log-in, log-out, maximize, meh, minimize, minimize-2, minus-circle, minus-square, minus, monitor, moon, more-horizontal, more-vertical, move, music, navigation-2, navigation, octagon, pause-circle, percent, plus-circle, plus-square, plus, power, radio, rss, search, server, share, shopping-bag, sidebar, smartphone, smile, square, table-2, tablet, target, terminal, trash-2, trash, triangle, tv, type, upload, x-circle, x-octagon, x-square, x, zoom-in, zoom-out The MIT License (MIT) (for the icons listed above) Copyright (c) 2013-present Cole Bemis Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software. THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
Repositories
GitHub & GitLab
Security feeds
Blogs, RSS & Atom
Communities
Social & submissions
Curated indexes
Security lists & trends
Curate & classify
Enrich & translate
Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. Fictional tool and repository. The description, categories, stars, forks and views are illustrative examples, not live or verified data. {"fictional":true,"name":"Tool","version":"1.0.1","repository":"owner/tool","live_metrics":false,"example_metrics":{"stars":1200,"forks":128,"views":8600}}
Tool
owner/tool v1.0.1
Discover assets and review HTTP security headers.
Reconnaissance
Web security
1,200 stars — Fictional example1.2k 128 forks — Fictional example128 8,600 views — Fictional example8.6k