

WantasticCore
 wantasticapp/wantasticcore
AIO Cloud Managment Server
ai-securityauthenticationcloud-security+6
14
wantasticapp/wantasticcoreAIO Cloud Managment Server
 owasp/appsec-agent
A TypeScript package that provides AI-powered agents for Application Security (AppSec) tasks, built on top of the frontier models.
 jdauphant/patch-openssl-cve-2014-0160
Patch openssl #heartbleed with ansible
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…

 kamalsrini/sentinel-cve
CLI tool that explains CVEs in plain English and scans repos for impact. Powered by Claude.
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
 aaronfay/cve-2015-0235-test
Ansible playbook to check vulnerability for CVE-2015-0235
 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 ericmtzmtz/pwnproxy
An open, local-first security testing platform for pentesters, AI agents, CI/CD pipelines, and teams.
 jq6l43d1/proxmox-lxc-docker-fix
Workaround for CVE-2025-52881: Fixes Docker/Podman breakage in Proxmox LXC containers caused by AppArmor incompatibility with runc 1.2.7+. Universal…
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday
 rocketchat/layne
A doggo that helps look for security issues in your repositories.
 aquasecurity/secfixes-tracker
Forked from https://gitlab.alpinelinux.org/kaniini/secfixes-tracker
 claranet/ansible-role-log4shell
Ansible role to detect Log4Shell (CVE-2021-44228) by scanning filesystem and open files for vulnerable JAR/WAR files, reporting version and…
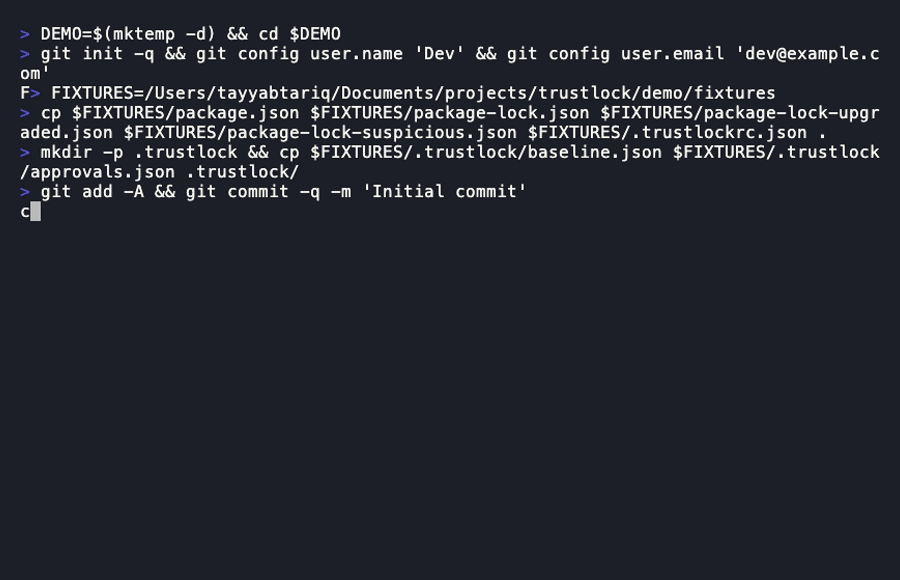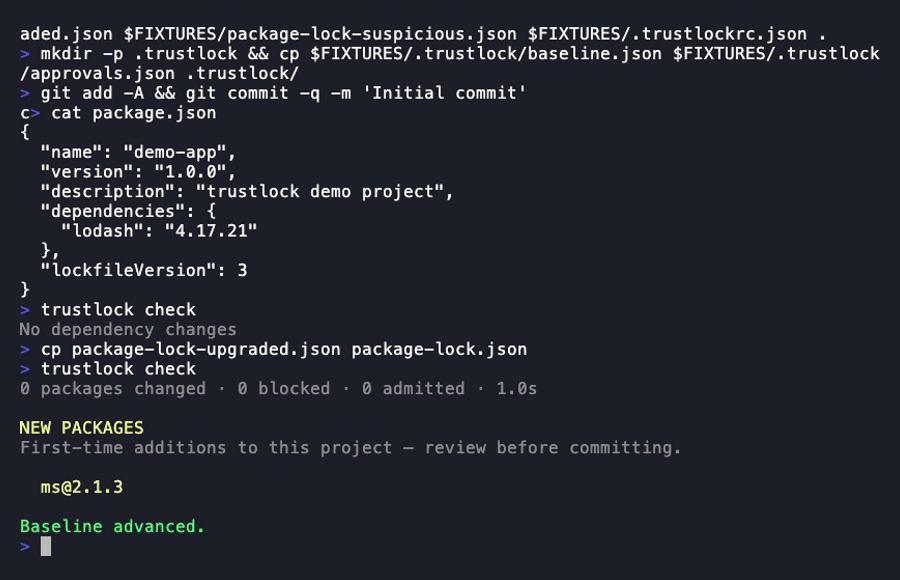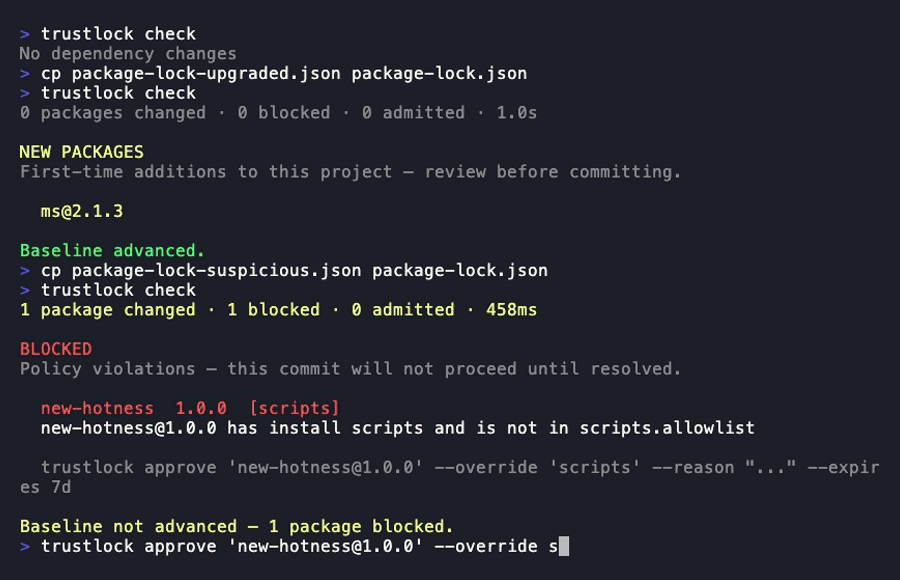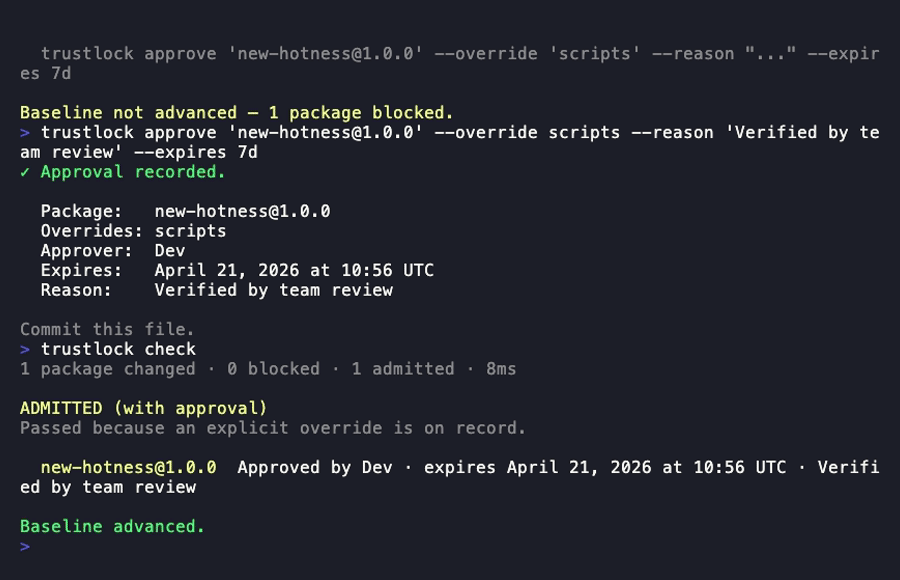 tayyabt/trustlock
A Git-native dependency admission controller. Evaluates trust signals on every dependency change and blocks commits or builds when packages fail your…

 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.