

check_struts
 andypitcher/check_struts
Apache Struts version analyzer (Ansible) based on CVE-2017-5638
cloud-securityconfiguration-auditingdevsecops+3
2
andypitcher/check_strutsApache Struts version analyzer (Ansible) based on CVE-2017-5638
 joaoreis13/flight-risk
Security toolkit for CVE-2025-55182 (React2Shell) — scan, detect, correlate, and test React Server Components RCE vulnerability
 tailwindrg/cve-2026-0300-audit
Read-only audit tooling for CVE-2026-0300 (PAN-OS User-ID Authentication Portal exposure)
 barappteam/nginx-cve-fix
Source-built nginx 1.25.5 container with backported CVE-2026-42945 fix, OpenSSL bump, full provenance chain, and VEX attestation.
 siyad01/agentbox
Open-source sandboxed runtime for AI agents — gVisor/Docker isolation, credential vault, immutable audit log. Built after CVE-2026-25253.
 rotavori/dasel-melange-apko
dasel v3.3.1 packaged with Melange and shipped as a minimal apko image, patched for CVE-2026-33320
 ashleyt3/docker-socket-risk-demos
Companion source for YouTube video "Stop Mounting docker.sock — Run Trivy Without Giving Away Root Access — (inspired by CVE-2026-33634)"
 salman-sec/patch-management-
Scenario-based training exercise for IT administrators: identify, approve, and deploy critical patches for financial systems under a 48-hour SLA…
 shoucheng3/apache__dolphinscheduler_cve-2023-51770_3_2_1_fixed
Exploit for CVE-2023-51770 targeting Apache DolphinScheduler versions 3.2.1 and earlier, enabling remote code execution via crafted workflow…
 moisei-dev/go-dbmigrate
Go library and CLI for managing database schema migrations with support for PostgreSQL, MySQL, SQLite, and Cassandra, including up/down migration…
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 vishnunandan555/cordon
Run any command inside a restricted filesystem view on Linux
 salesforce/vulnreport
Open-source pentesting management and automation platform by Salesforce Product Security
 mobsf/mobile-security-framework-mobsf
Automated mobile application security testing framework for Android, iOS, and Windows. Performs static and dynamic analysis, malware detection, and…
 m14r41/pentestingeverything
Complete Solution for VAPT/AppSec and Pentesting Guide: Web | Mobile | API | Thick Client | Source Code Review | DevSecOps | Wireless | Network…
 bridgecrewio/terragoat
Intentionally vulnerable Terraform infrastructure for learning cloud misconfiguration detection and DevSecOps practices across AWS, Azure, and GCP.
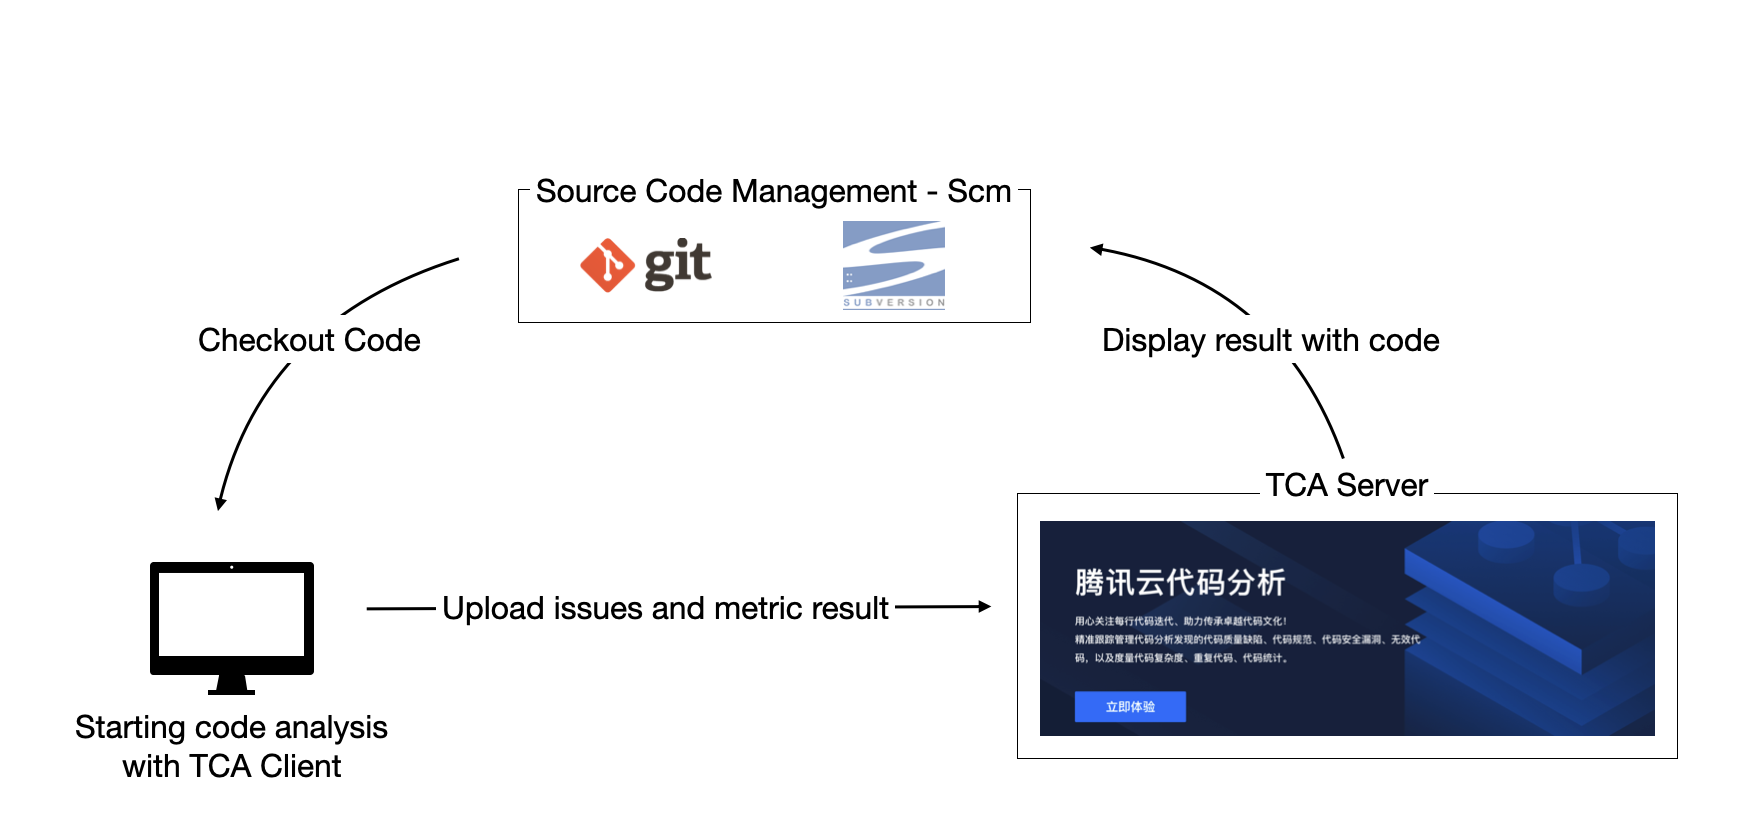 tencent/codeanalysis
Enterprise-grade static code analysis platform with multi-language support, security vulnerability detection, code quality metrics, and DevOps…
 cider-security-research/cicd-goat
A deliberately vulnerable CI/CD environment. Learn CI/CD security through multiple challenges.