

GuardScan
 ntanwir10/guardscan
100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI
ai-securityapi-securitycloud-security+8
ntanwir10/guardscan100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI

 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 c3rb3ru5d3d53c/signatures
Community Detection Signature Build and Distribution Pipeline for YARA, Suricata, Snort and Sigma
 afine-com/glassworm-hunter
Detects GlassWorm supply chain attack payloads by scanning VS Code extensions, npm/PyPI packages, and git repos for invisible Unicode payloads,…
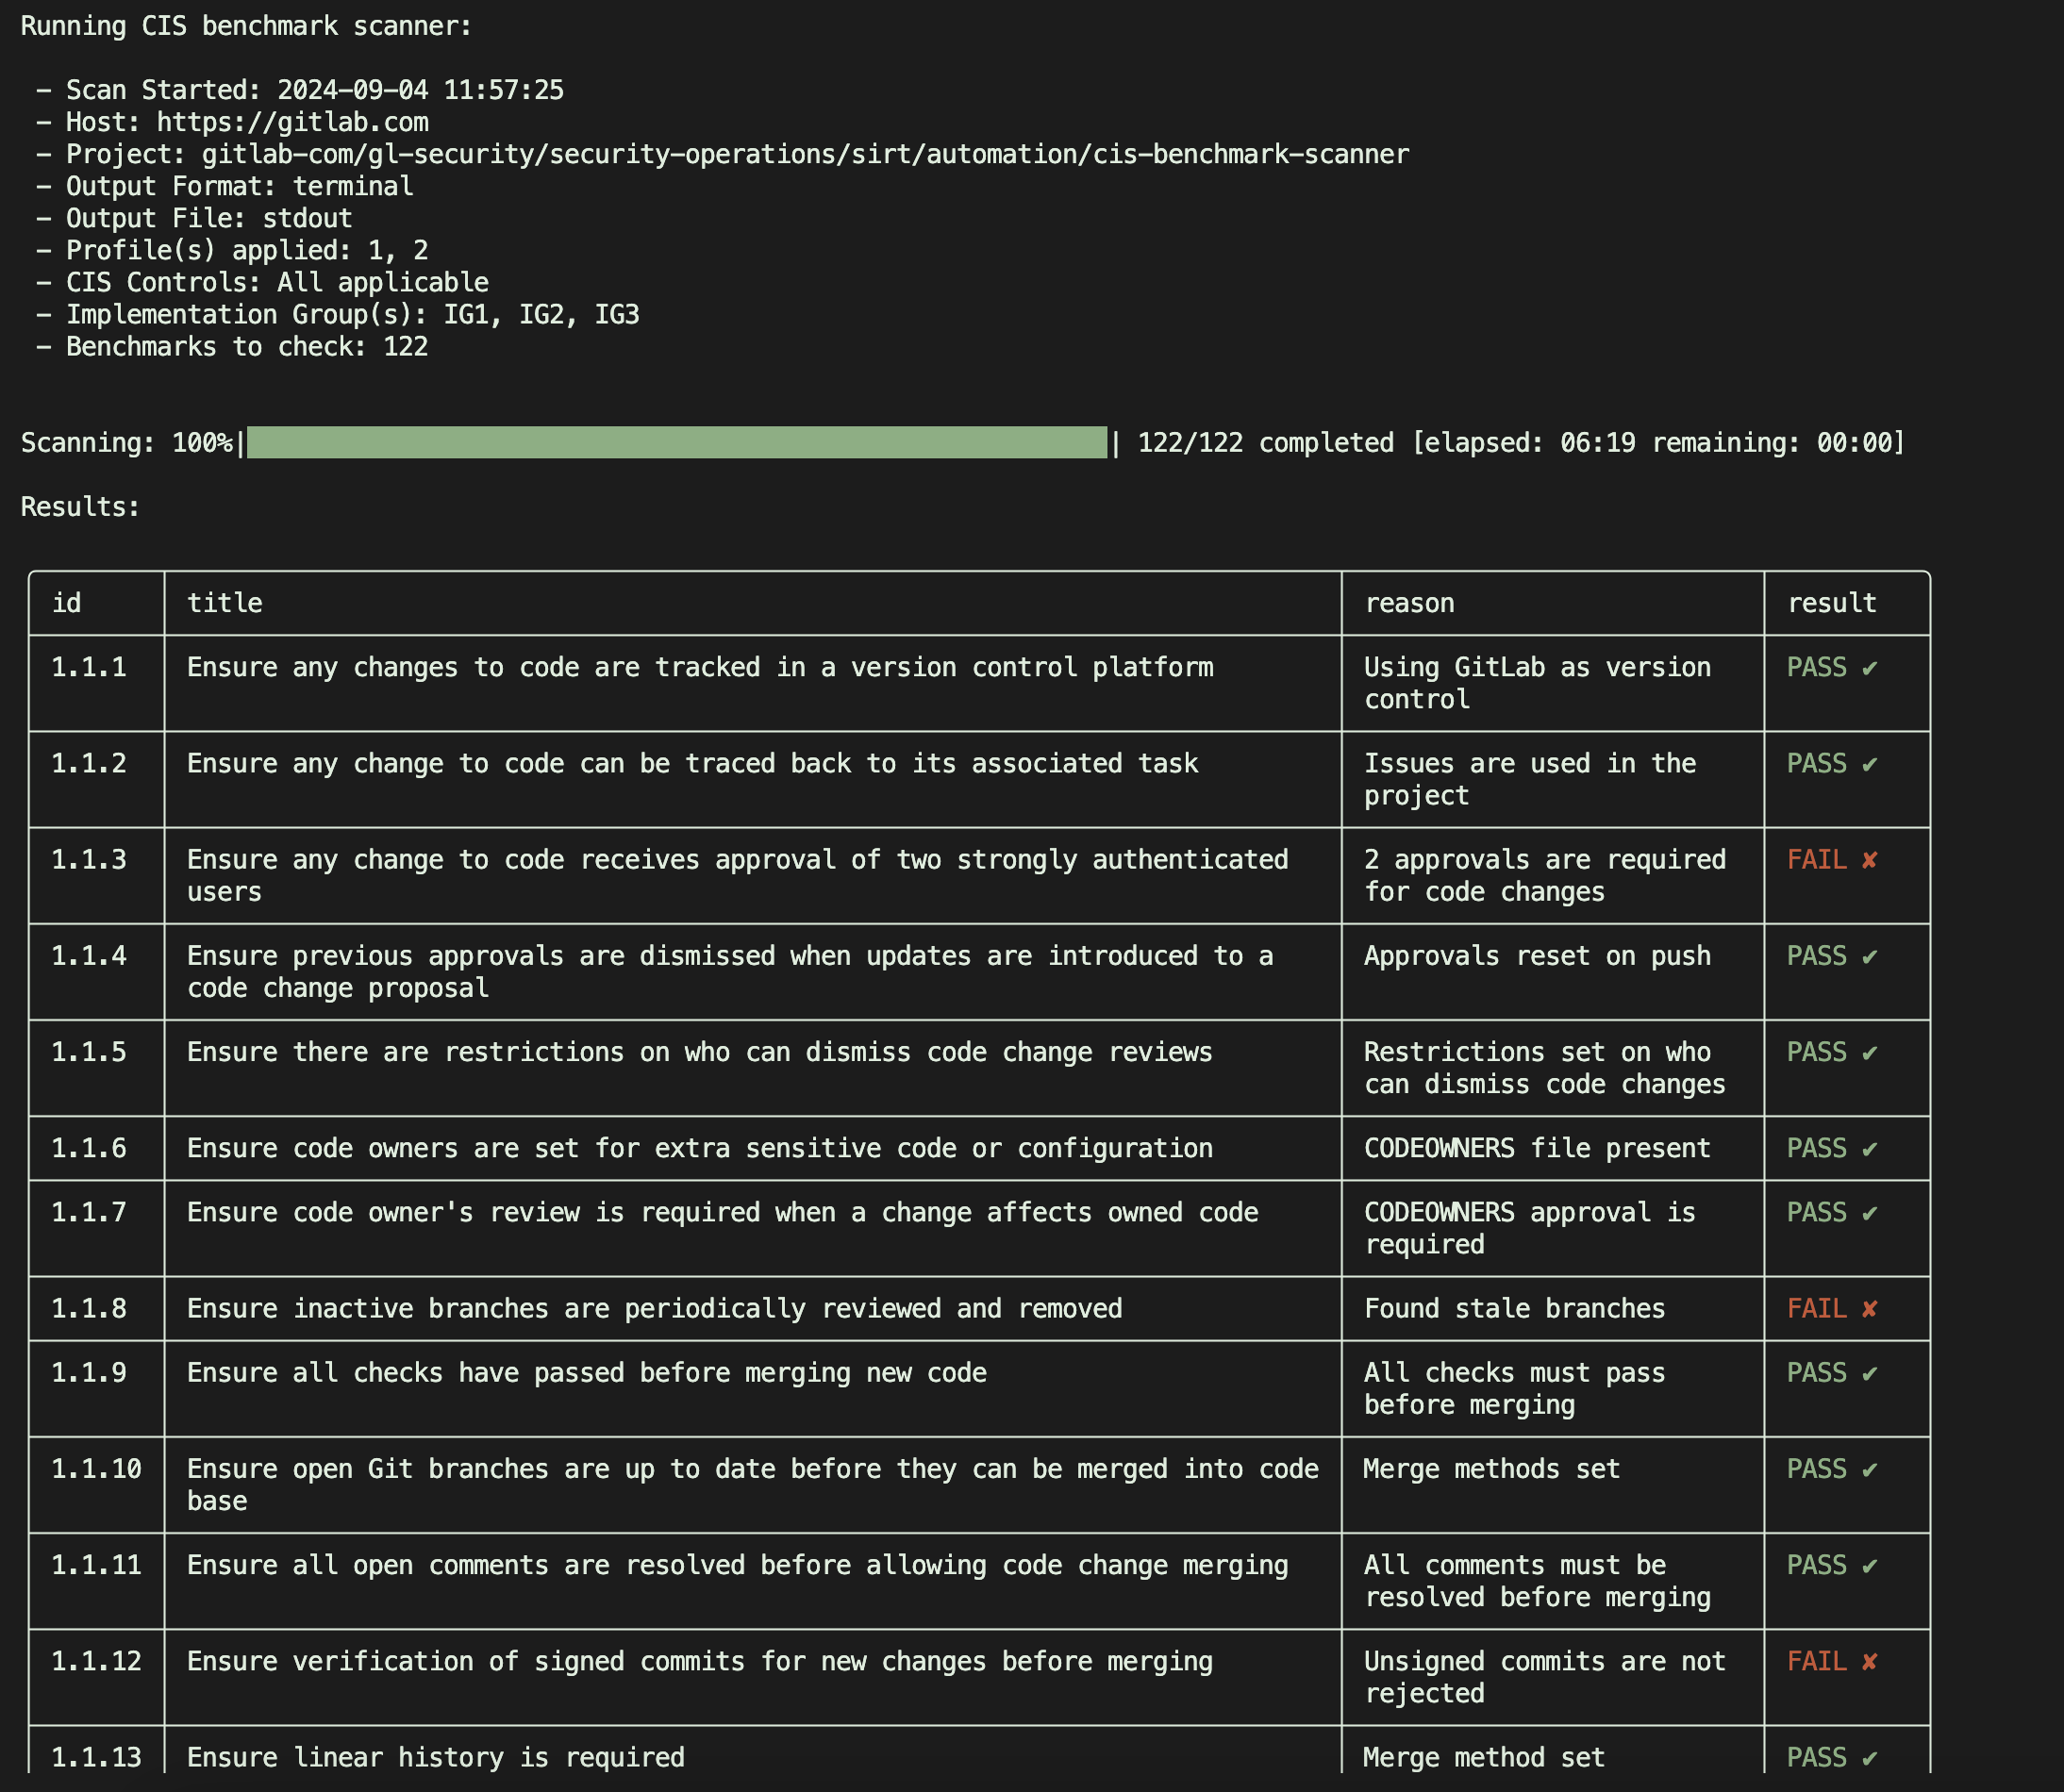
 gitlab-security-oss/cis/gitlabcis
Audits GitLab projects against the CIS GitLab Benchmark via read-only API checks, generating JSON reports on compliance and hardening recommendations.
 qarait/ephemera
Zero-Trust SSH CA
 masriyan/fufufafa
Framework for Unified Flaw & Fault Auditing The ultimate AWS Cloud Security Audit Framework that makes security auditing so easy, you can do it even…
 teycir/apihunter
Async API security scanner in Rust for CORS, CSP, GraphQL, JWT, OpenAPI, and active API posture checks.
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 nightwatchcybersecurity/airflowscan
Checklist and tools for increasing security of Apache Airflow
 nationwide-group-oss/cryptoptic
CodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 noah4ever/sshconfig-lint
Rule-based linter for OpenSSH client config files that detects duplicate hosts, missing identity files, weak algorithms, wildcard ordering issues,…
 rapticore/orenpmguard
Defense Against the Shai-Hulud Supply Chain Attack
 ecomtech-oss/pisc
Public OCI-Image (docker image) Security Checker
 projectdiscovery/naabu-action
A fast port scanner written in go with a focus on reliability and simplicity.