

Log4j-CVE-Detect
 darkarnium/log4j-cve-detect
Detections for CVE-2021-44228 inside of nested binaries
binary-analysiscontainer-securitydevsecops+4
35
darkarnium/log4j-cve-detectDetections for CVE-2021-44228 inside of nested binaries
 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans

 rezmoss/sbomlyze
Git diff for SBOMs—compare CycloneDX, SPDX, and Syft documents, detect tampering, and gate CI.
 lucab85/log4j-cve-2021-44228
Ansible playbook automating Red Hat's Log4j detector script to scan Linux hosts for CVE-2021-44228 (Log4Shell) vulnerability with GPG verification.
 makerchecker/makerchecker
Open-source security gateway & static scanner for AI agents. Enforce role-based access control (RBAC), human-in-the-loop approvals, segregation of…
 manishrawat21/cisa-kev-threat-intel-orchestrator
Zero-touch pipeline that turns newly weaponized CVEs from the CISA Known Exploited Vulnerabilities (KEV) catalog into production-ready Sigma…
 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 brennhill/sloppy-joe
Shields against supply-chain, slopsquatting, and typosquatting attacks from dependencies and code.
 akanthed/secureai-scan
SecureAI-Scan is a CLI tool that scans TypeScript and JavaScript codebases for security issues specific to AI-powered apps — prompt injection, MCP…
 42crunch/api-security-audit-action
Automates static API security auditing of OpenAPI contracts in CI/CD, running 300+ checks for authentication, authorization, and data constraints,…
 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
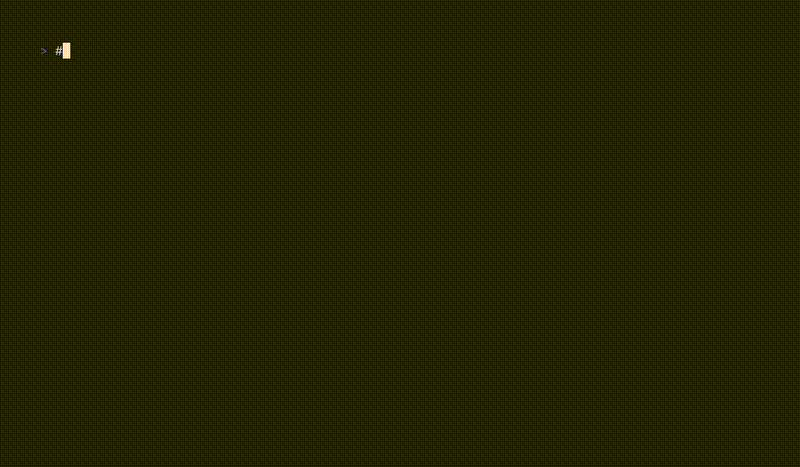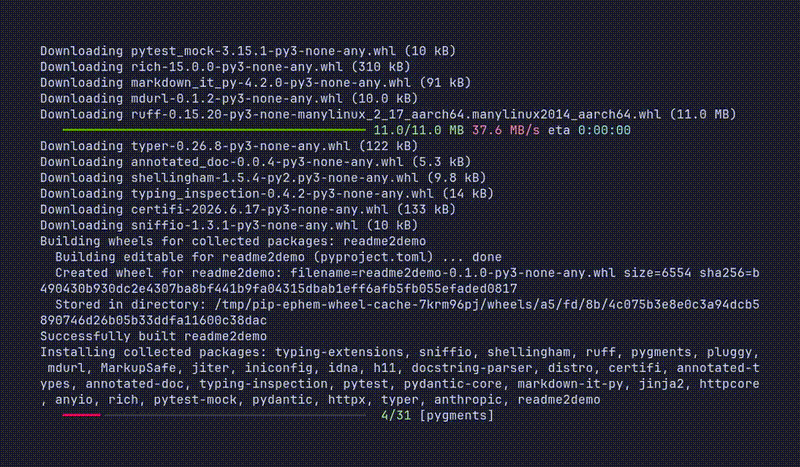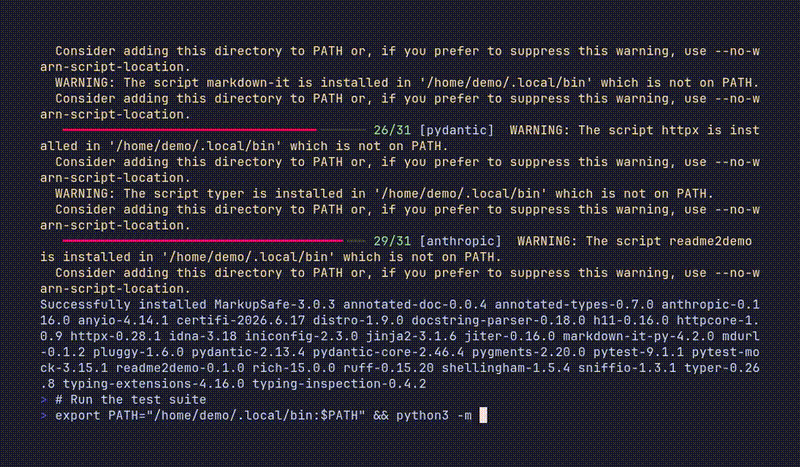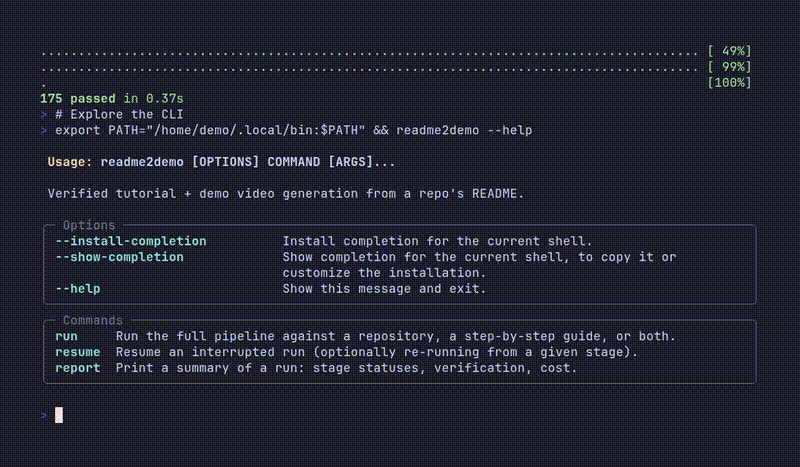 alphacrack/readme2demo
Verified tutorials and demo videos from your README. An AI agent runs it in a hardened Docker sandbox and replays it in a fresh container before…
 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
 0xcyberstan/cve-2026-42533-config-scanner
Static config scanner that flags nginx configs vulnerable to the complex_value two-pass capture-clobbering bug (regex map + regex capture → heap…
 eskatos/creadur-rat-gradle
Apache RAT (Release Audit Tool) Gradle Plugin
 mattijsmoens/intentshield
Pre-execution intent verification for AI agents. Audits what your AI is about to do, not what it says. Zero dependencies, deterministic, hash-sealed.
 gensecaihq/cve-2024-3094-vulnerability-checker-fixer
Shell script and Ansible playbook to detect and remediate CVE-2024-3094 in xz-utils by checking package versions, upgrading or downgrading to a…