
actions-secrets
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
code-analysisdevsecopssecret-detection+1
gmh5225/actions-secretsAdding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 shoucheng3/cov-int
XWiki Commons CVE-2023-31126 v14.10.3 for Coverity analysis
 shoucheng3/spring-cloud__spring-cloud-config_cve-2020-5410_2-1-8-release
Centralized configuration server for distributed systems with HTTP API, Git-backed storage, property encryption/decryption, and integration with…
 kavgan/vuln_test_repo_public_ruby_gemfile_cve-2016-6317
Detects known vulnerabilities in Ruby Gemfile dependencies by scanning for specific CVEs, enabling automated security checks in development pipelines.
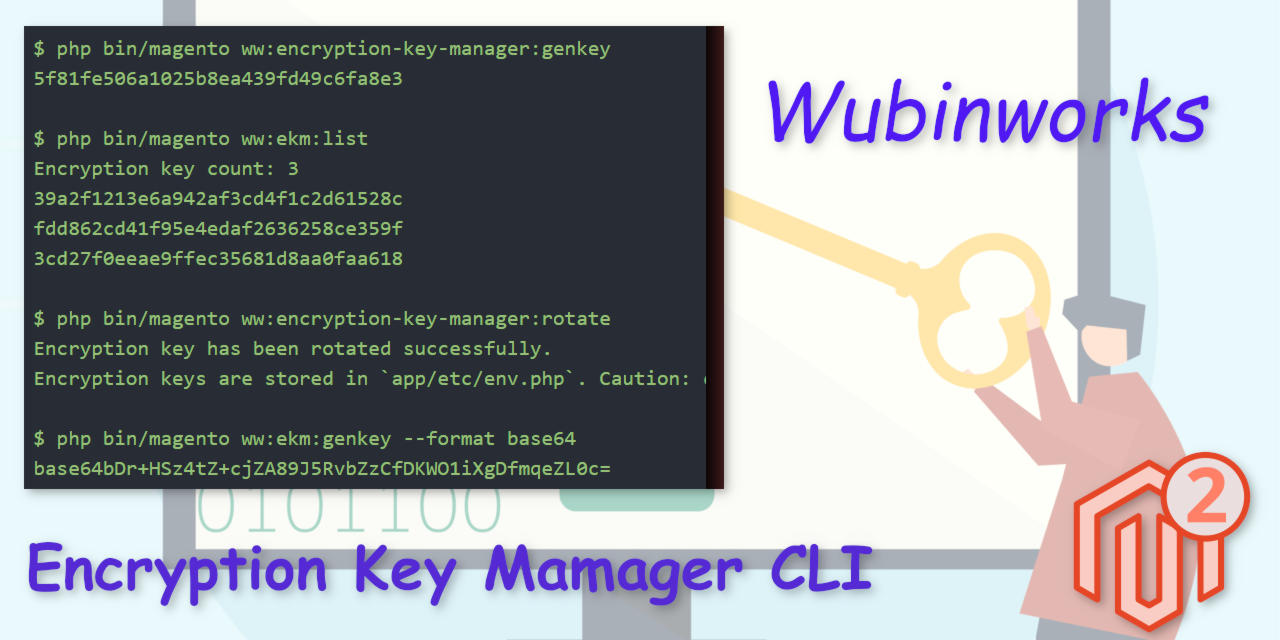 wubinworks/magento2-encryption-key-manager-cli
A utility for Magento 2 encryption key rotation and management. CVE-2024-34102(aka Cosmic Sting) victims can use it as an aftercare.
 shoucheng3/eclipse__hawkbit_cve-2020-27219_0-3-0m6
Domain-independent back end for rolling out software updates to constrained edge devices, controllers, and gateways over IP-based infrastructure,…
 shoucheng3/jenkinsci__workflow-cps-plugin_cve-2022-25173_2646-v6ed3b5b01ff1
Exploit for CVE-2022-25173 targeting Jenkins Pipeline Groovy Plugin's CPS interpreter sandbox bypass, enabling arbitrary code execution within…
 shoucheng3/jenkinsci__workflow-multibranch-plugin_cve-2022-25175_706-vd43c65dec013
Exploit for CVE-2022-25175 targeting Jenkins Pipeline: Multibranch plugin, enabling automated exploitation of a specific vulnerability in CI/CD…
 shoucheng3/payara__payara_cve-2022-37422_5-2022-2
Jakarta EE and MicroProfile application server runtime for development and containerized deployments, supporting cloud-native middleware with…
 atlassion/rs4logj-cve-2021-44228
Provides upgrade and mitigation instructions for Apache Log4j vulnerability CVE-2021-44228 in Remote Syslog products, including version checks and…
 open-aims/log4j
Patched Log4j 1.2.17 library with the vulnerable JMSAppender class removed to mitigate CVE-2021-4104, intended as a drop-in replacement for affected…
 drkbcn/lblfixer_cve_2023_30839
PrestaShop <1.7.8.9 Fix for CVE-2023-30839 and CVE-2023-30545
 shoucheng3/jenkinsci__script-security-plugin_cve-2023-24422_1228.vd93135a_2fb_25
Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…
 shoucheng3/spring-cloud__spring-cloud-config_cve-2020-5405_2-1-6-release
Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…
 melonsmasher/chef_tissues
Install patch for CVE-2017-0145 AKA WannaCry.
 shoucheng3/jenkinsci__docker-commons-plugin_cve-2022-20617_1-17
Jenkins plugin providing shared API for Docker credential management, registry authentication, daemon configuration, and image fingerprinting across…
 shoucheng3/ff4j__ff4j_cve-2022-44262_1_8_13_fixed
Feature toggle framework for Java enabling runtime feature activation, role-based access, AOP-driven toggling, monitoring, audit trails, and a web…
 mightysai1997/cve-2024-3094
Shell scripts to detect CVE-2024-3094 backdoor in liblzma5 across Kubernetes pods and Docker containers, with SBOM generation via Trivy for…