

check_struts
 andypitcher/check_struts
Apache Struts version analyzer (Ansible) based on CVE-2017-5638
cloud-securityconfiguration-auditingdevsecops+3
27 years ago
andypitcher/check_strutsApache Struts version analyzer (Ansible) based on CVE-2017-5638
 devopstoday11/tarian
Anti-Virus for K8s. Protect your Applications running on Kubernetes from malicious attacks with pre-registered source code, runtime processes…
 apsl/salt-shellshock
Salt recipe for shellshock (CVE-2014-6271)
 jrmurray000/cve-2020-8554
OPA Gatekeeper-based policy templates to mitigate CVE-2020-8554 by restricting Kubernetes Service external IPs to an allow list, preventing traffic…
 liamromanis101/cifswitch-check
Detection script for CIFSwitch - CVE-2026-46243
 nexaiceo/nexus-os
The Governed Agentic AI Operating System — Rust + Tauri 2.0 | 65 crates, 658 commands, 84 pages, 5,029 tests, 10/10 OWASP
 cj667113/oci-ansible-fix-cve-2026-31431
Ansible playbook that automates remediation of CVE-2026-31431 (Copy Fail) on OCI Linux instances by installing updated kernel packages, rebooting,…
 flyniu666/ingress-nginx-0.21-1.19.5
based on nginx 1.19.5 to fix for CVE-2018-16843, CVE-2018-16844, CVE-2019-9511, CVE-2019-9513, and CVE-2019-9516
 mgiay/cve-2026-8053-mongodb
Desc "CVE-2026-8053 CHECKER"-20260518-16h30-GMT+7
 yakovyakov/cve-2026-31431-mitigation
Detection and mitigation tooling for CVE-2026-31431 (Copy Fail) on Linux kernels. Includes Phalanx-CCS and Silent4Labs scripts plus an Ansible…
 contrast-security-oss/cve-2021-44228
Professional Service scripts to aid in the identification of affected Java applications in TeamServer
 trickyearlobe/inspec-log4j
An Inspec profile to check for Log4j CVE-2021-44228 and CVE-2021-45046
 salman-sec/patch-management-
Scenario-based training exercise for IT administrators: identify, approve, and deploy critical patches for financial systems under a 48-hour SLA…
 pvharmo2/gha-lab-2f775f277c
Authorized lab reproduction of CVE-2025-47928 (spotipy-dev/spotipy pull_request_target secrets exfiltration) — snapshot at vulnerable commit 4f5759d
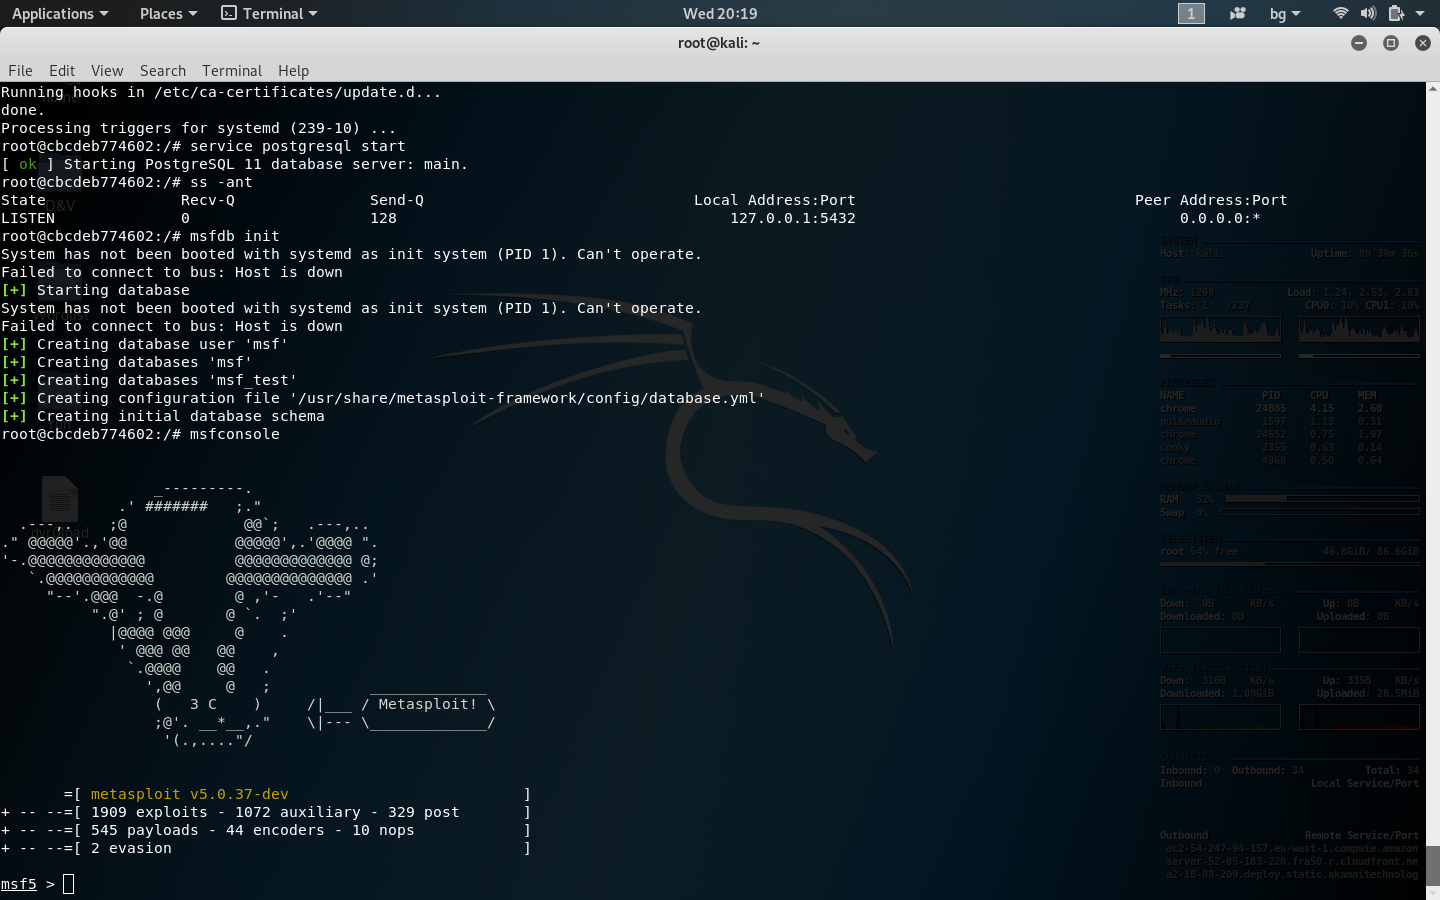 nu11secur1ty/kali-linux-docker
kali-linux-docker
 gouldnicholas/cve-2026-4660-poc
PoC for CVE-2026-4660: arbitrary file read via git checkout in hashicorp/go-getter
 dolutech/patch-manual-cve-2025-26465-e-cve-2025-26466
Patch Manual para a correção das CVE-2025-26465-e-CVE-2025-26466, para sistemas sem update do OpenSSH
 alexzorin/cve-2017-2636-el
Ansible role for workaround for CVE-2017-2636 (Red Hat) - https://access.redhat.com/security/cve/CVE-2017-2636