

GitLeaks
 niclas-zone/ci/gitleaks
CI component for Gitleaks SAST tool that scans git repositories for hardcoded secrets, API keys, and tokens with custom and remote configuration…
code-analysisdevsecopssecret-detection+1
1
niclas-zone/ci/gitleaksCI component for Gitleaks SAST tool that scans git repositories for hardcoded secrets, API keys, and tokens with custom and remote configuration…
 devopstoday11/tarian
Anti-Virus for K8s. Protect your Applications running on Kubernetes from malicious attacks with pre-registered source code, runtime processes…
 hackervlogofficial/cve-2026-23918
This is a proactive tool for security auditing. For your GitHub repository, you’ll want a description that highlights its safety (non-intrusive) and…
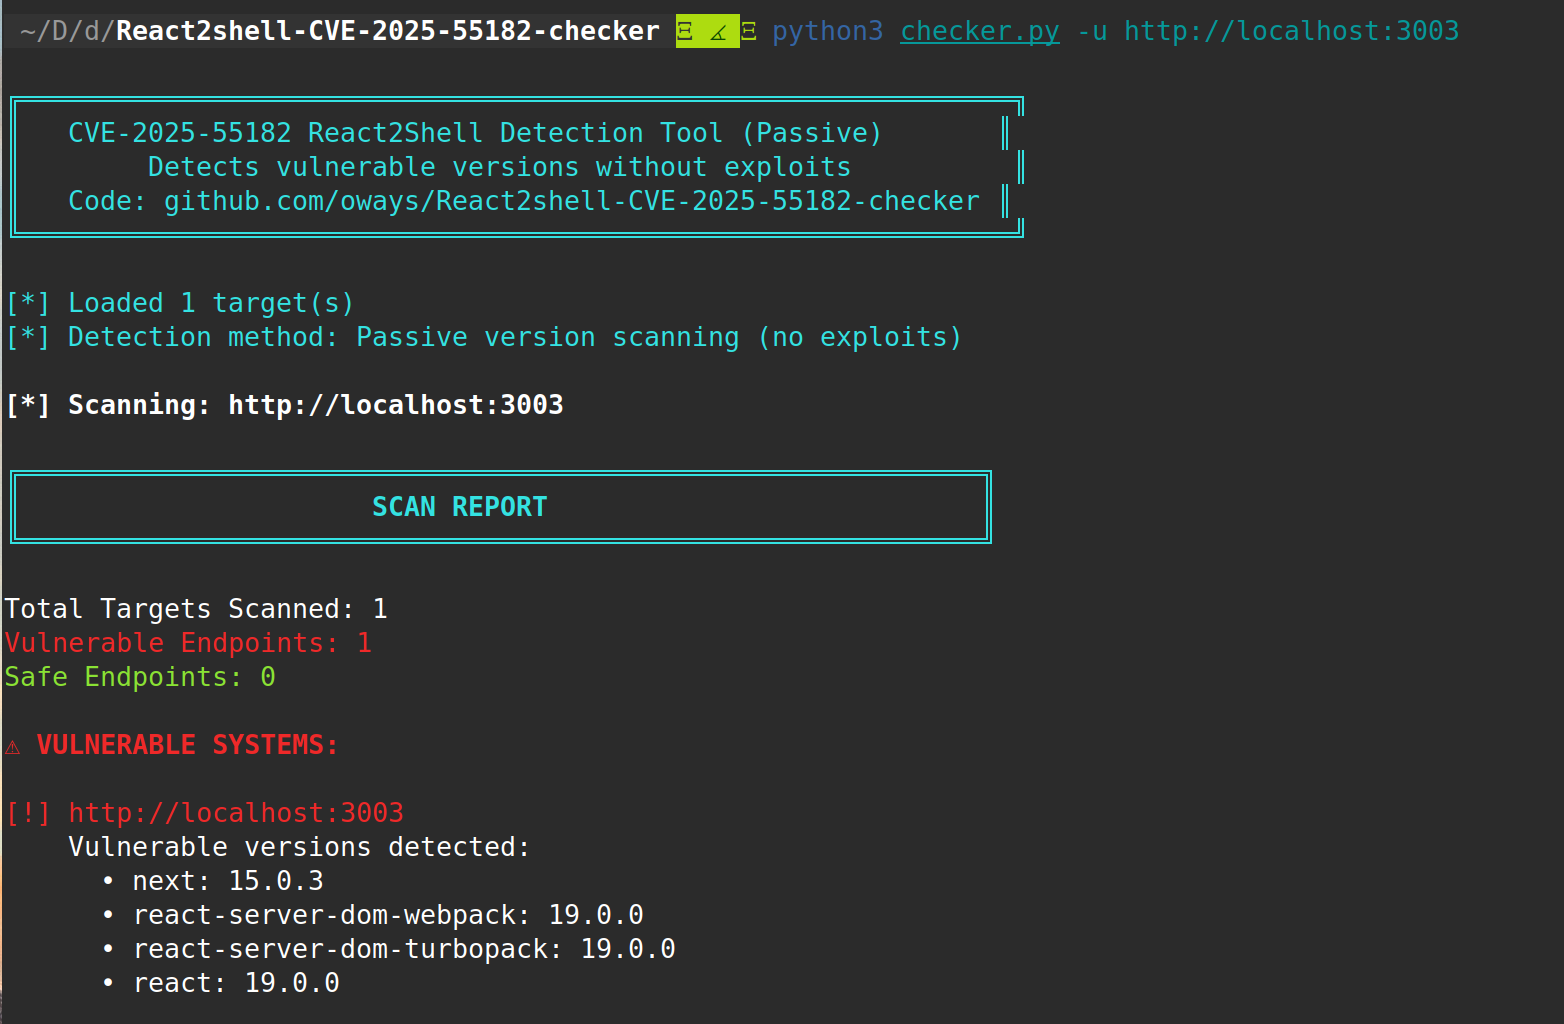 oways/react2shell-cve-2025-55182-checker
Passive CVE-2025-55182 detection tool for vulnerable React Server Components. Scans package.json, JavaScript bundles, HTTP headers, and API endpoints…
 shivang0/guardmodel
GitHub Action that scans ML model files for malicious code and security vulnerabilities
 gouldnicholas/cve-2026-4660-poc
PoC for CVE-2026-4660: arbitrary file read via git checkout in hashicorp/go-getter
 joaoreis13/flight-risk
Security toolkit for CVE-2025-55182 (React2Shell) — scan, detect, correlate, and test React Server Components RCE vulnerability
 apsl/salt-shellshock
Salt recipe for shellshock (CVE-2014-6271)
 flyniu666/ingress-nginx-0.21-1.19.5
based on nginx 1.19.5 to fix for CVE-2018-16843, CVE-2018-16844, CVE-2019-9511, CVE-2019-9513, and CVE-2019-9516
 joltcan/ansible-role-cve-2026-31431
Ansible role that applies and verifies the modprobe.d mitigation for CVE-2026-31431 by disabling the algif_aead kernel module, with safety checks for…
 omerati/almalinux-fix-cve-2026-31431
Automates kernel patching for CVE-2026-31431 and Dirty Frag, sets secure kernel as default in GRUB, and disables testing repo for production safety.
 paulorlima9/copyfail-fix
Quick mitigation and patch script for CVE-2026-31431 (Copy Fail) on Ubuntu/Debian VPS
 eximiait/cve-2026-31431
Ansible playbooks to check and mitigate CVE-2026-31431 on Linux hosts, with scripts for local, remote, and containerized environments, including…
 net0bsd/mitigaciones
Automated detection and mitigation of CVE-2026-31431 local privilege escalation on Linux via Bash scripts and Ansible playbooks, with CIS-standard…
 tailwindrg/cve-2026-0300-audit
Read-only audit tooling for CVE-2026-0300 (PAN-OS User-ID Authentication Portal exposure)
 wavesman/cve-2026-31431-fleet-remediator
Fleet-scale CVE-2026-31431 audit and remediation orchestrator for Linux hosts via SSH, with strict host-key verification and multi-format reporting.
 kavin71725/cve-2025-12543-fix-for-wildfly
Docker base image with backported Host header validation fix for CVE-2025-12543 in Undertow 1.4.x, enabling secure deployment of WildFly 11…
 cybergabisoft/depalert
DepAlert is an open-source security gate for your CI/CD pipeline. It analyzes SBOMs against malware intelligence data and quickly tells you whether…