
envsec
 davidnussio/envsec
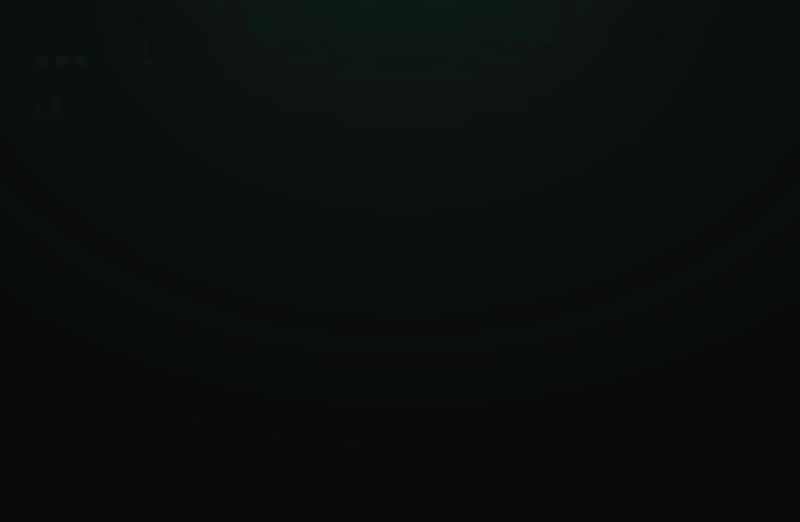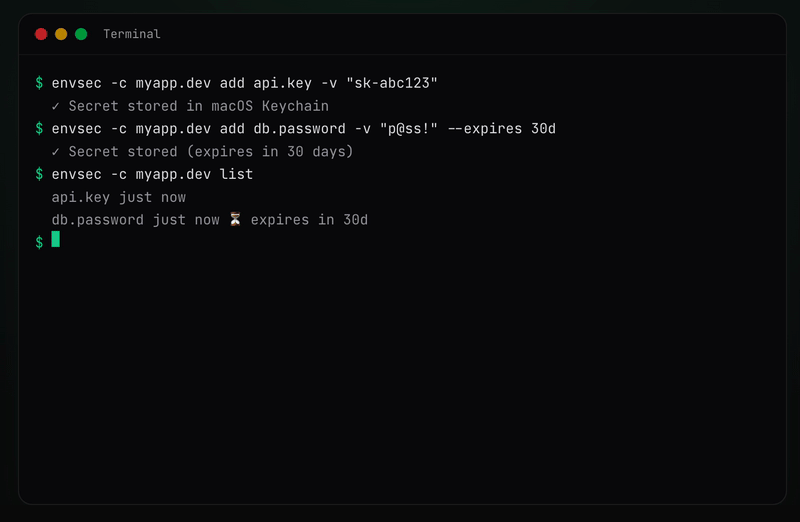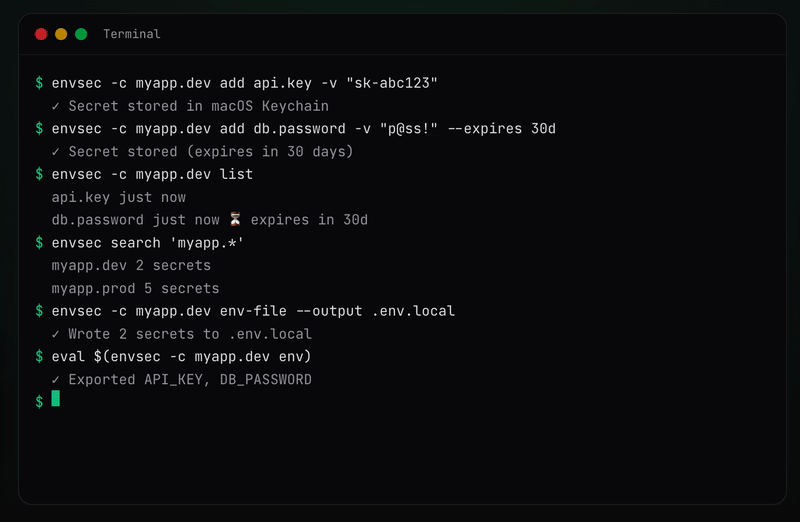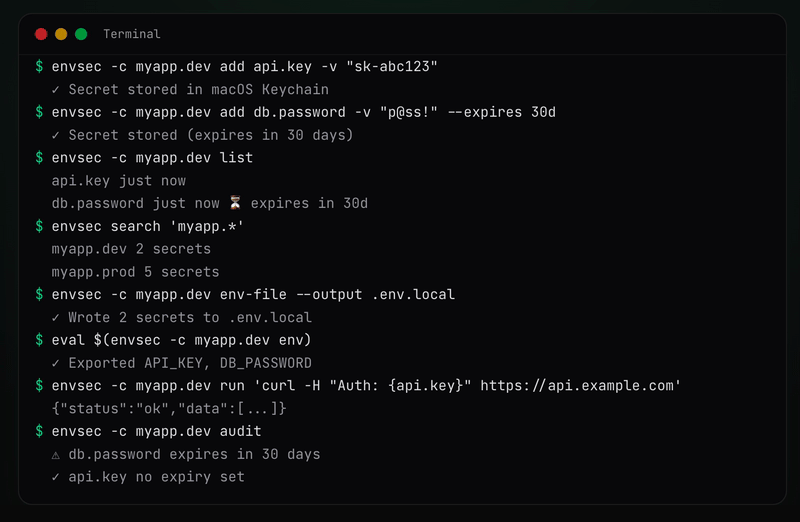
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)
authentication-authorizationcloud-securitydevsecops+3
16
davidnussio/envsecSecure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)
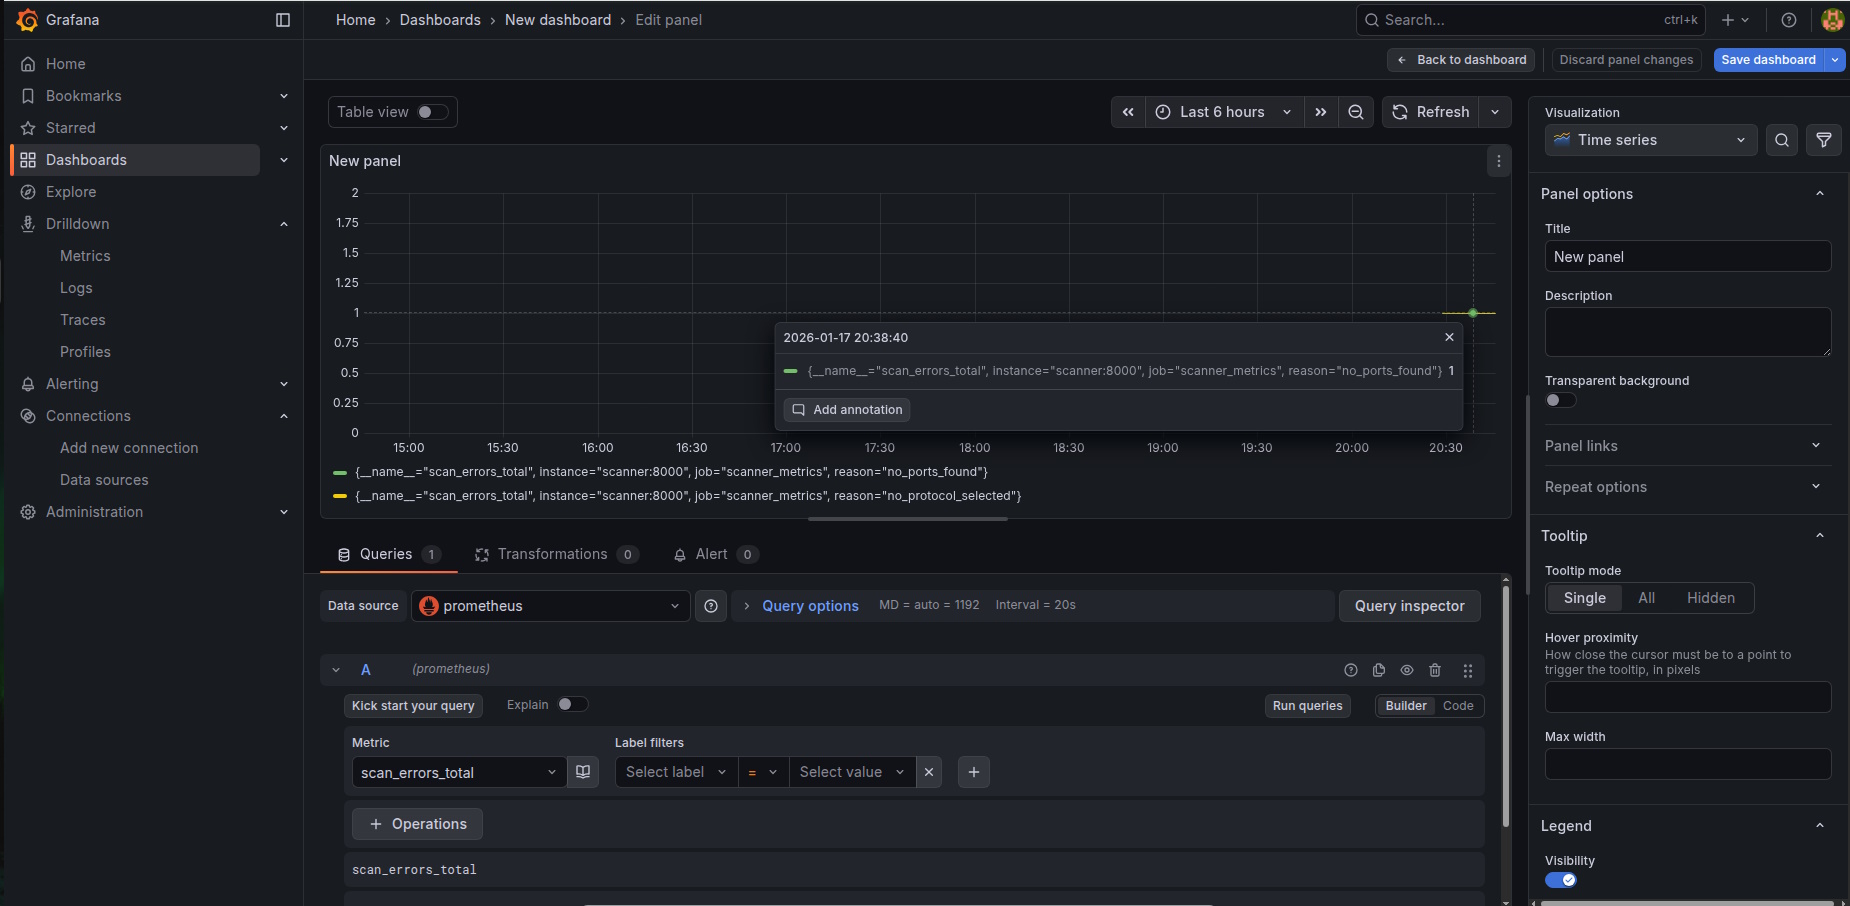 znakar/sharktooth
Port Scanner with Docker & Prometheus + Grafana integration. A tool for network auditing with multithreading support and real-time monitoring.
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…
 hackervlogofficial/cve-2026-23918
This is a proactive tool for security auditing. For your GitHub repository, you’ll want a description that highlights its safety (non-intrusive) and…
 facebook/infer
A static analyzer for Java, C, C++, and Objective-C
 pypa/pip-audit
Audits Python environments, requirements files and dependency trees for known security vulnerabilities, and can automatically fix them
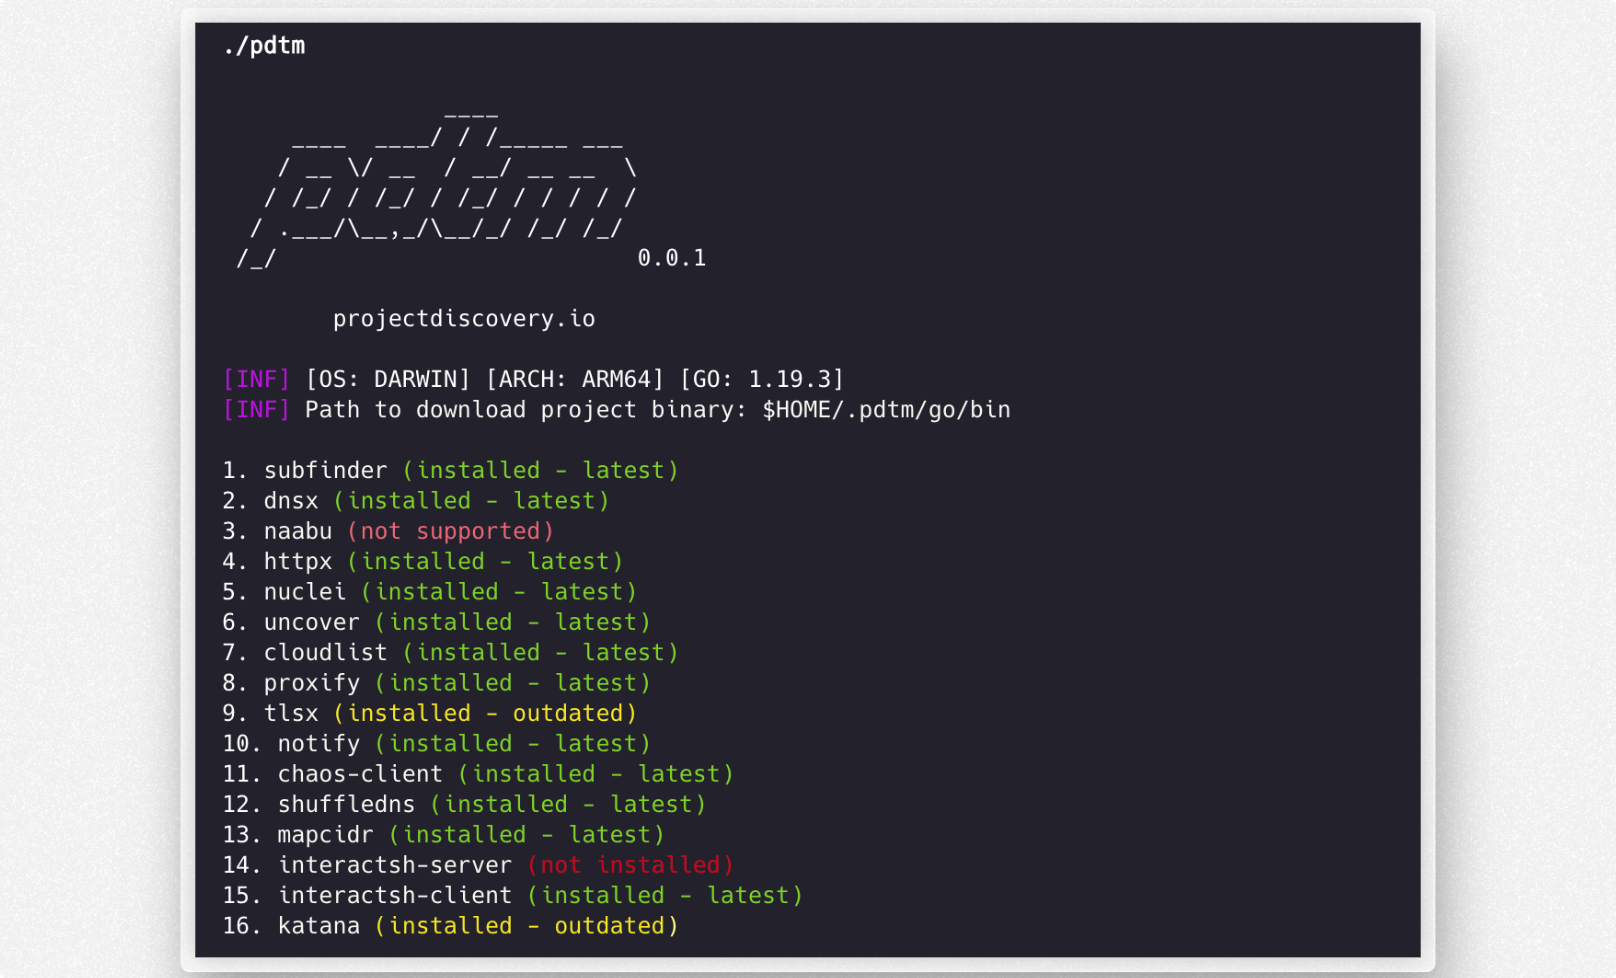 projectdiscovery/pdtm
ProjectDiscovery's Open Source Tool Manager
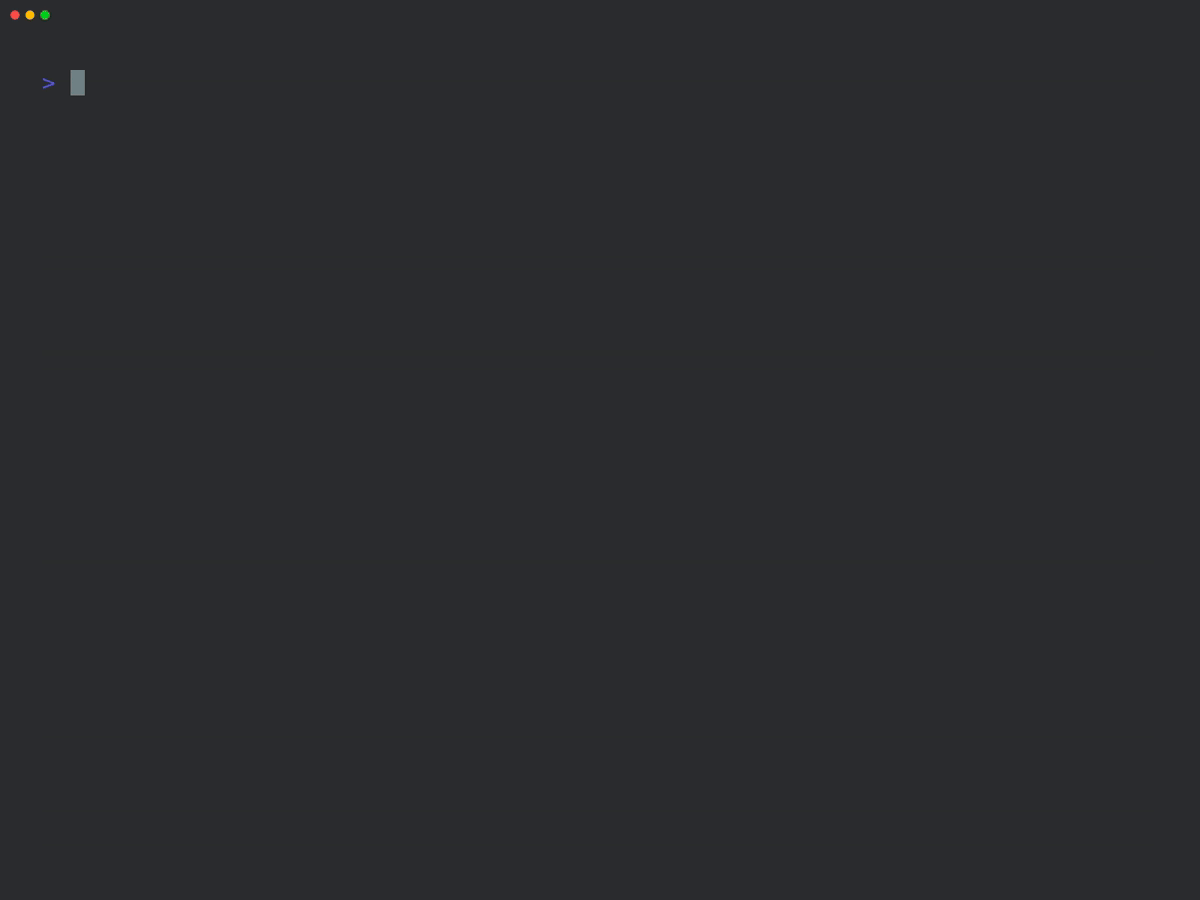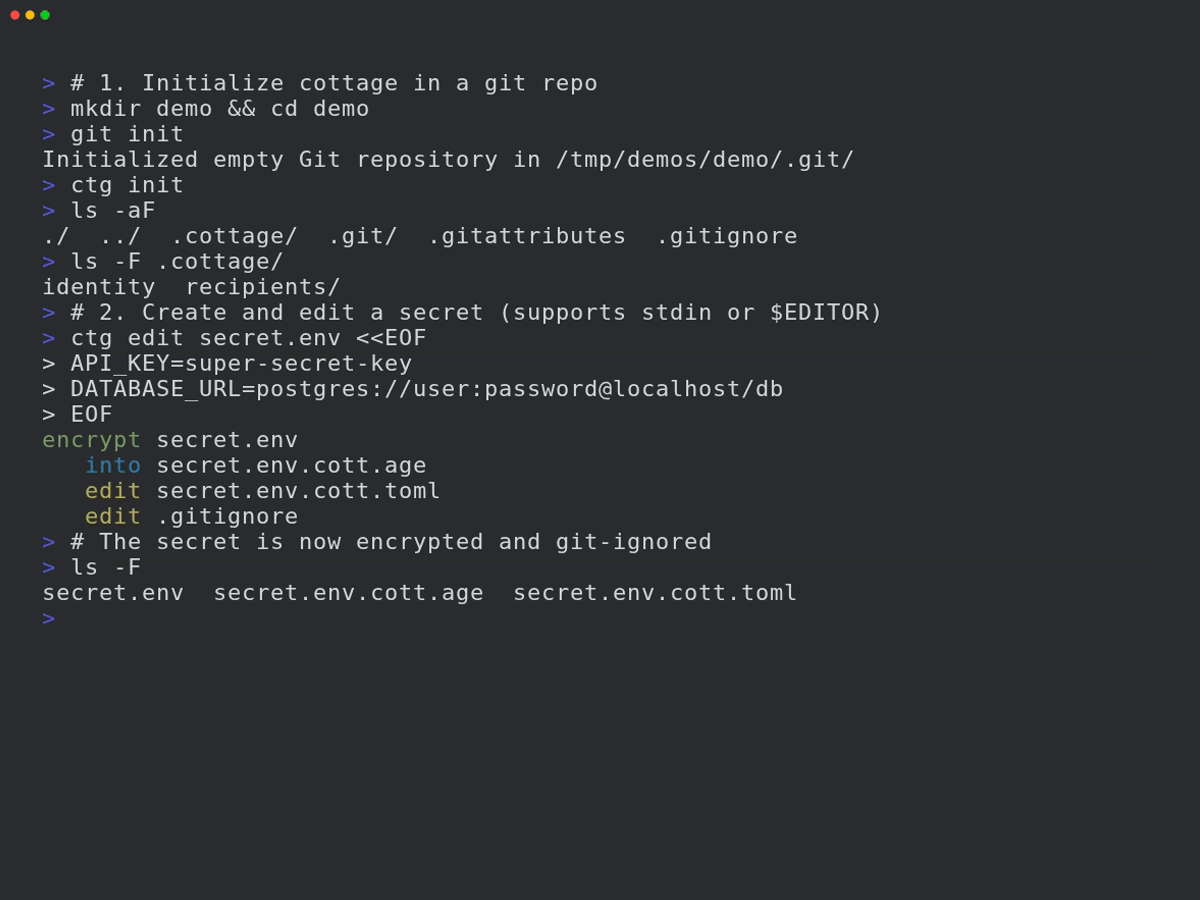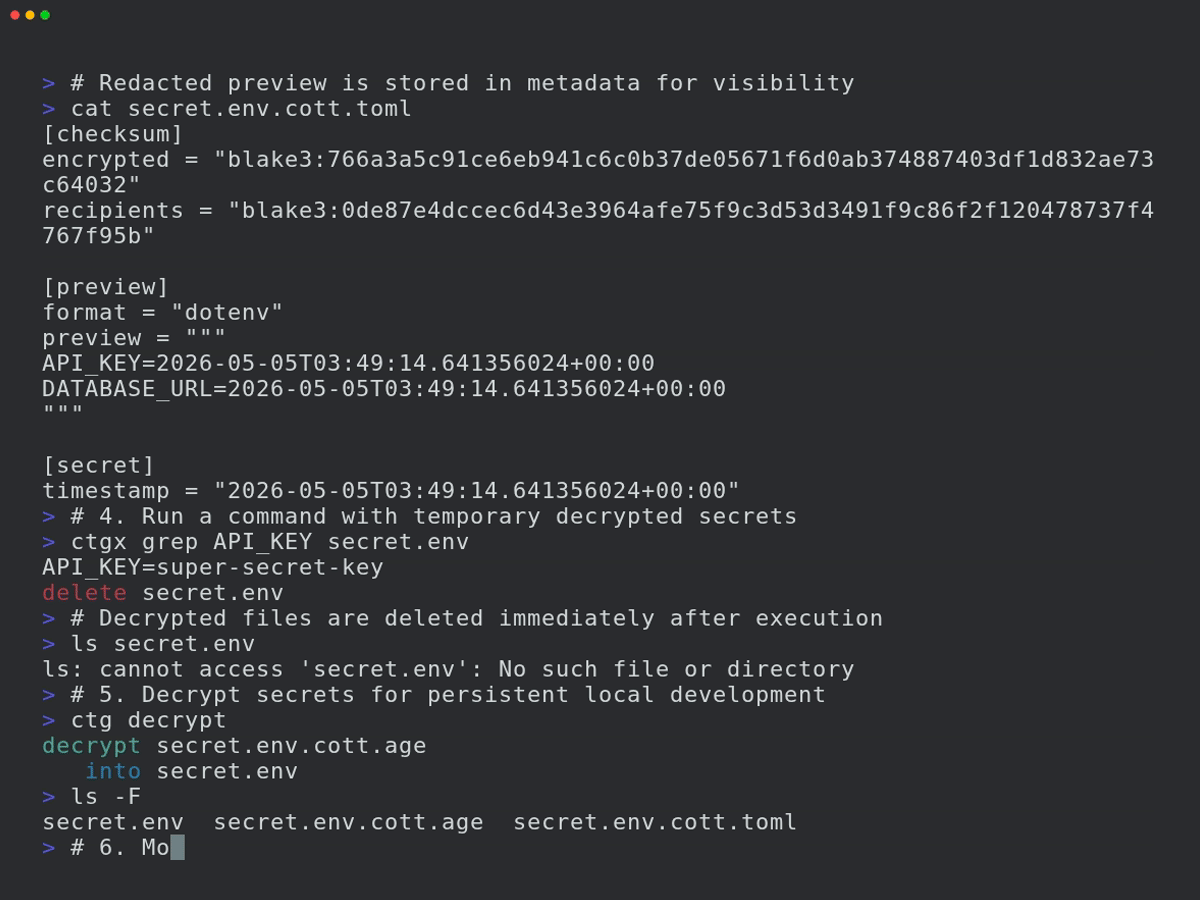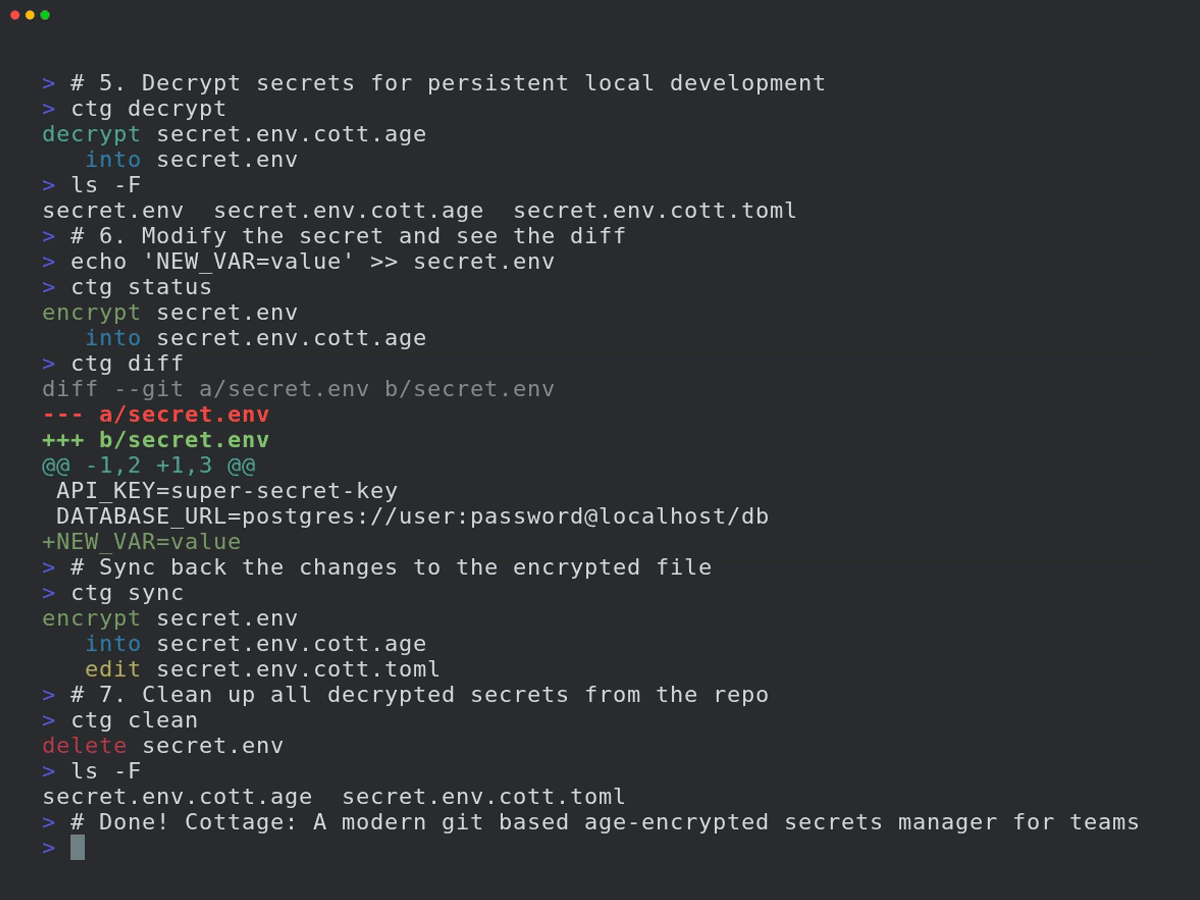 sayanarijit/cottage
A modern git based age-encrypted secrets manager for teams.
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 reverseclabs/azuredevops-enum
Read-only Azure DevOps enumeration tool that queries the REST API to surface projects, repositories, service connections, builds, pipeline secrets,…
 coinbase/salus
We would like to request that all contributors please clone a *fresh copy* of this repository since the September 21st maintenance.
 tillson/git-hound
Fast GitHub recon tool. Scans for leaked secrets across all of GitHub, not just known repos and orgs. Support for GitHub dorks.
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 scopeblind/scopeblind-gateway
Ed25519 signed receipts + Cedar policies for AI agents. Finance mandate gate (Legate), proof packs, 3 IETF Internet-Drafts. npx protect-mcp
 az9713/cve-lite-on-pi
Running OWASP cve-lite-cli against the pi monorepo: scan journey and key finding (vitest CVE-2026-47429).
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
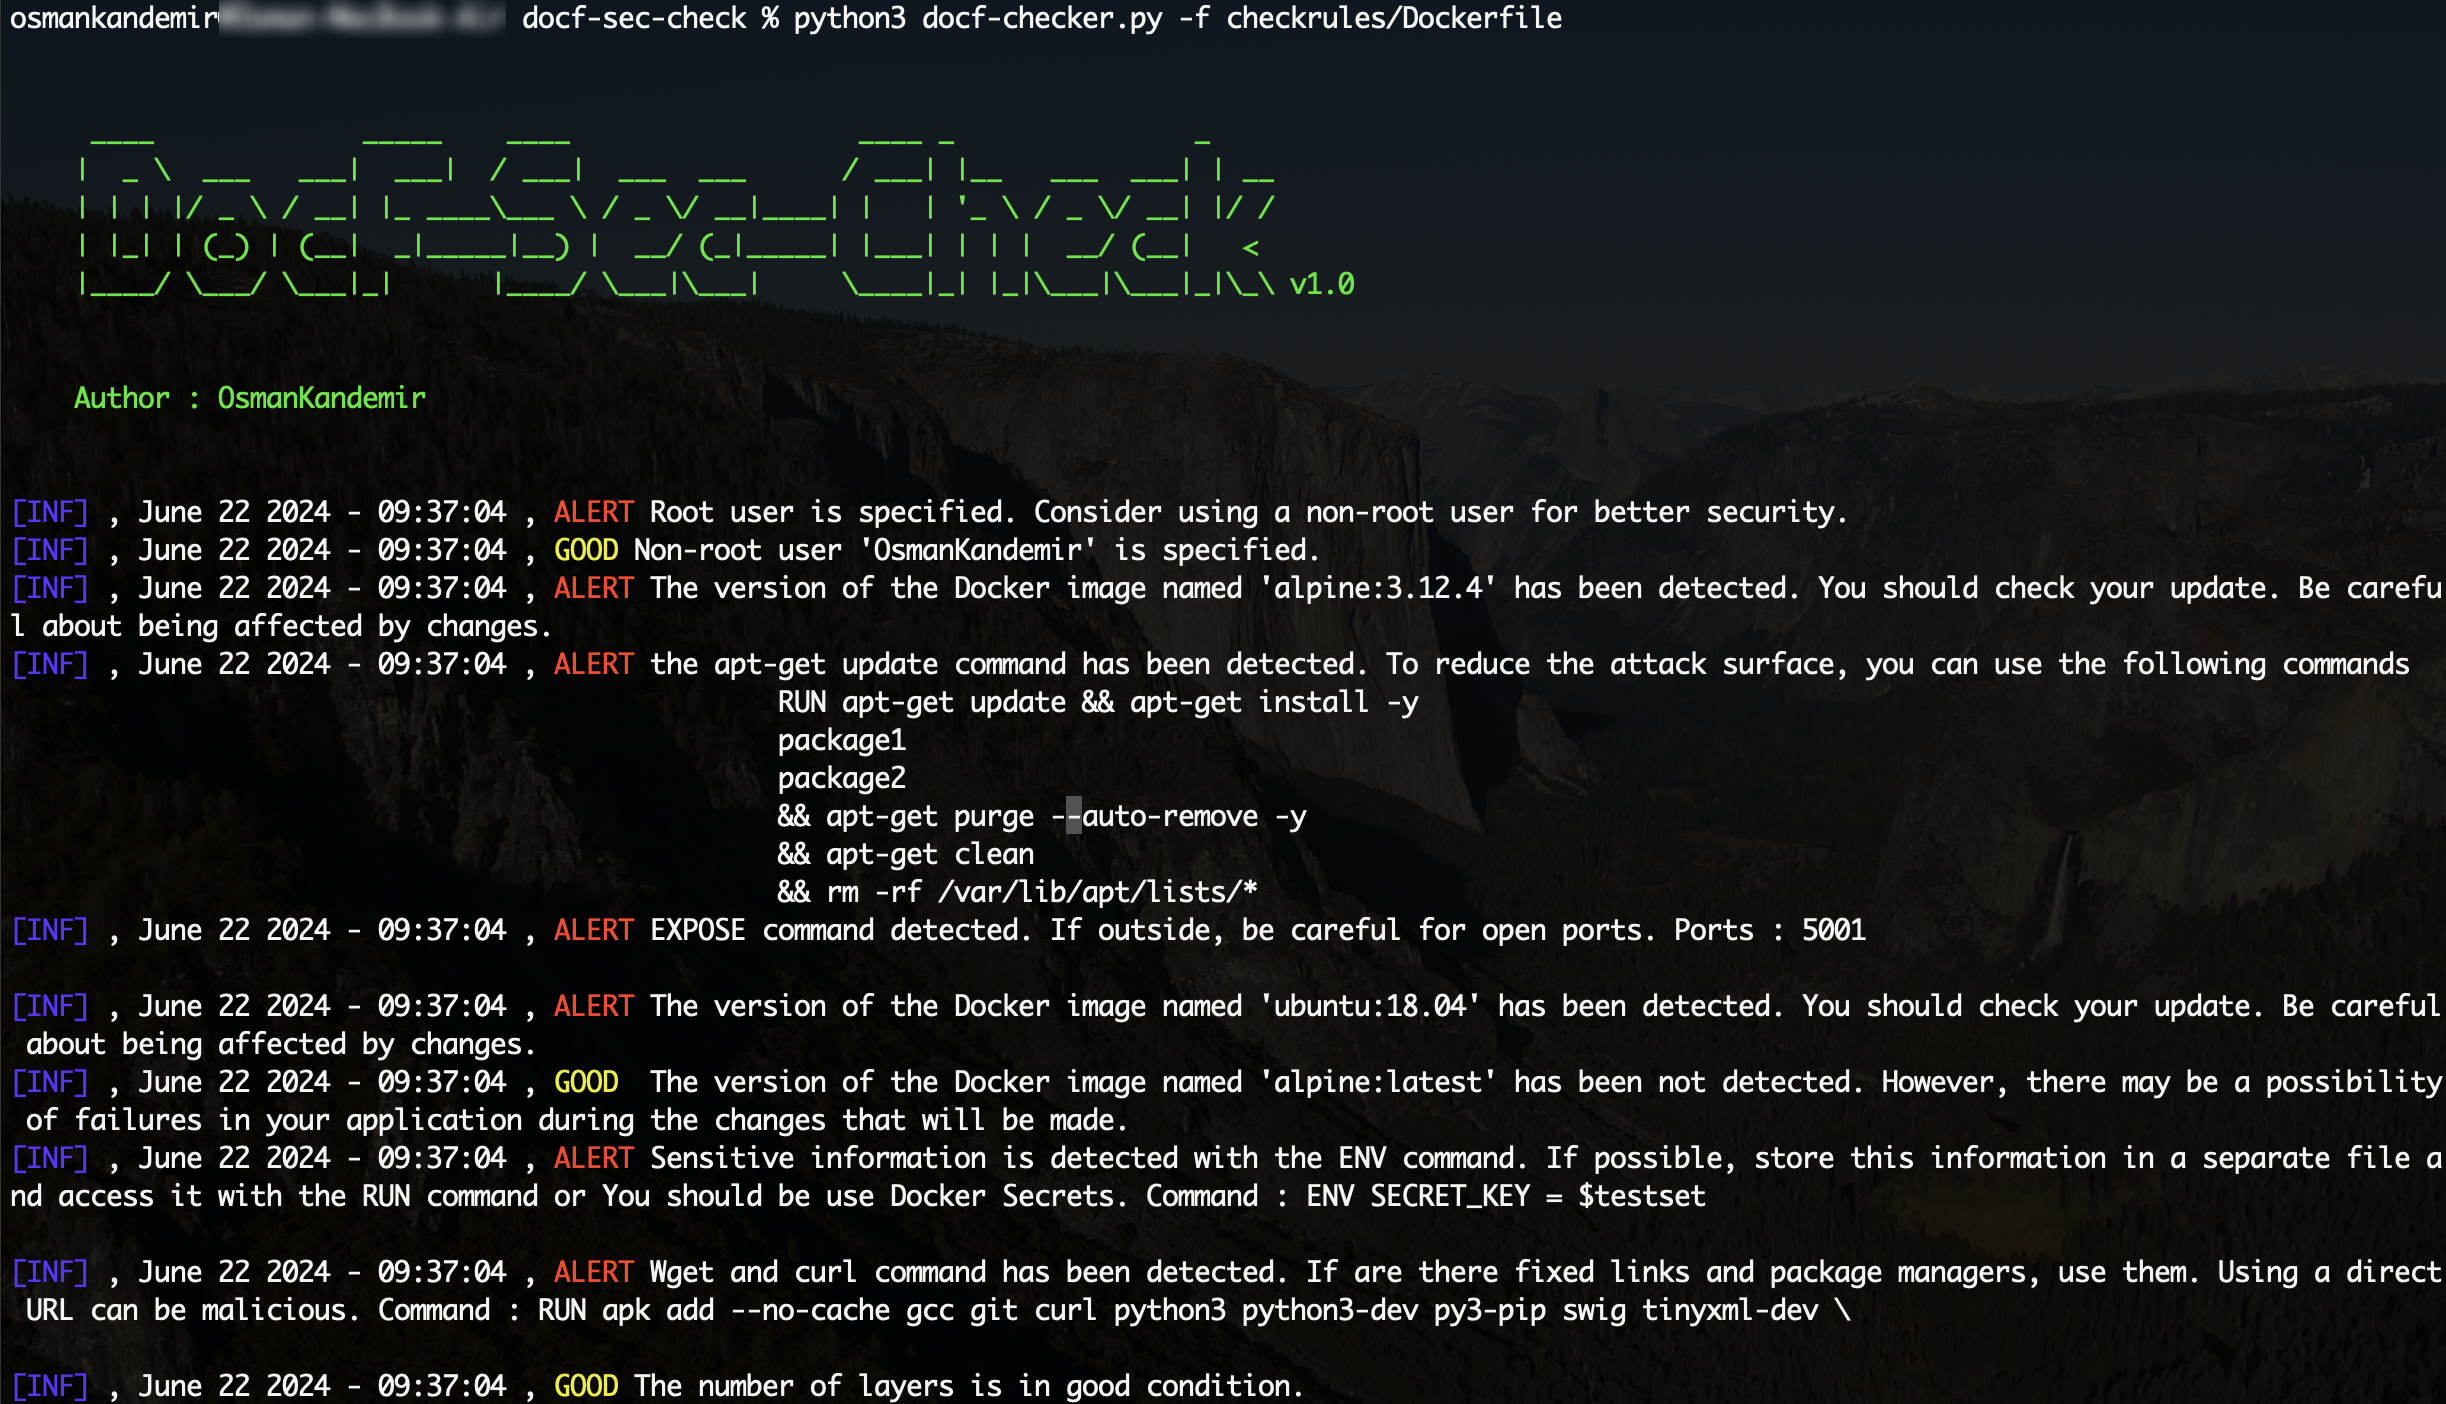 osmankandemir/docf-sec-check
Static analysis tool that scans Dockerfiles for insecure commands and configuration issues, providing actionable security notifications to harden…