
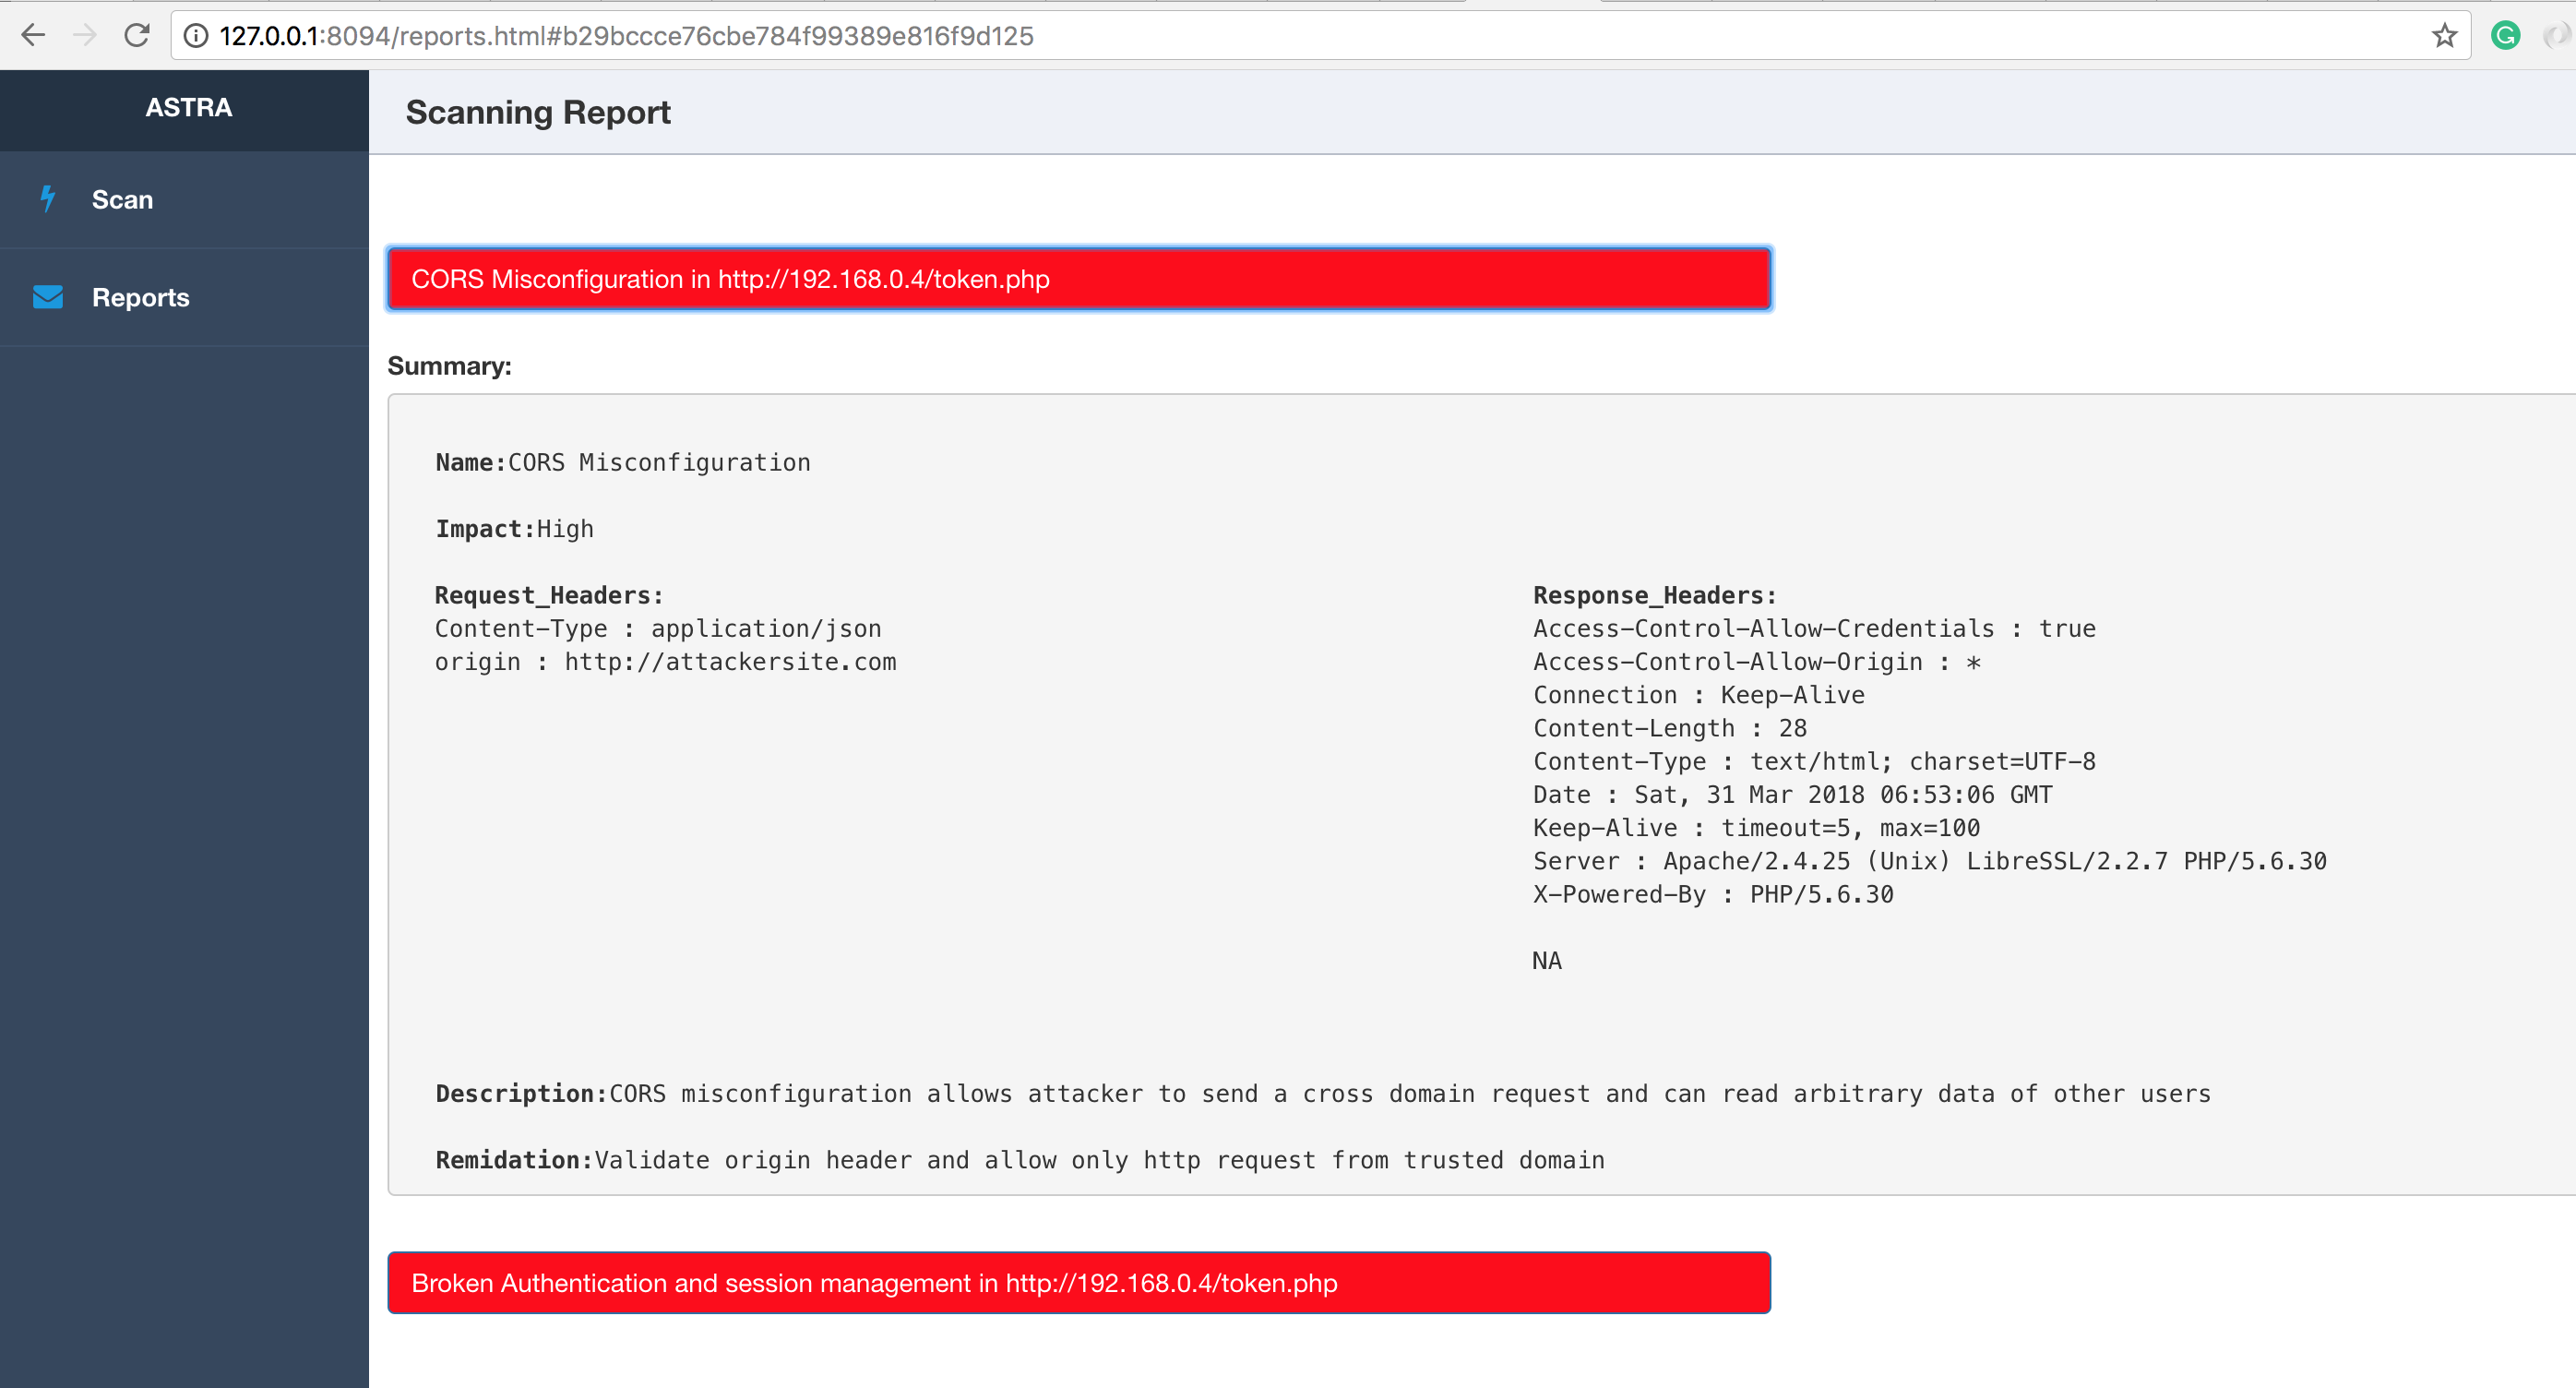
Astra
 flipkart-incubator/astra
Automated Security Testing For REST API's
api-security-testingdevsecopspenetration-testing+2
flipkart-incubator/astraAutomated Security Testing For REST API's
 bearer/bearer
Code security scanning tool (SAST) to discover, filter and prioritize security and privacy risks.
 owasp-noir/noir
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
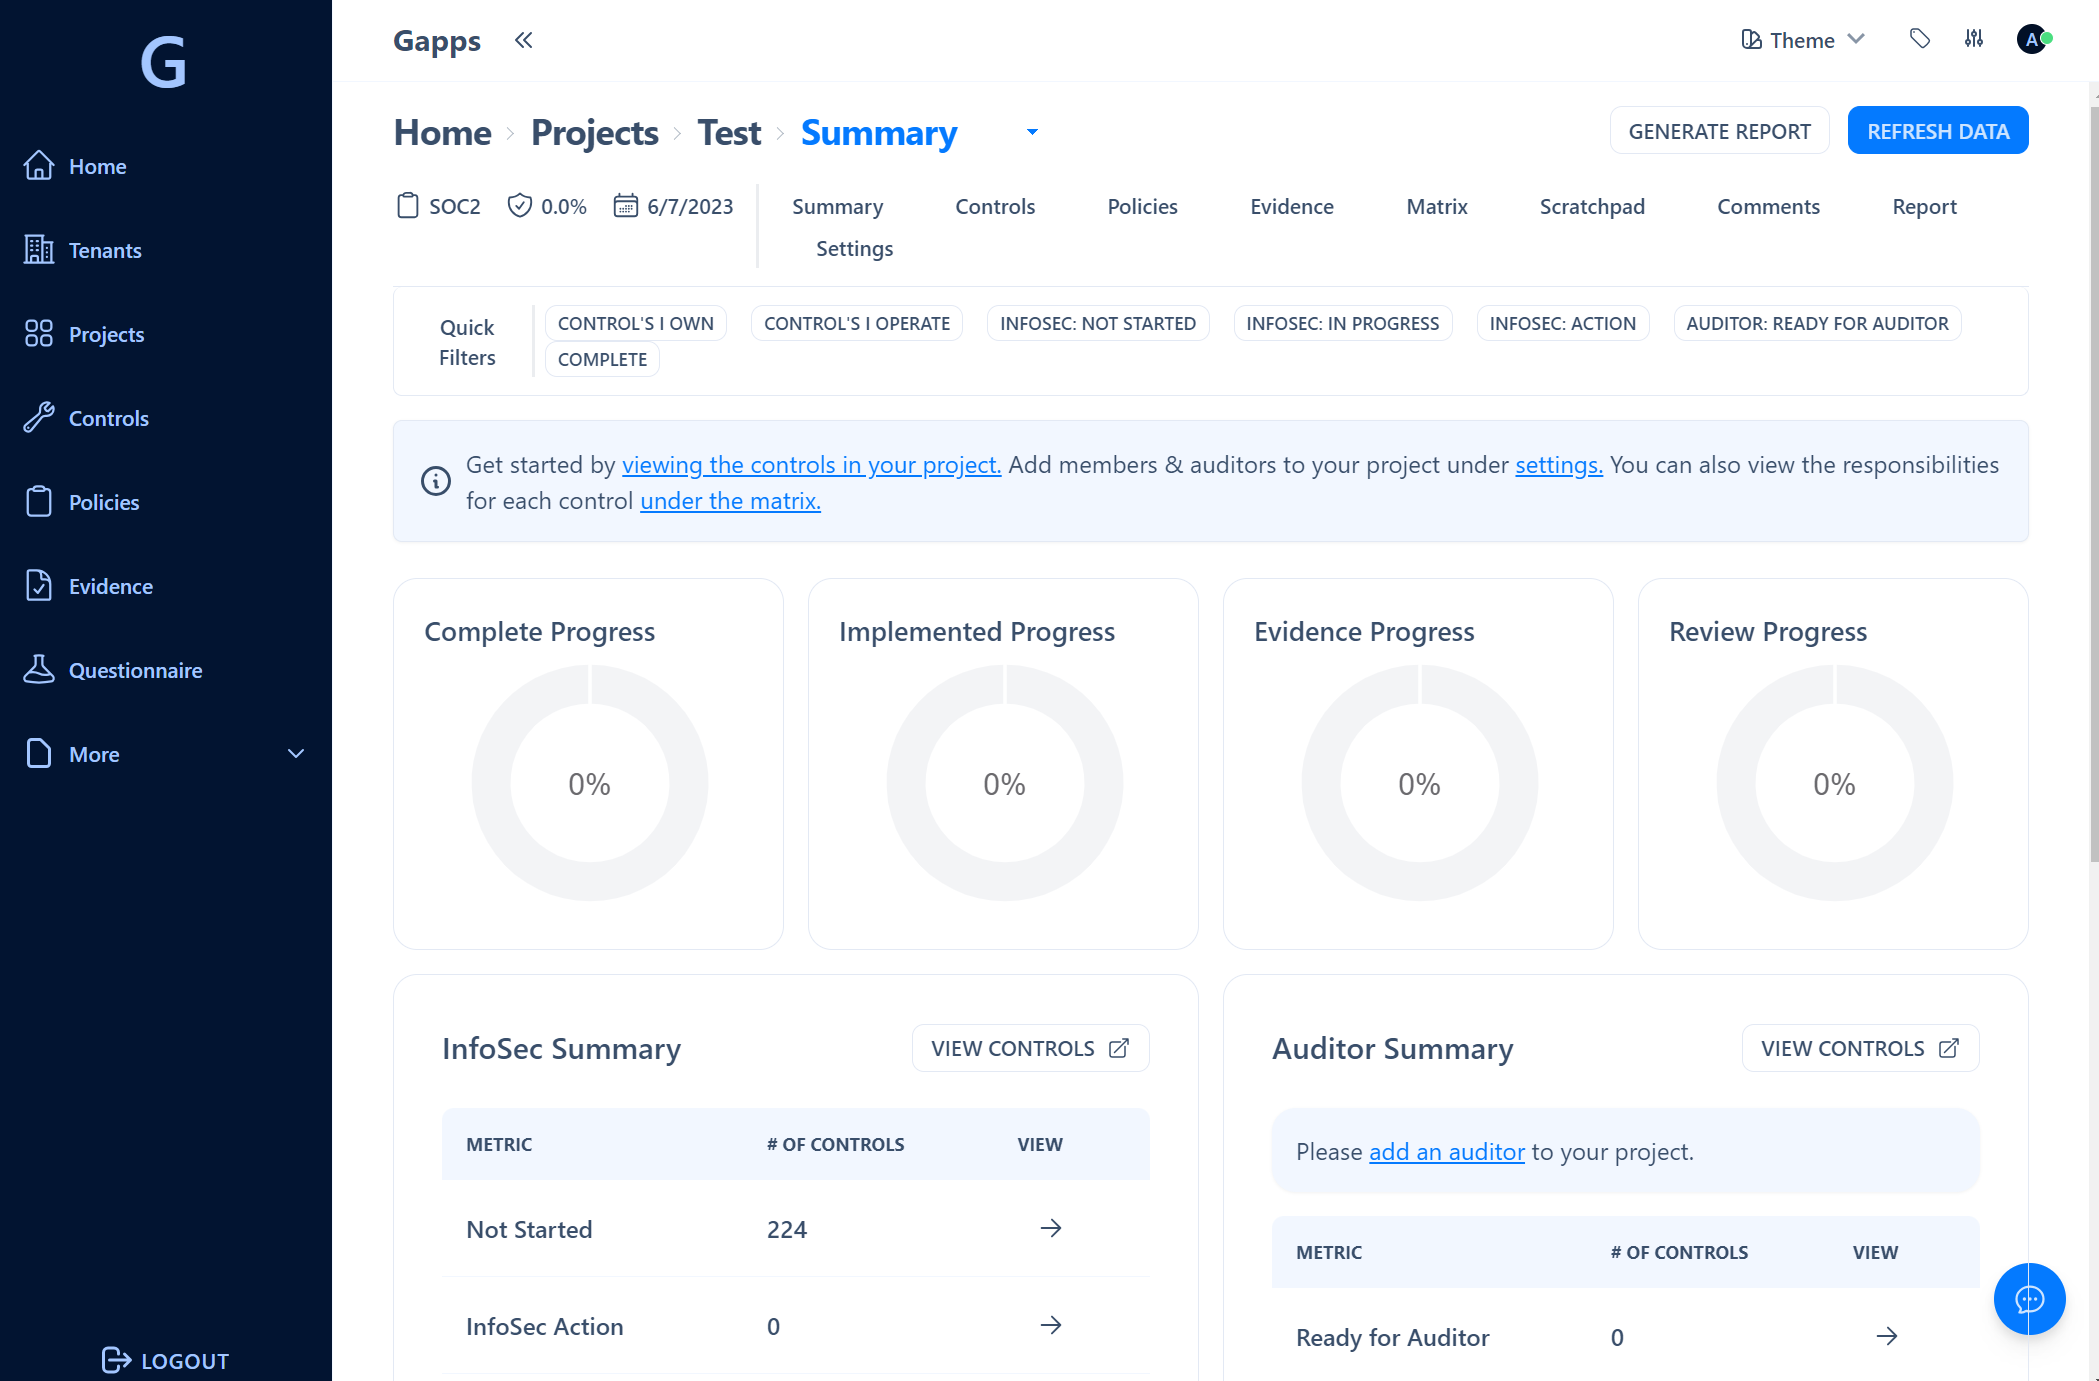 bmarsh9/gapps
Security compliance platform - SOC2, CMMC, ASVS, ISO27001, HIPAA, NIST CSF, NIST 800-53, CSC CIS 18, PCI DSS, SSF tracking
 cyclonedx/cyclonedx-cli
CLI for generating, analyzing, merging, diffing, validating, signing, and converting CycloneDX SBOMs across JSON, XML, Protobuf, CSV, and SPDX…
 bbva/apicheck
The DevSecOps toolset for REST APIs
 crucible-security/crucible
pytest for AI agents - Autonomous red-teaming, behavioral monitoring & security testing for LLM agents
 vhscom/private-landing
🔐 Learn authentication by building it right. An extensible, standards-compliant reference implementation for Cloudflare Workers with Hono, Turso,…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 owasp/owasp-aibom
OWASP project defining an AI Bill of Materials (AIBOM) standard to document AI/ML components, dependencies, and supply chain risks for AI security…
 owasp/pscf
OWASP framework providing structured security capabilities for software products, derived from regulatory and industry standards analysis to guide…
 owasp/security-culture
OWASP Security Culture repository
 owasp/teach-appsec
OWASP teaching modules covering application security fundamentals including risk management, secure software development, and operations security for…
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
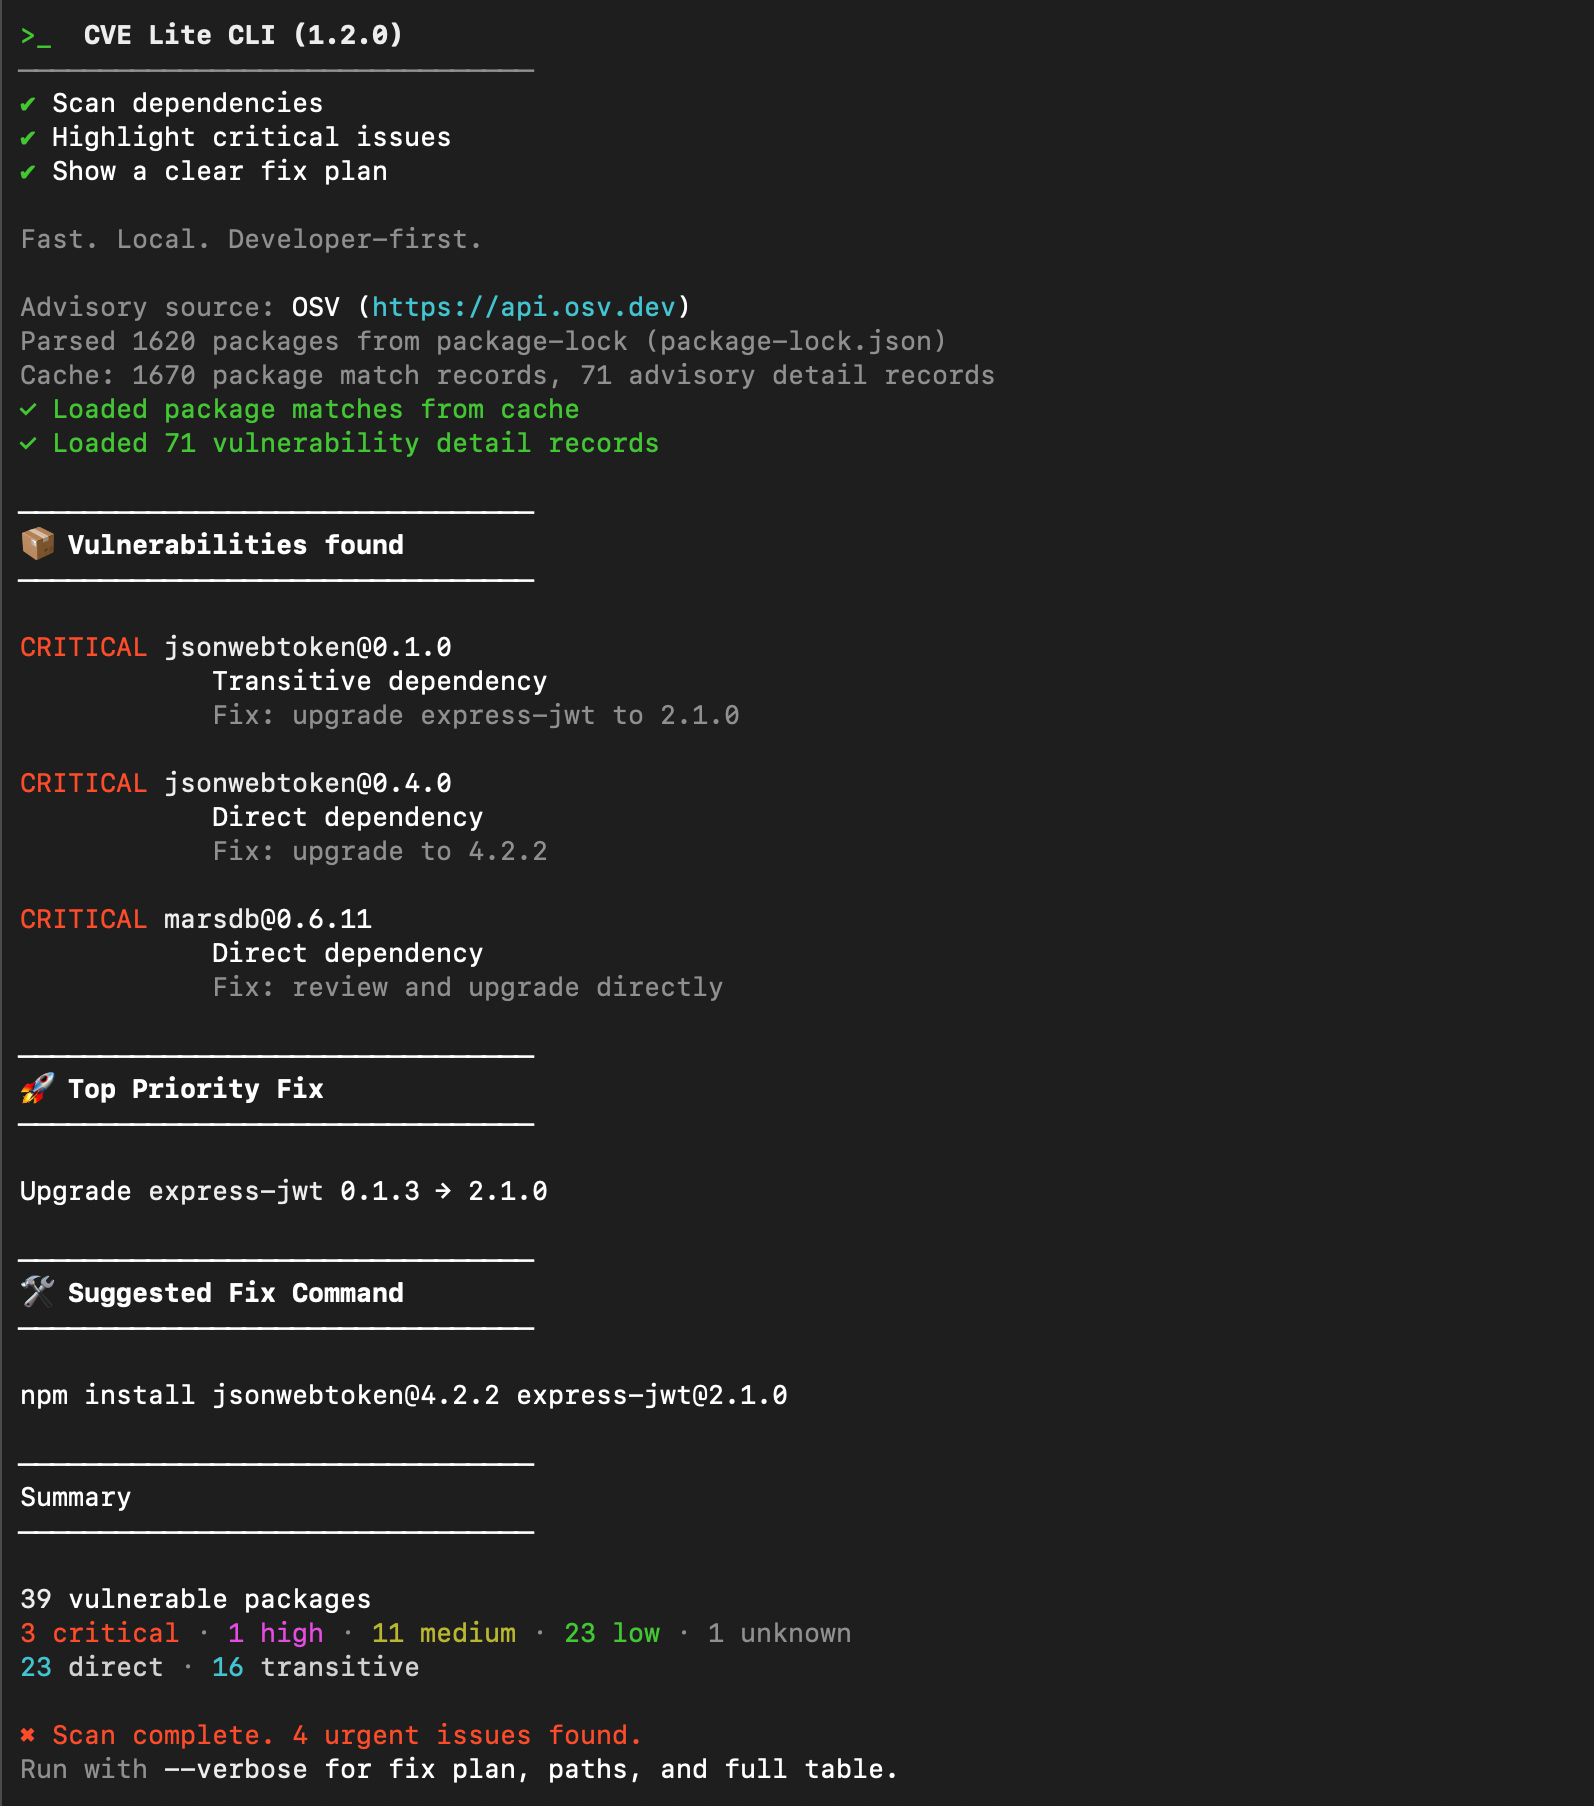 owasp/cve-lite-cli
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
 owasp/docker-security
Getting a handle on container security