
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 manishrawat21/cisa-kev-threat-intel-orchestrator
Zero-touch pipeline that turns newly weaponized CVEs from the CISA Known Exploited Vulnerabilities (KEV) catalog into production-ready Sigma…
 pirafrank/vault-conductor
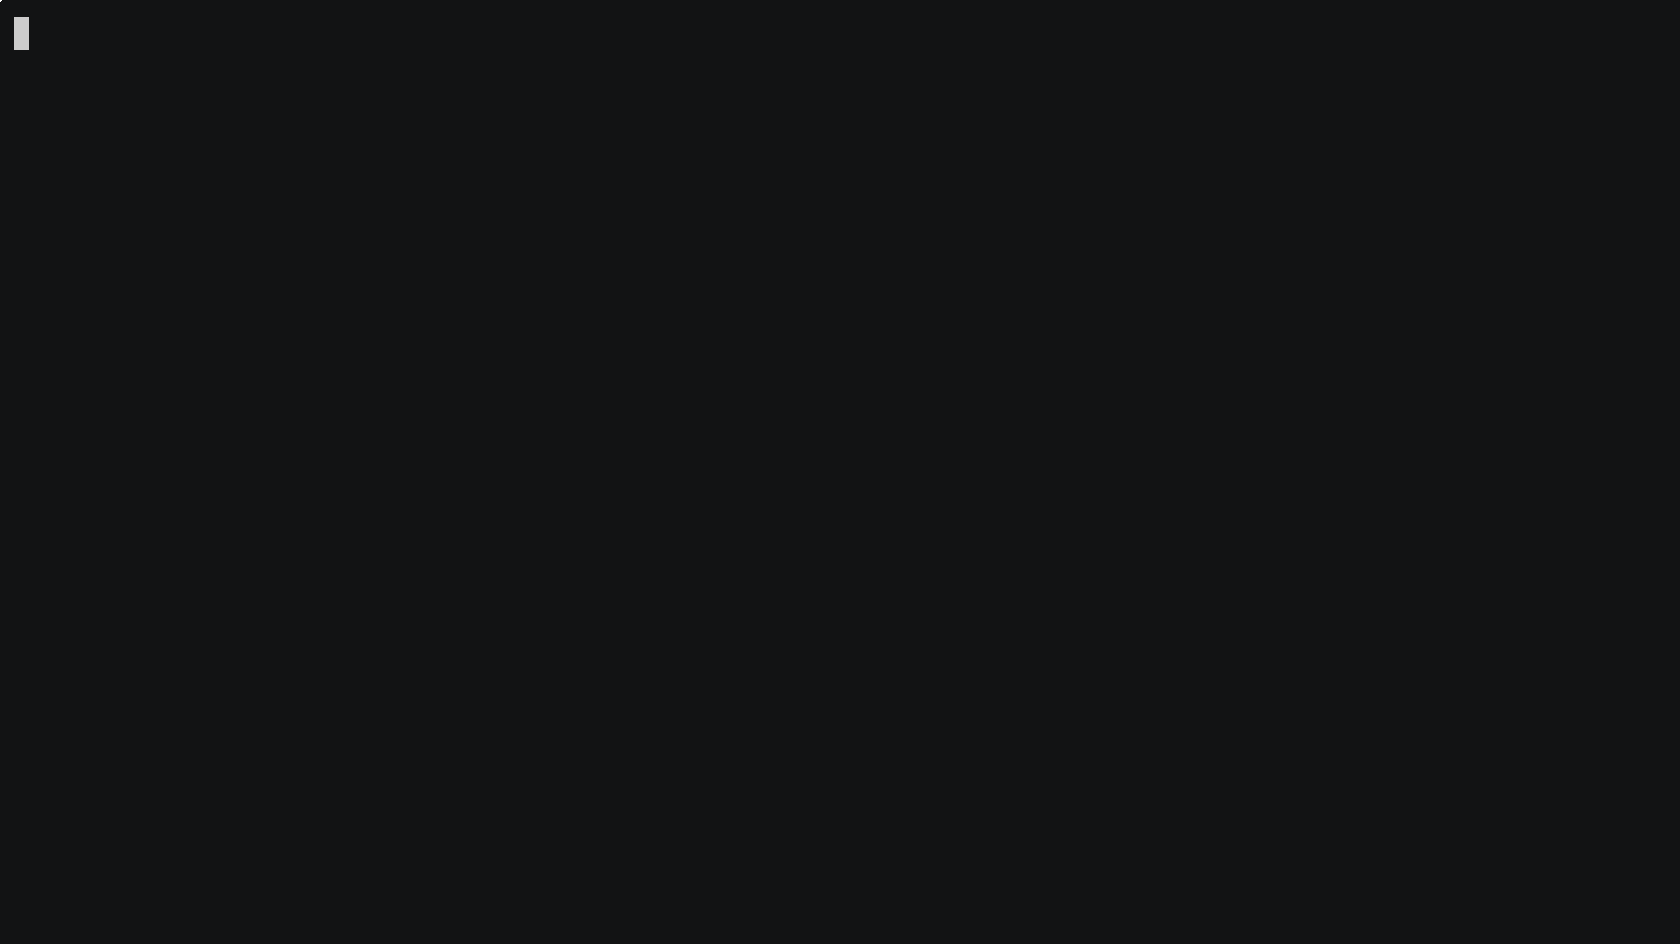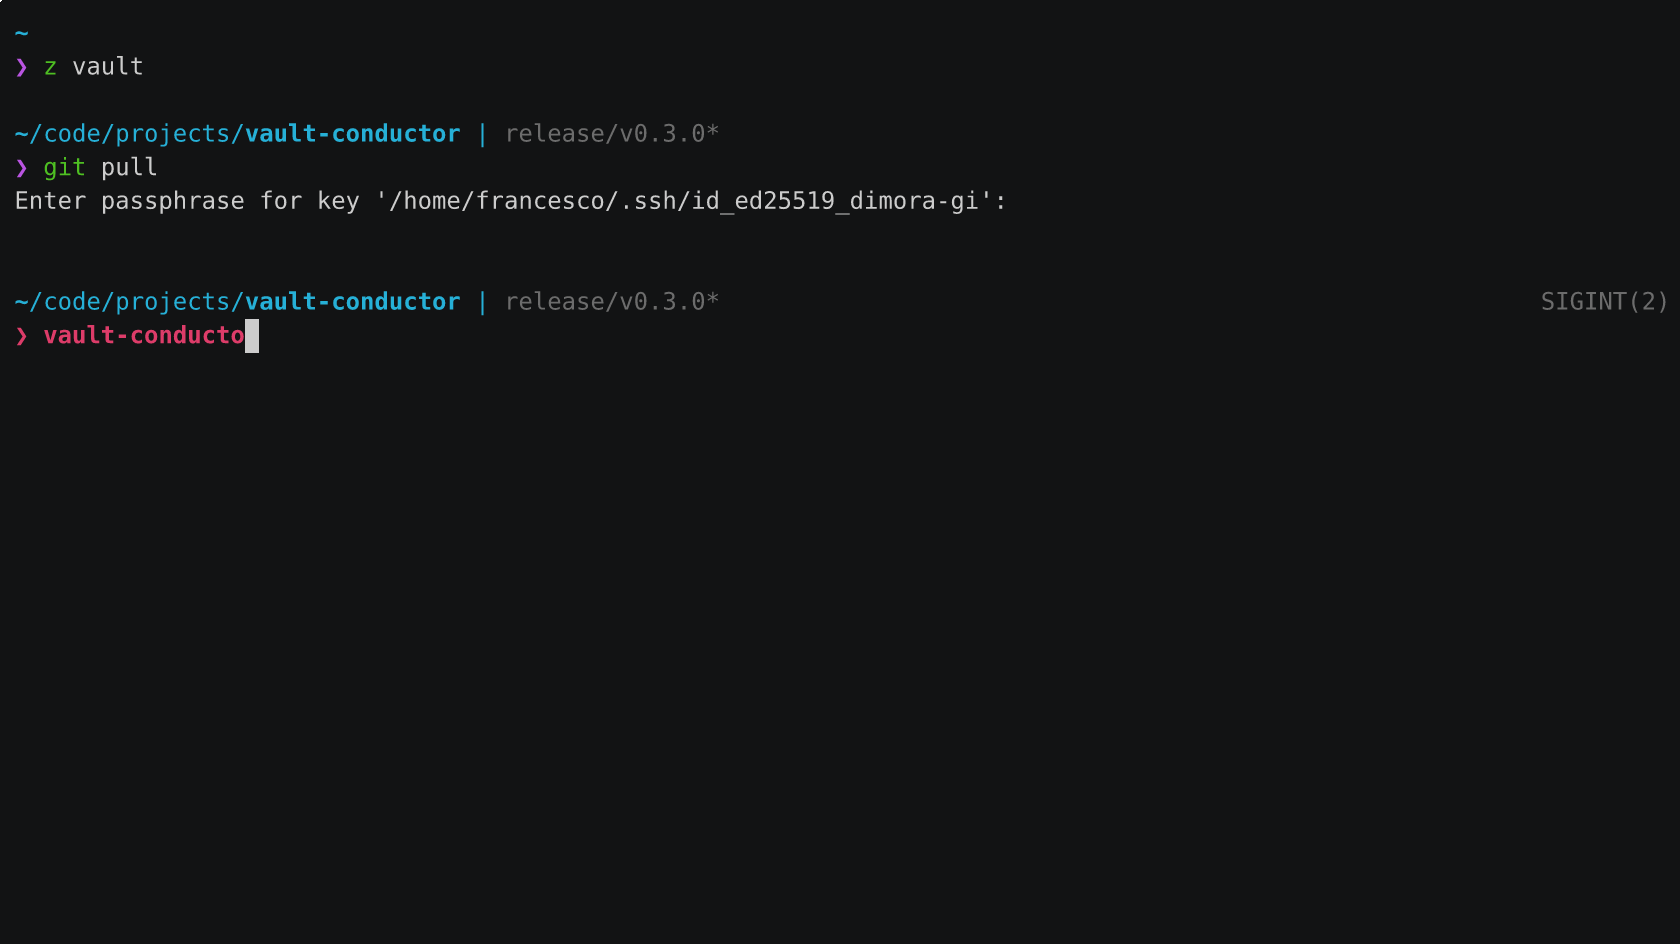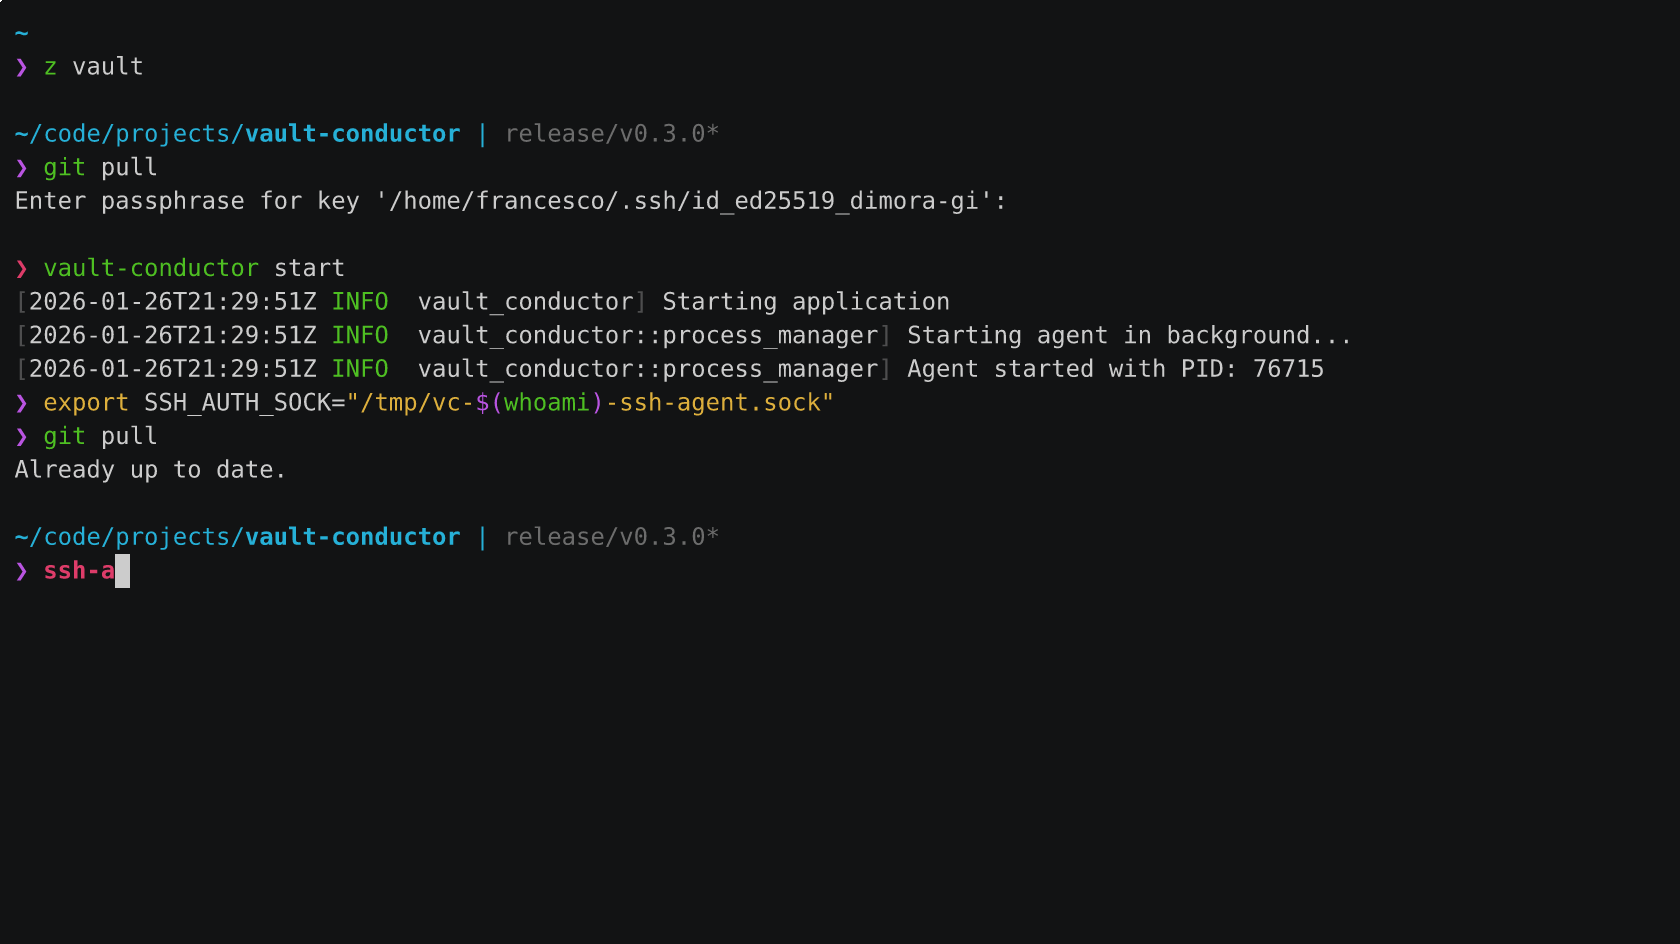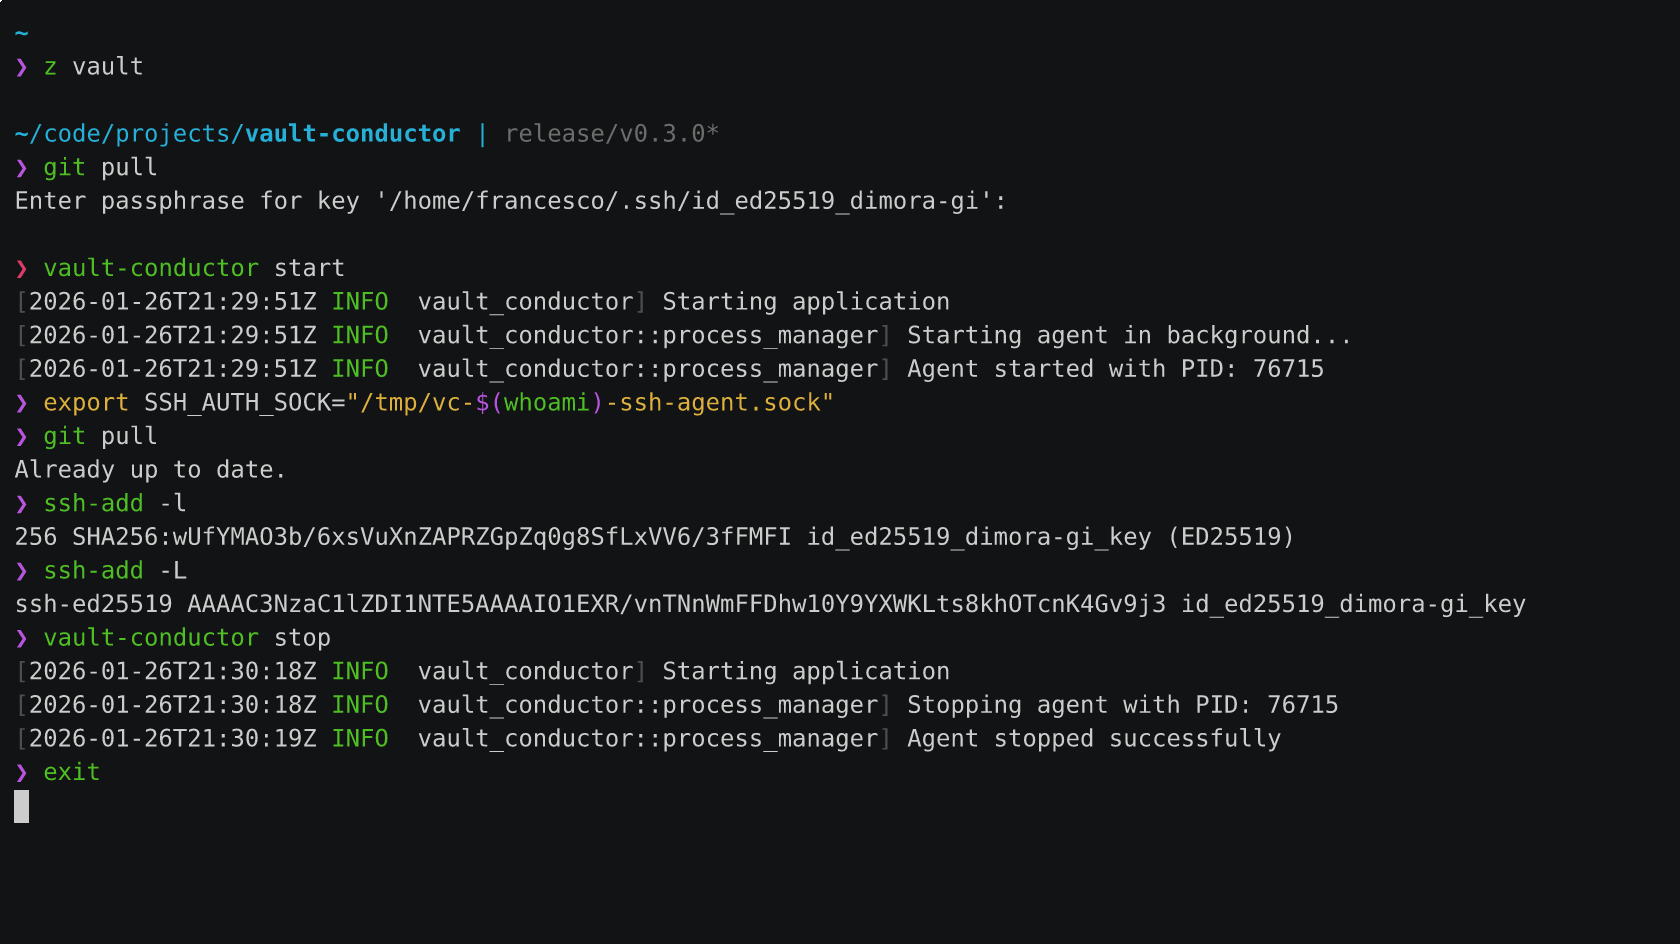
An SSH Agent that provides SSH keys stored in Bitwarden Secrets Manager
 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…
 aquasecurity/trivy-repo
deb/rpm repository for Trivy
 pgedge/pgedge-anonymizer
An anonymizer tool for replacing PII and similar data in dev/test databases copied from production
 gensecaihq/cve-2024-3094-vulnerability-checker-fixer
Shell script and Ansible playbook to detect and remediate CVE-2024-3094 in xz-utils by checking package versions, upgrading or downgrading to a…
 fran314/secrets-manager-rs
A command-line tool for securely backing up, restoring, and verifying secrets using interoperable standards like age encryption and coreutils,…
 scopeblind/scopeblind-gateway
Ed25519 signed receipts + Cedar policies for AI agents. Finance mandate gate (Legate), proof packs, 3 IETF Internet-Drafts. npx protect-mcp
 aquasecurity/trivy-plugin-kubectl
A Trivy plugin that scans the images of a kubernetes resource
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
 kamalsrini/sentinel-cve
CLI tool that explains CVEs in plain English and scans repos for impact. Powered by Claude.
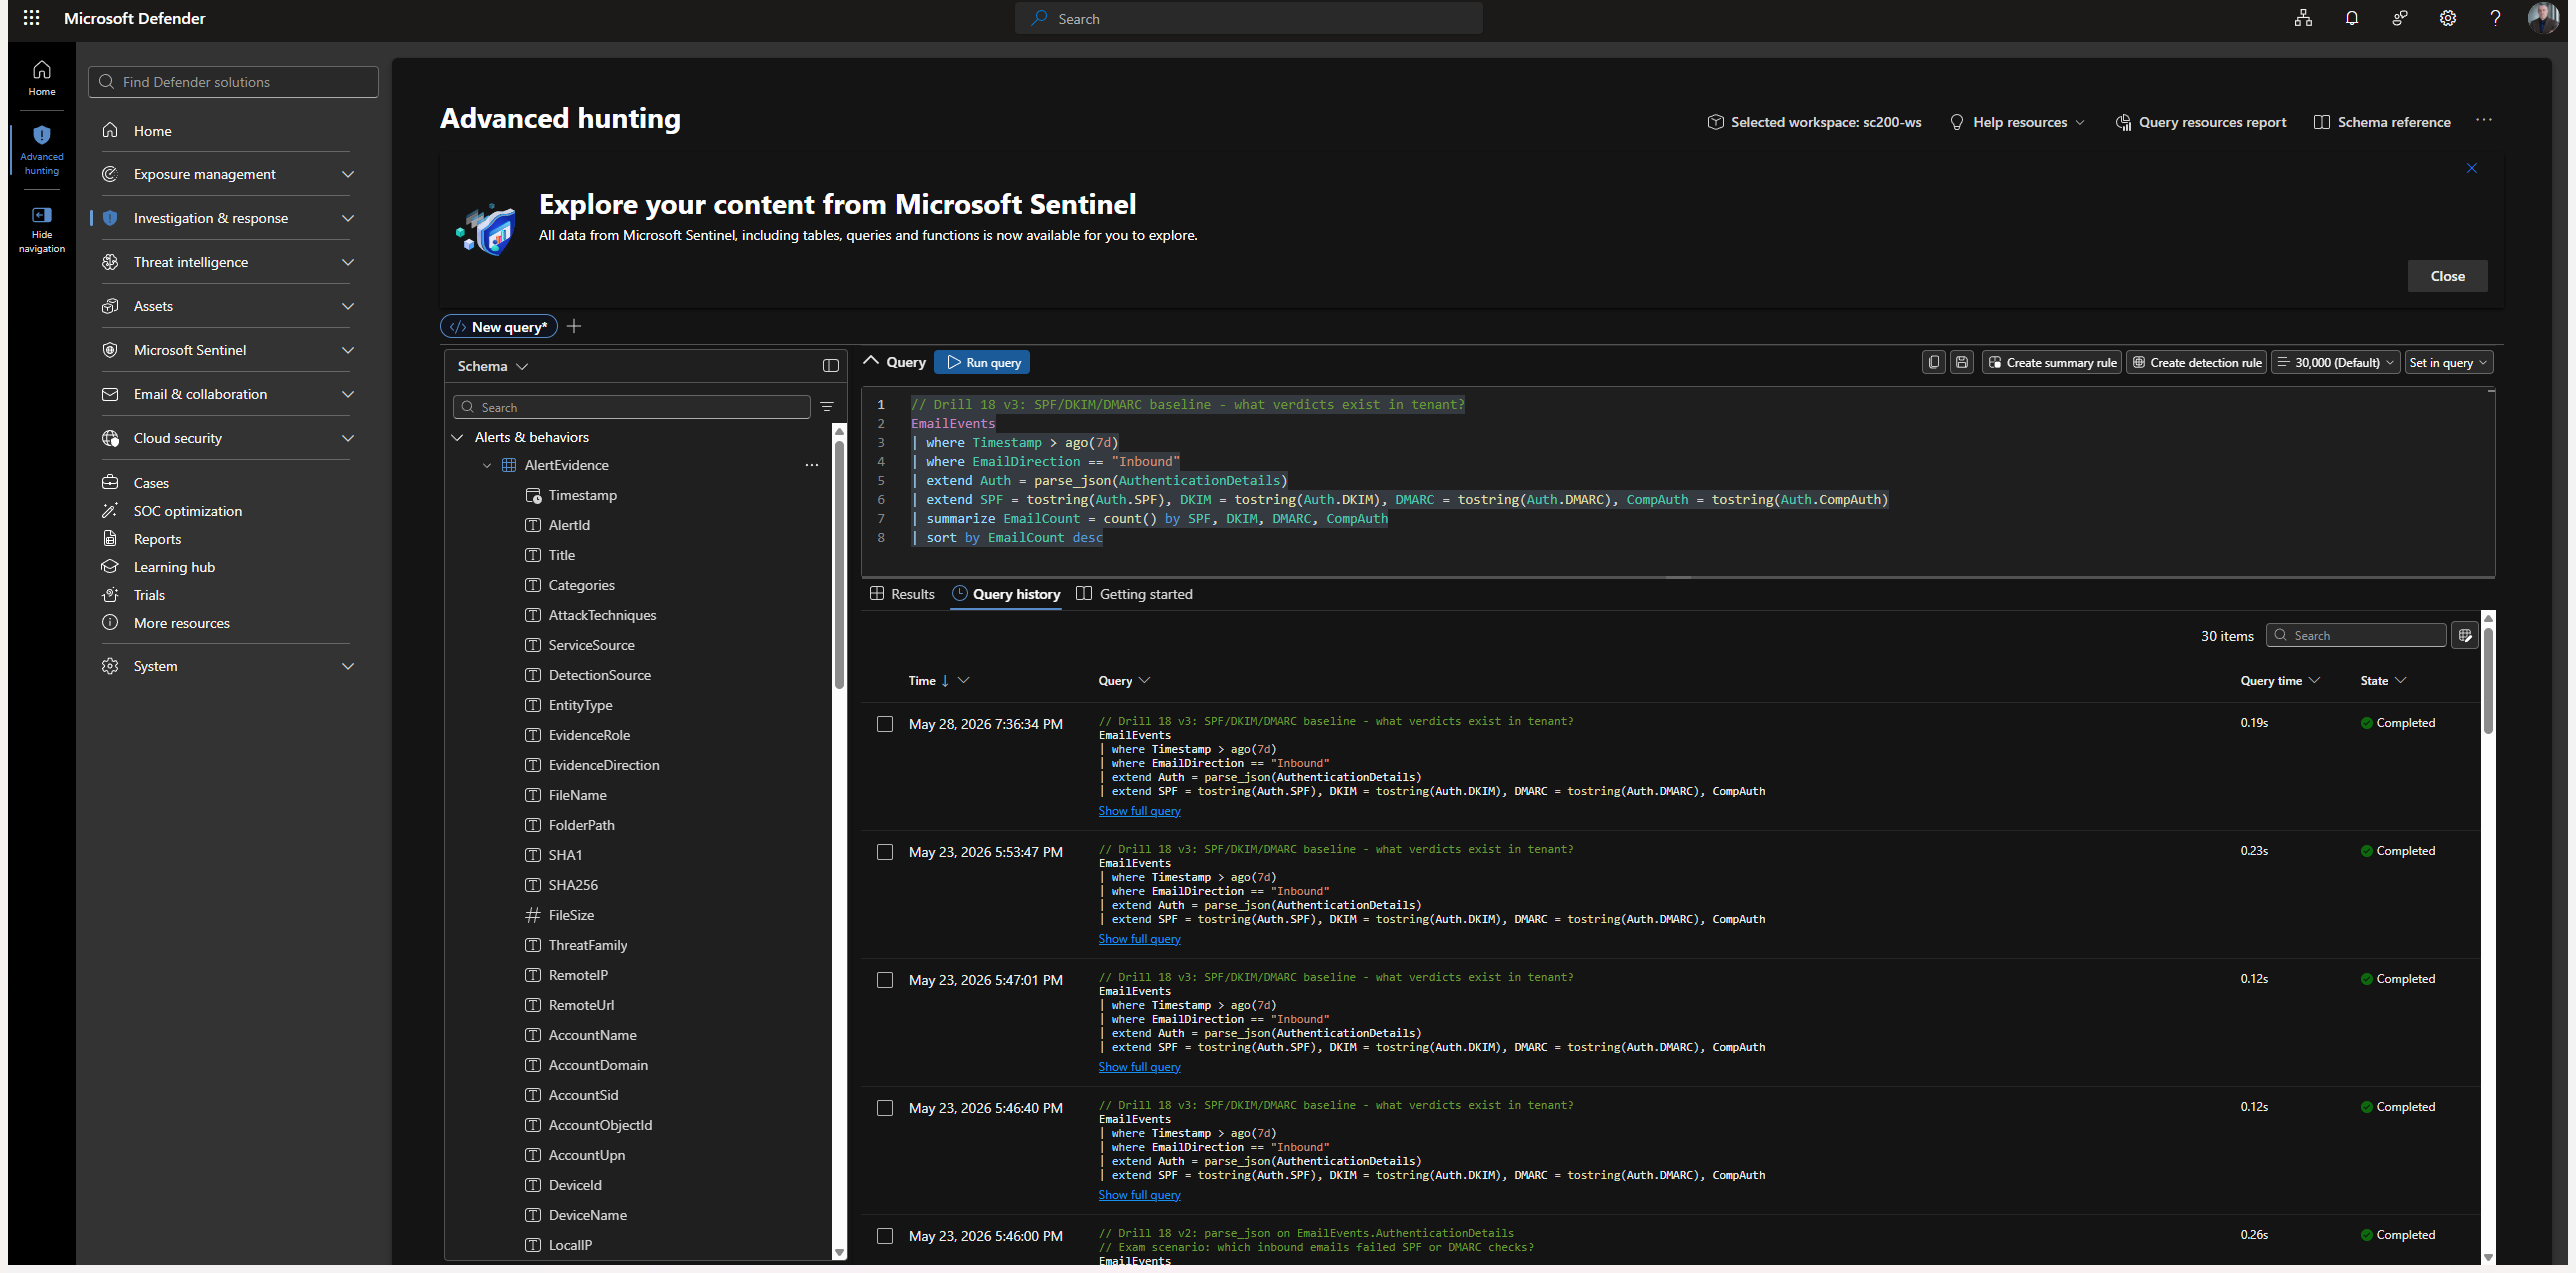 ibondarenko1/azure-sentinel-detection-engineering
9 MITRE ATT&CK-mapped KQL detections on a live Microsoft Sentinel + Defender XDR environment (control-plane, endpoint, identity), with a PR-gated…
 claranet/ansible-role-log4shell
Ansible role to detect Log4Shell (CVE-2021-44228) by scanning filesystem and open files for vulnerable JAR/WAR files, reporting version and…
 wantasticapp/wantasticcore
AIO Cloud Managment Server
 taptap/cve-2025-59489
Automated scanner that detects Unity runtime injection vulnerability CVE-2025-59489 in Android APKs by extracting Unity version and checking against…
 mhaggis/package-inferno
A Public Package Scanner for The Community