

cynative
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
ai-securitycloud-securitycontainer-security+7
185
cynative/cynativeRead-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
 check-spelling/check-spelling
Spelling checker action to check spelling in repositories / pull requests / commits
 pompelmi/pompelmi
ClamAV antivirus scanning for Node.js — scan file uploads with a single function call. Zero dependencies. Typed Symbol verdicts. Local or…
 jsdelivr/globalping-probe
The globalping probe code that runs on your hardware and connects to the global community network of probes
 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…
 hubblestack/hubble
Hubble is a modular, open-source security compliance framework. The project provides on-demand profile-based auditing, real-time security event…
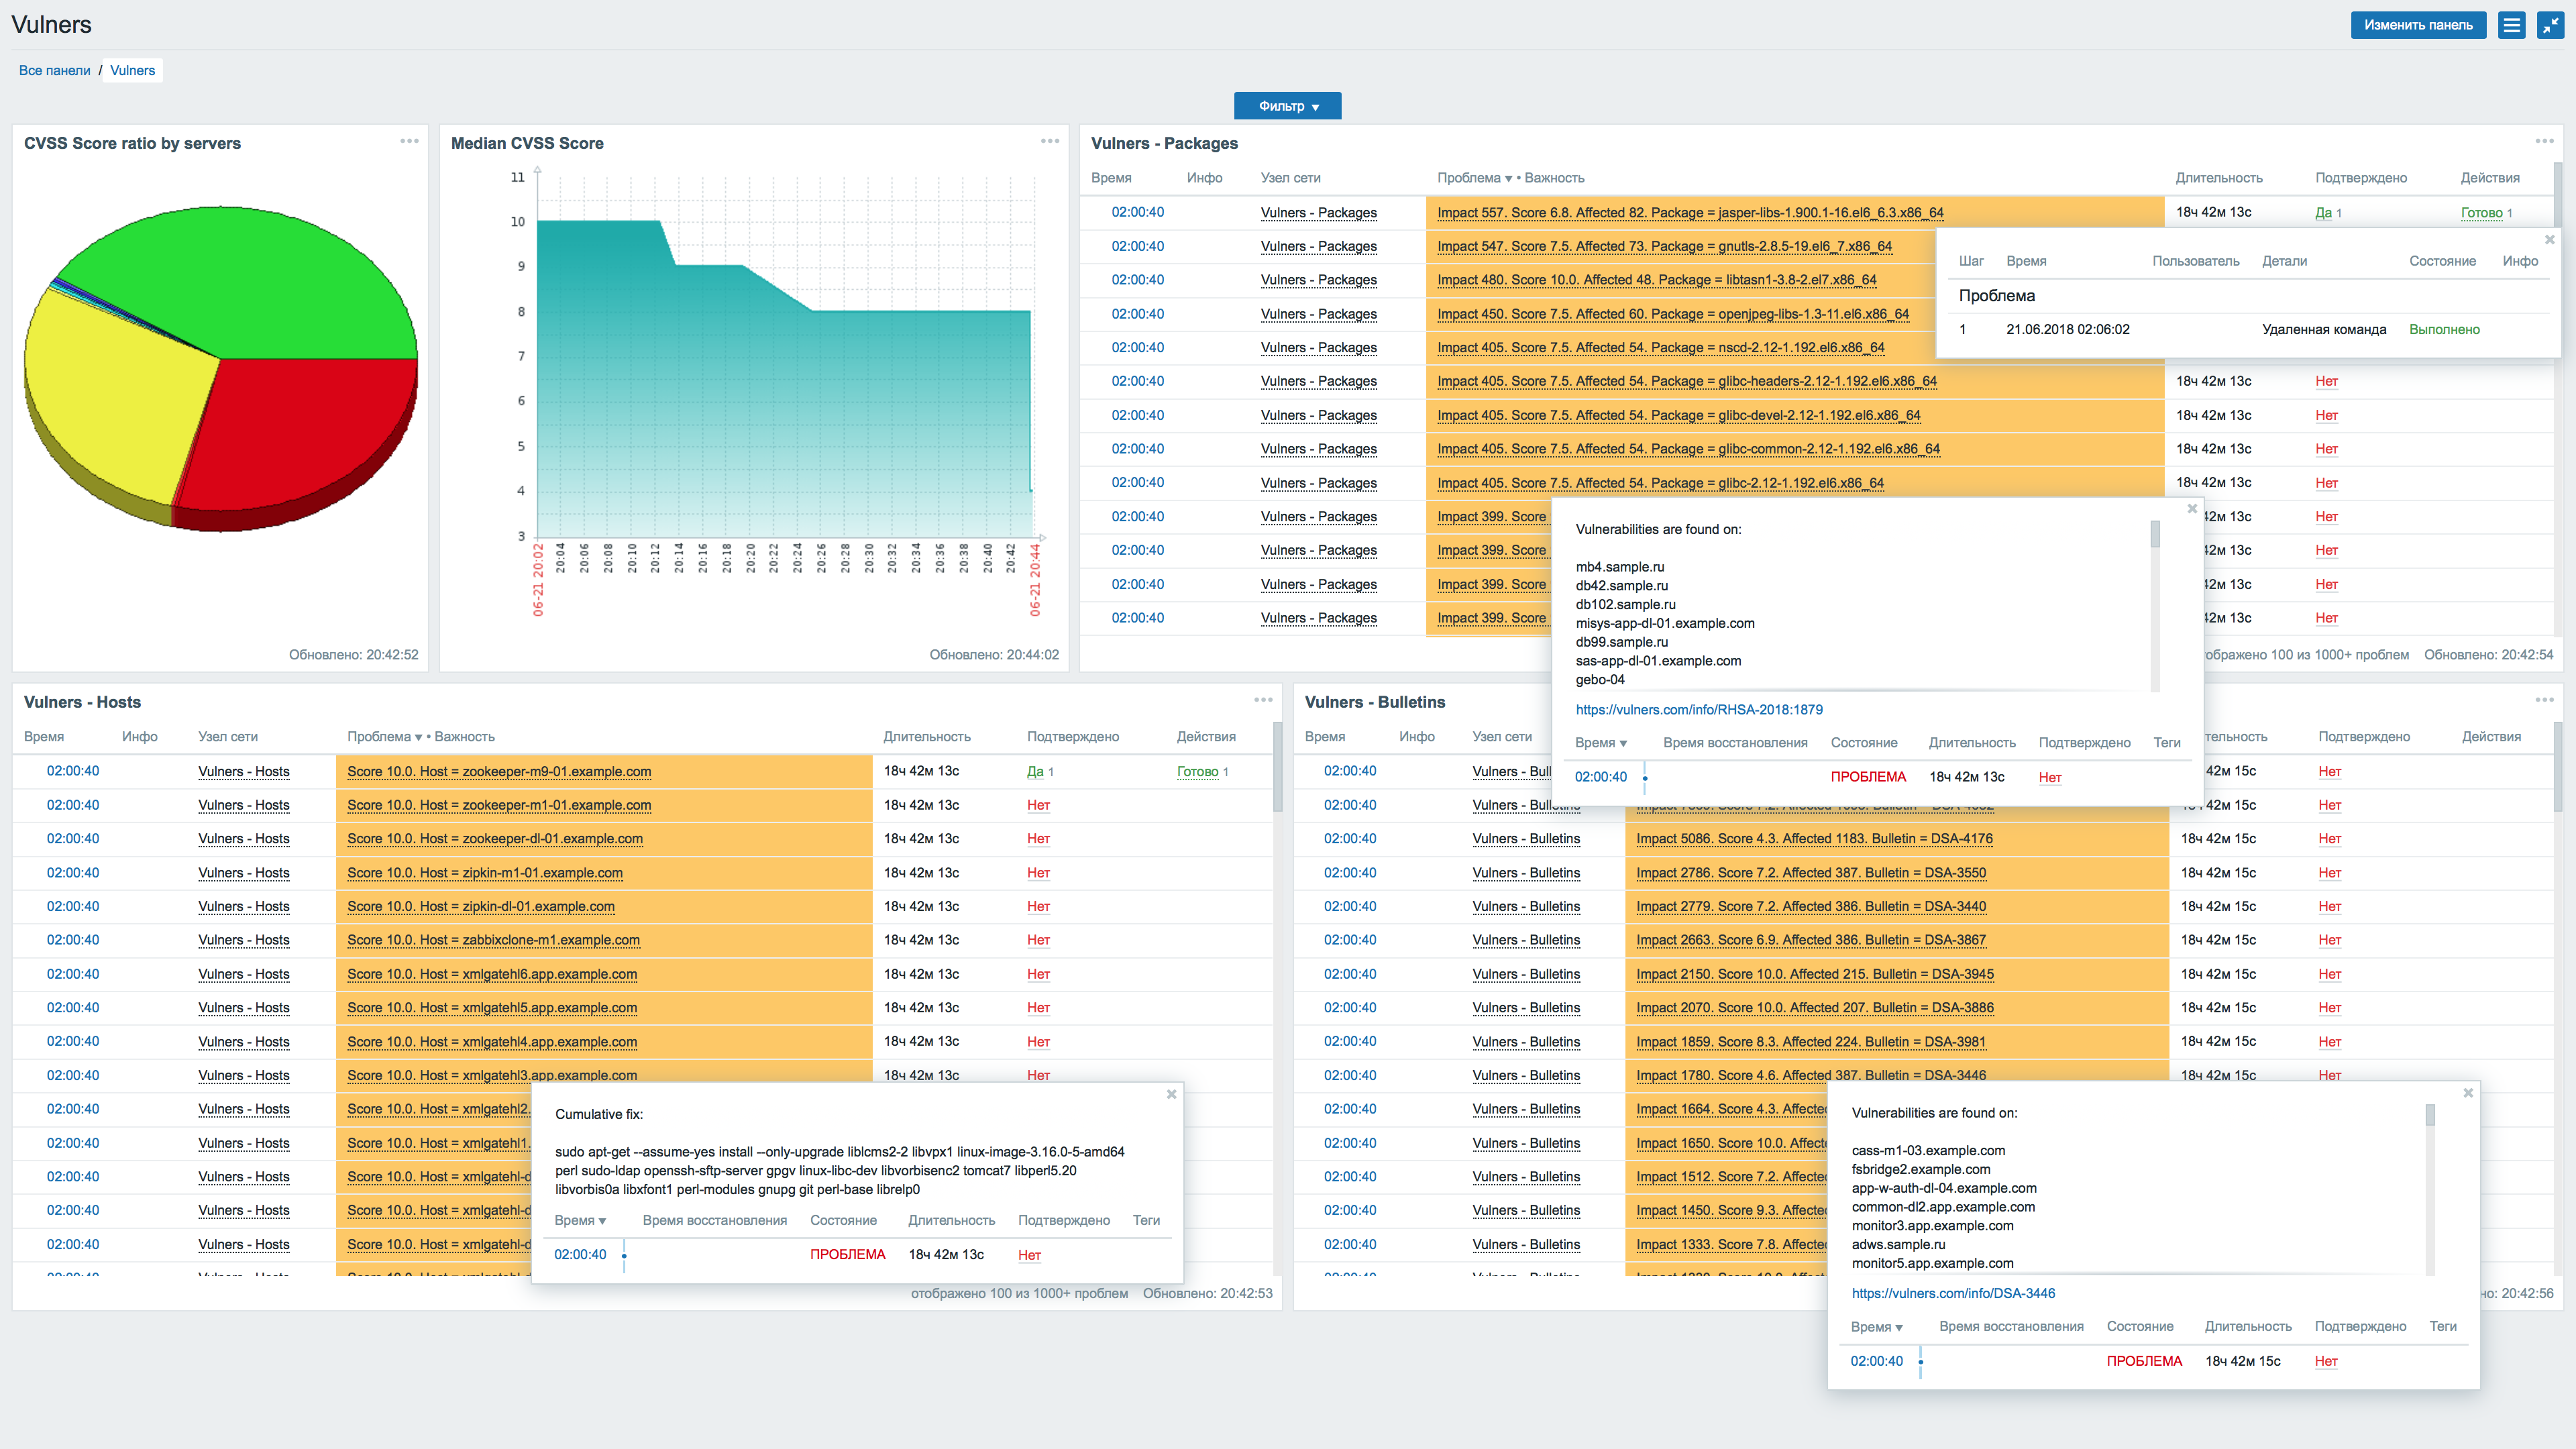 vulnerscom/zabbix-threat-control
Zabbix vulnerability assessment plugin
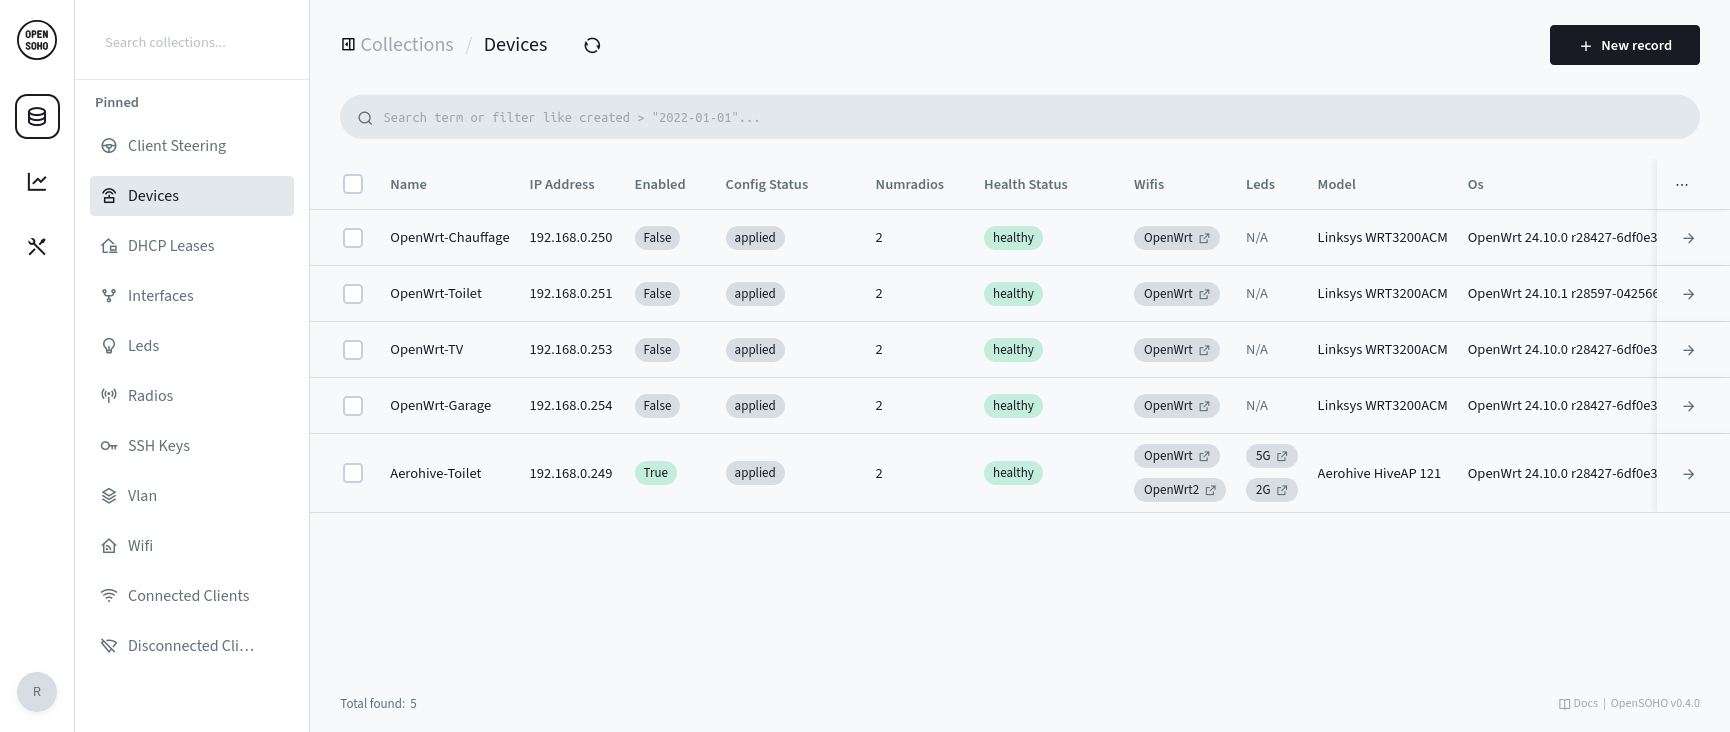 rubenbe/opensoho
Lightweight OpenWRT device management platform for small networks. Centralized configuration, monitoring, and WiFi management for 2–20 devices with…
 lore-hex/quill-router
TrustedRouter.com repo for secure LLM proxying
 vercel-labs/fix-react2shell-next
One command to fix CVE-2025-66478 (React 2 Shell RCE) in your Next.js / React RSC app.
 projectdiscovery/depx
Malicious package & supply-chain intelligence
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 safedep/gryph
Security layer for AI coding agents. Works with Claude Code, Cursor, Windsurf, Gemini CLI, OpenCode, Pi Agent and more.
 videns/vulners-scanner
Vulnerability scanner based on vulners.com audit API

 robocoder/rips-scanner
RIPS - A static source code analyser for vulnerabilities in PHP scripts
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 arnica/depsguard
Harden your package manager configs against supply chain attacks.