
threatmap
 bogdanticu88/threatmap
IaC threat modeler with STRIDE, MITRE ATT&CK, and PASTA frameworks. REST API, GraphQL, and Docker support for Terraform, CloudFormation, and…
api-securitycloud-securityconfiguration-auditing+5
62
bogdanticu88/threatmapIaC threat modeler with STRIDE, MITRE ATT&CK, and PASTA frameworks. REST API, GraphQL, and Docker support for Terraform, CloudFormation, and…
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 xenoncyber/envy
A terminal based tool for managing secrets with both tui and cli support
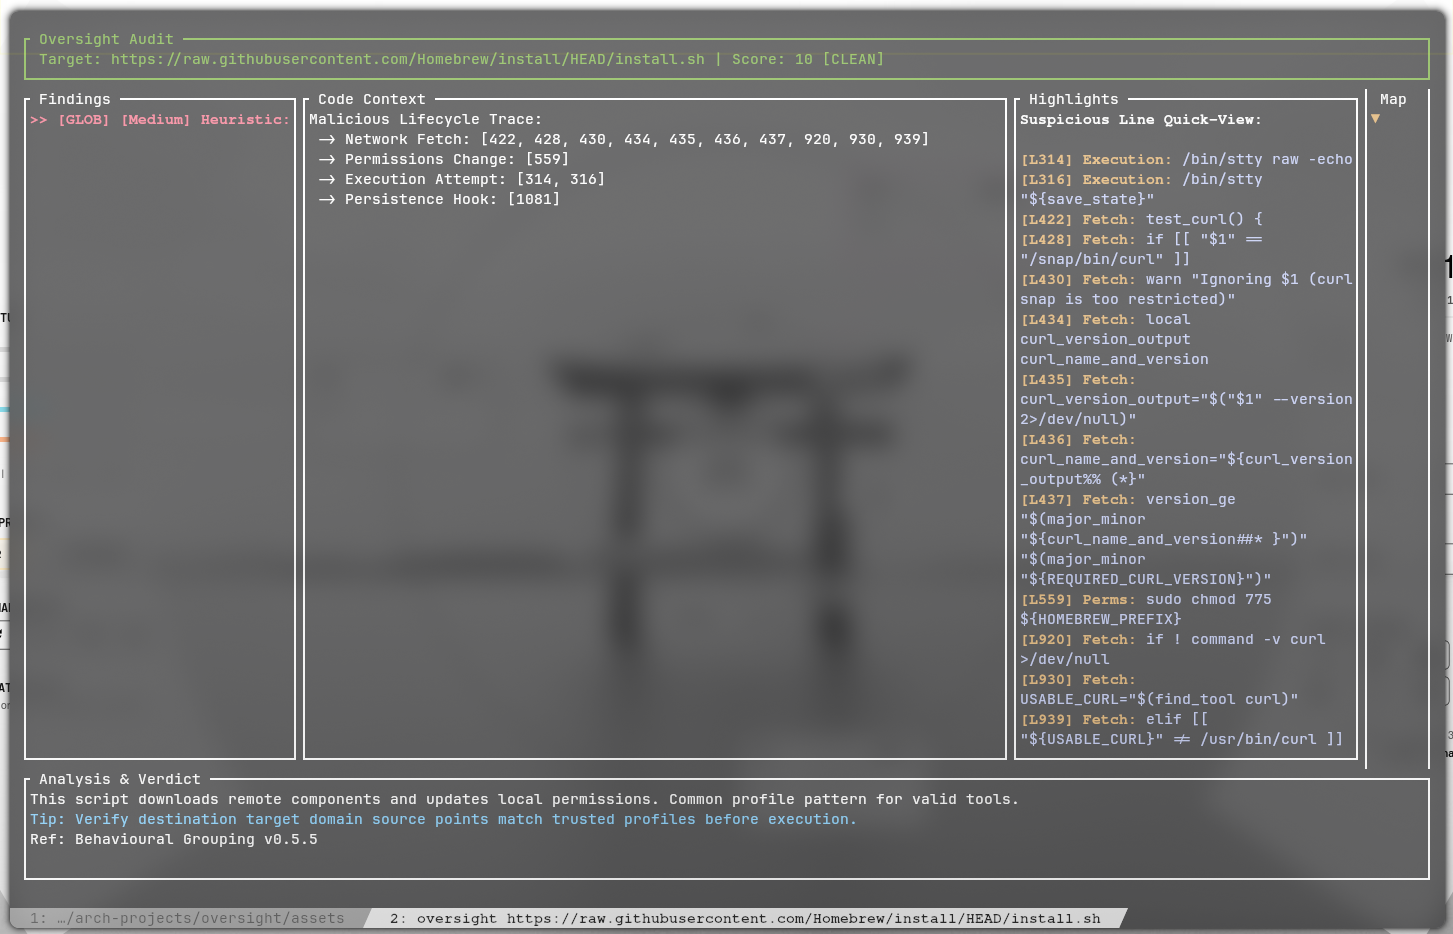 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
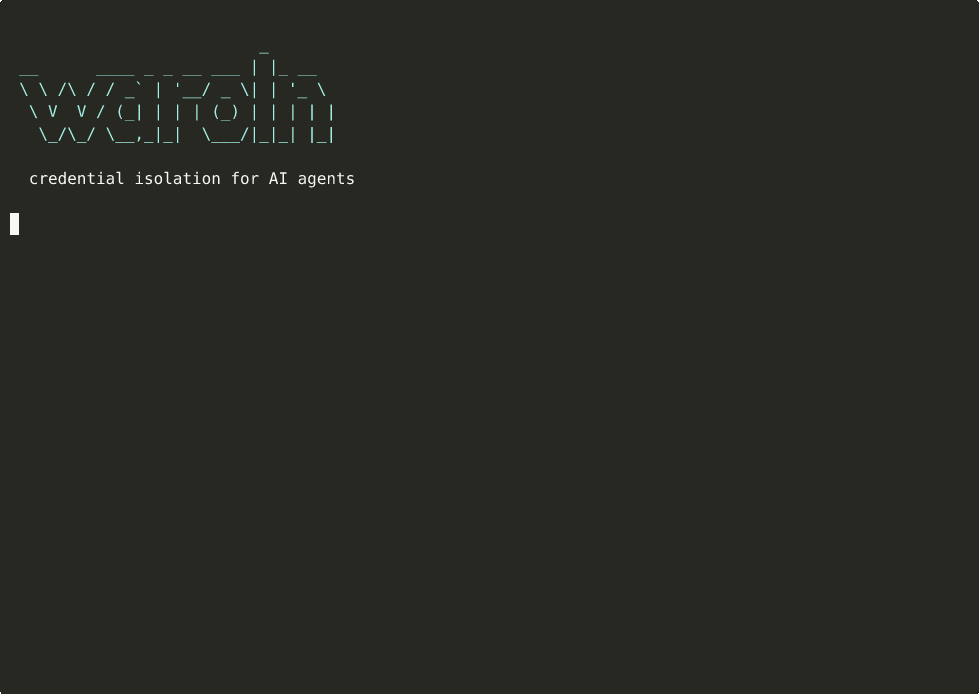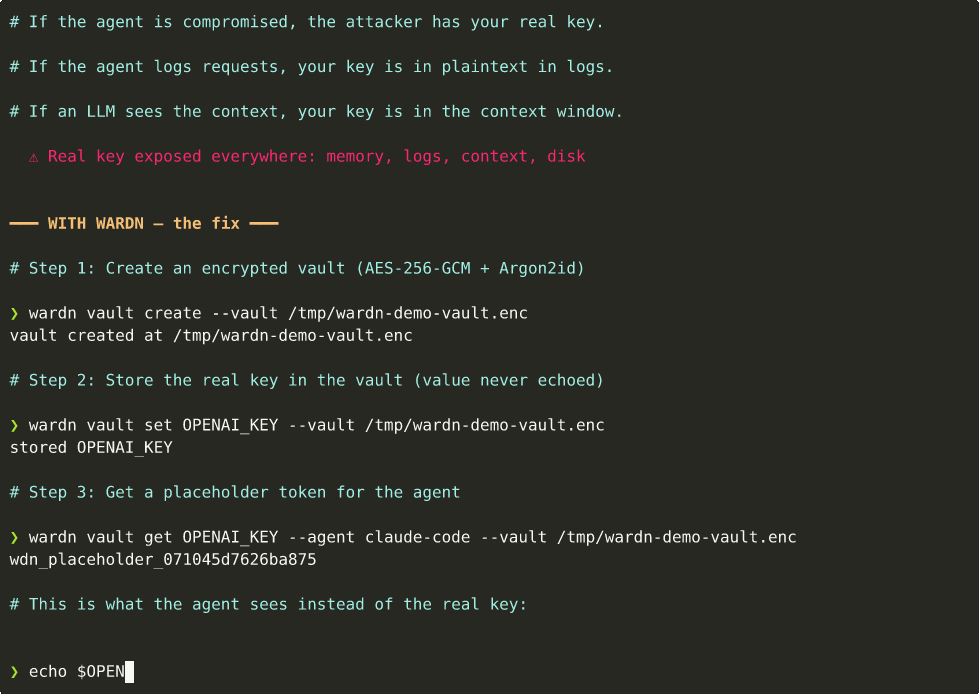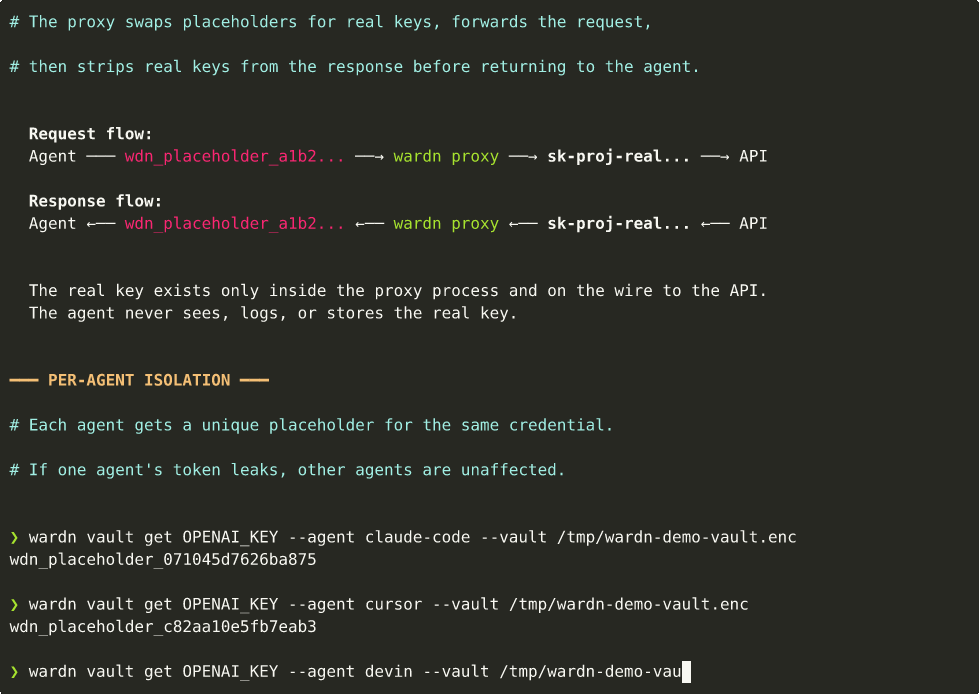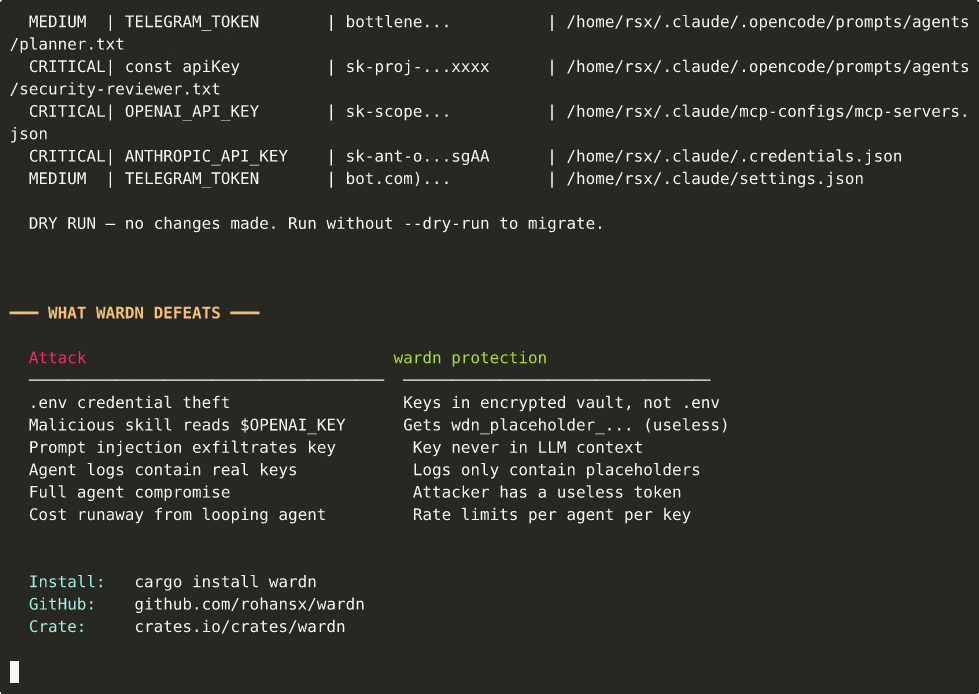 rohansx/wardn
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.
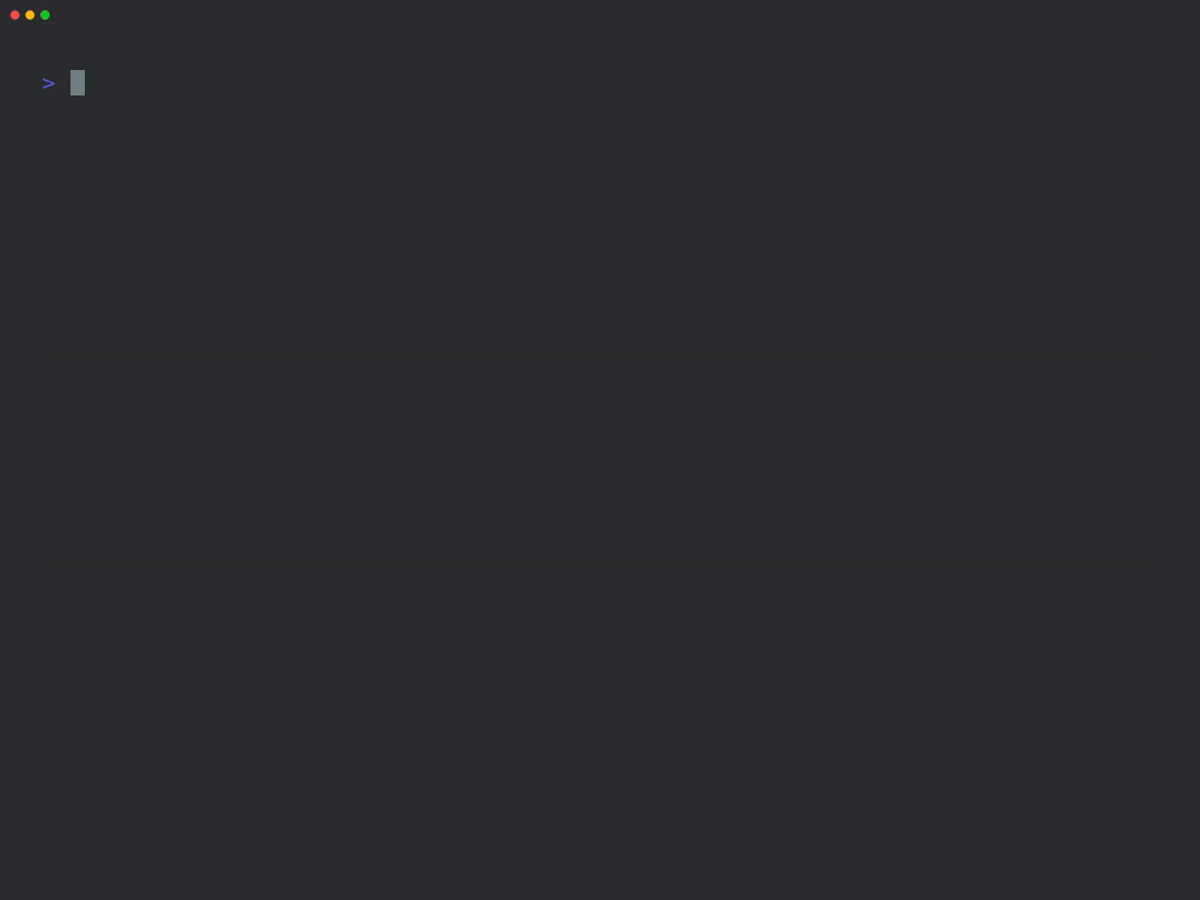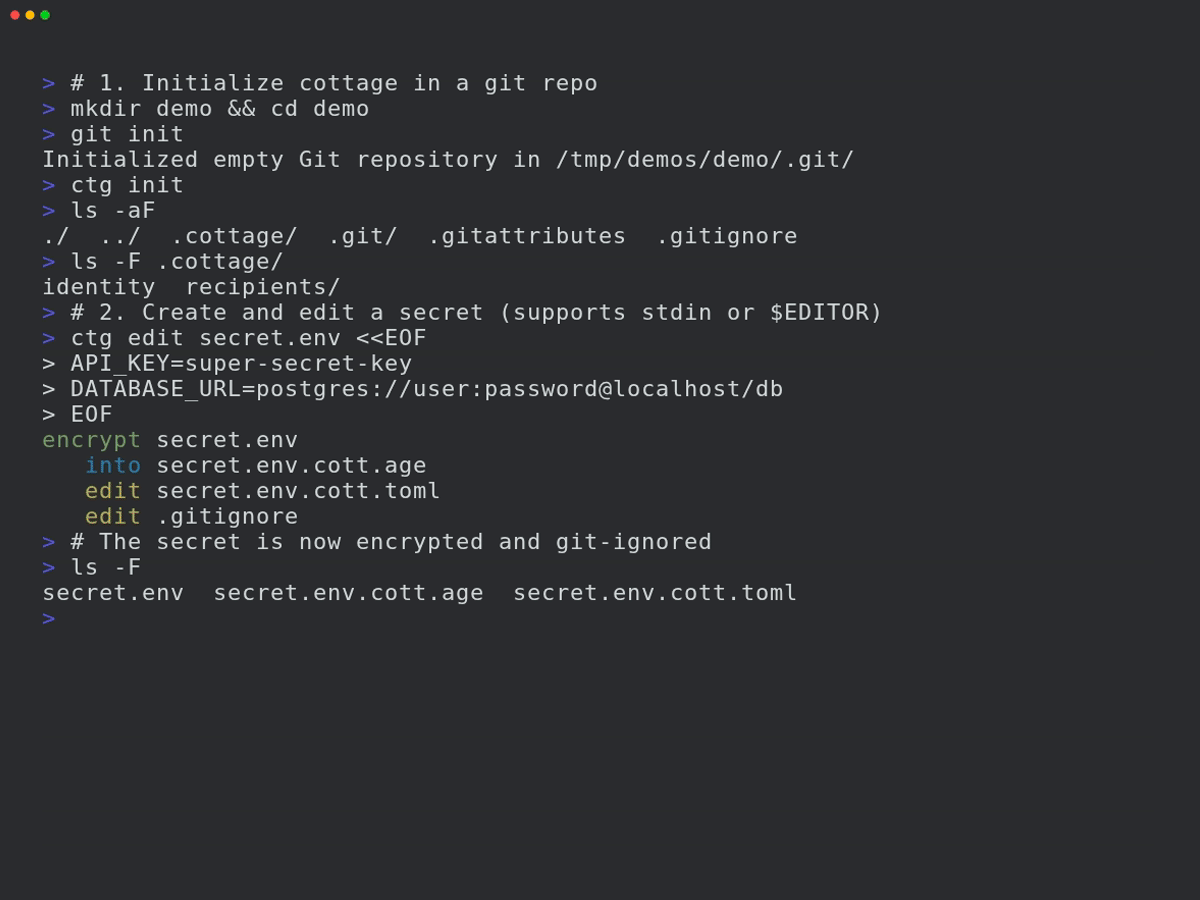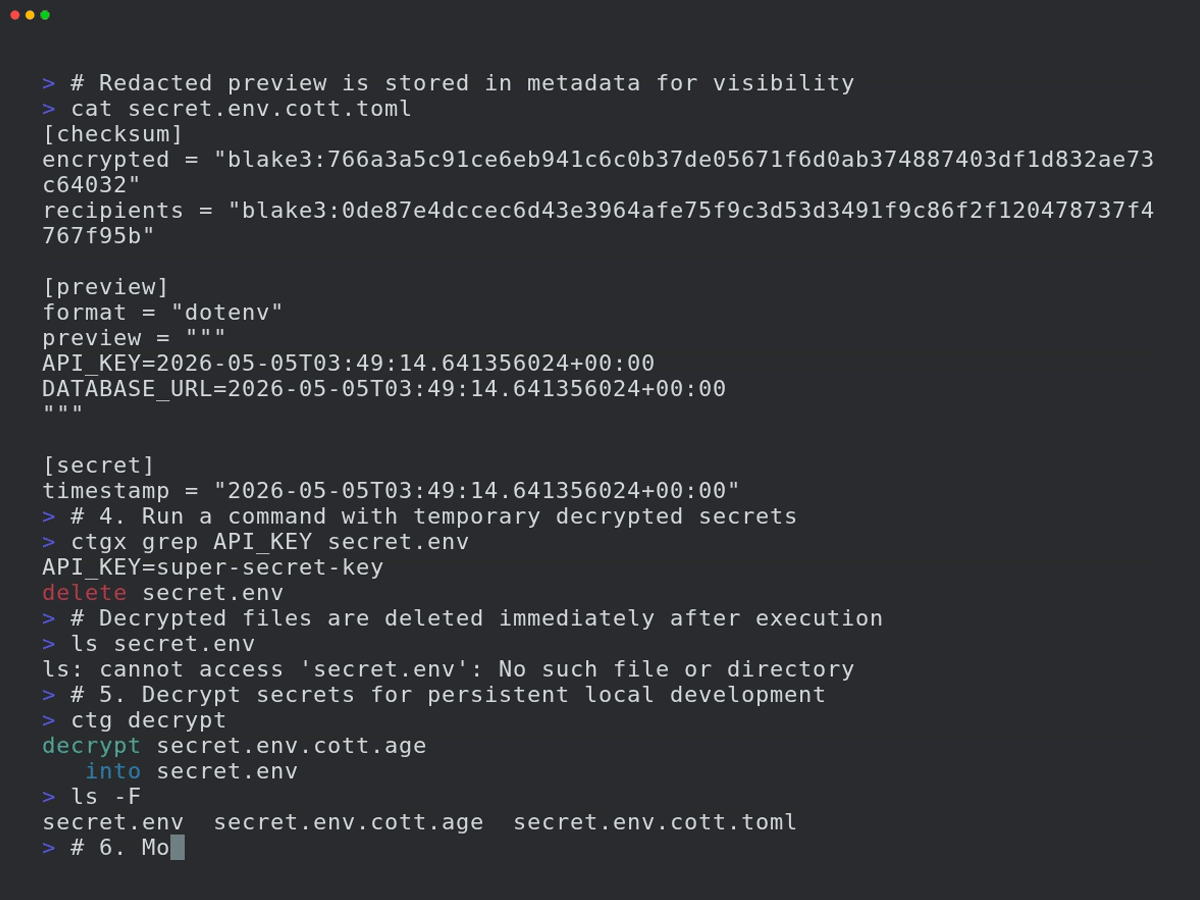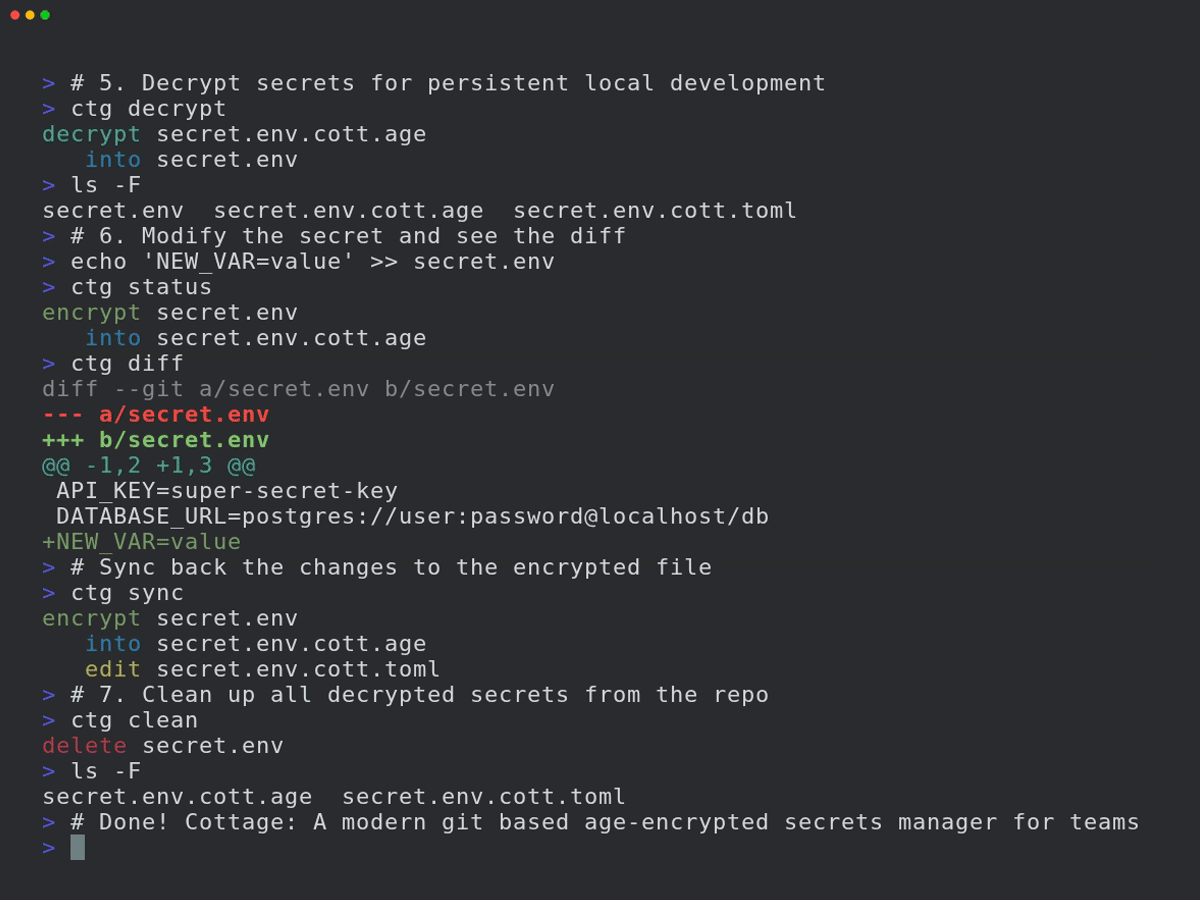 sayanarijit/cottage
A modern git based age-encrypted secrets manager for teams.
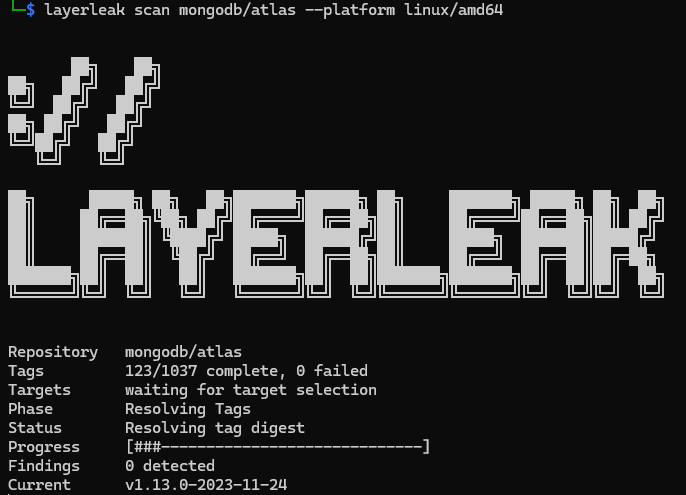 brumbelow/layerleak
layerleak the Docker Hub Secret Scanner
 lore-hex/quill-router
TrustedRouter.com repo for secure LLM proxying
 tech4242/aquaman
🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…
 darkarnium/log4j-cve-detect
Detections for CVE-2021-44228 inside of nested binaries
 0xcyberstan/cve-2026-42533-config-scanner
Static config scanner that flags nginx configs vulnerable to the complex_value two-pass capture-clobbering bug (regex map + regex capture → heap…
 farenhytee/database-sentinel
Claude Skill that audits your projects for RLS misconfigurations, exposed keys, auth bypasses, and storage vulnerabilities. 27 anti-patterns sourced…
 robert-auger/safer-dependencies
Automated dependency security layer for AI coding assistants that audits packages for CVEs, typosquats, abandonment, version-age issues, and hash…
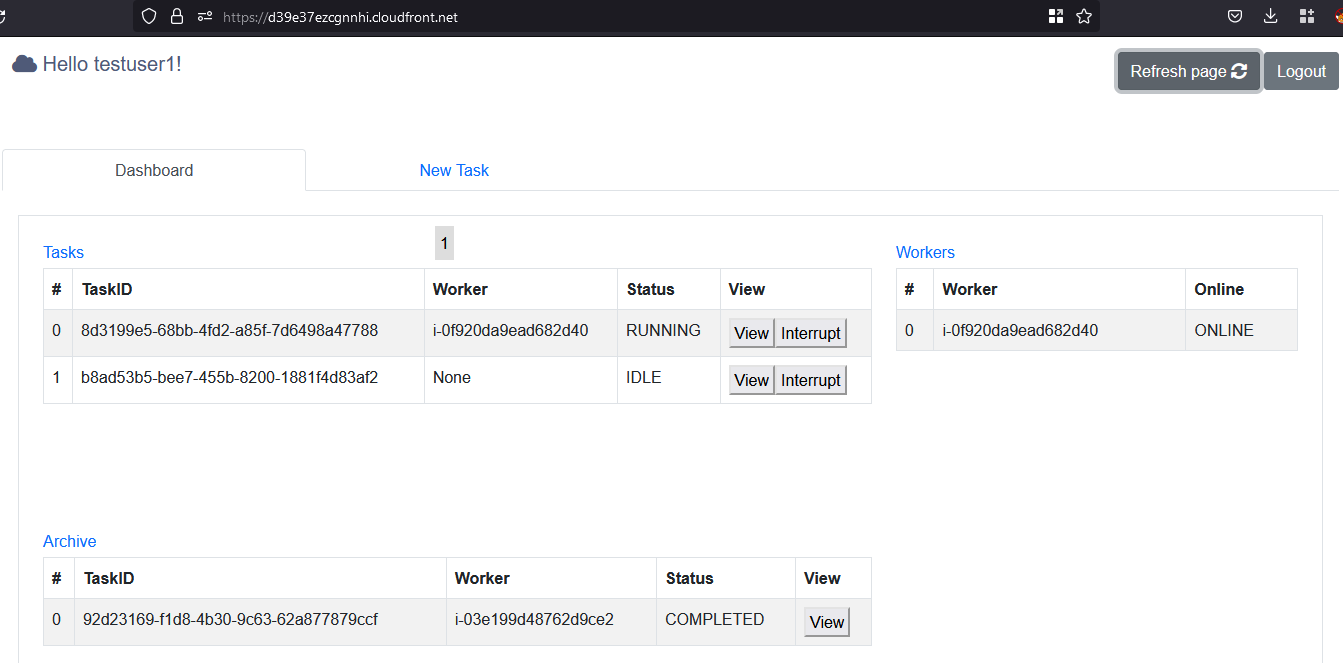 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
 mattijsmoens/intentshield
Pre-execution intent verification for AI agents. Audits what your AI is about to do, not what it says. Zero dependencies, deterministic, hash-sealed.
 lucab85/log4j-cve-2021-44228
Ansible playbook automating Red Hat's Log4j detector script to scan Linux hosts for CVE-2021-44228 (Log4Shell) vulnerability with GPG verification.
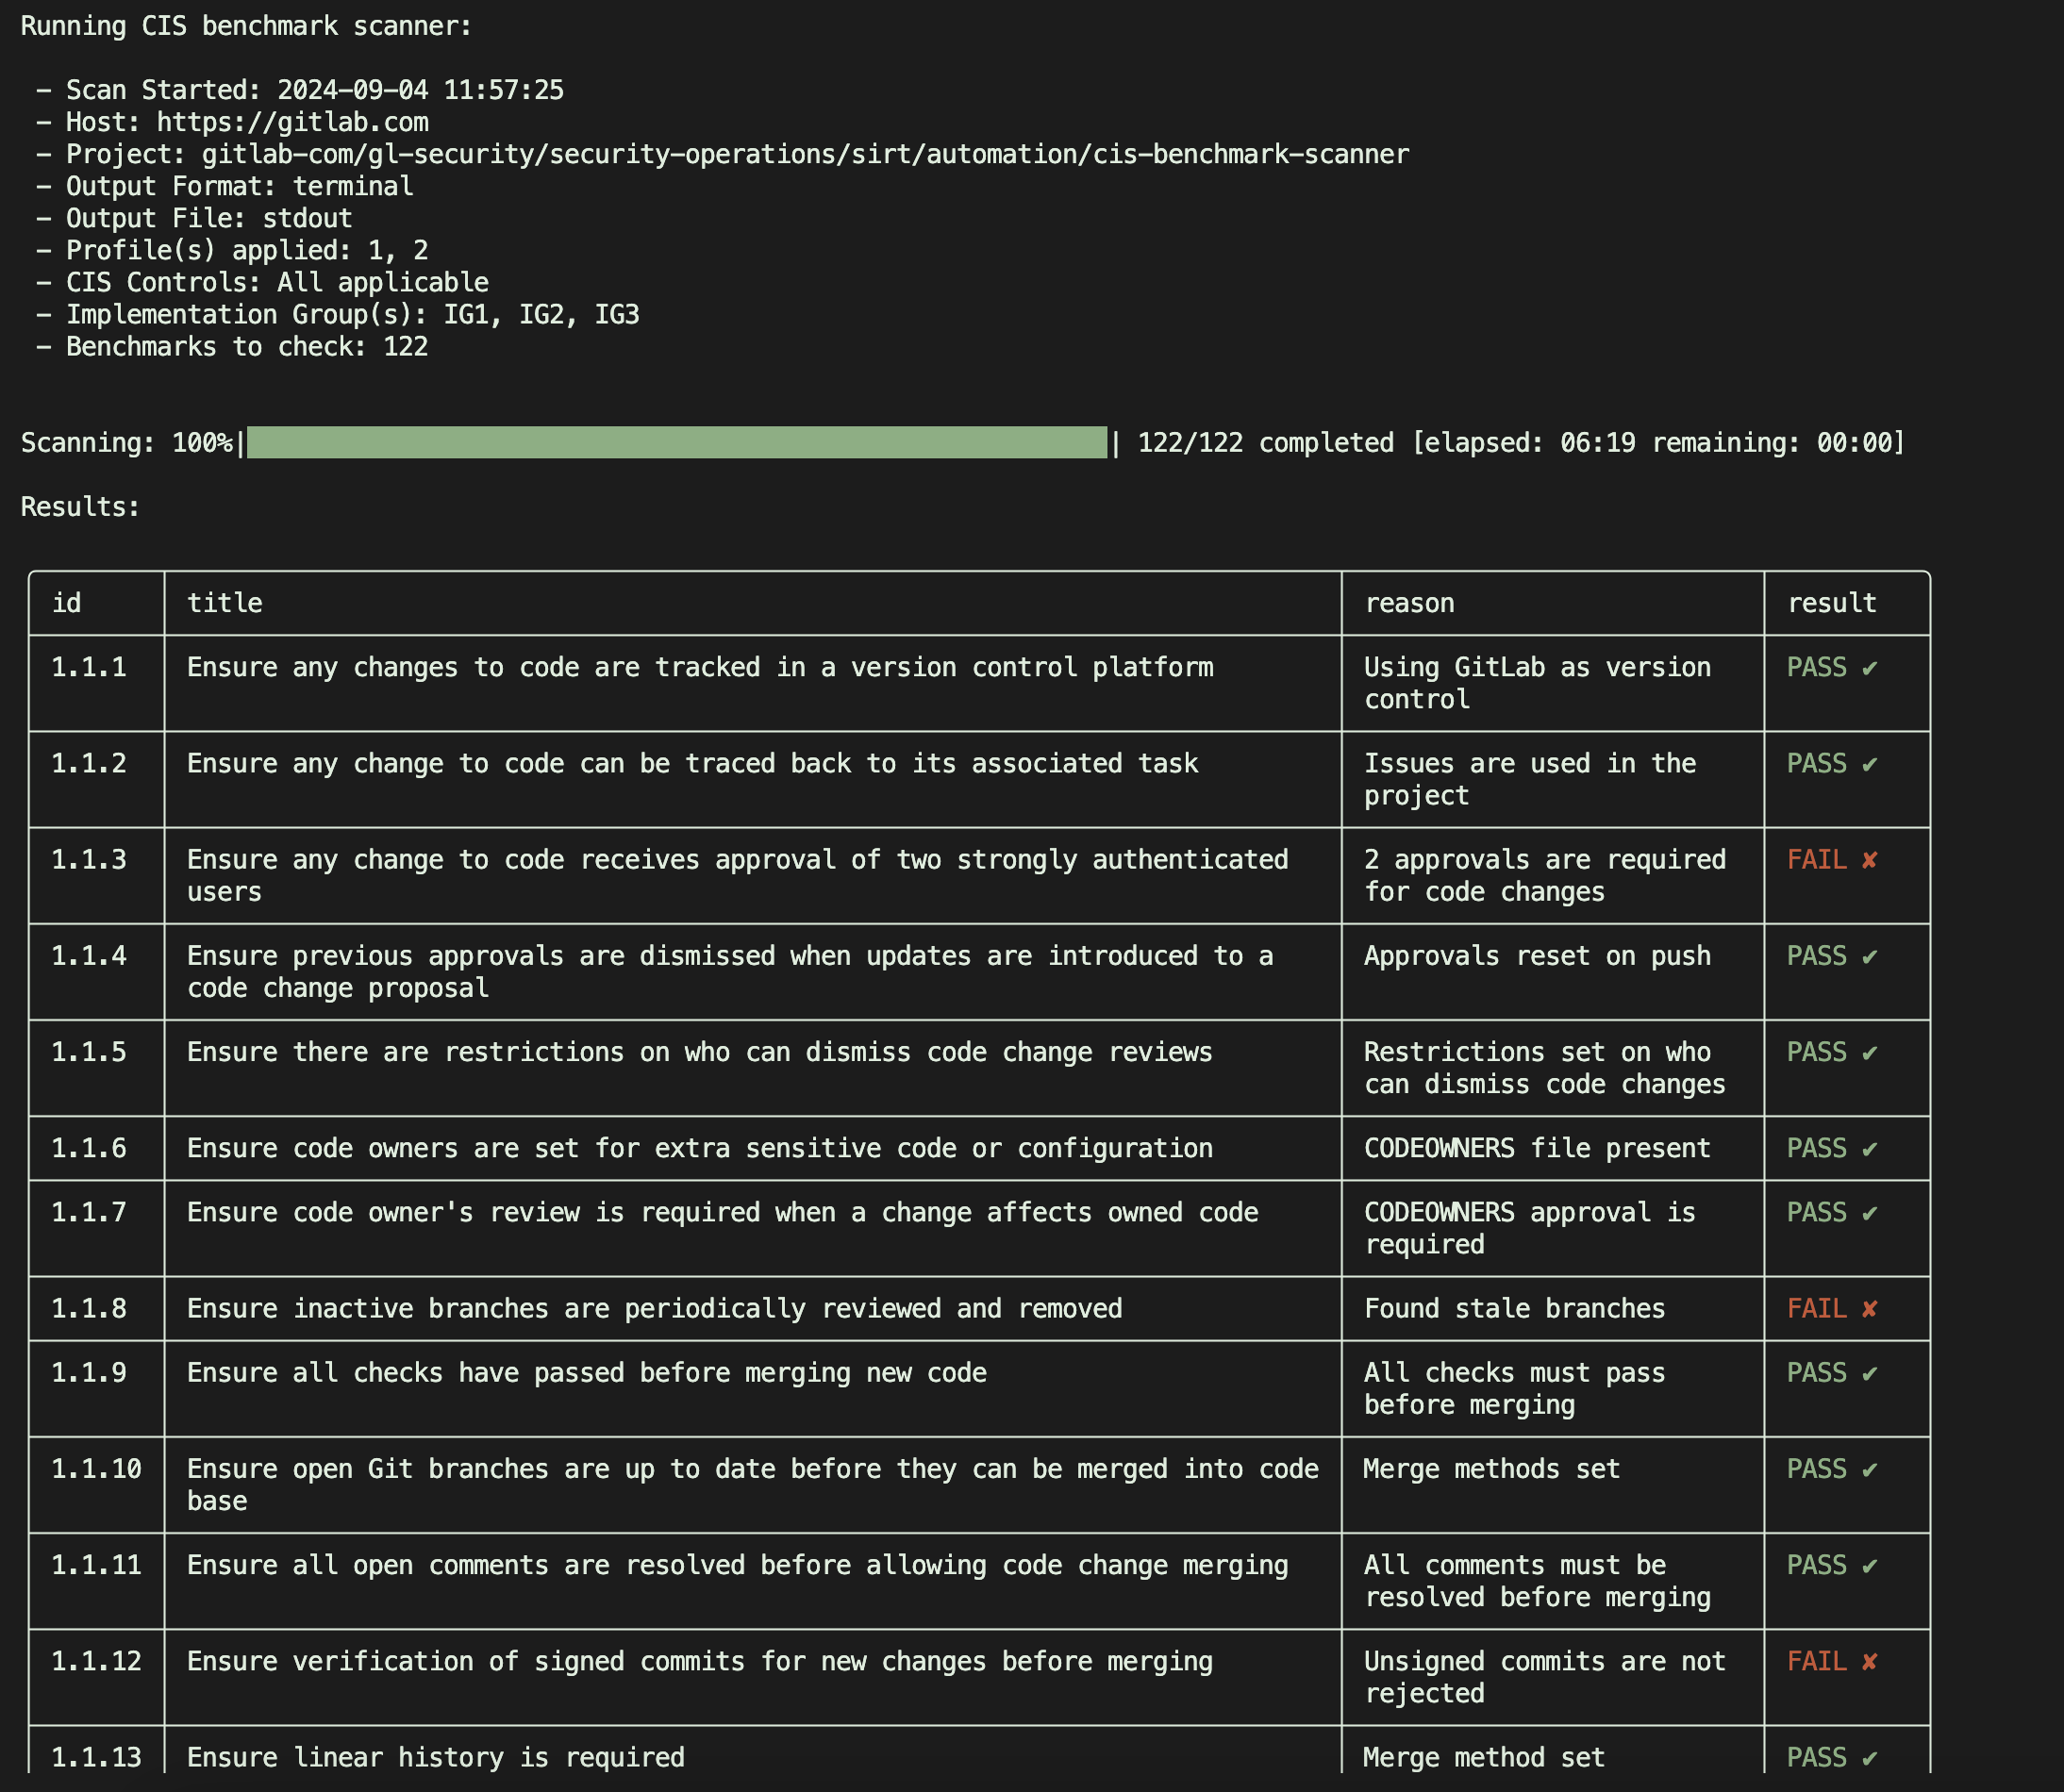
 gitlab-security-oss/cis/gitlabcis
Audits GitLab projects against the CIS GitLab Benchmark via read-only API checks, generating JSON reports on compliance and hardening recommendations.