
ephemera
 qarait/ephemera
Zero-Trust SSH CA
authentication-authorizationcloud-infrastructure-securityconfiguration-auditing+6
qarait/ephemeraZero-Trust SSH CA

 eduardolat/authkeysync
🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files
 tomjwxf/scopeblind-gateway
Security gateway for MCP servers with per-tool policy enforcement, Ed25519-signed audit receipts, and shadow-mode logging. Supports Cedar, OPA, and…
 owasp/xpsd
Reachability triage for vulnerability scans. Feeds scanner findings to an LLM agent that reads your source and decides which CVEs are actually…
 guettli/fix-cve-2020-15228
Python script that automatically patches GitHub Actions workflow files to replace deprecated and insecure ::set-env and ::add-path commands with the…
 xiaoqimikko/jackson-check
jackson-databind + jackson-core 26 条安全公告自查:按坐标逐条求交集给出真正到位的版本(2.18.11/2.21.7/2.22.3/3.1.7/3.2.3,2.21.6 已不够);扫源码降噪告诉你真中几条;含 1 条 GitHub…
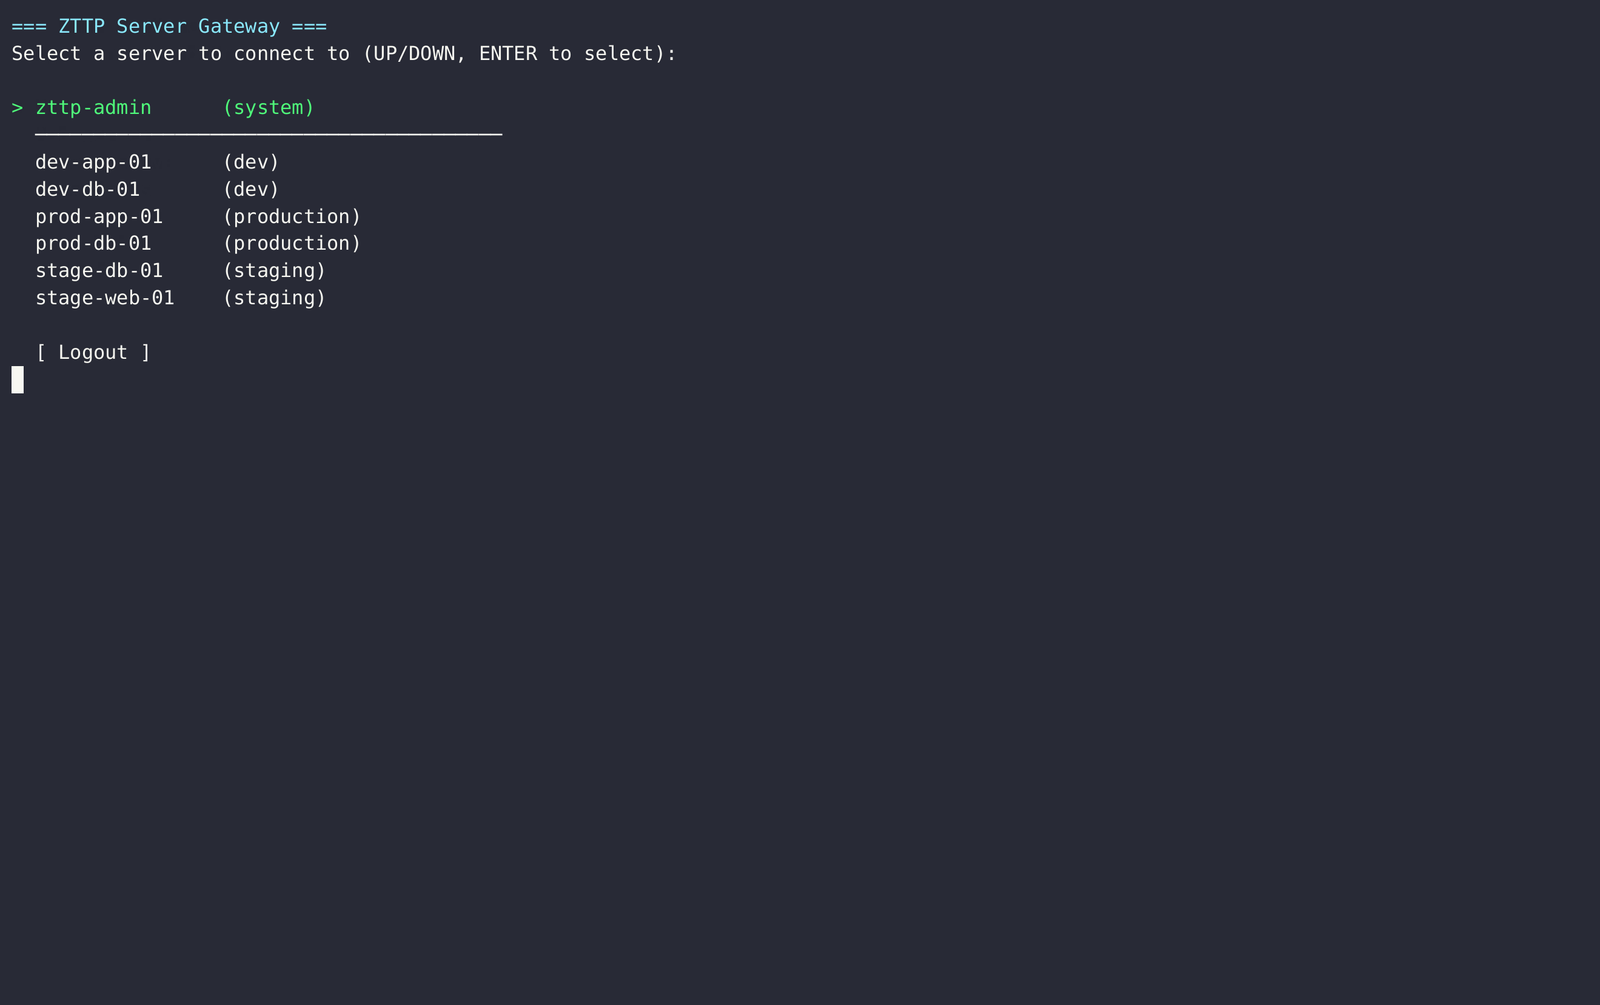
 nihal799/zttp
Zero-trust SSH bastion proxy with Vault-backed key management, RBAC policy enforcement, full session recording, and admin TUI for auditable access to…
 the-infra-company/kcatcher
Catch what's lurking in your Kafka clusters.
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 praetorian-inc/capability-sdk
Shared Go SDK defining a standard capability interface for security scanners, with multi-format finding output (terminal, JSON, NDJSON, Markdown,…
 philippeabraxas-jpg/responsible-alliance-protocol
Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…
 luiscastellanos-dev/cobol-shield
Security hardening toolkit for COBOL legacy systems — invisible Unicode detection, format boundary analysis, source transformation integrity
 adarsh14734/aegis-releases
Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…
 marcstraube/zappzarapp-php-security
PHP 8.4+ security library (mirror)
 edtrackai/nextjs-supabase-stripe-security-checker
Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…
 nexaiceo/nexus-os
The Governed Agentic AI Operating System — Rust + Tauri 2.0 | 65 crates, 658 commands, 84 pages, 5,029 tests, 10/10 OWASP
 cosignet/sdk
Thin TypeScript + zero-dep Python client and recipes to gate high-risk actions behind a payload-bound passkey approval.