
kyverno
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
cloud-infrastructure-securitycloud-securityconfiguration-auditing+4
8.3k
kyverno/kyvernoEnforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
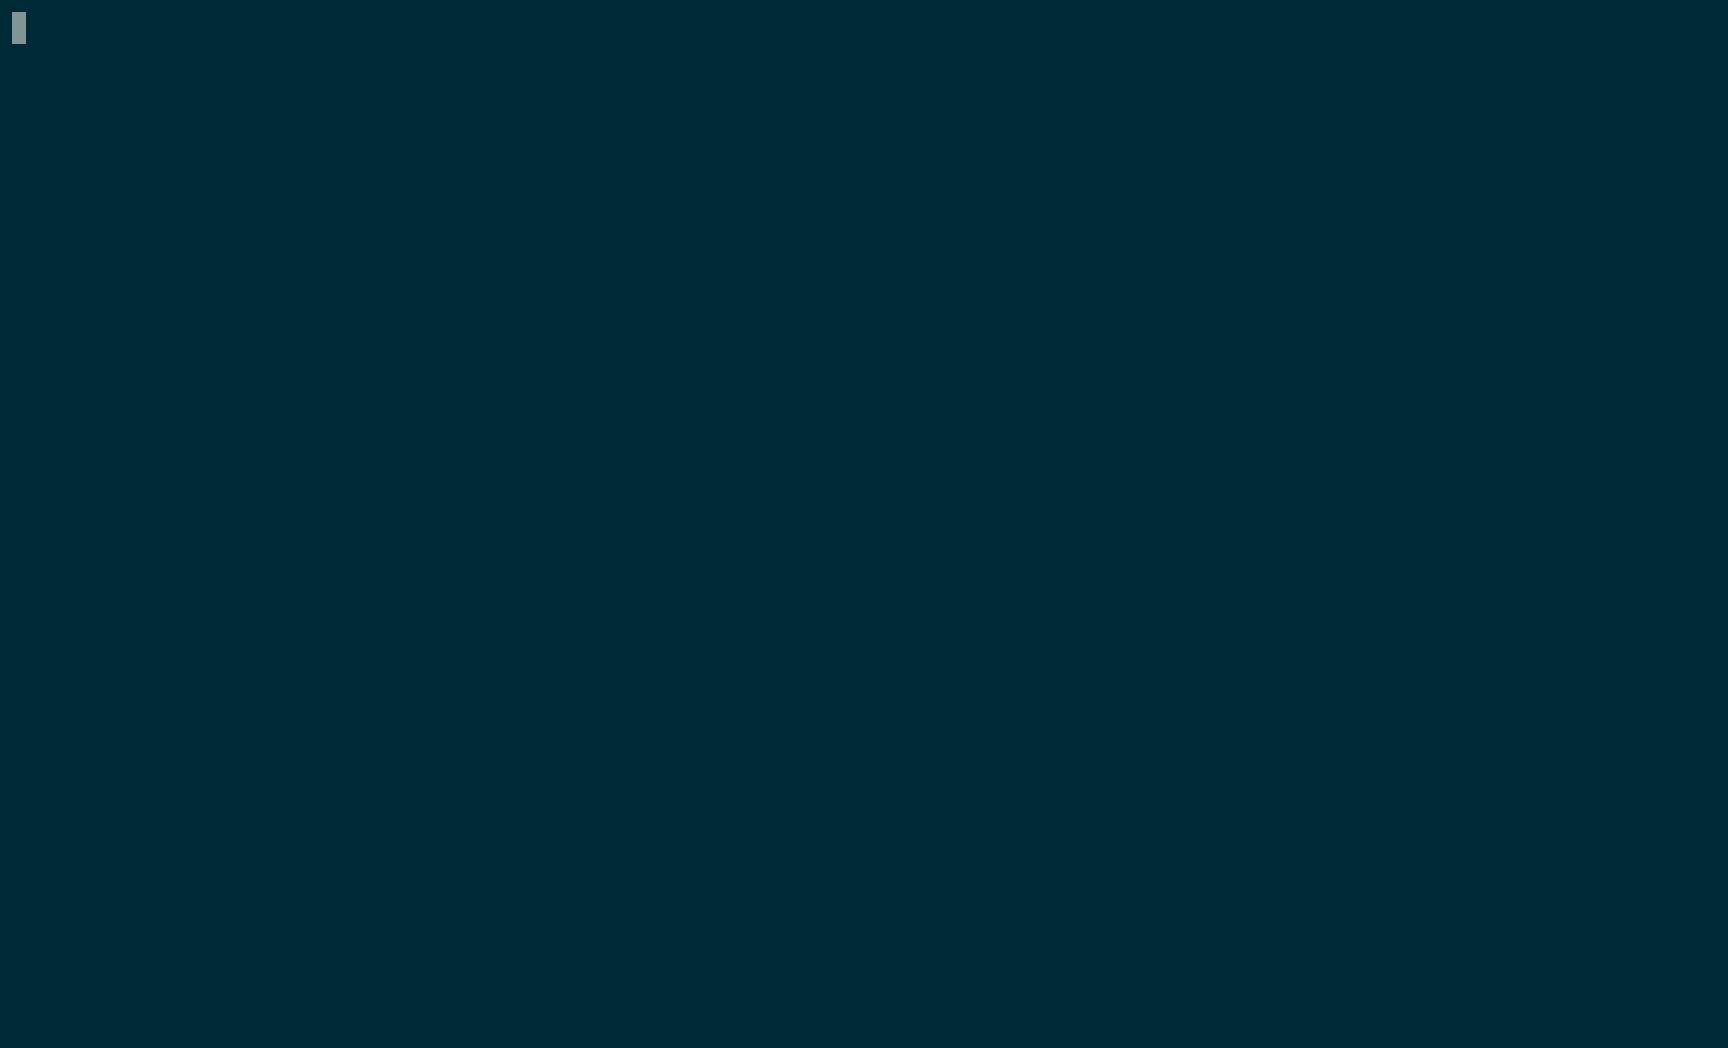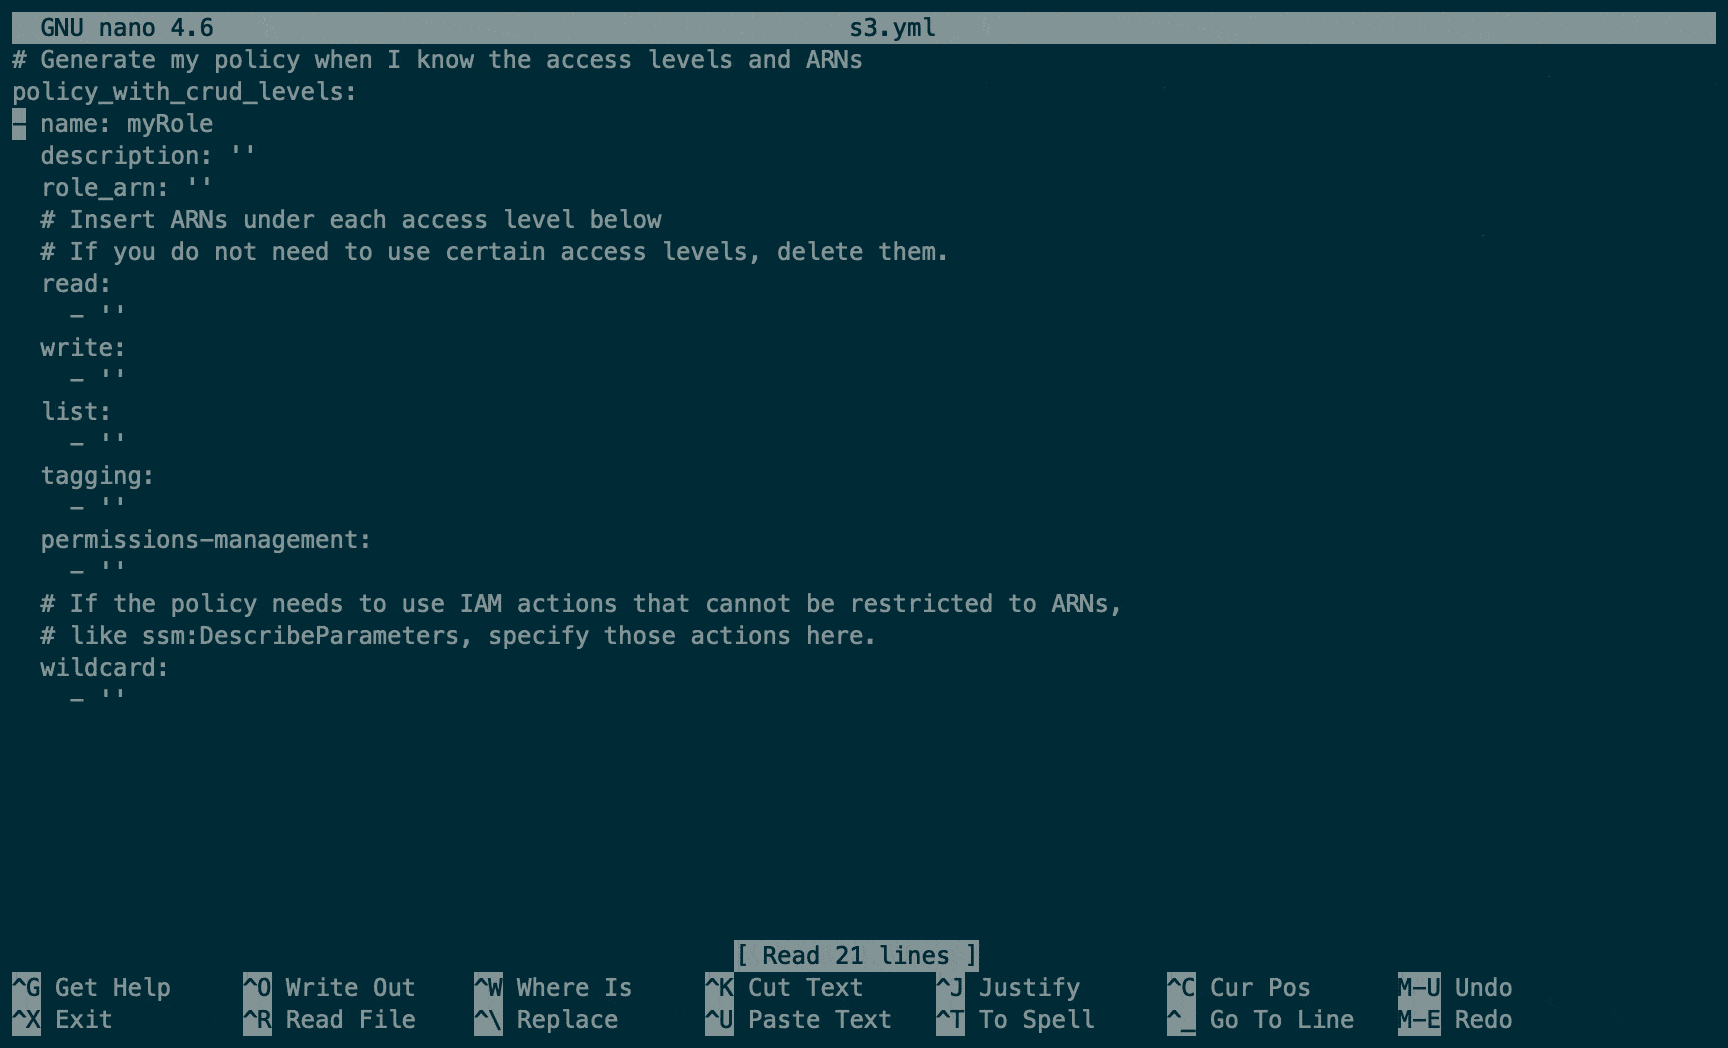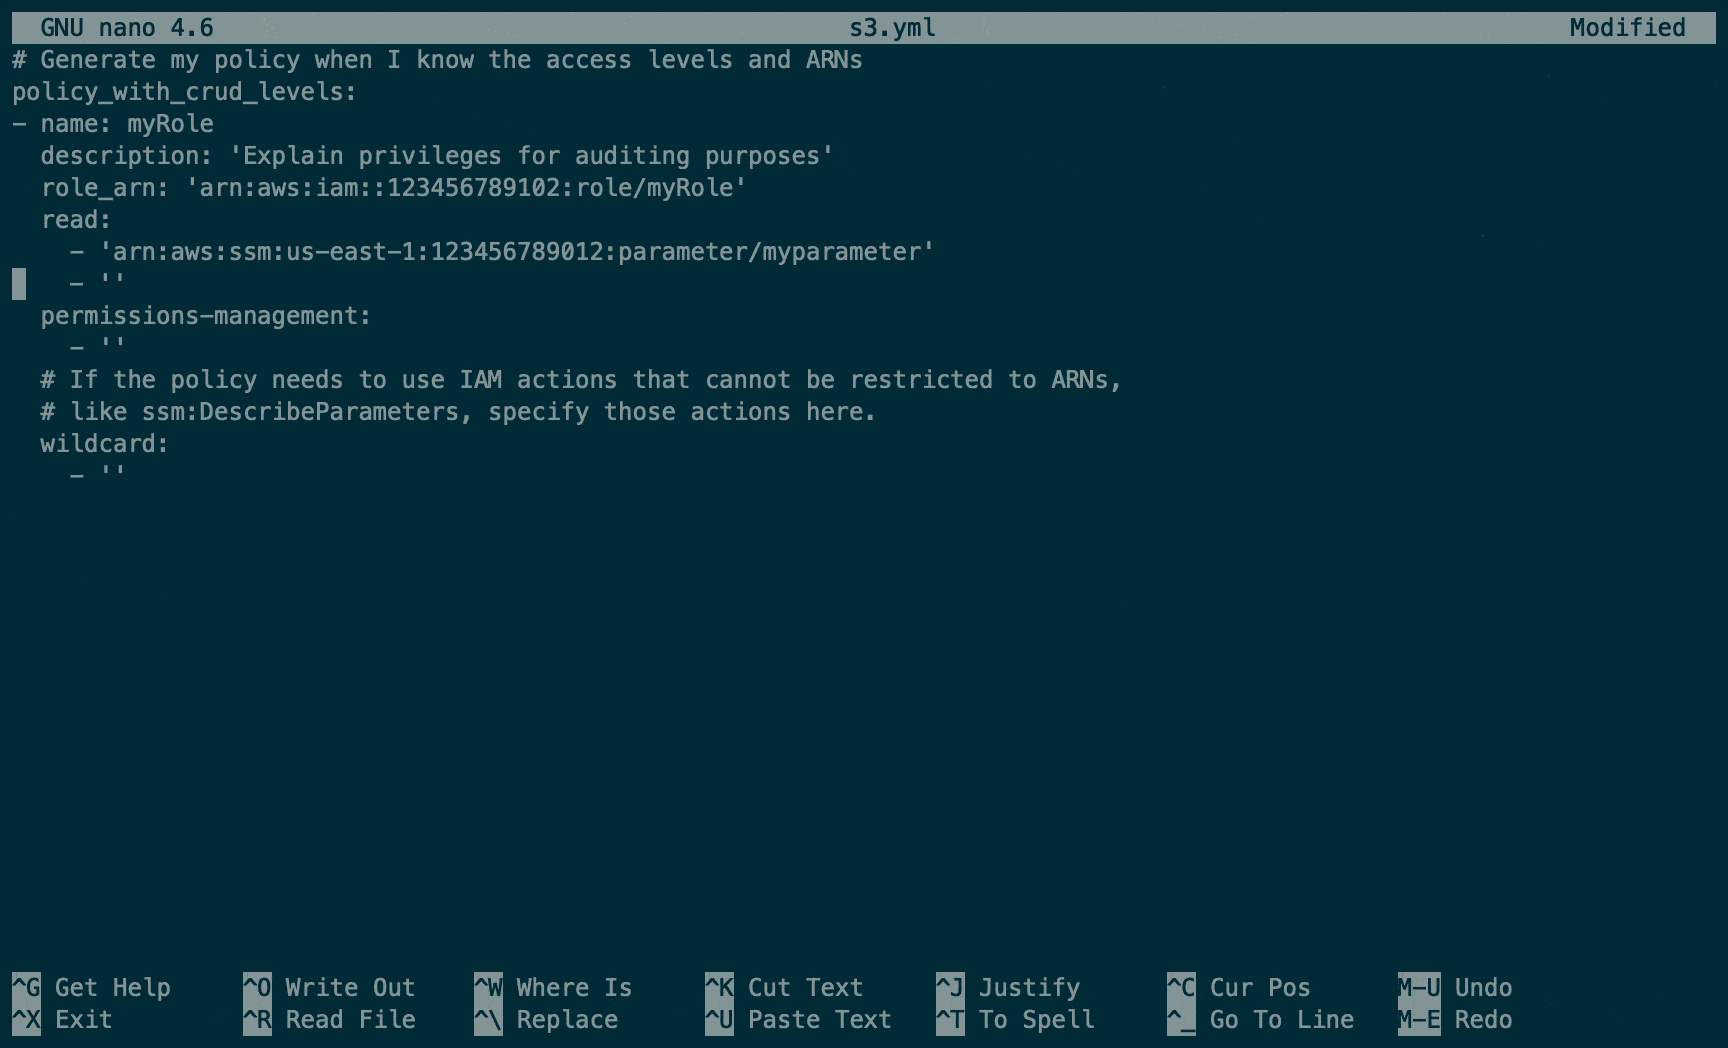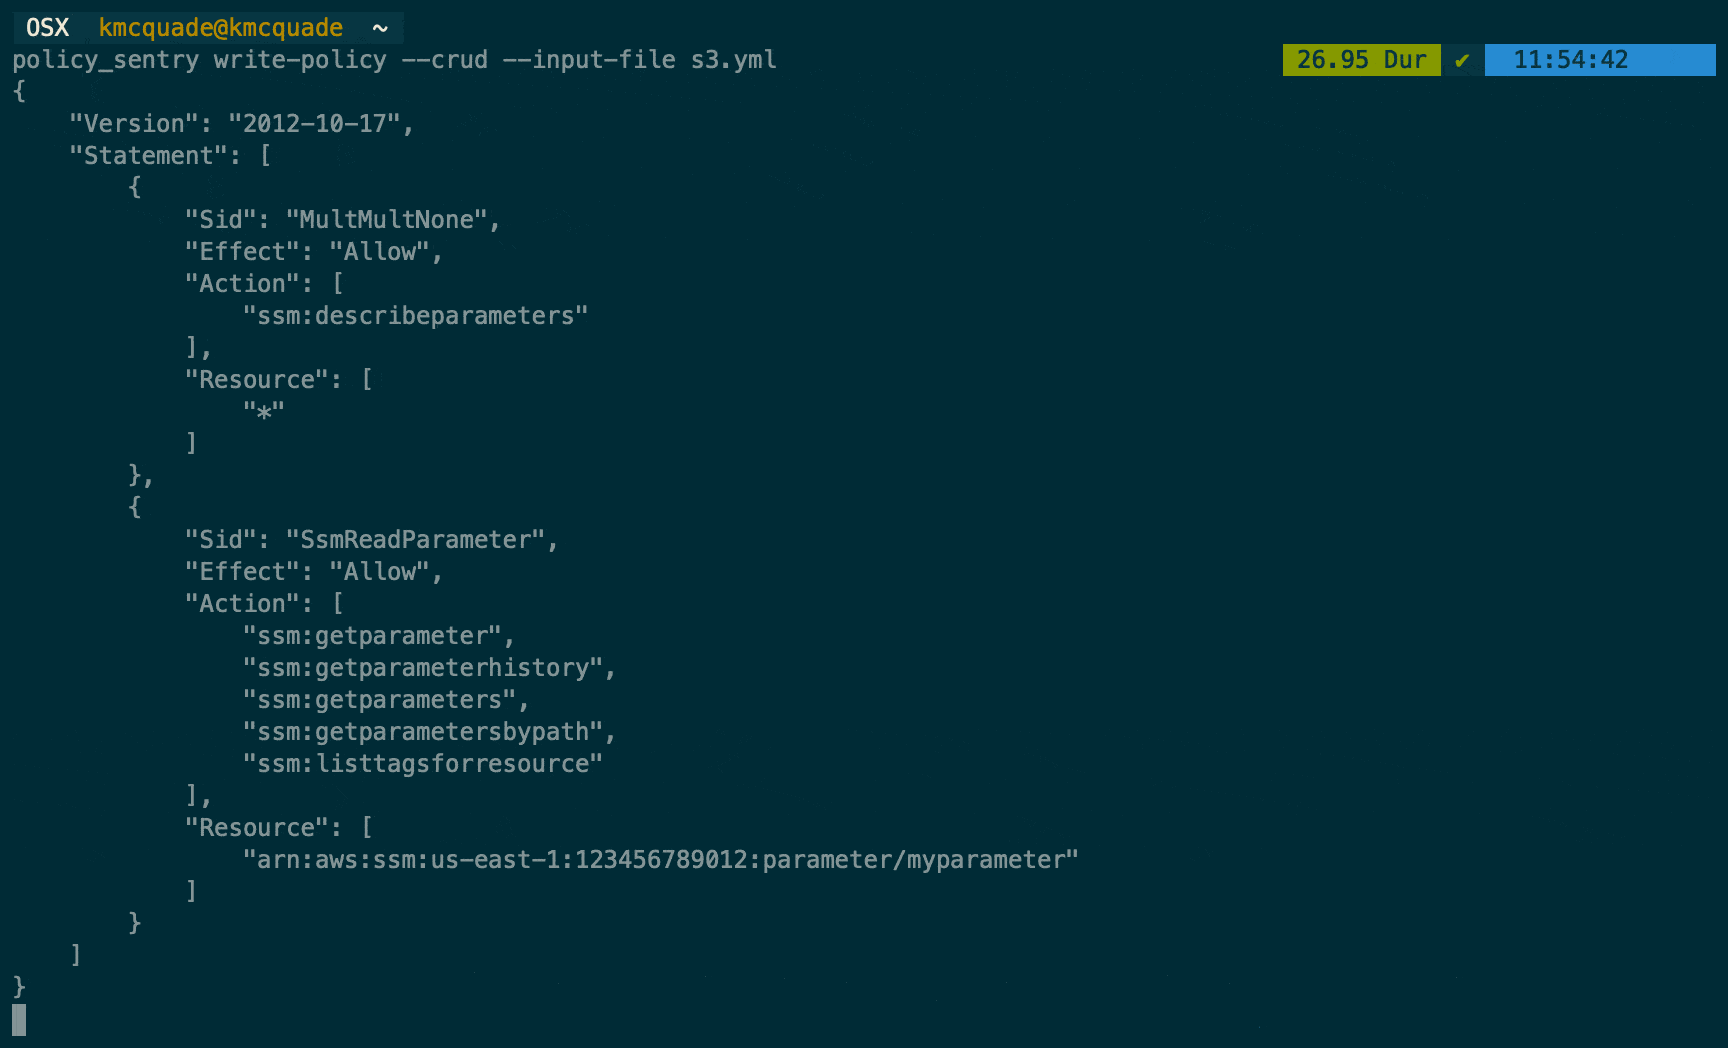 salesforce/policy_sentry
Generates least-privilege AWS IAM policies based on resource ARNs and access levels, automating secure policy creation for cloud infrastructure.
 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 aquasecurity/trivy-plugin-kubectl
A Trivy plugin that scans the images of a kubernetes resource
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance