
cynative
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
ai-securitycloud-securitycontainer-security+7
202
cynative/cynativeRead-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
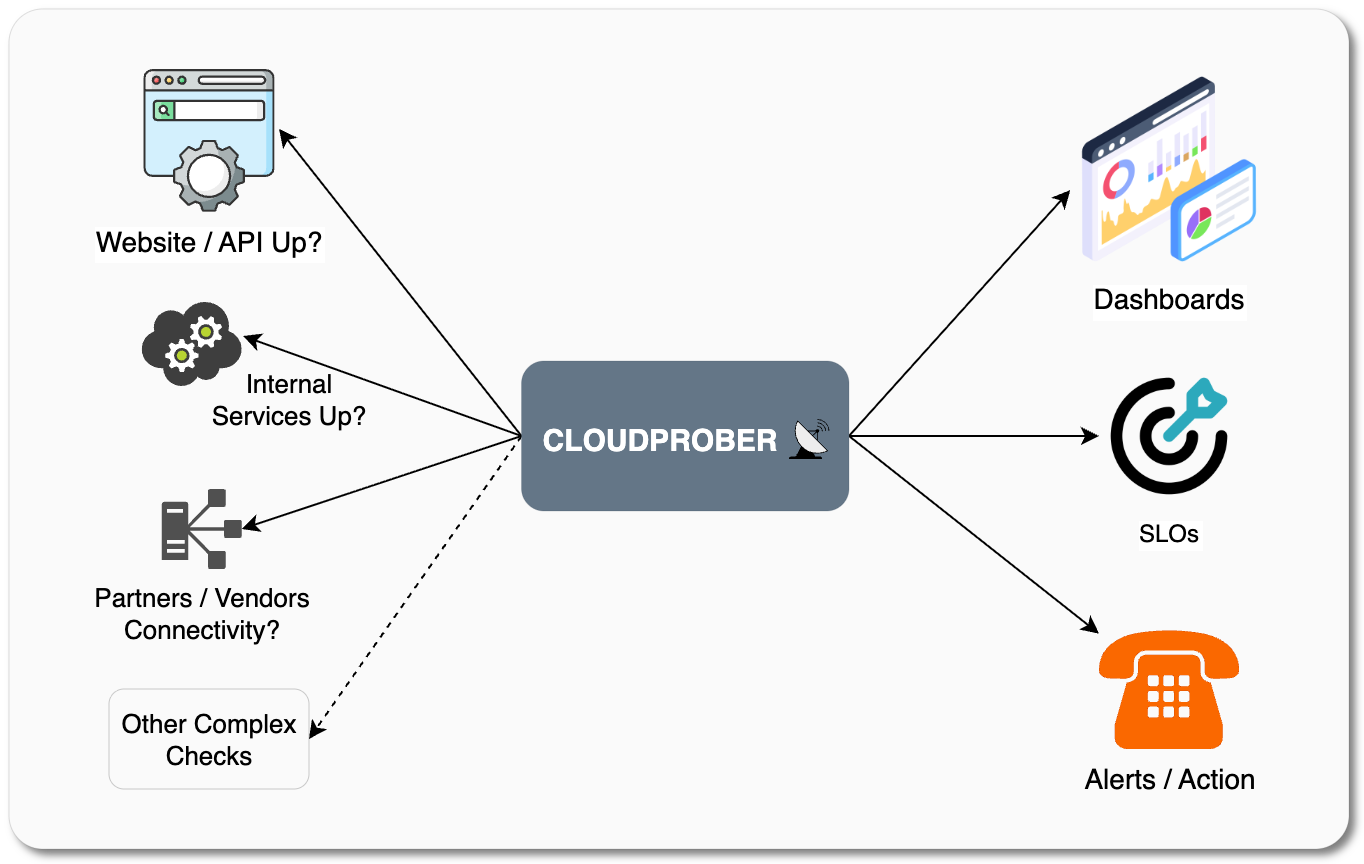 cloudprober/cloudprober
An active monitoring software to detect failures before your customers do.
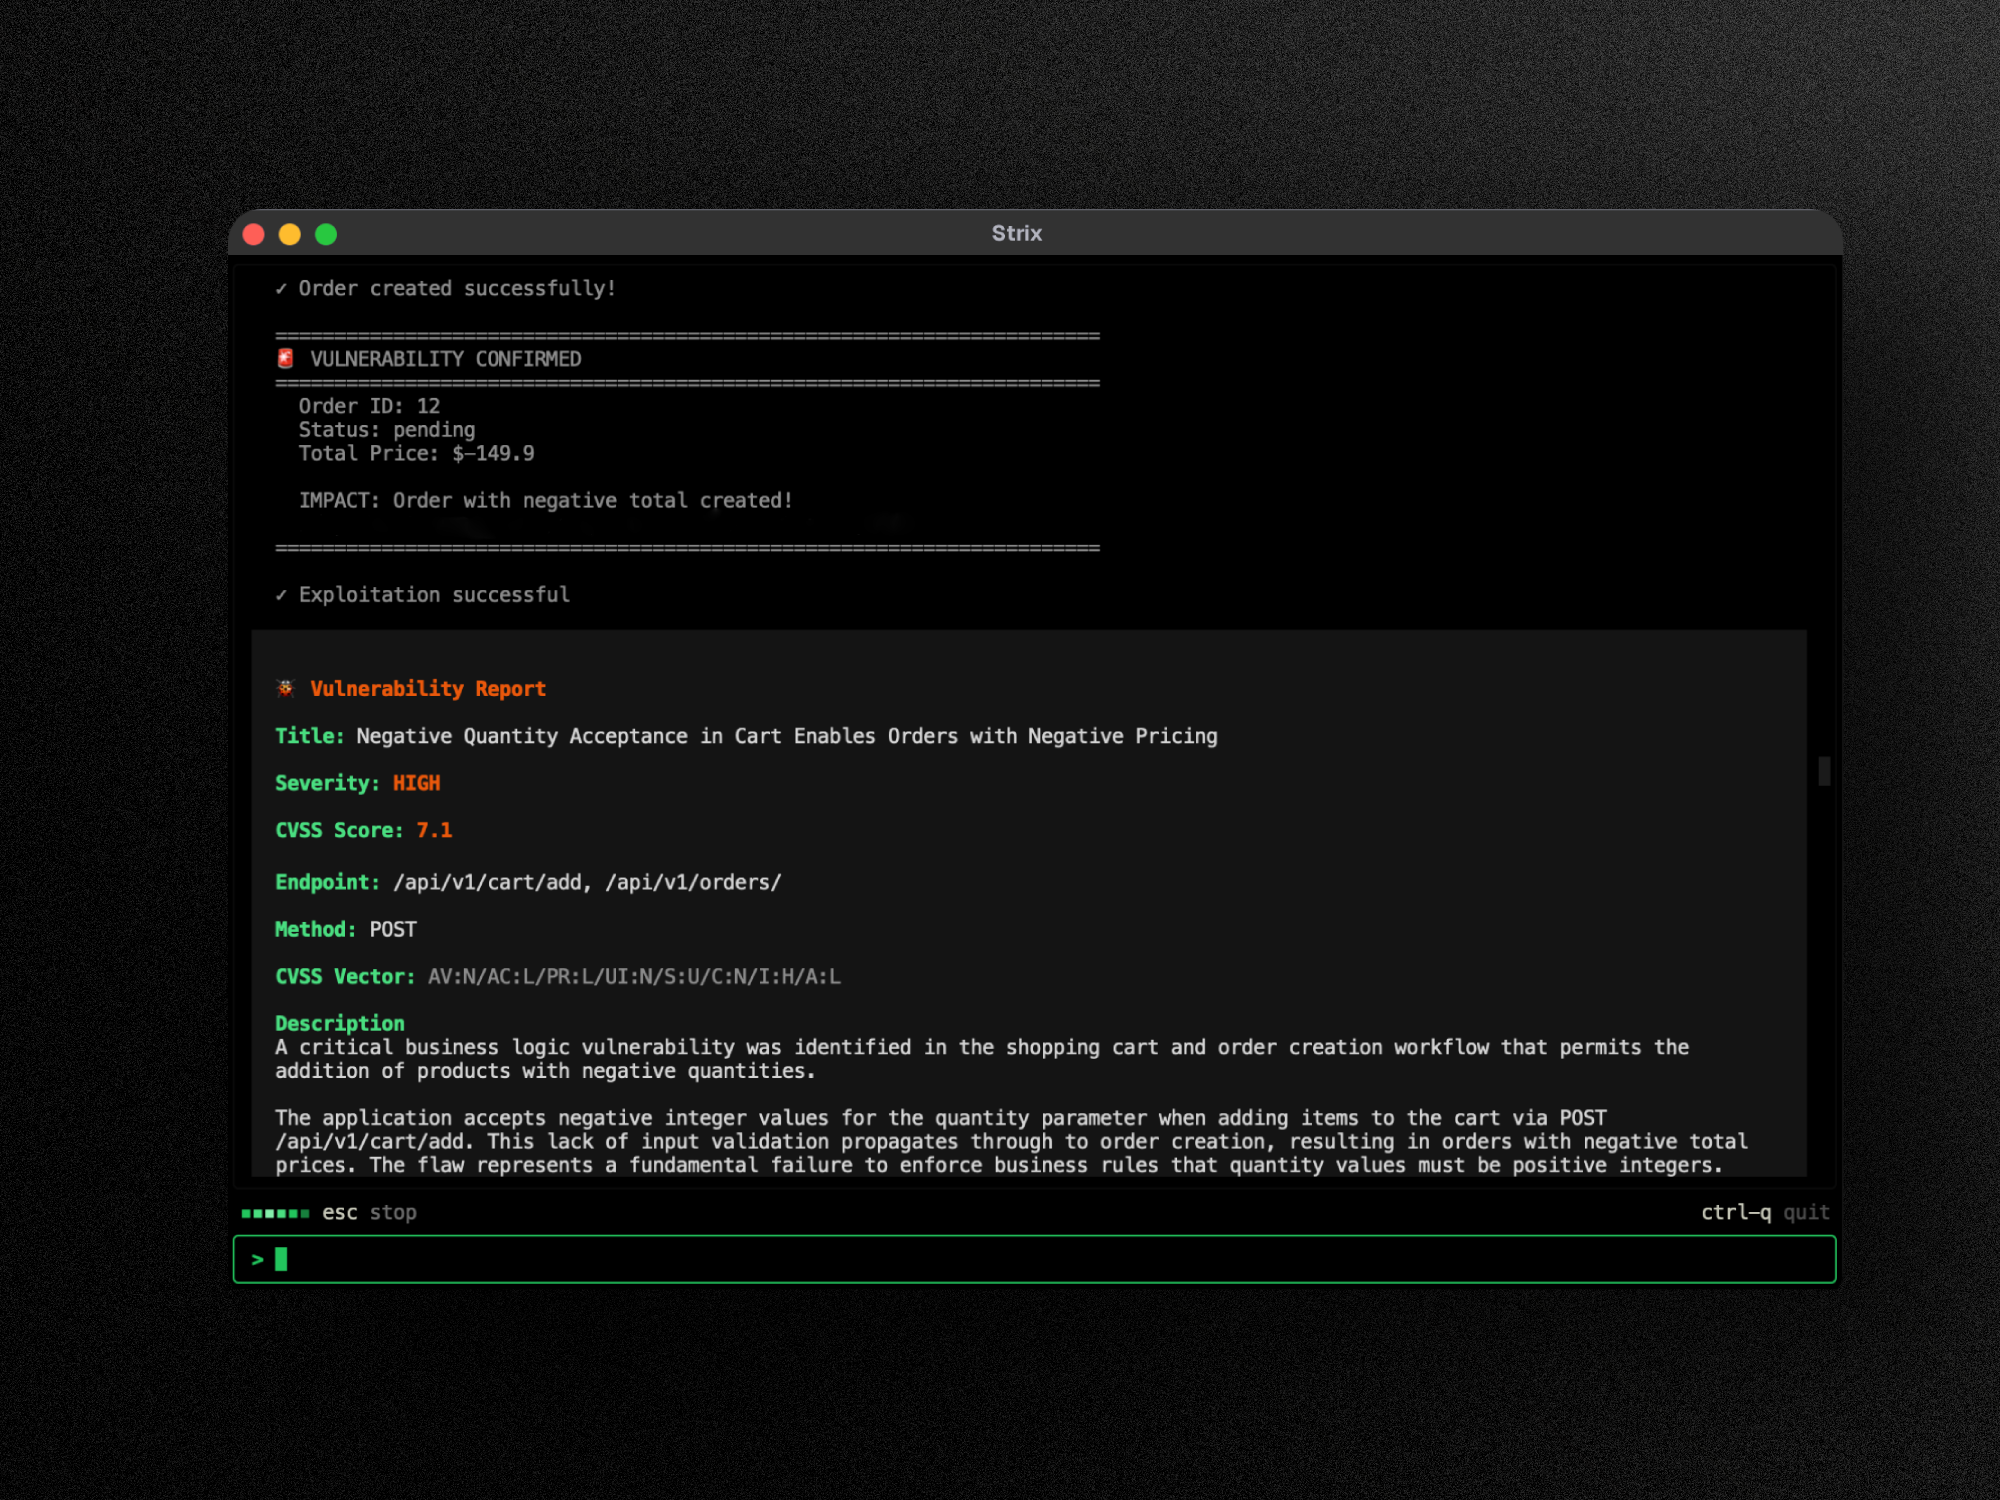 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
 raskrebs/sonar
CLI tool for inspecting and managing services listening on localhost ports
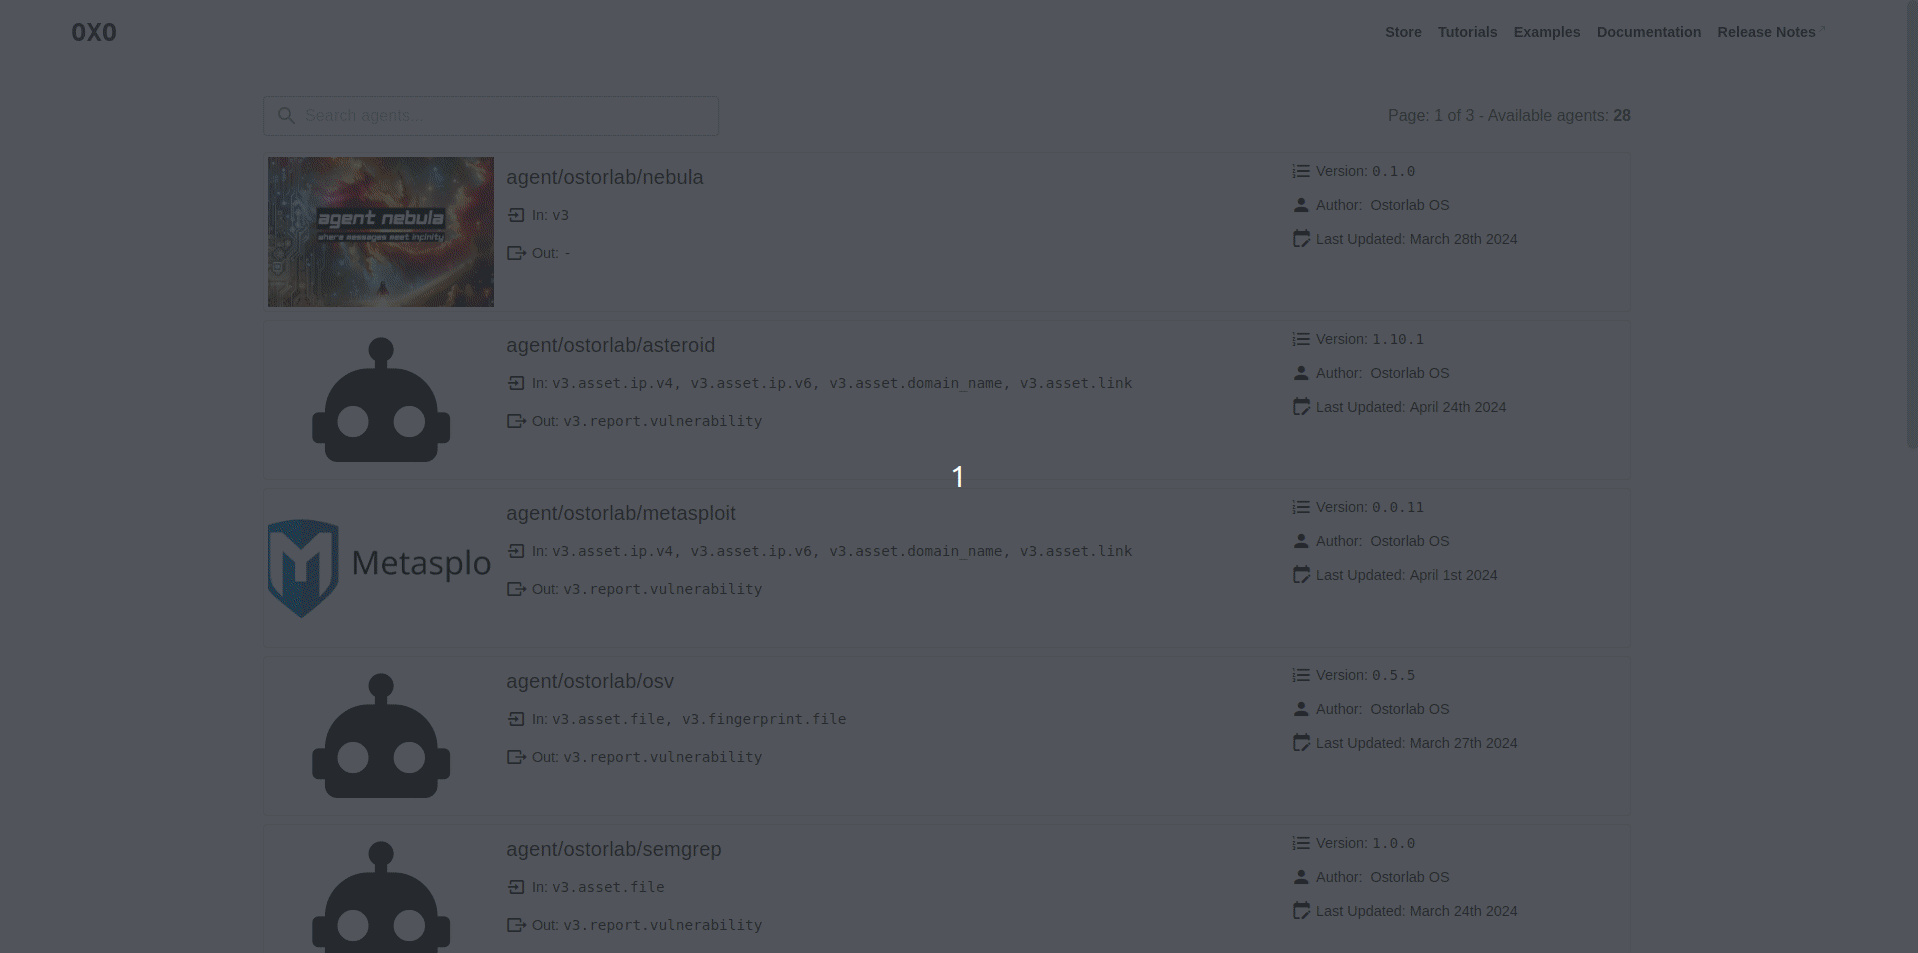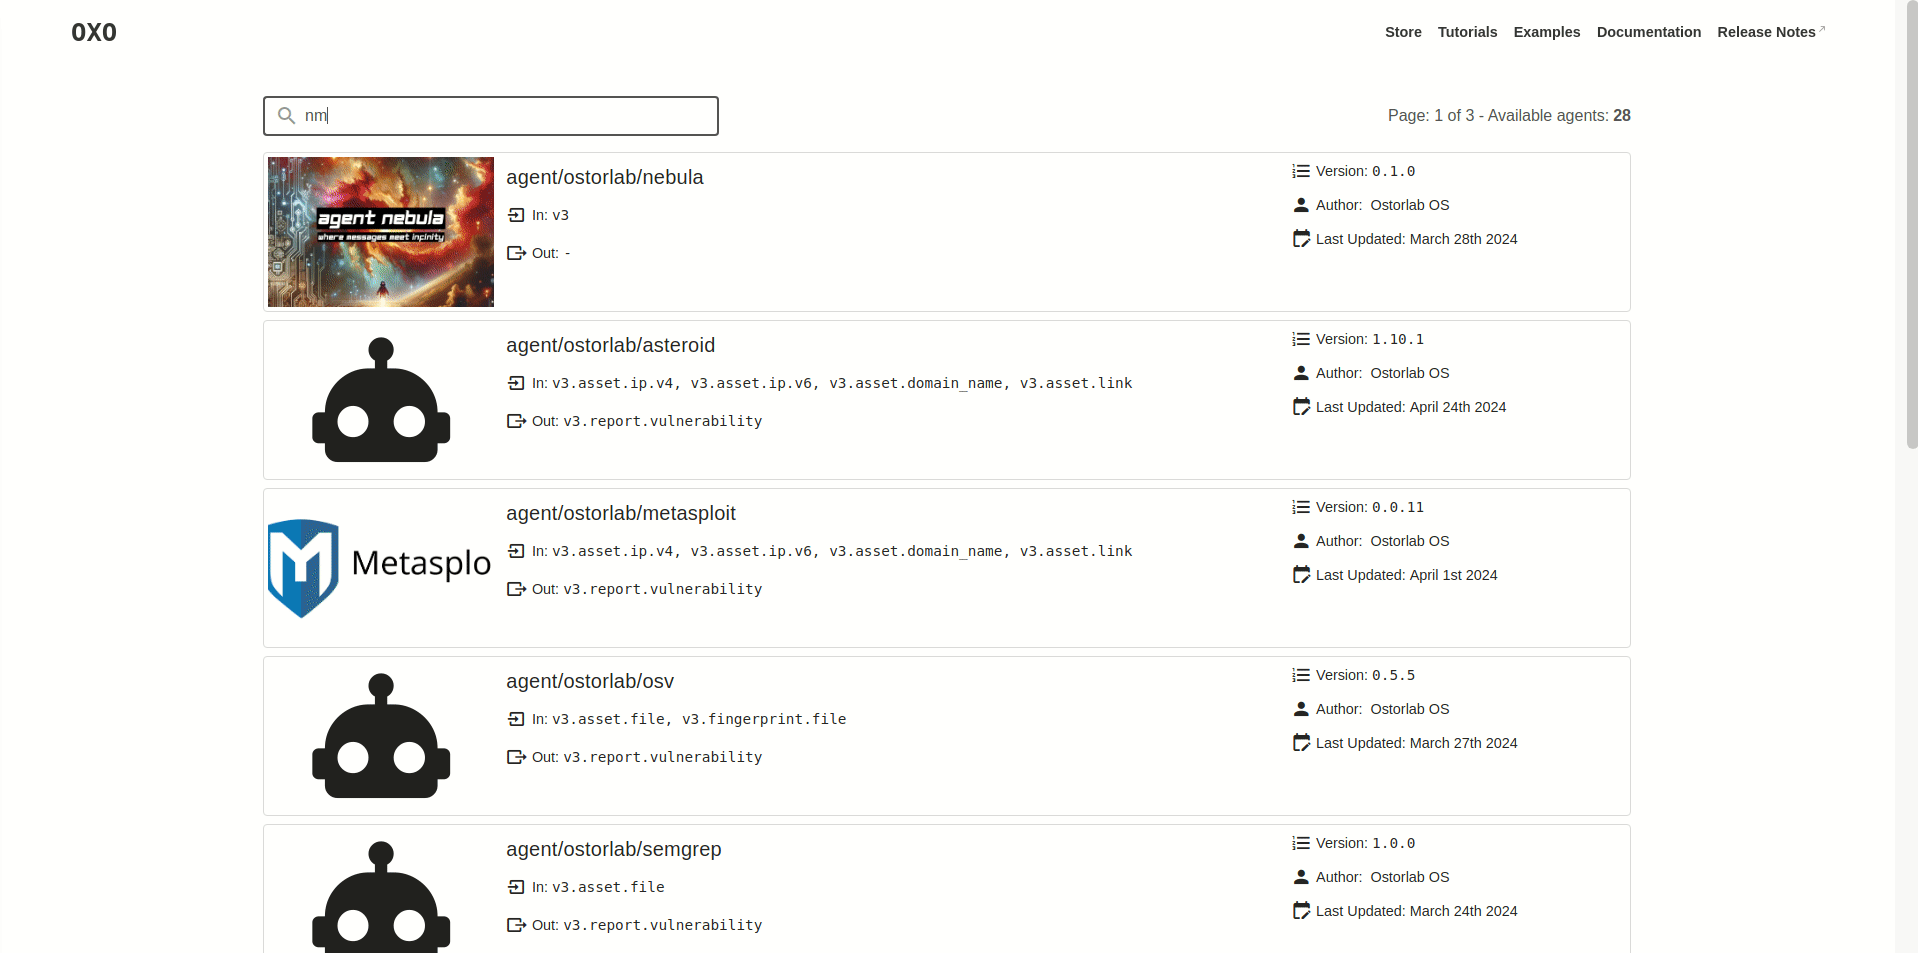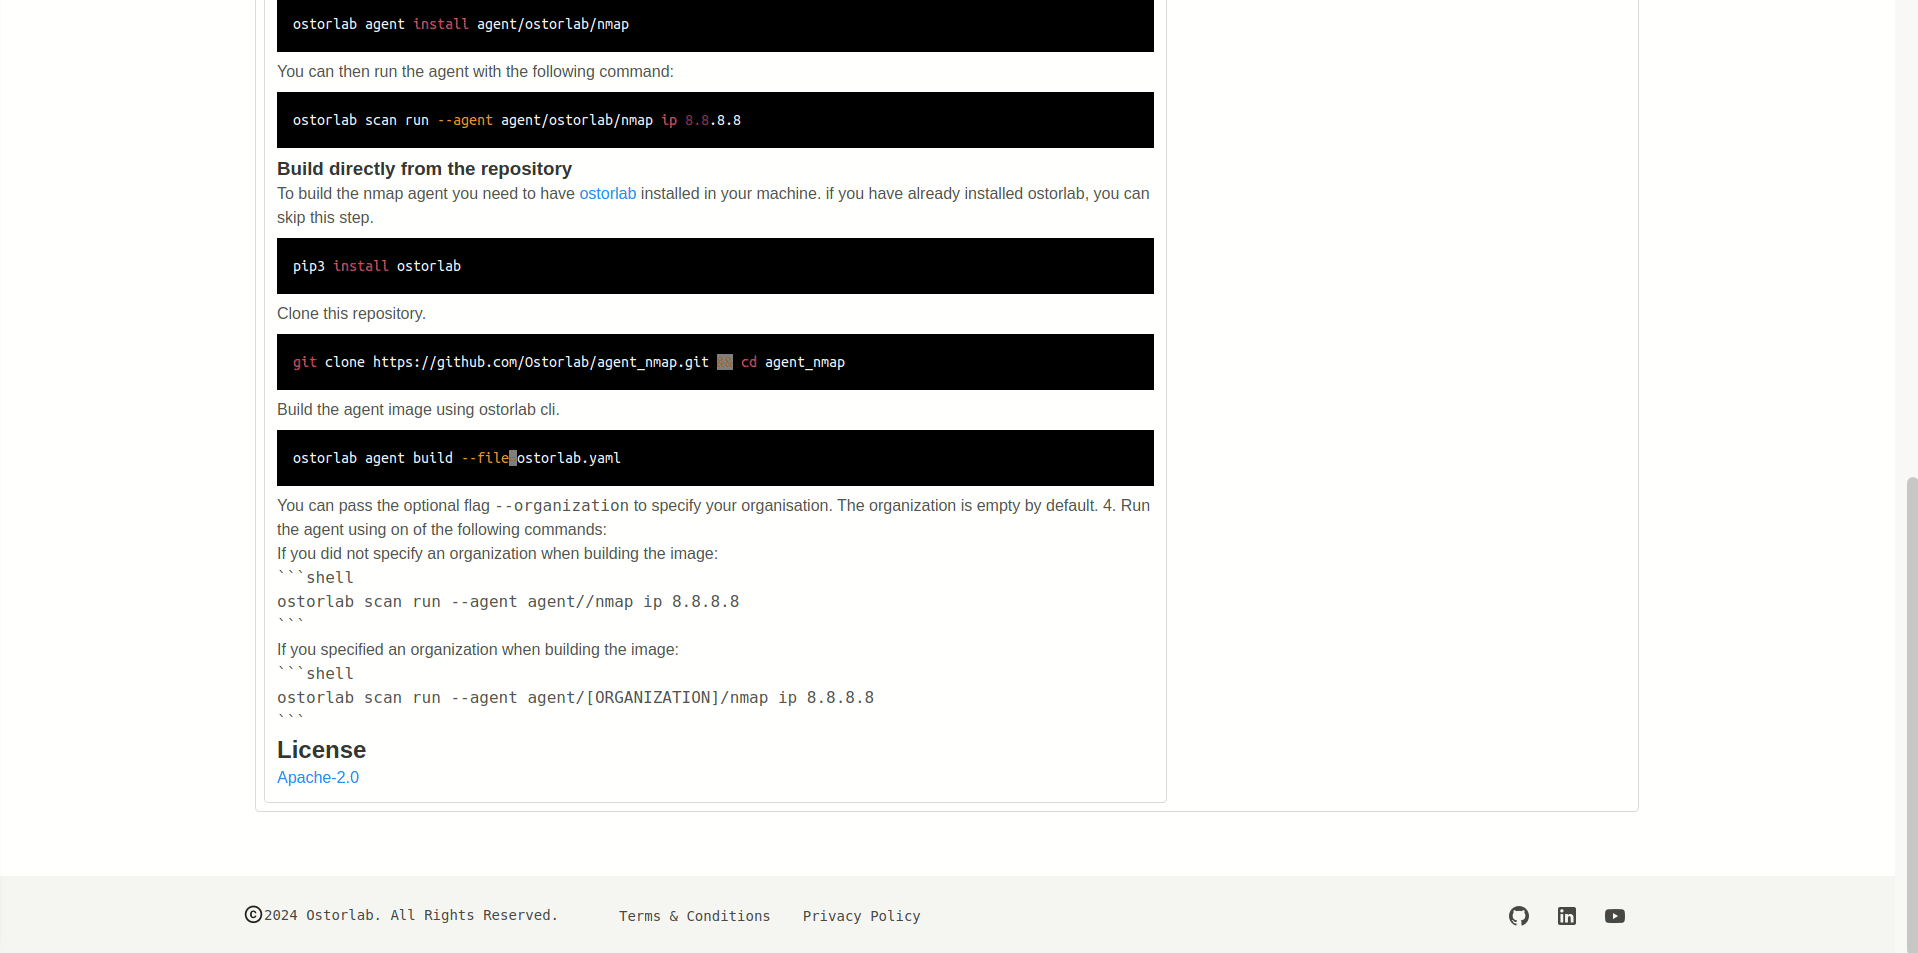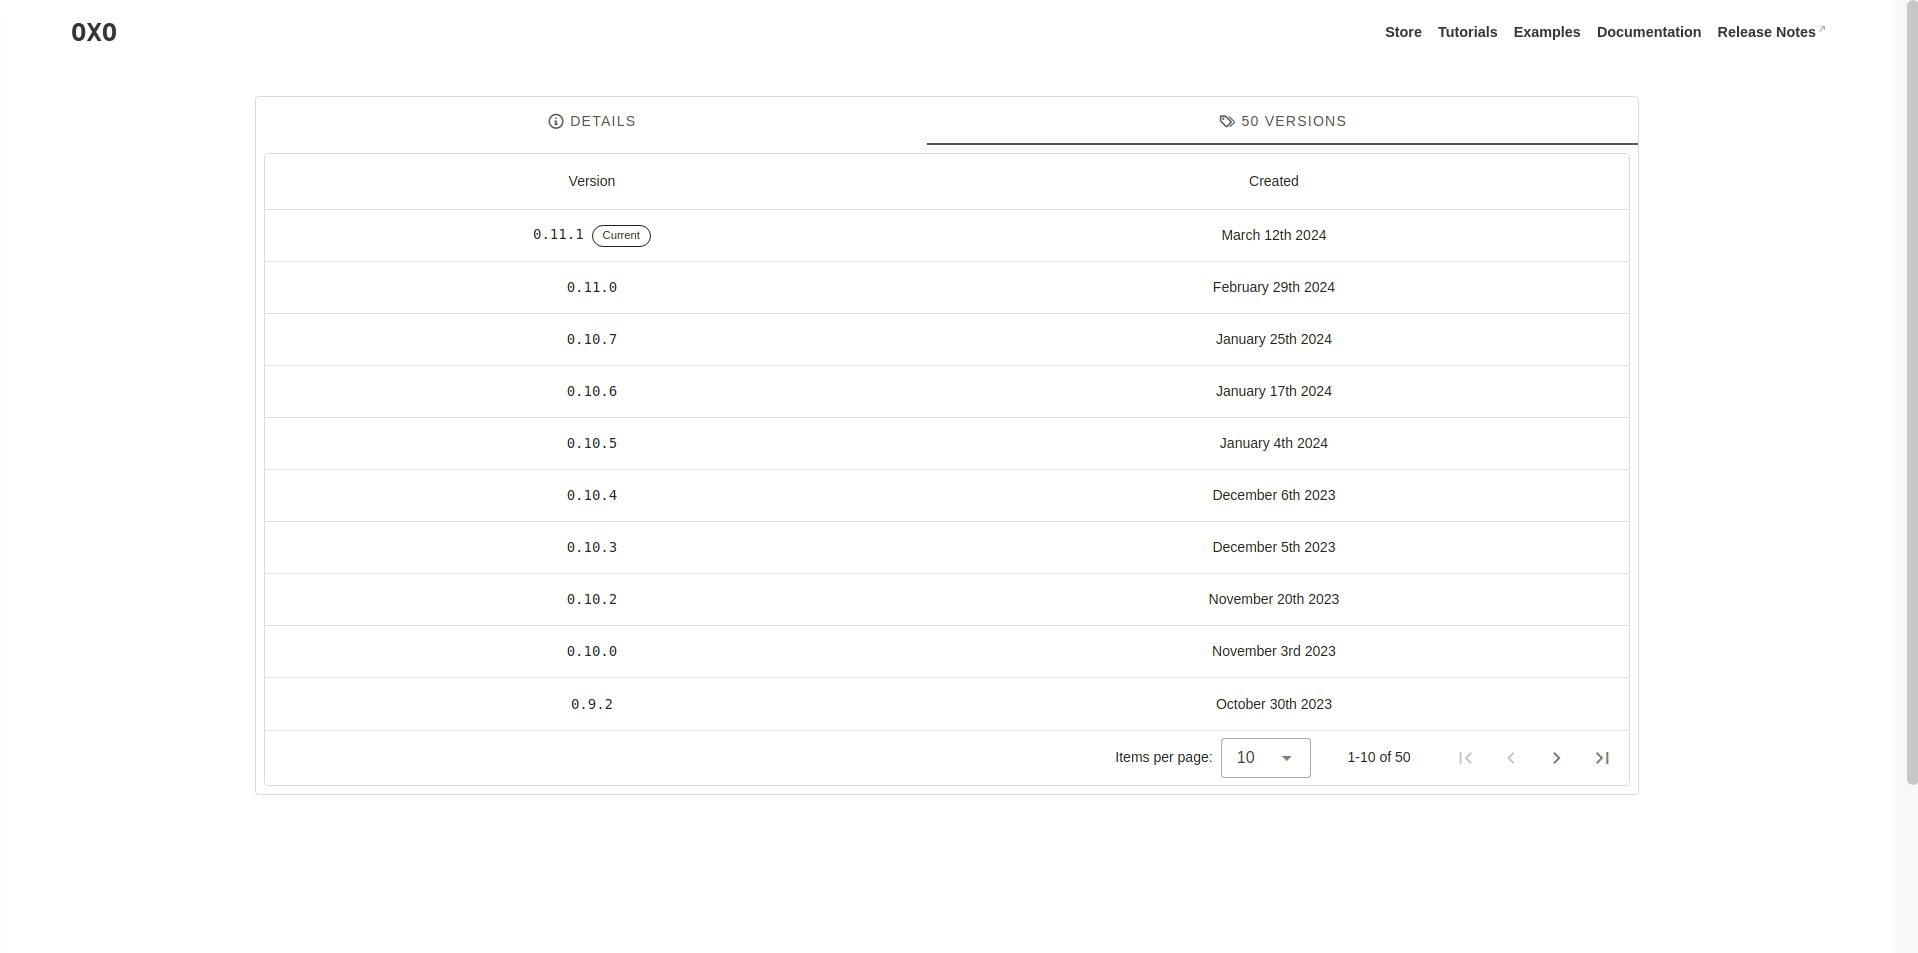 ostorlab/oxo
Modular security scanning orchestrator that combines specialized agents for vulnerability detection, reconnaissance, and fingerprinting across…
 ascit31/dark-moon
Autonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…
 netalertx/netalertx
Centralized network visibility and continuous asset discovery. Monitor devices, detect change, and stay aware across distributed networks.
 xalgord/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 pensarai/apex
AI-powered offensive security testing using autonomous agents, directly in your terminal.
 jsdelivr/globalping-probe
The globalping probe code that runs on your hardware and connects to the global community network of probes
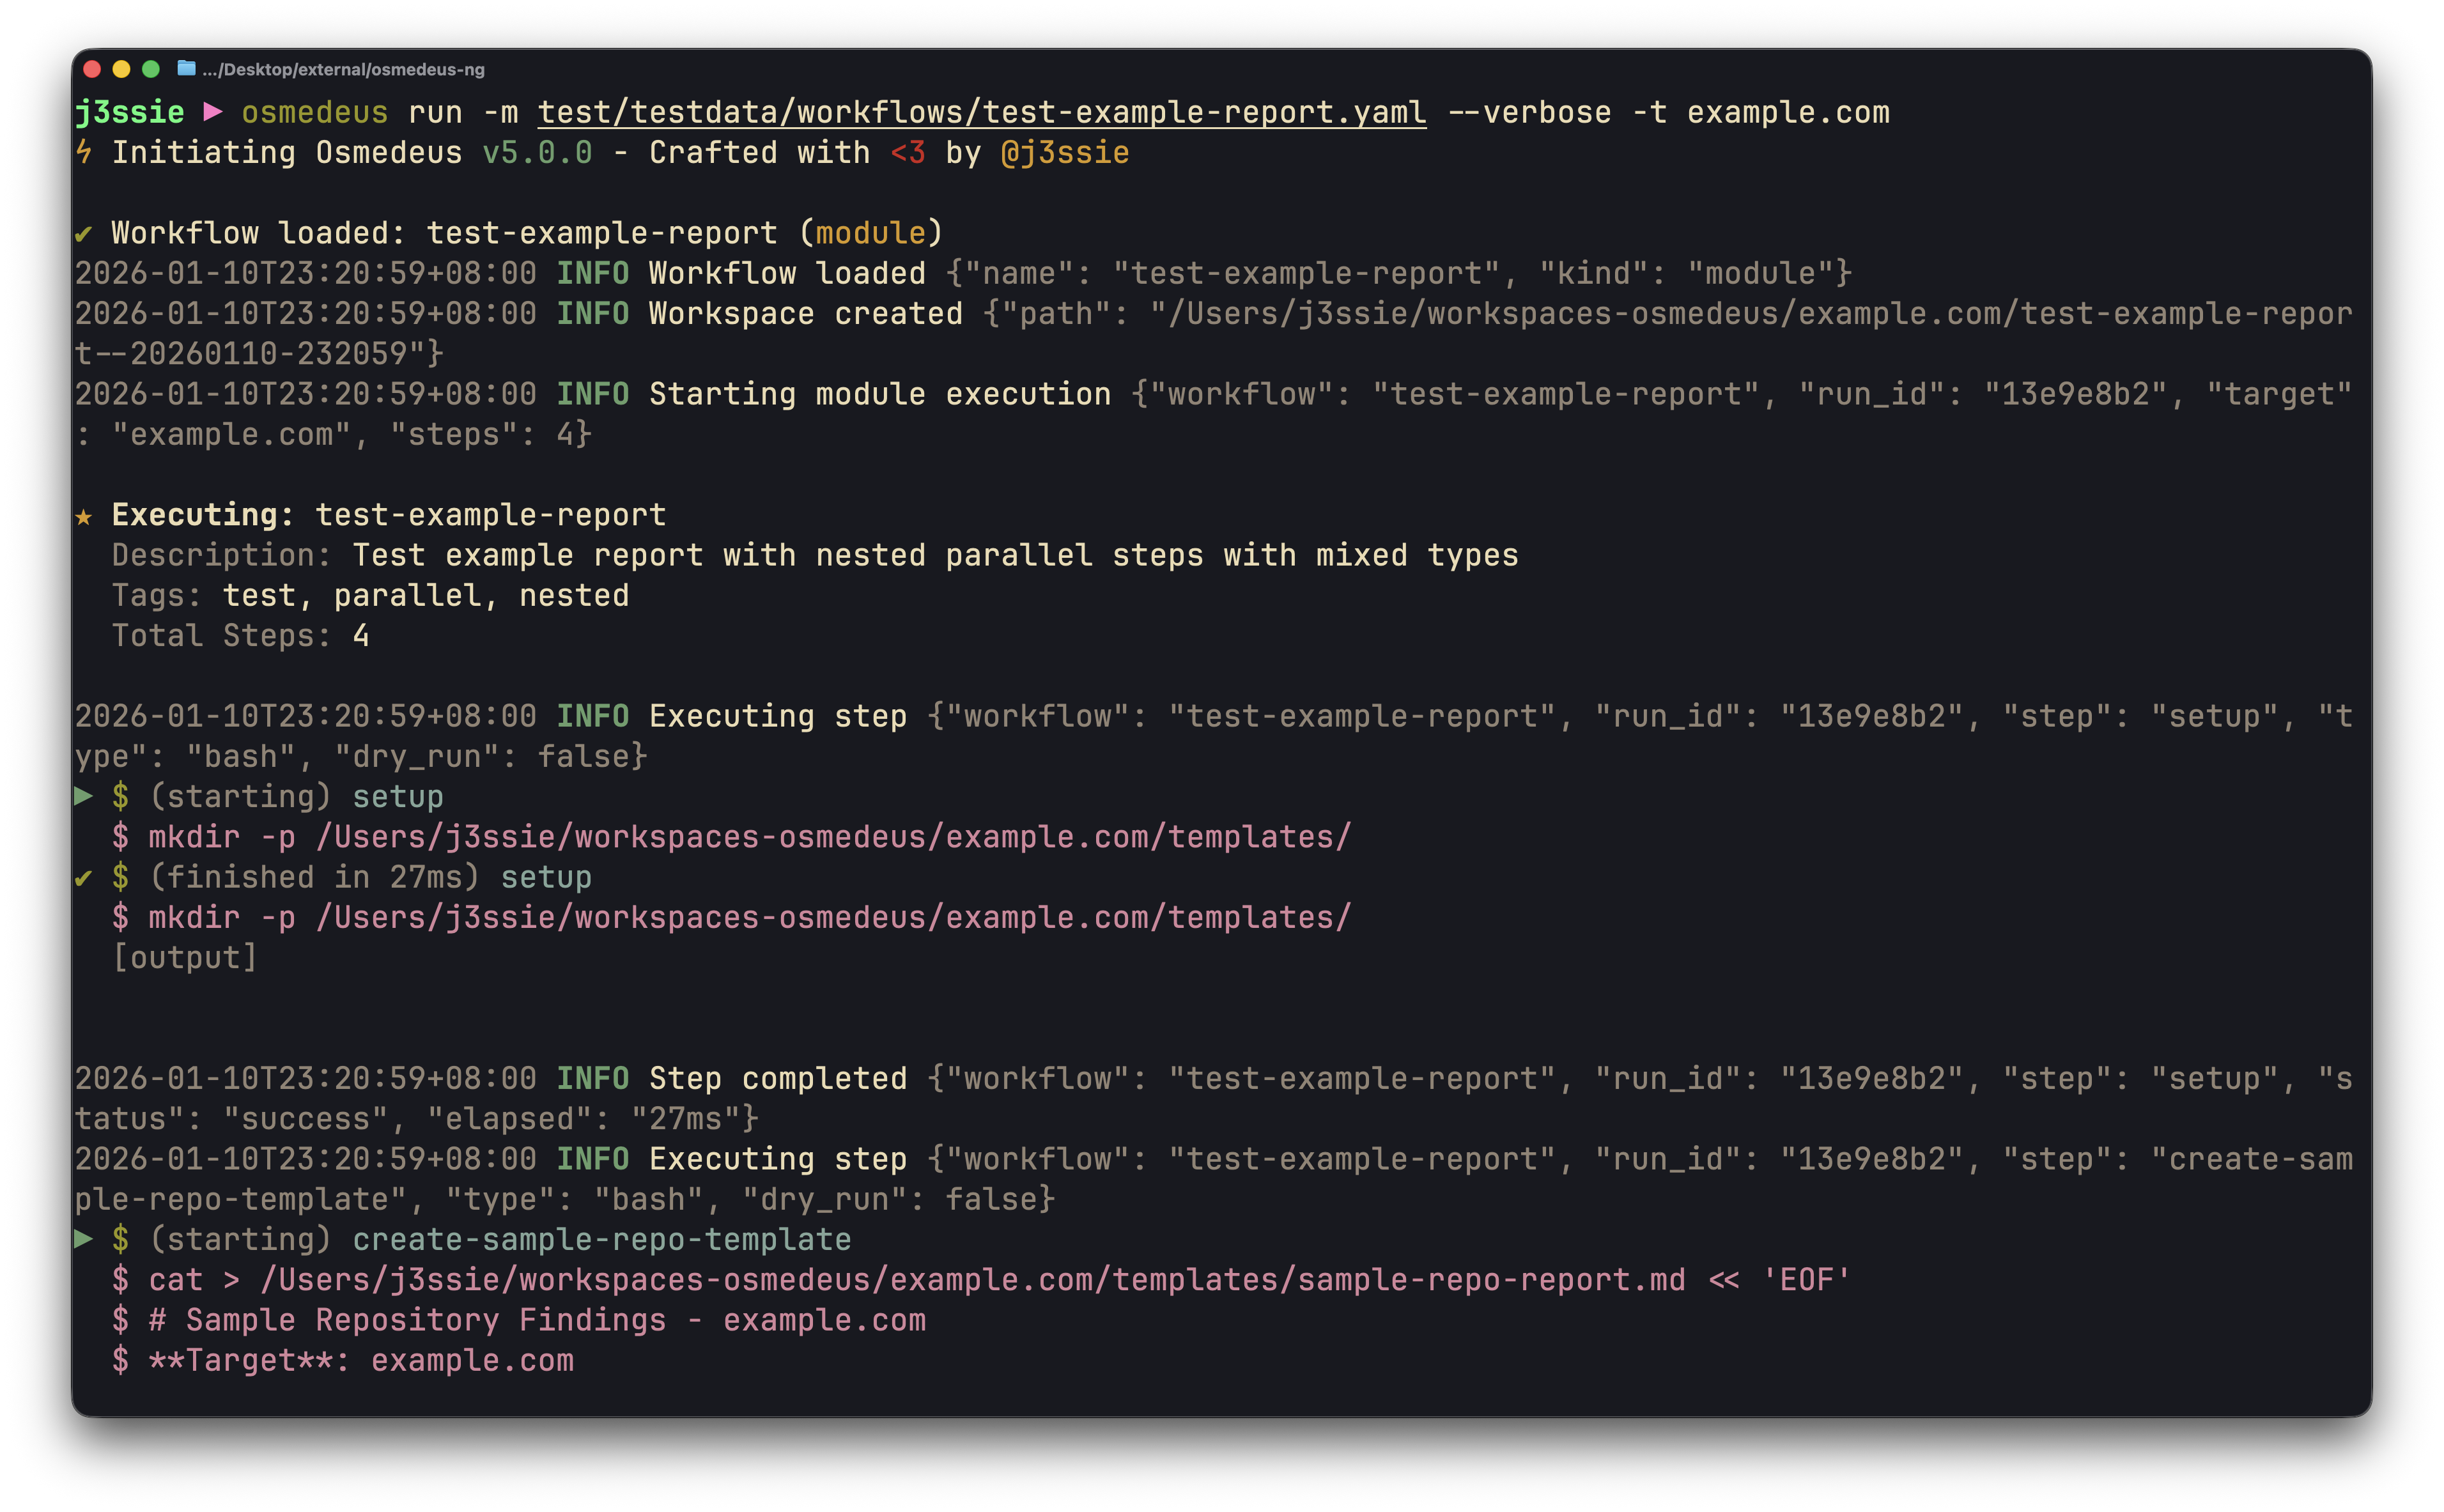 j3ssie/osmedeus
A Modern Orchestration Engine for Security
 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 infobyte/faraday
Open Source Vulnerability Management Platform
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
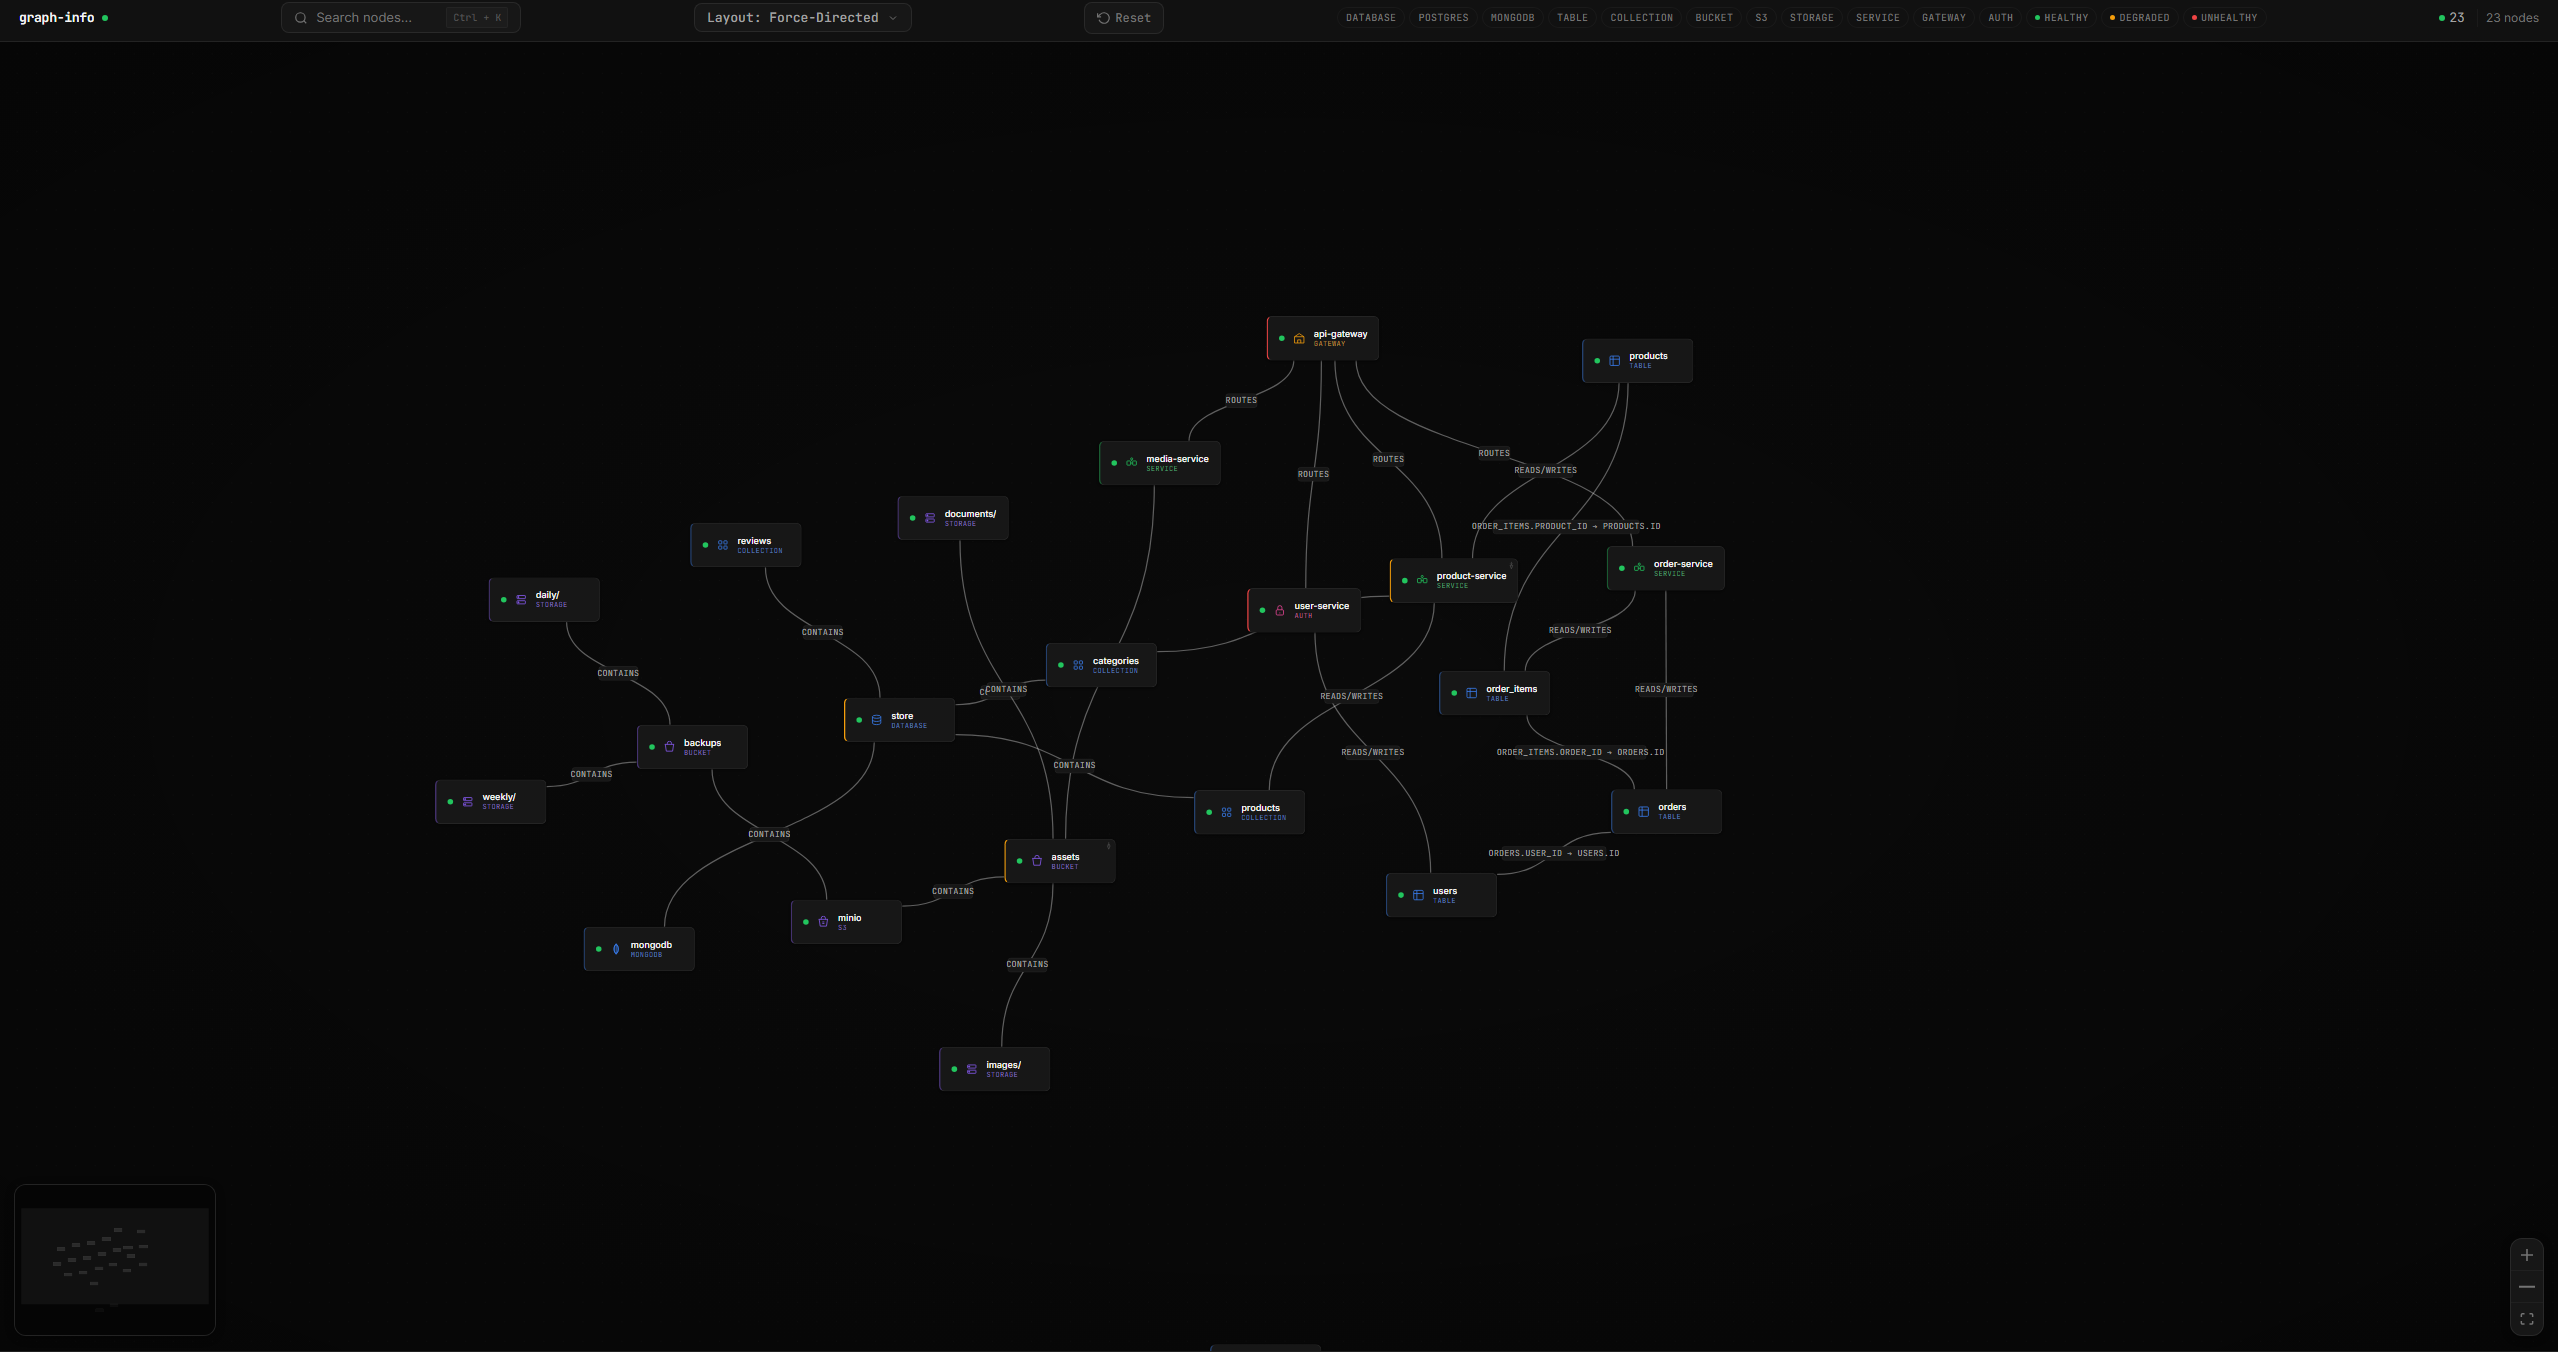 guilherme-grimm/graph-go
simply nodes and graphs