

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
11.1k
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
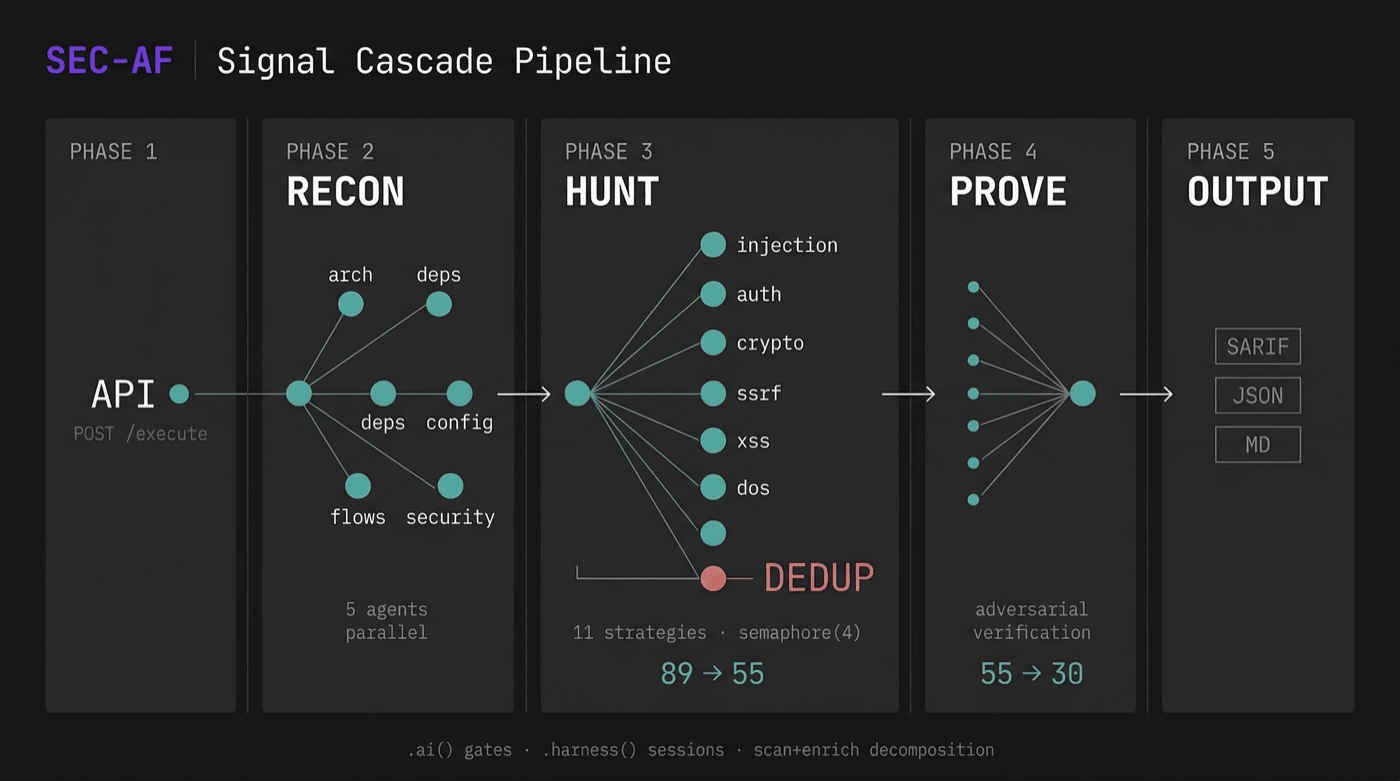 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
 ansvar-systems/eu_compliance_mcp
EU focused compliance MCP server
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 gitlab-da/tutorials/security-and-governance/custom-scanner-integration/fern-pattern-scanner
Scans selected files for patterns stated in rules. This is used in order to find secrets you may have accidentally written to a file. This scanner is…
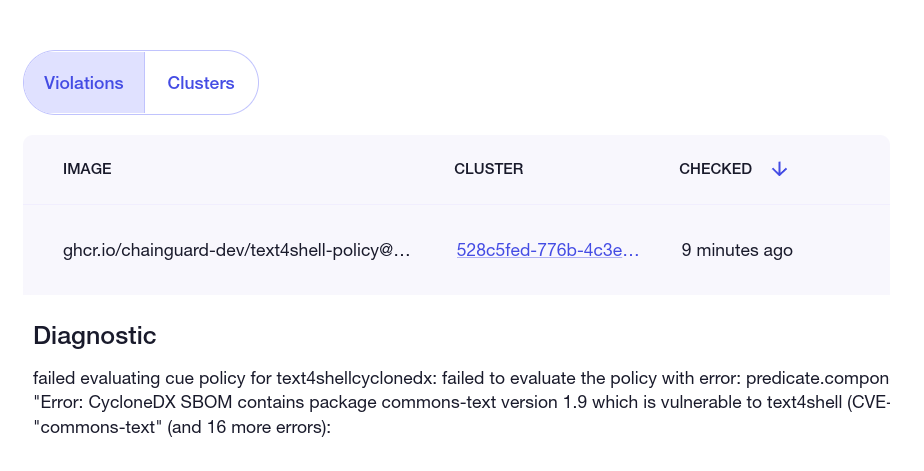 chainguard-dev/text4shell-policy
ClusterImagePolicy demo for cve-2022-42889 text4shell
 alexandreroman/cve-2021-44228-workaround-buildpack
Buildpack providing a workaround for CVE-2021-44228 (Log4j RCE exploit)
 itinerisltd/trellis-cve-2018-6389
Mitigate CVE-2018-6389 WordPress load-scripts / load-styles attacks