
aquaman
 tech4242/aquaman
🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…
api-securityauthentication-authorizationcloud-security+7
37
tech4242/aquaman🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…
 xiaoqimikko/async-http-client-check
Self-hosted AI workspace with agents, skills, and tools (Gmail, Calendar) that runs entirely on your own provider API keys (BYOK). Bring your own…
 jsdelivr/globalping-probe
The globalping probe code that runs on your hardware and connects to the global community network of probes
 gduma-phdata/patch-cve-2026-07219
Deploys a critical patch for F5 BIG-IP iControl REST vulnerability CVE-2026-07219, with validation and deployment tracking for production…
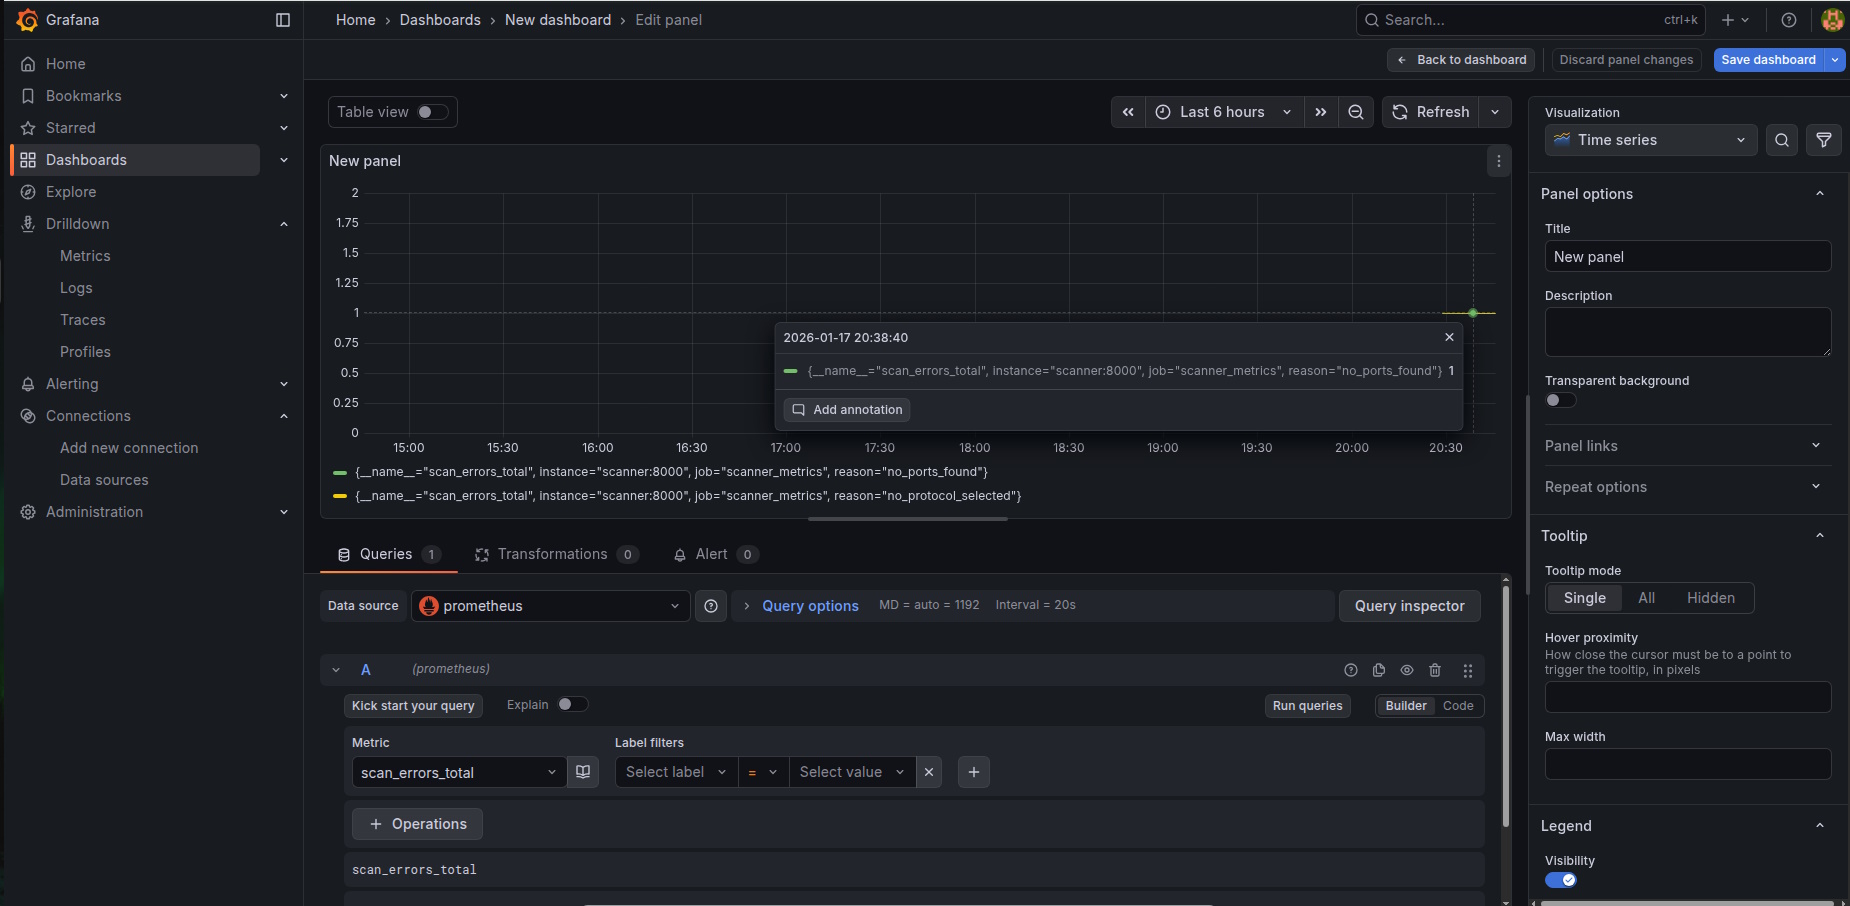 znakar/sharktooth
Port Scanner with Docker & Prometheus + Grafana integration. A tool for network auditing with multithreading support and real-time monitoring.
 ntanwir10/guardscan
100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI
 scythe-io/purple-team-exercise-framework
Purple Team Exercise Framework
 helixar-ai/mcp-security-checklist
MCP is being adopted rapidly. Security guidance is lagging behind. This checklist gives security engineers, platform teams, and technical leaders a…
 delvygonzalez/react2shell-security-toolkit
Security toolkit to detect CVE-2025-55182 (React2Shell) vulnerability
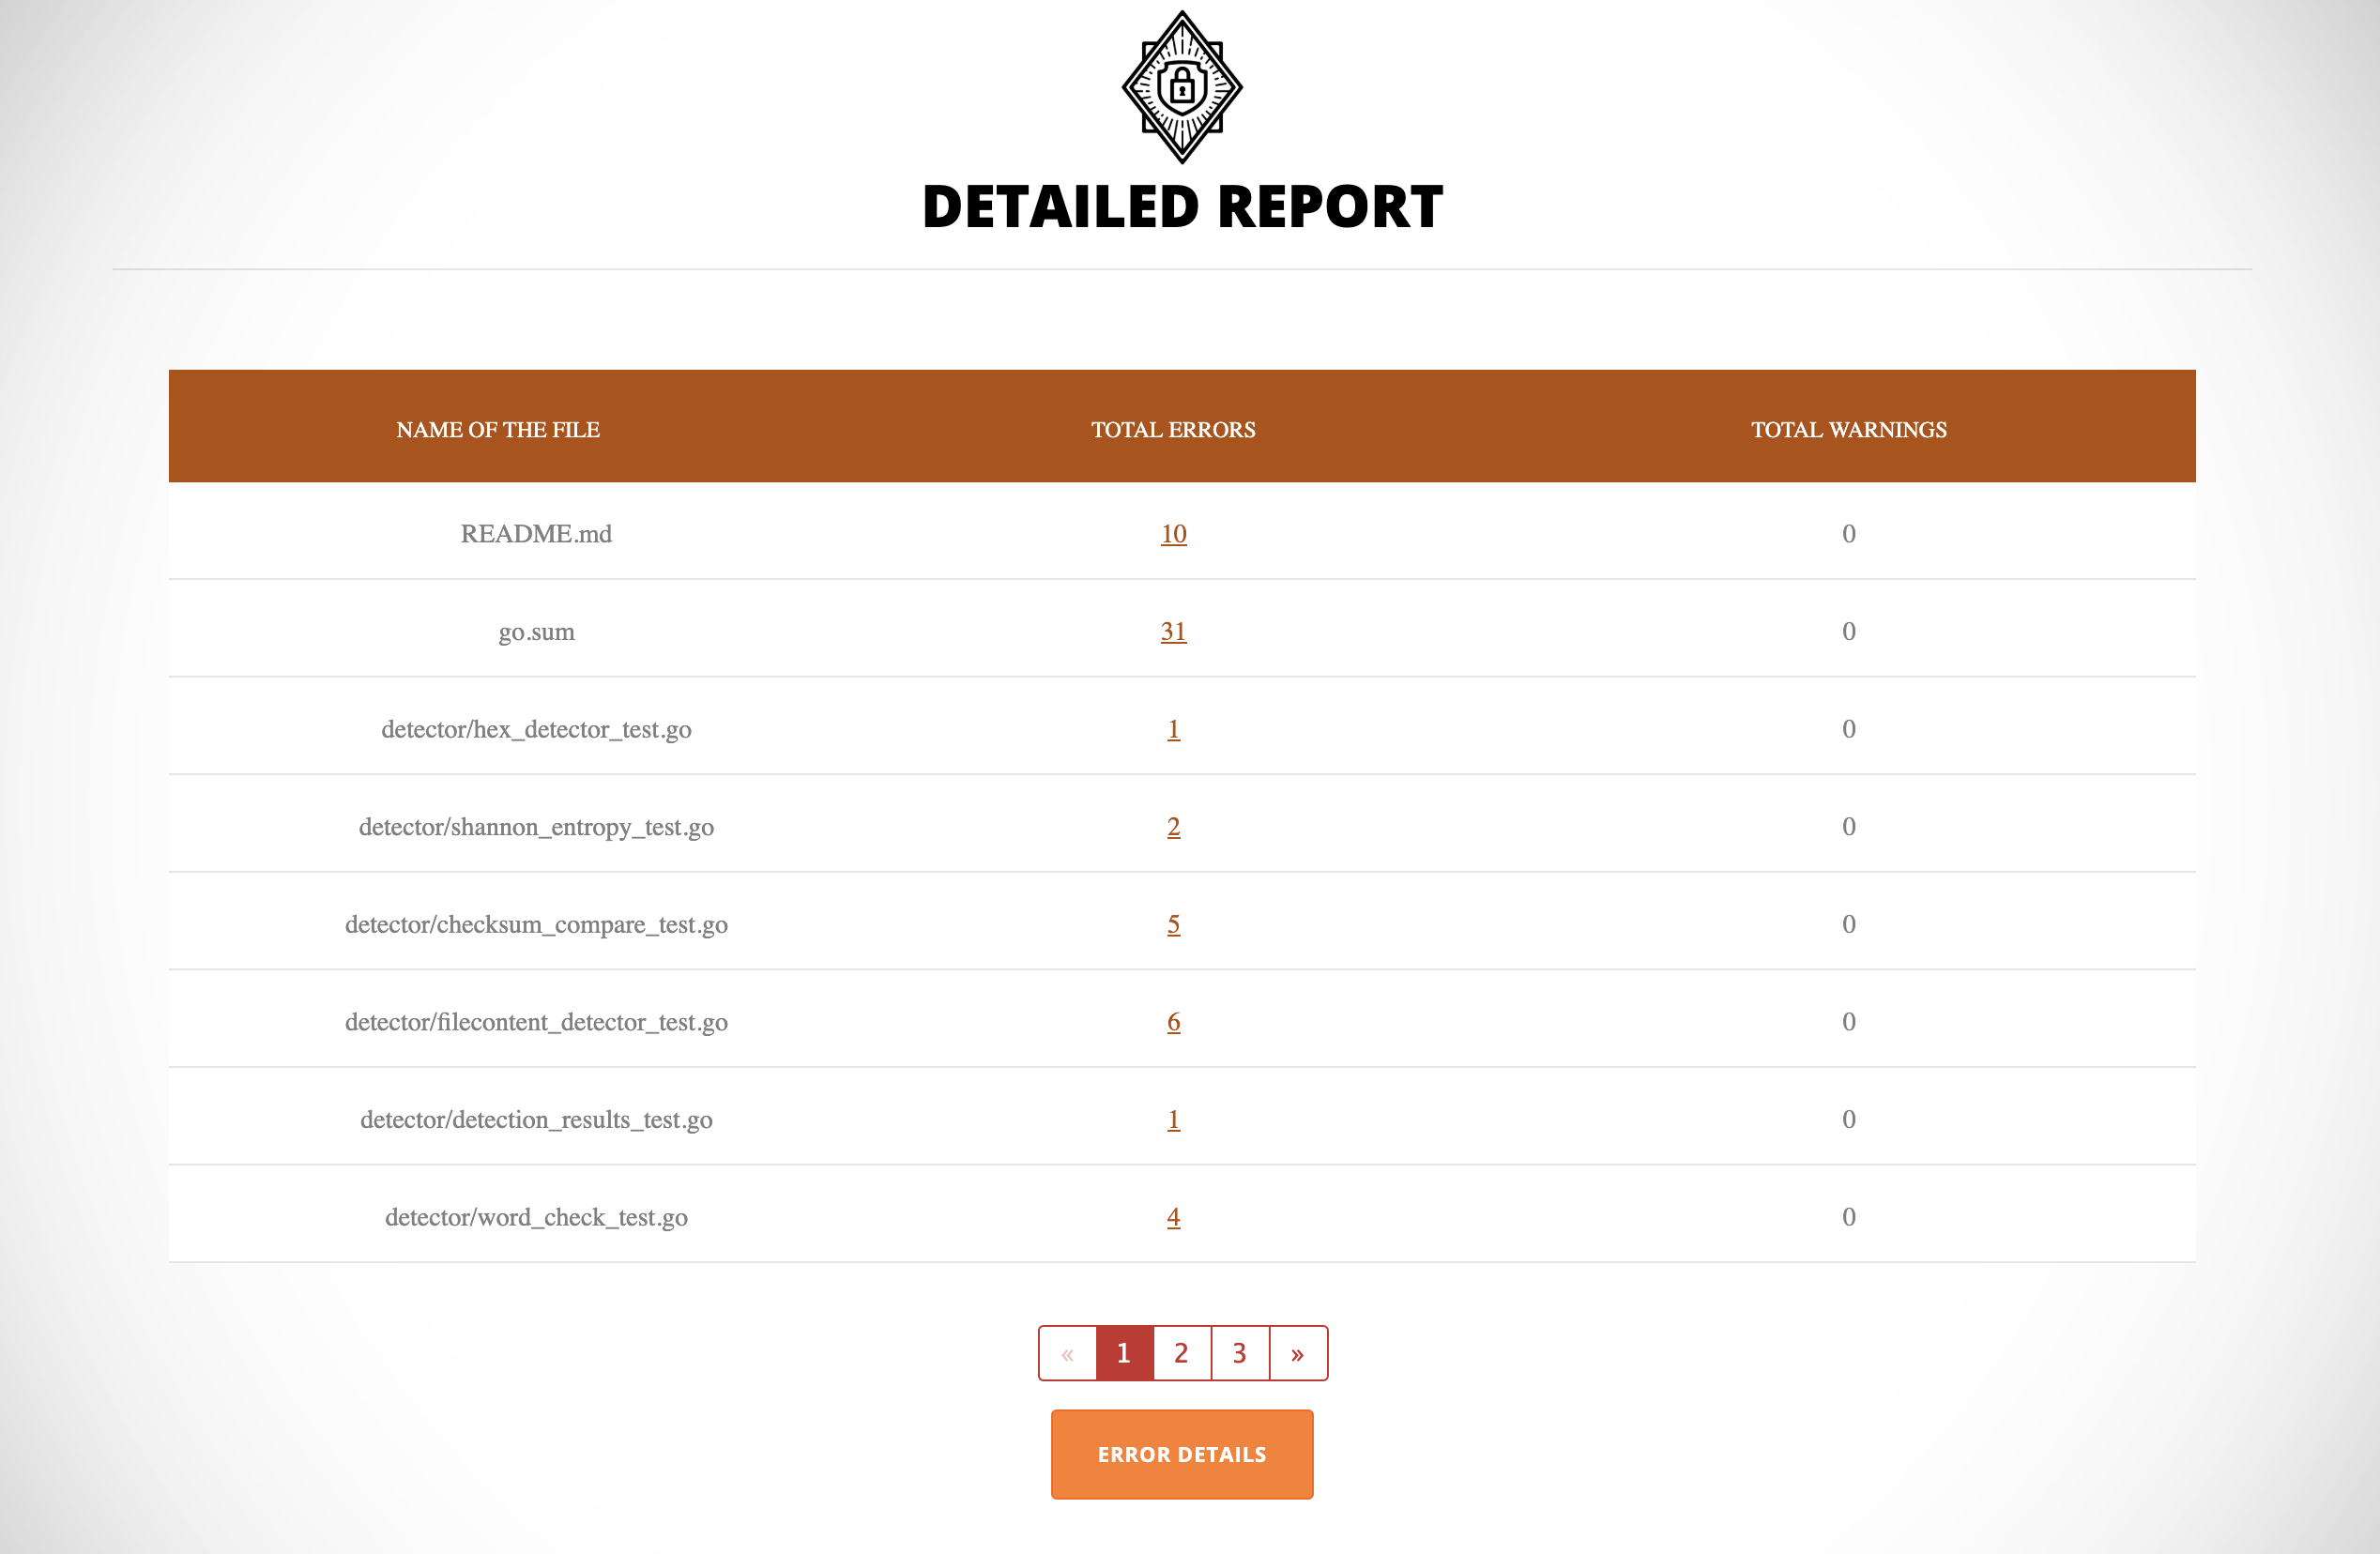 thoughtworks/talisman
Git hook-based secret scanner that detects tokens, passwords, and private keys in outgoing changesets, preventing sensitive data from being committed…
 aws-samples/kubernetes-log4j-cve-2021-44228-node-agent
Kubernetes DaemonSet that hot-patches JVMs to mitigate Log4j2 vulnerabilities (CVE-2021-44228, CVE-2021-45046) by disabling JNDI lookups, providing…
 irgoncalves/f5-waf-enforce-sig-cve-2021-44228
This enforces signatures for CVE-2021-44228 across all policies on a BIG-IP ASM device
 alebedev87/gatekeeper-cve-2020-8554
OPA Gatekeeper constraint policy that detects and prevents Kubernetes clusters from being vulnerable to CVE-2020-8554, enforcing secure configuration.
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 olacabs/jackhammer
Jackhammer - One Security vulnerability assessment/management tool to solve all the security team problems.
 alexzorin/cve-2017-2636-el
Ansible role for workaround for CVE-2017-2636 (Red Hat) - https://access.redhat.com/security/cve/CVE-2017-2636