
Archived
anchore-engine
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
static-analysisvulnerability-scannerscontainer-security+3
1.6k
anchore/anchore-engineA service that analyzes docker images and scans for vulnerabilities
 ustayready/outpost
AWS Testing and Reporting Management Tool
 devsecopsdocs/nuclearpond
Nuclear Pond is a utility leveraging Nuclei to perform internet wide scans for the cost of a cup of coffee.
 octarinesec/kube-scan
kube-scan: Octarine k8s cluster risk assessment tool
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 meterianhq/log4j-vuln-coverage-check
A simple project to check coverage of Log4J vuln CVE-2021-44228 (and related)
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
 aquasecurity/trivy-plugin-attest
Publish SBOM attestation
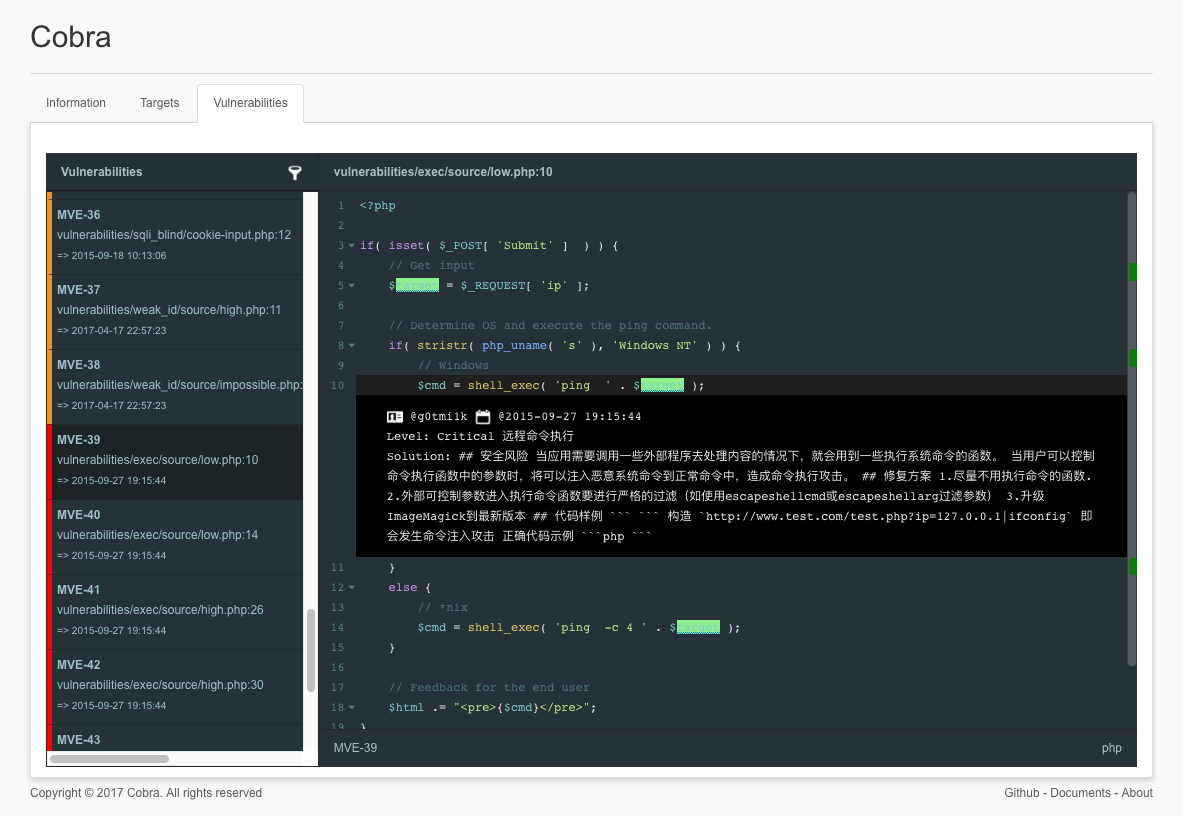 feeicn/cobra
Source Code Security Audit (源代码安全审计)
 aws-samples/kubernetes-log4j-cve-2021-44228-node-agent
Kubernetes DaemonSet that hot-patches JVMs to mitigate Log4j2 vulnerabilities (CVE-2021-44228, CVE-2021-45046) by disabling JNDI lookups, providing…
 hillu/local-log4j-vuln-scanner
[Moved to Codeberg] Simple local scanner for vulnerable log4j instances
 bugbounty-site/gitsecure
Detect exposed API keys on GitHub commits.
 peterthomasawen/opensslupgrade1.1.1q-ubuntu
A script to change OpenSSL versions on Ubuntu to 1.1.1q to protect against CVE-2022-2097.
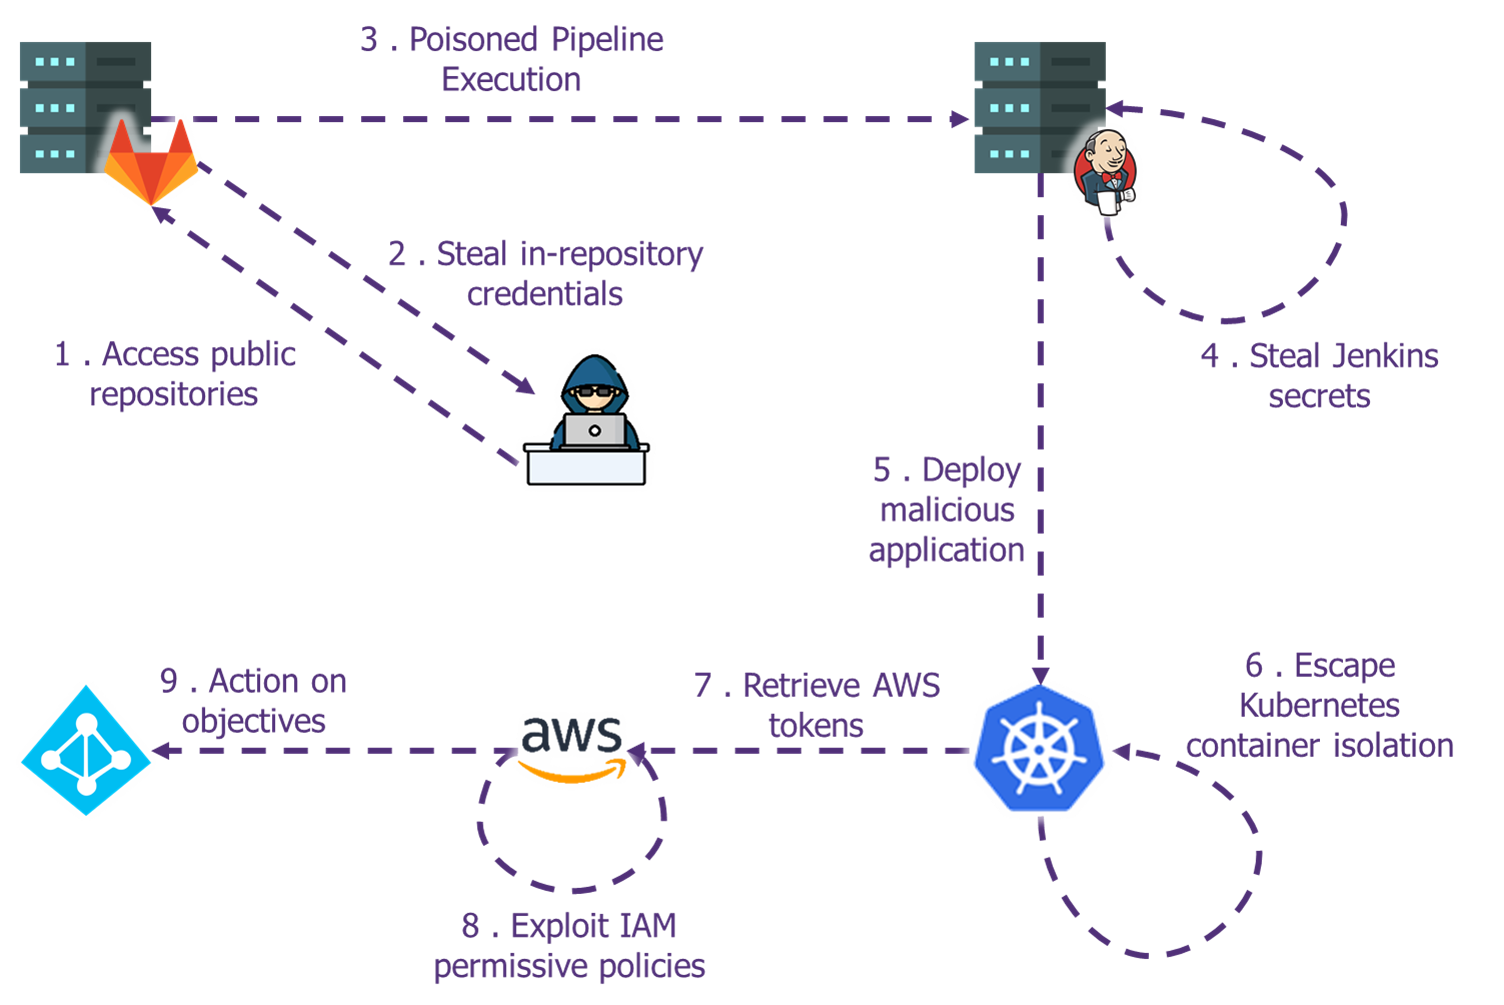 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 aquasecurity/trivy-module-wordpress
Trivy example module for WordPress
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 irgoncalves/f5-waf-quick-patch-cve-2021-44228
This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode
 mebibite/log4jhound
Created after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…