
kodex
 kiprotect/kodex
A privacy and security engineering toolkit: Discover, understand, pseudonymize, anonymize, encrypt and securely share sensitive and personal data:…
encryption-decryption-toolsscripting-automationconfiguration-auditing+3
127
kiprotect/kodexA privacy and security engineering toolkit: Discover, understand, pseudonymize, anonymize, encrypt and securely share sensitive and personal data:…
 aquasecurity/vex-repo-spec
VEX Repository Specification
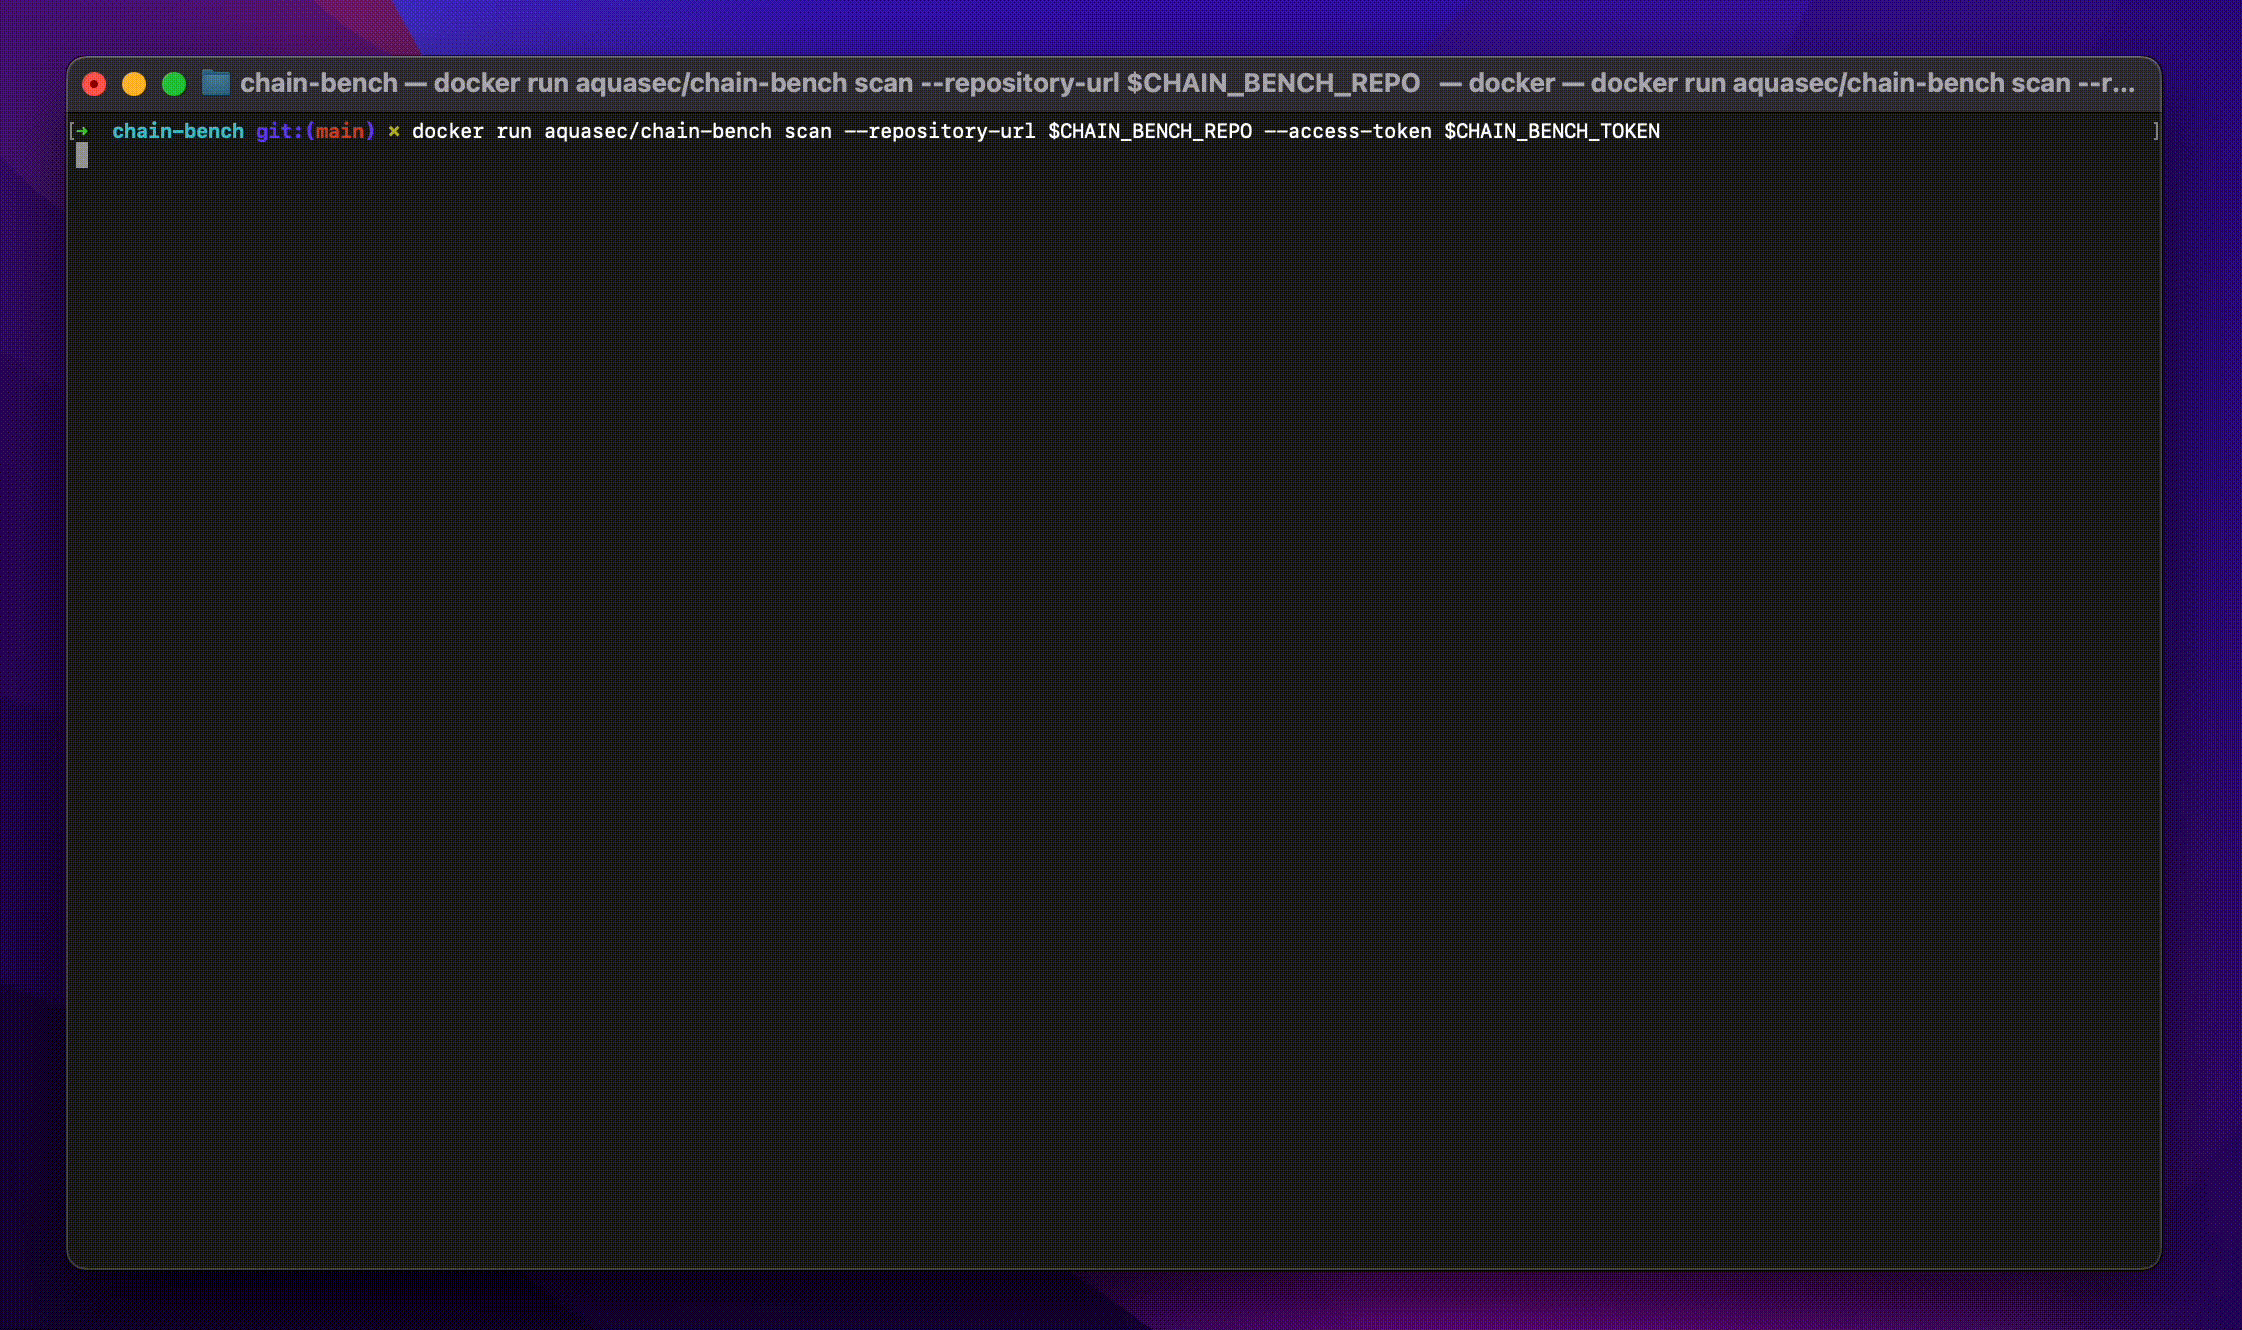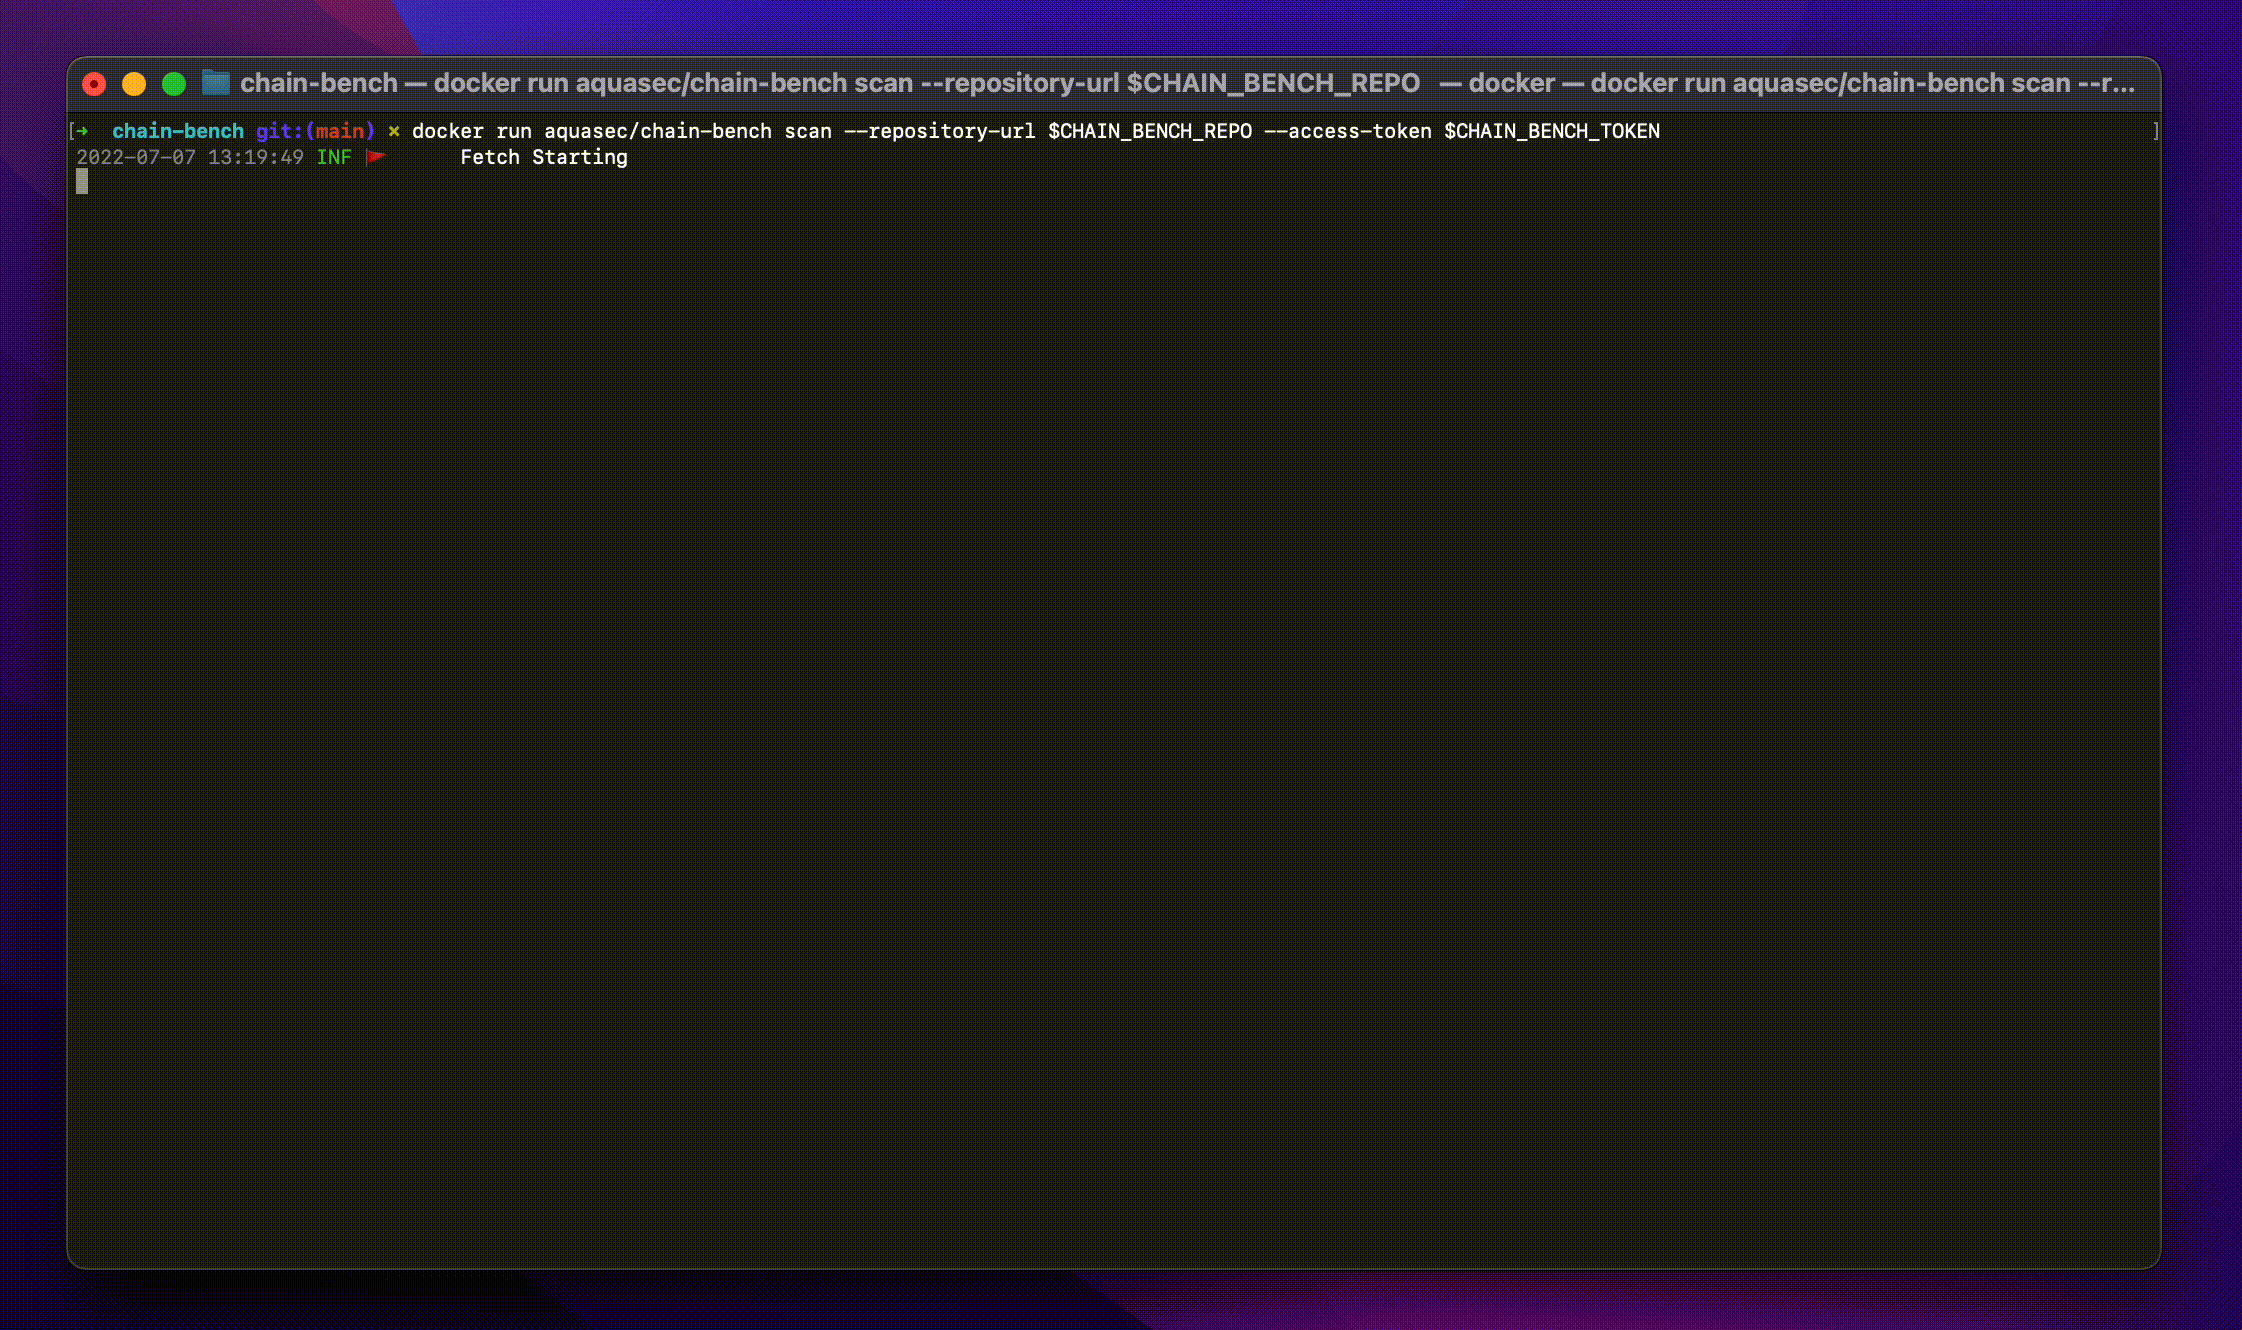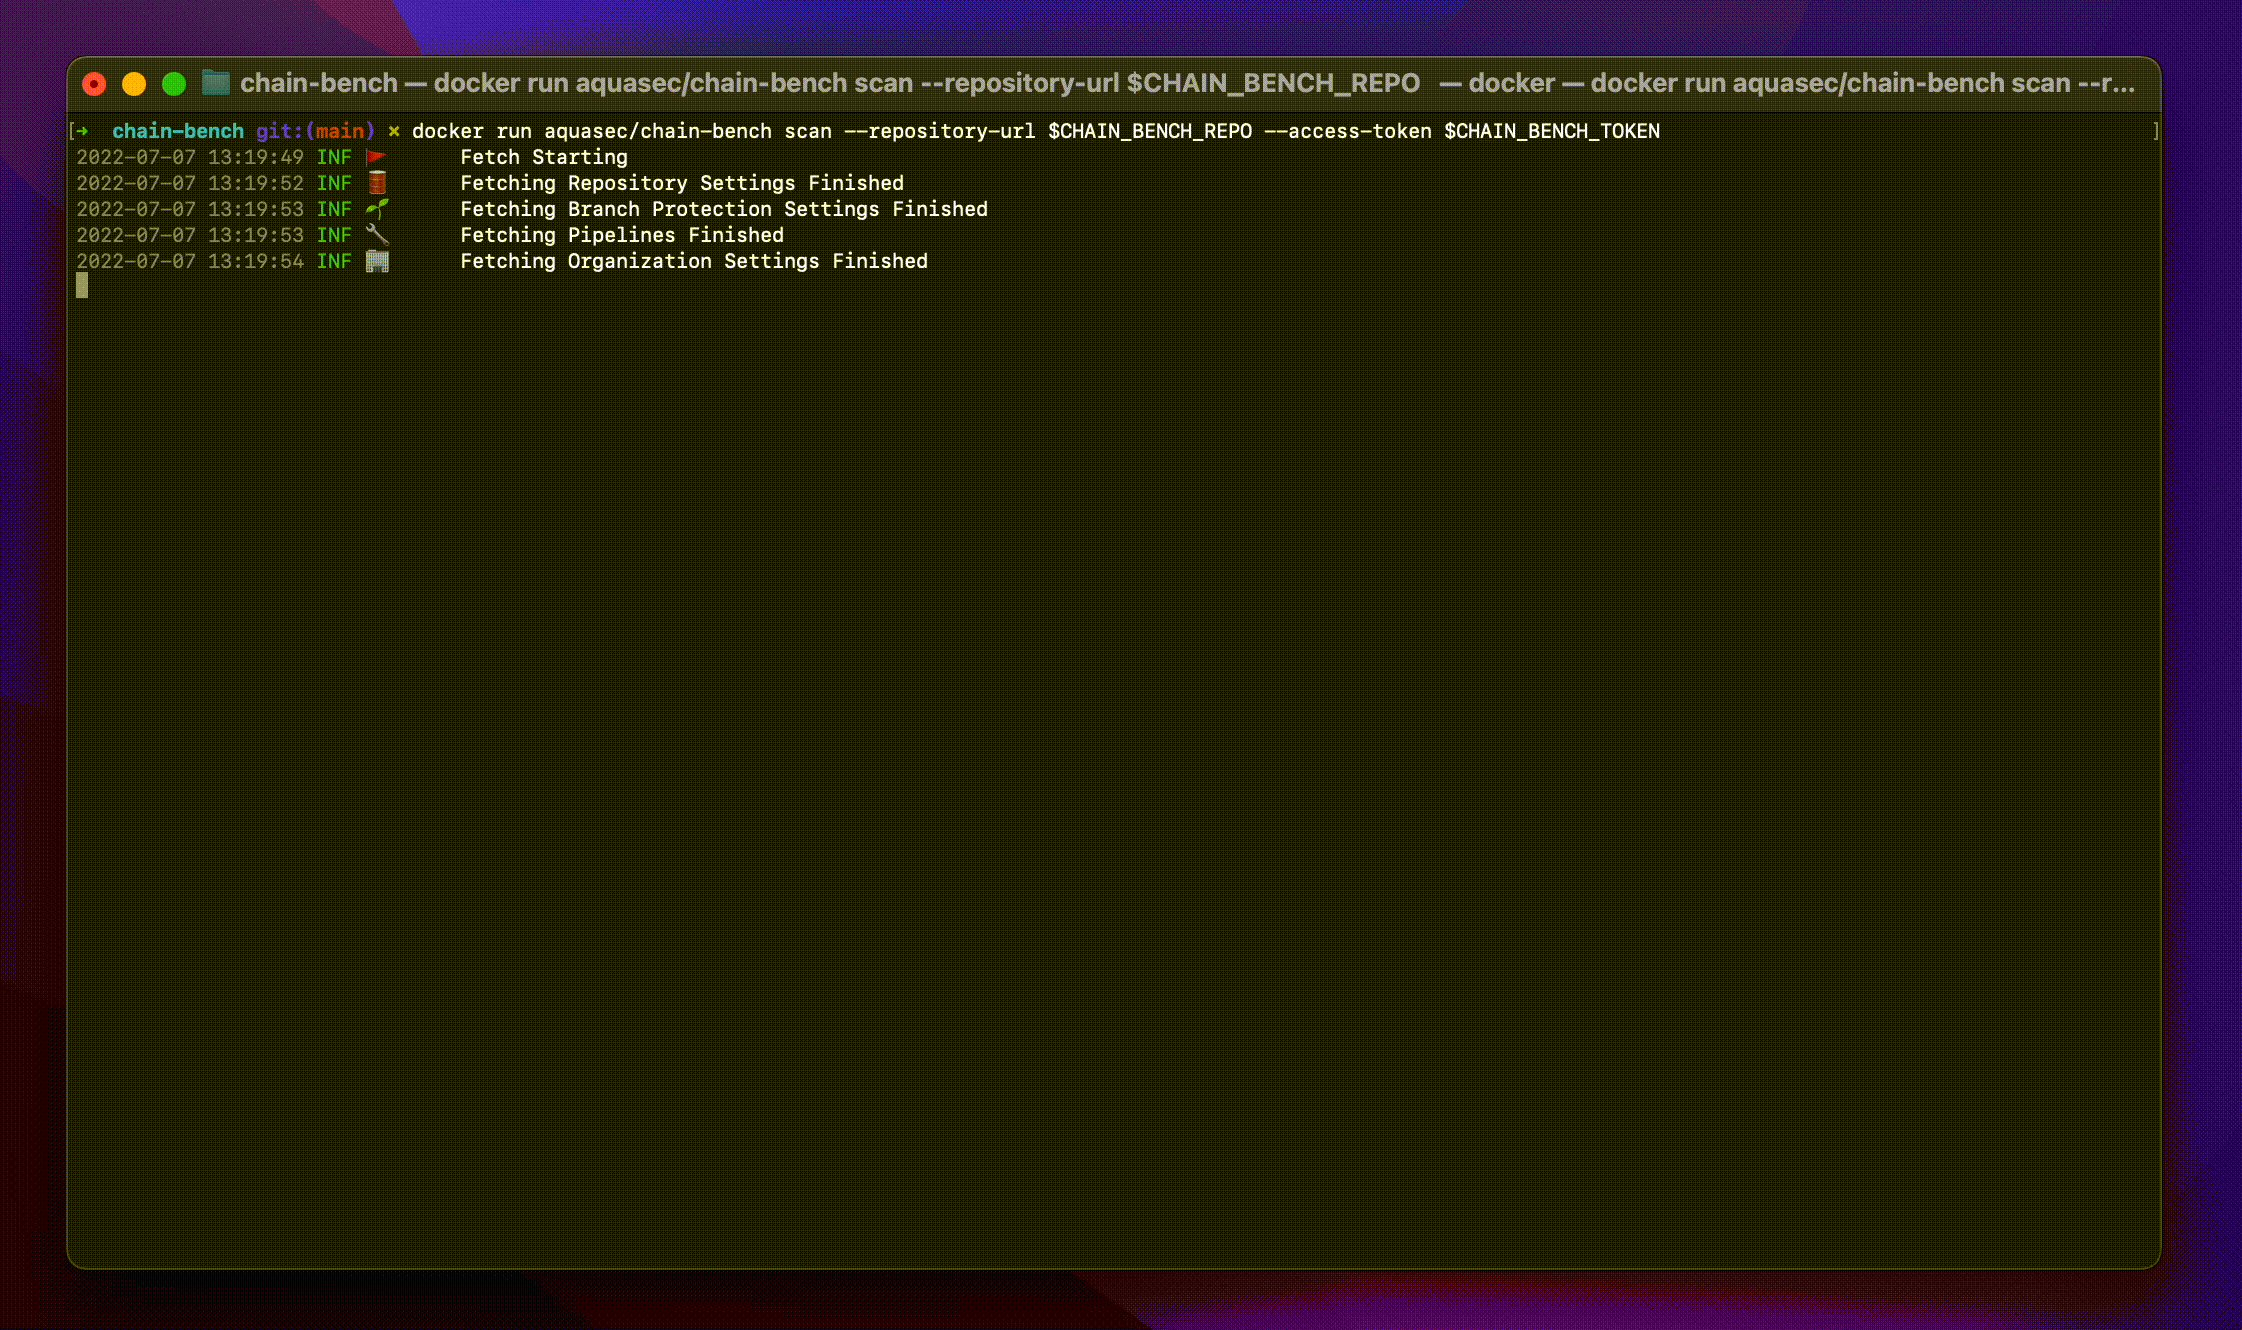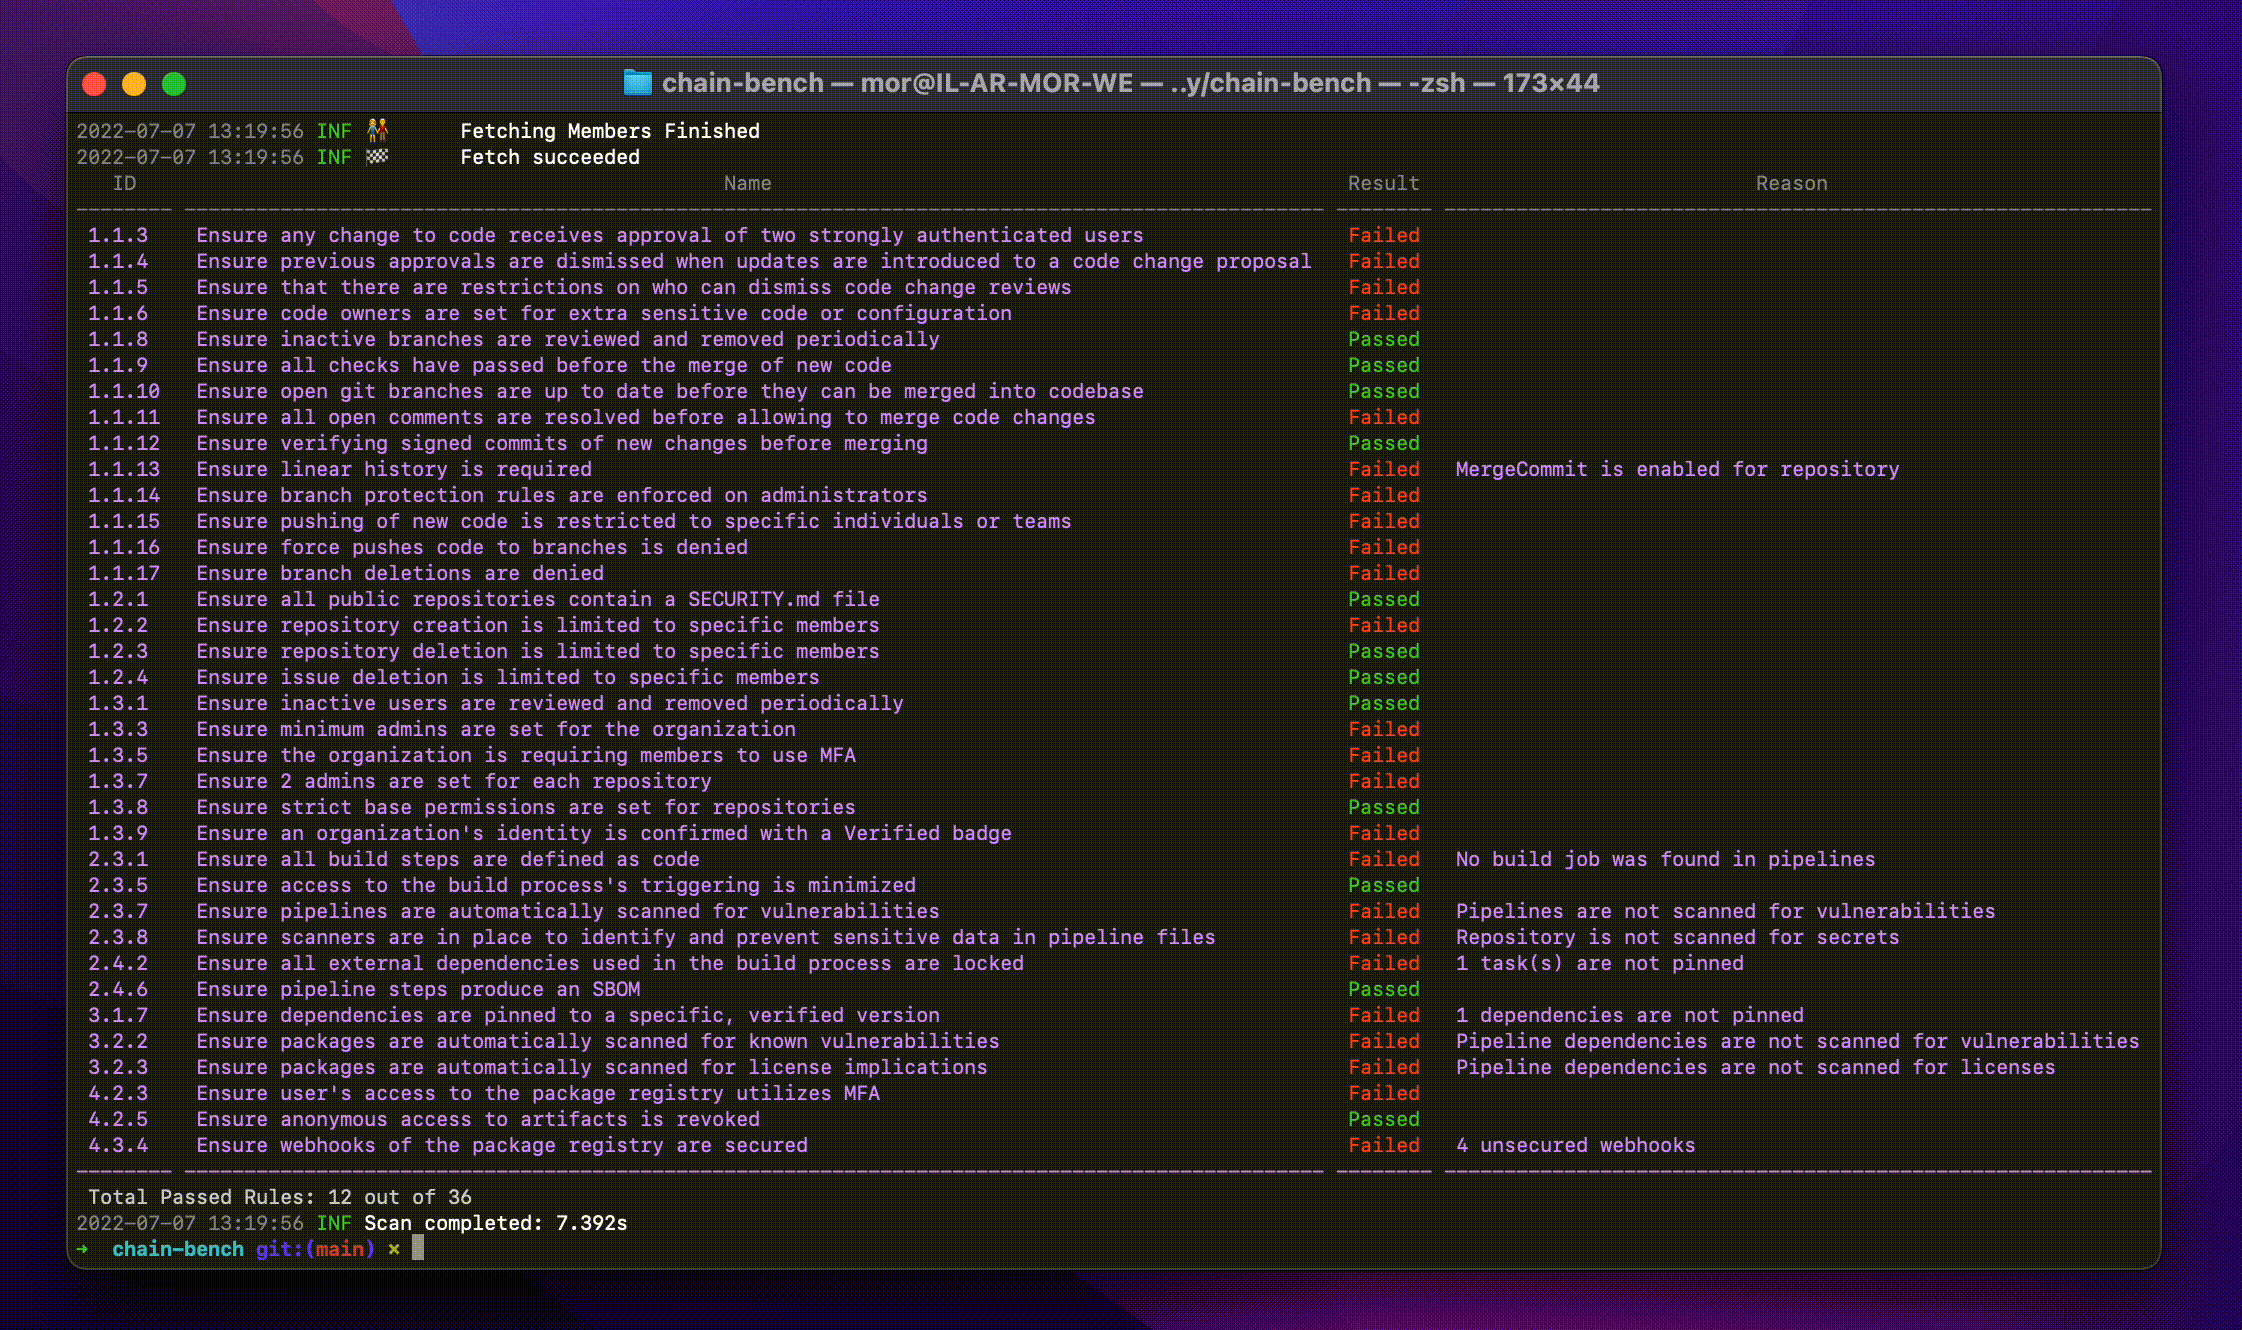 aquasecurity/chain-bench
Audits software supply chain security compliance against the CIS benchmark, scanning SCM settings, branch protections, dependencies, and CI/CD…
 purs3lab/argus
Staged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…
 cider-security-research/cicd-goat
A deliberately vulnerable CI/CD environment. Learn CI/CD security through multiple challenges.
 dgourillon/mitigate-cve-2024-6387
Shell script to detect and mitigate CVE-2024-6387 vulnerability by auditing system configurations and applying recommended fixes.
 vkaushik-chef/regresshion
Chef Inspec profile for checking regreSSHion vulnerability CVE-2024-6387
 felipecruz91/node-ip-vex
Sample project that uses VEX to supress CVE-2024-29415.
 zenzue/cve-2024-6387-mitigation
Mitigation Guide for CVE-2024-6387 in OpenSSH
 daniel-odrinski/cve-2024-6387-mitigation-ansible-playbook
An Ansible Playbook to mitigate the risk of RCE (CVE-2024-6387) until platforms update OpenSSH to a non-vulnerable version.
 claranet/ansible-role-log4shell
Ansible role to detect Log4Shell (CVE-2021-44228) by scanning filesystem and open files for vulnerable JAR/WAR files, reporting version and…
 fabacab/awesome-cybersecurity-blueteam
:computer:🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.
 gitlab-da/tutorials/security-and-governance/custom-scanner-integration/fern-pattern-scanner
Scans selected files for patterns stated in rules. This is used in order to find secrets you may have accidentally written to a file. This scanner is…
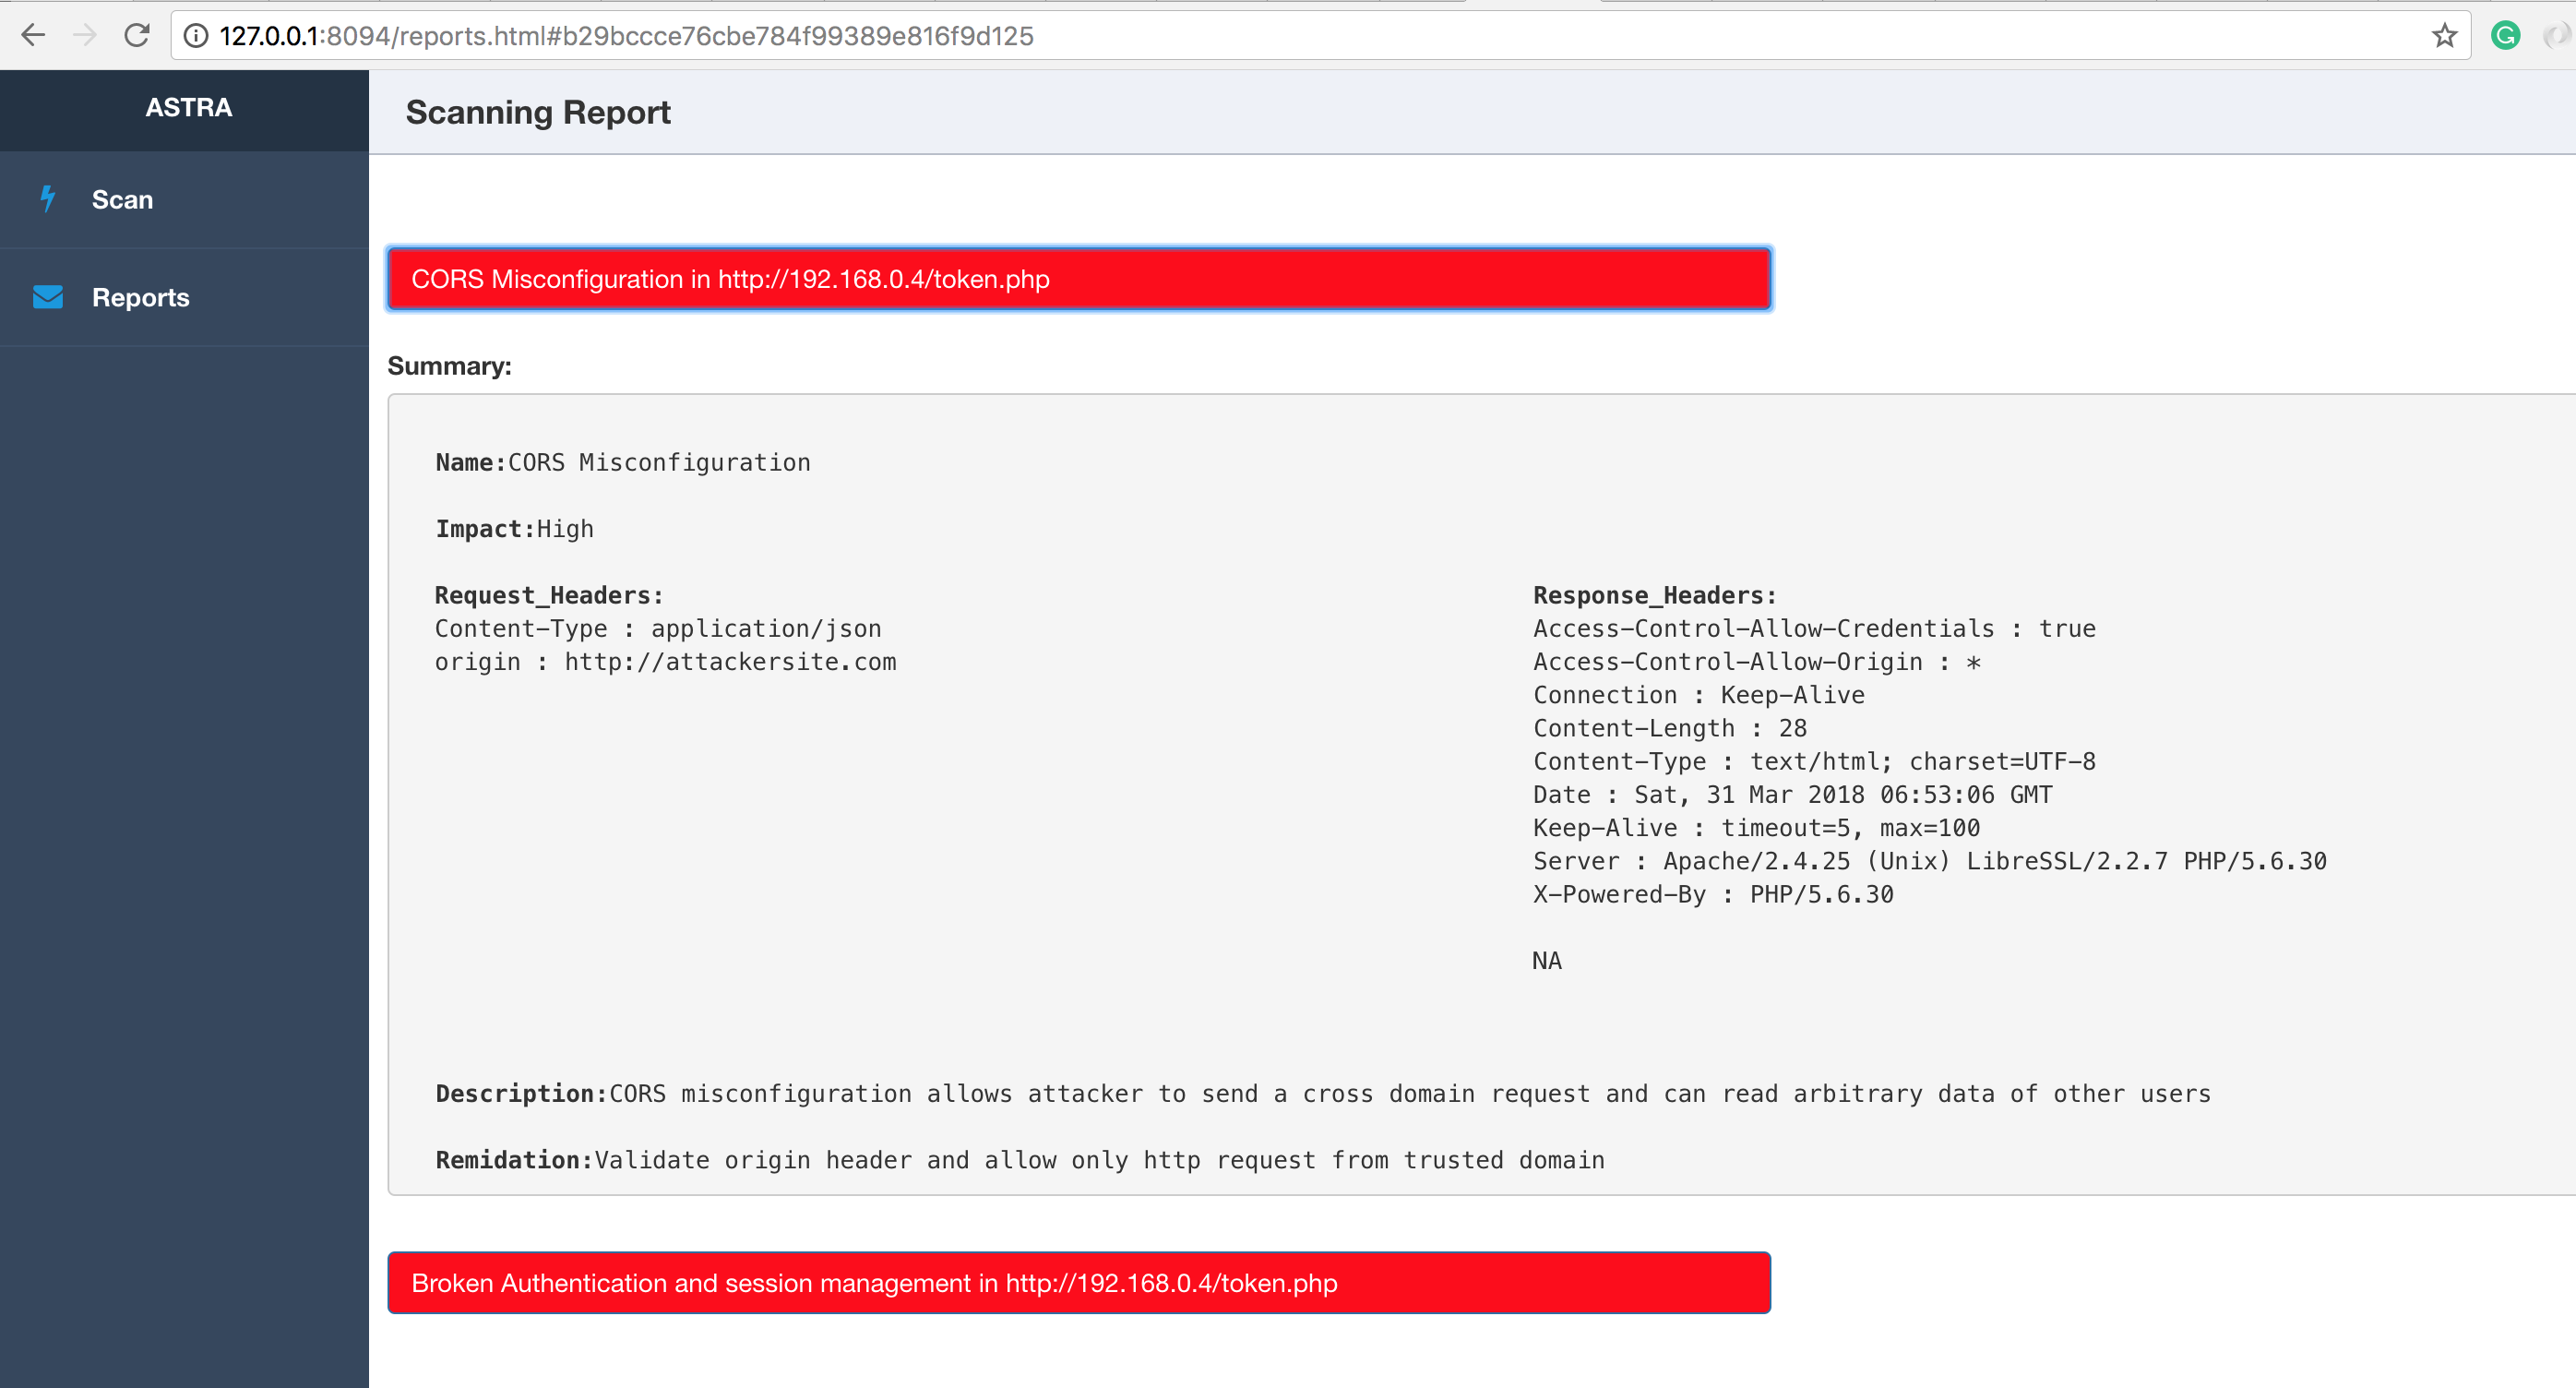 flipkart-incubator/astra
Automated Security Testing For REST API's
 globocom/huskyci
Performing security tests inside your CI
 aquasecurity/trivy-plugin-kubectl
A Trivy plugin that scans the images of a kubernetes resource
 kube-tarian/tarian
eBPF-based runtime security agent for Kubernetes that detects unknown processes and file changes, enforces pre-registered constraints, and automates…
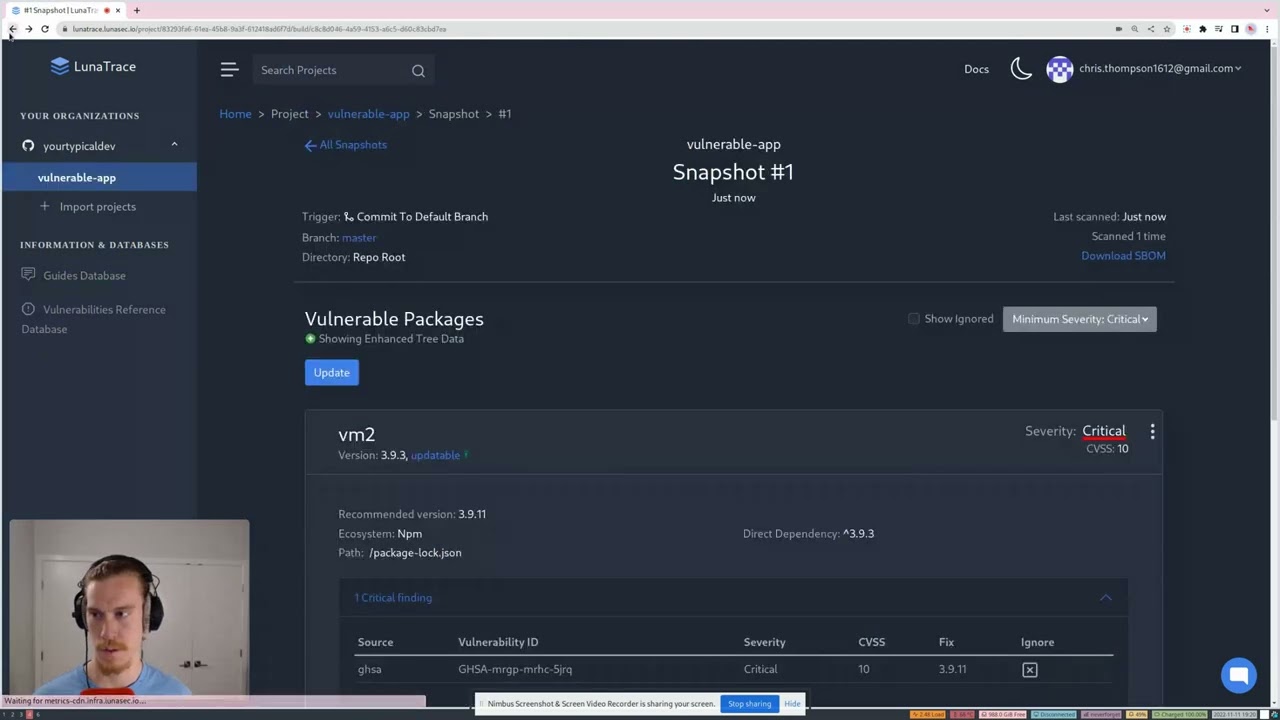 lunasec-io/lunasec
LunaSec - Dependency Security Scanner that automatically notifies you about vulnerabilities like Log4Shell or node-ipc in your Pull Requests and…