

runeward
 runewardd/runeward
Governed execution cells for AI agents.
ai-securityauthentication-authorizationcloud-security+7
1
runewardd/runewardGoverned execution cells for AI agents.
 rh-rahulshetty/log4shell-cve-2021-44228
Deliberately vulnerable Java/Maven fixture for testing Log4Shell (CVE-2021-44228) detection, code-impact classification, and remediation guidance in…
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 yonliud/cve-2026-0303
Checkov PoC: arbitrary code execution through auto-loaded configuration and unsigned external Python checks.
 offensive360/sast-scan-action
GitHub Action: Offensive360 SAST scan with SARIF output for code scanning. 60+ languages. Free for open source.
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…
 disrex-group/stylesmuggler-adobe-patches
composer require delivery of Adobe's official APSB26-146 (CVE-2026-75650) fix for Magento, via cweagans/composer-patches. Auto-selects the patch for…
 pvharmo2/gha-lab-00d54c717d
Security-research lab: CVE-2026-47172 (workflow_run pwn request in deploy.yaml) — flattened snapshot of duck-organization/questbot at 1903b2f
 pvharmo2/gha-lab-5511dc3f73
Authorized security-research lab reproducing CVE-2026-45131 (pwn request in .github/workflows/pull-request.yaml) — snapshot of…
 dev-sec/puppet-os-hardening
This puppet module provides numerous security-related configurations, providing all-round base protection.
 pvharmo2/gha-lab-5bce203f66
Security-research lab: reproduction of CVE-2026-41249 (GHSA-q58j-g3f4-h26h) — pull_request_target pwn request in .github/workflows/static.yml,…
 xiaoqimikko/netty-http2-check
Offline Java tool that scans jars and versions to determine exposure to seven netty-codec-http2 CVEs, recommending the single patched version that…
 pigeonlabshq/pigeon
Enforce least-privilege delegation for AI agents with signed, scoped credentials. Grant sub-agents narrow capabilities and resources, verify actions…
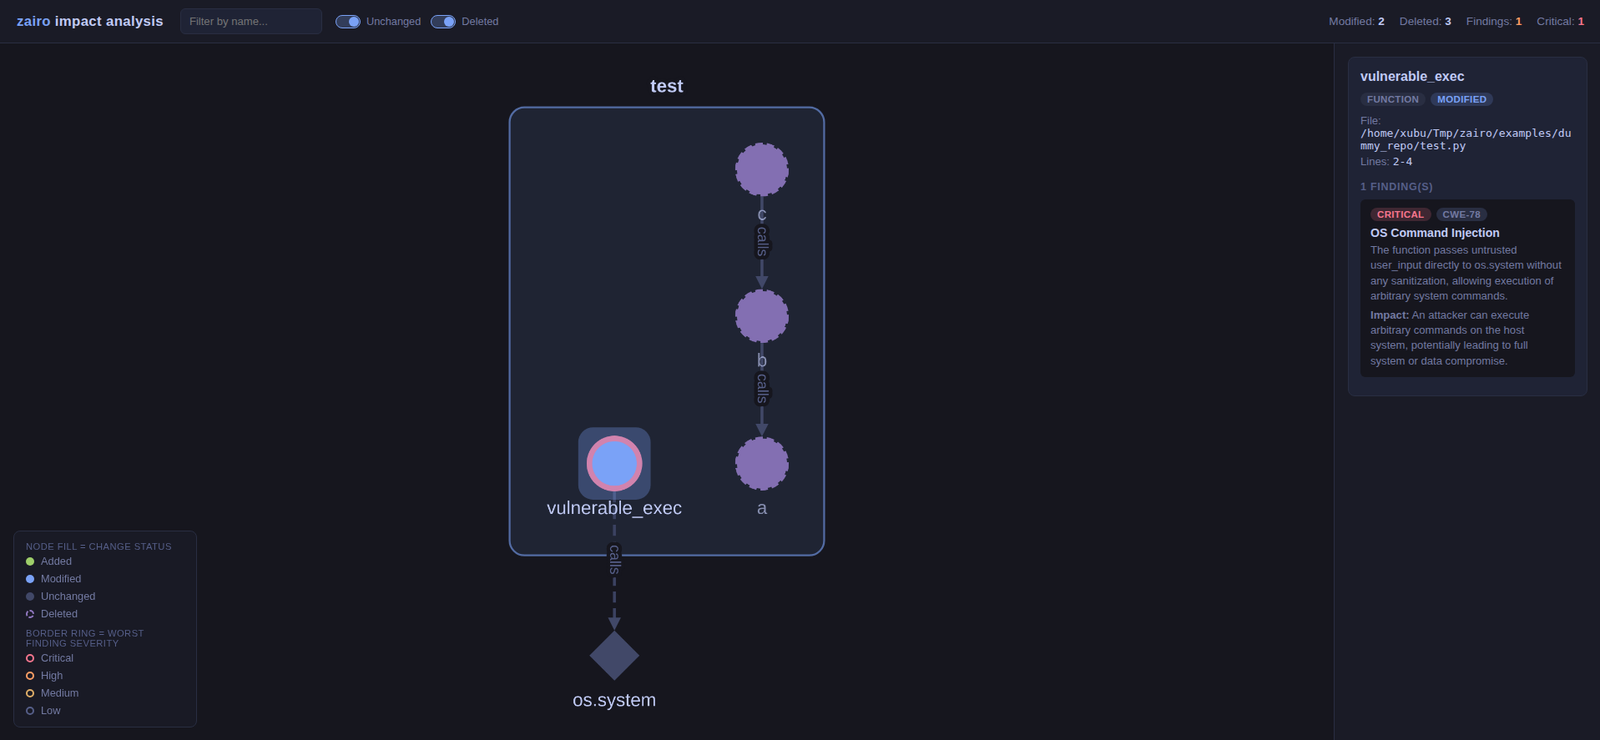 iamavu/zairo
Scans code diffs with context to build an impact graph and uses LLMs to find vulnerabilities, supporting multi-repo scans and CI gating with SARIF…
 pvharmo2/gha-lab-3f1ff30e9c
Authorized security-research lab reproducing CVE-2026-31852 (jellyfin/jellyfin-ios pull_request_target pwn in code-quality.yml) — isolated snapshot,…