

autorun-audit
 ag3ntsc4rn/autorun-audit
Find code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…
ai-securitycode-analysisconfiguration-auditing+6
ag3ntsc4rn/autorun-auditFind code that runs without you asking: repo files that execute on folder open (VS Code tasks, agent hooks, MCP, devcontainers) and Python…
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 xiaoqimikko/async-http-client-check
Self-hosted AI workspace with agents, skills, and tools (Gmail, Calendar) that runs entirely on your own provider API keys (BYOK). Bring your own…
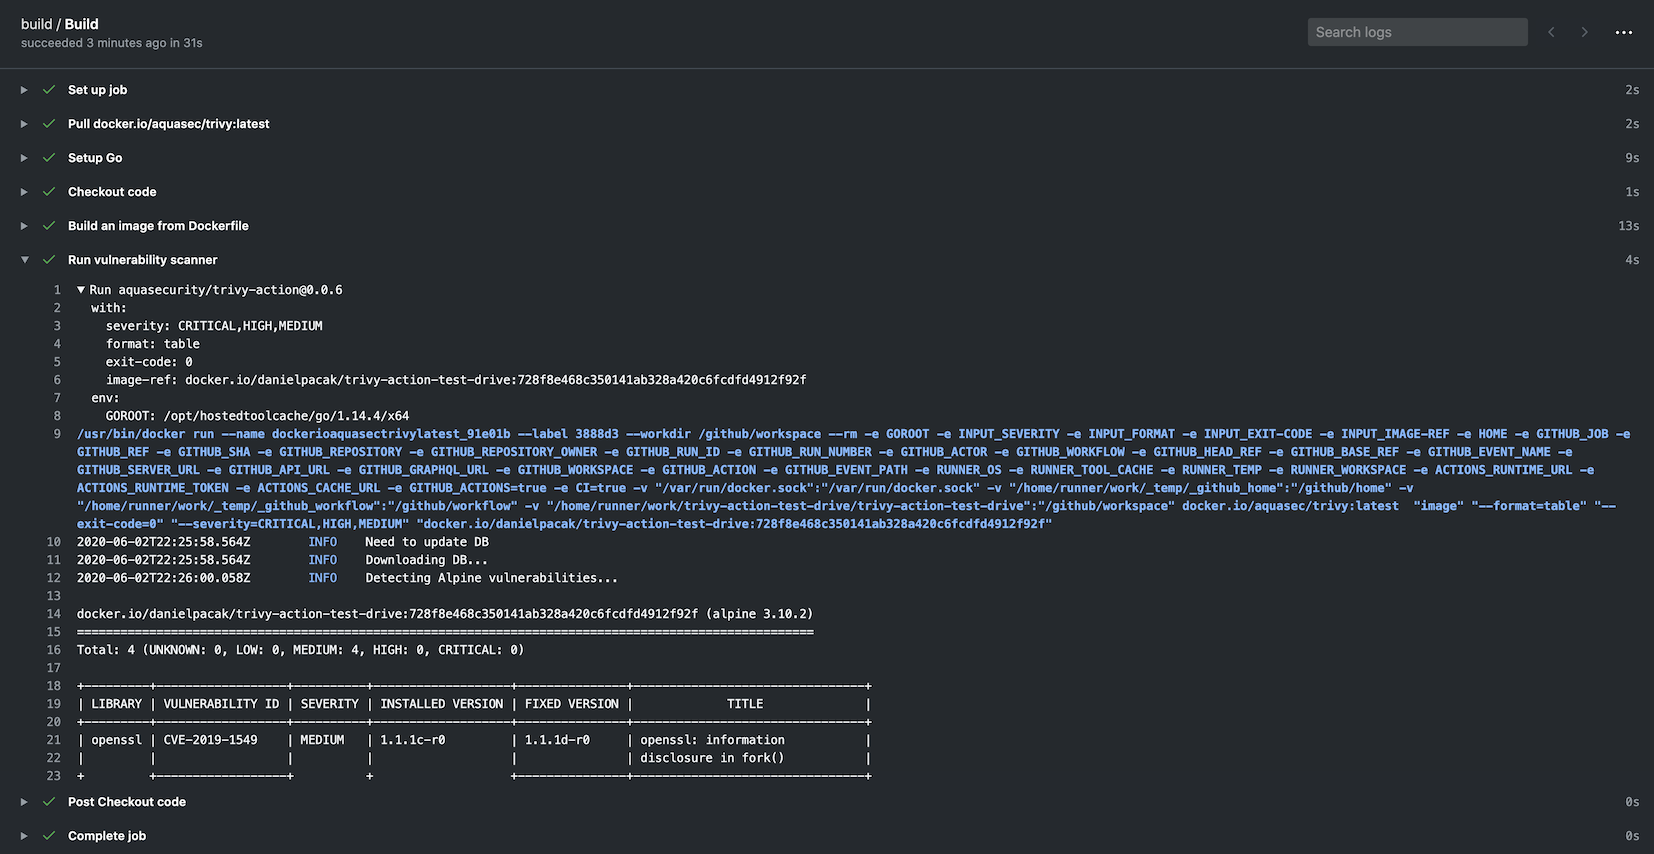 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
 bande-a-bonnot/boucle-framework
Autonomous agent framework with structured memory, safety hooks, and loop management. Built by the agent that runs on it.
 dbzoo/log4j_scanner
Filesystem scanner for Log4Shell (CVE-2021-44228) and related CVEs. Detects vulnerable JAR files via hash matching and class presence. Runs…
 cyberark/vulnhalla
Automated security analysis pipeline that runs CodeQL queries on GitHub repositories and uses LLMs to classify and filter true vulnerabilities from…
 jsdelivr/globalping-probe
The globalping probe code that runs on your hardware and connects to the global community network of probes
 iulianvostrut/contexthound
Static analysis CLI that scans codebases for LLM prompt-injection, data-exfiltration, jailbreak, and unsafe agent/tool vulnerabilities. Runs fully…
 swelljoe/flar
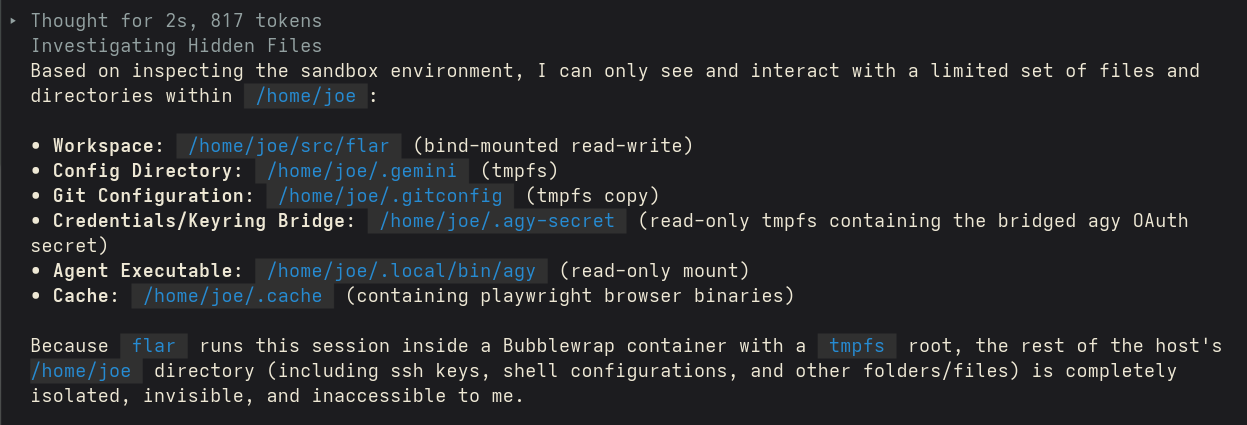
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
 sqlsure/sqlsure
Semantic inspector for SQL — catches fan-out double-counting, additivity violations, wrong join keys, and policy breaches before the query runs.…
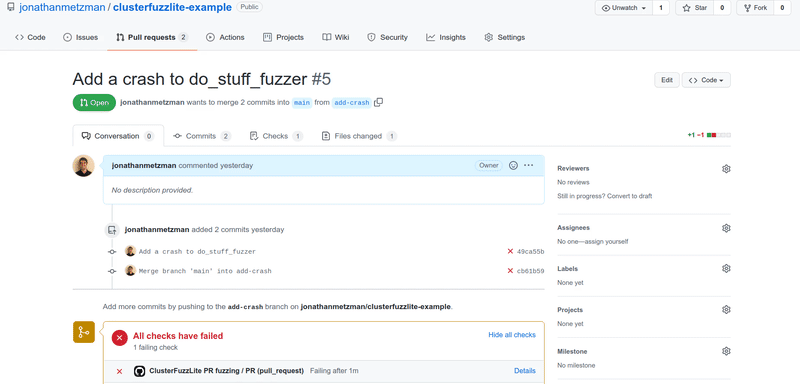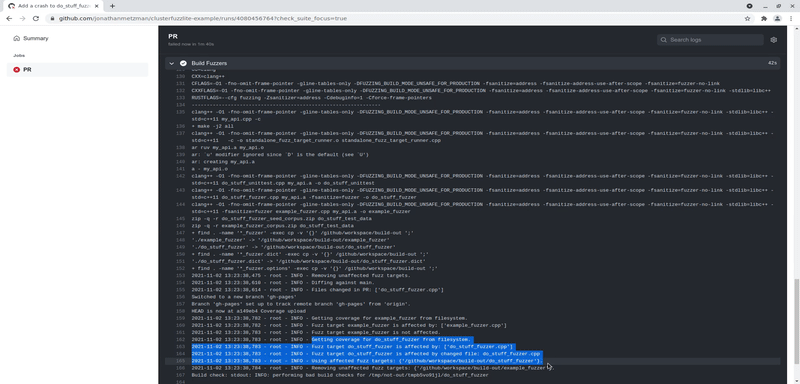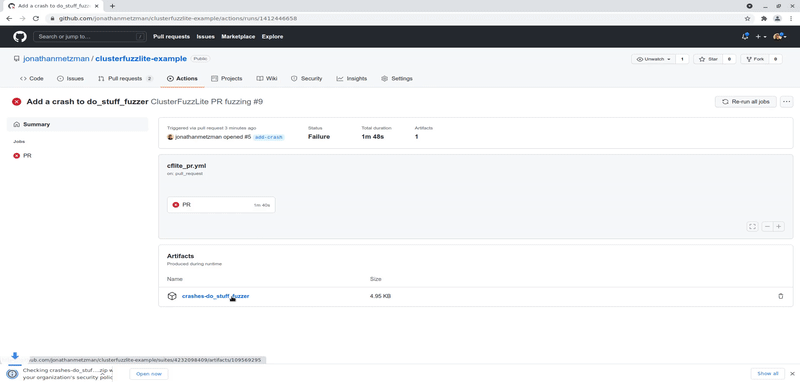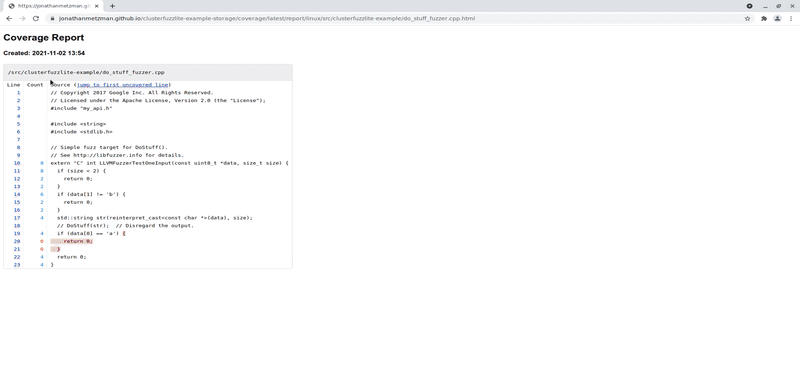 google/clusterfuzzlite
Continuous fuzzing solution integrated into CI workflows to find vulnerabilities in code changes and batch runs, supporting multiple languages and CI…