
CVE-2026-23918
This is a proactive tool for security auditing. For your GitHub repository, you’ll want a description that highlights its safety (non-intrusive) and…

This is a proactive tool for security auditing. For your GitHub repository, you’ll want a description that highlights its safety (non-intrusive) and…

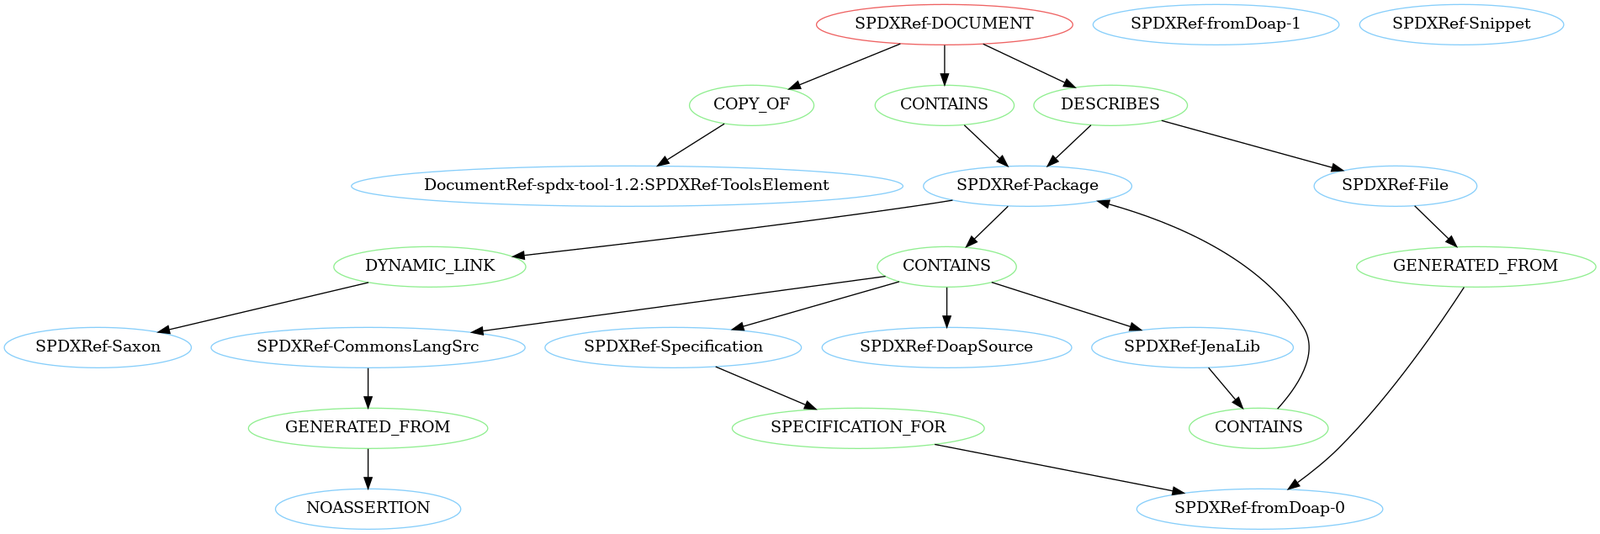
A Python library to parse, validate and create SPDX documents.

OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.

System utility that identifies and restarts daemons using outdated libraries after package upgrades to maintain security. Supports containers and…

Nuclear Pond is a utility leveraging Nuclei to perform internet wide scans for the cost of a cup of coffee.

Gradle plugin for fast, reproducible Eclipse IDE provisioning as a build artifact, with support for OSGi, p2, and RCP builds.

Software composition analysis tool that detects publicly disclosed vulnerabilities in project dependencies using CPE matching, generating detailed…

A utility for Magento 2 encryption key rotation and management. CVE-2024-34102(aka Cosmic Sting) victims can use it as an aftercare.

Safely install NPM packages

Catch what's lurking in your Kafka clusters.

🔐 Lightweight CLI utility designed to synchronize SSH public keys from remote URLs into local authorized_keys files

Python script that automatically patches GitHub Actions workflow files to replace deprecated and insecure ::set-env and ::add-path commands with the…

A lightweight utility designed to detect and remediate systems affected by CVE-2024-3094, a critical vulnerability impacting [insert affected…

CLI tool for inspecting and managing services listening on localhost ports

Proof-of-concept exploit for CVE-2019-17041, a buffer overflow in rsyslog's parser, demonstrating remote code execution.

Powershell-based bot framework

Nuclear Pond is a utility leveraging Nuclei to perform internet wide scans for the cost of a cup of coffee.