
log4jhound
 mebibite/log4jhound
Created after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…
code-analysisdevsecopsstatic-analysis+2
mebibite/log4jhoundCreated after the disclosure of CVE-2021-44228. Bash script that detects Log4j occurrences in your projects and systems, allowing you to get insight…
 jas502n/database-spring-enc
sprint encode (plan text) get enc password
 corelight/corelight-ansible-roles
Corelight-Ansible-Roles are a collection of Ansible Roles and playbooks that install, configure, run and manage a variety of Corelight, Suricata and…
 adamsjack711-ux/pkgxray
Pre-install security for AI agents, npm packages, and MCP servers. Zero-dep local static analysis; normal scans never execute package code.
 arzaan789/keyguard
Scan codebases and GCP projects for exposed API credentials
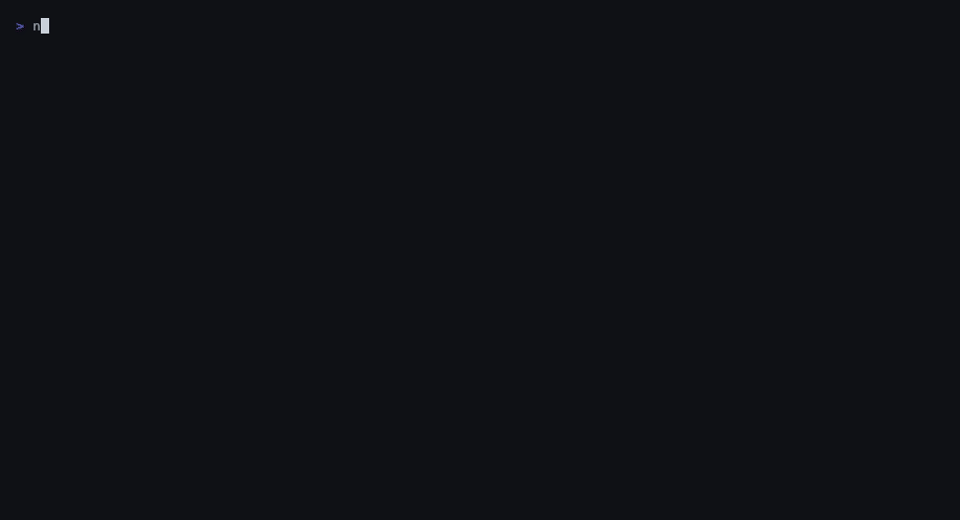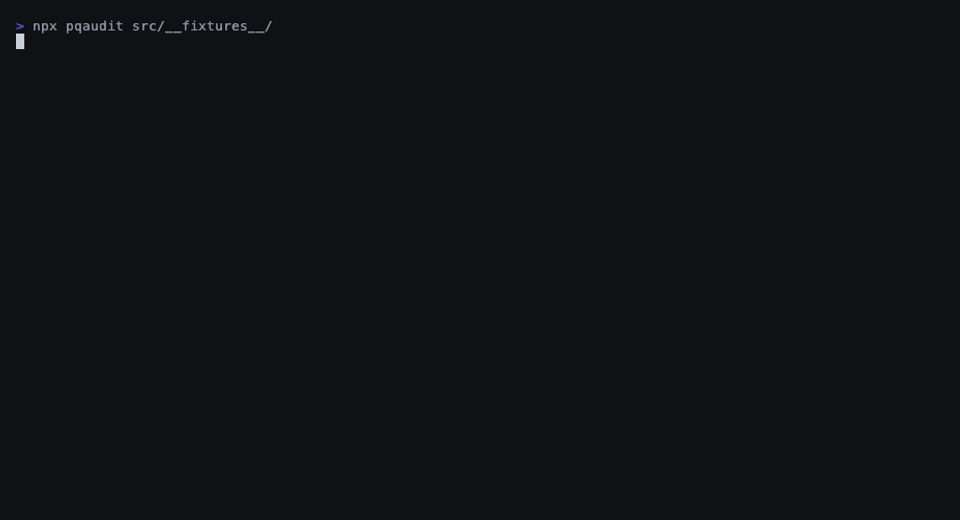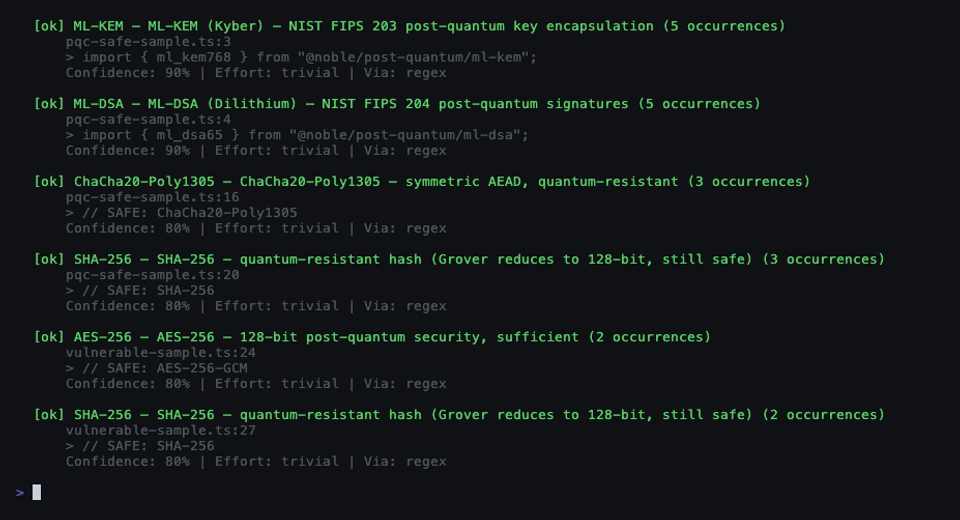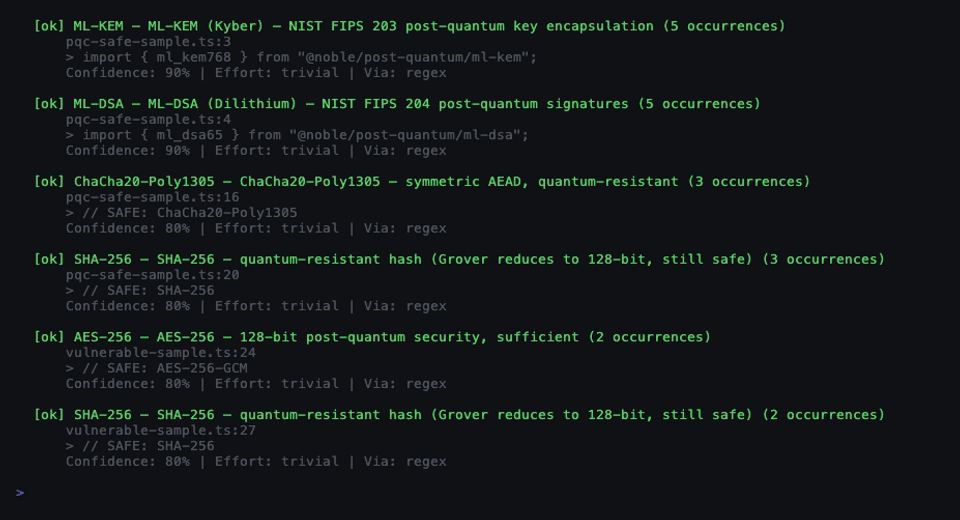 pqcworld/pqaudit
Scan codebases for quantum-vulnerable cryptography. Detect RSA, ECDSA, Ed25519, ECDH before Q-Day. CycloneDX CBOM + SARIF output.
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 mhaskar/bughound
Static code analysis tool based on Elasticsearch
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 zzugab/juice-shop-with-kubeadm-and-tf
Automated deployment of OWASP Juice Shop on Kubernetes using kubeadm and Terraform, with integrated Trivy vulnerability scanning for DevSecOps…
 itinerisltd/trellis-cve-2018-6389
Mitigate CVE-2018-6389 WordPress load-scripts / load-styles attacks
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities