kafka-keycloak-oauth

Apache Kafka 4.1.0 (KRaft) with Keycloak OAuth2 authentication using Strimzi - bypasses CVE-2025-27817 URL allowlist restriction

Apache Kafka 4.1.0 (KRaft) with Keycloak OAuth2 authentication using Strimzi - bypasses CVE-2025-27817 URL allowlist restriction

Compiles source code into auditable, signed APK packages using declarative pipelines for Wolfi/Alpine, with multi-architecture QEMU emulation and…

Ansible Playbook for CVE-2023-36845(Juniper Networks Junos OS 远程代码执行漏洞)

Draw.io libraries for threat modeling diagrams

Go library for safe YAML and shell generation, using syntax-aware templates to detect and block injection attacks via annotations for trusted data.

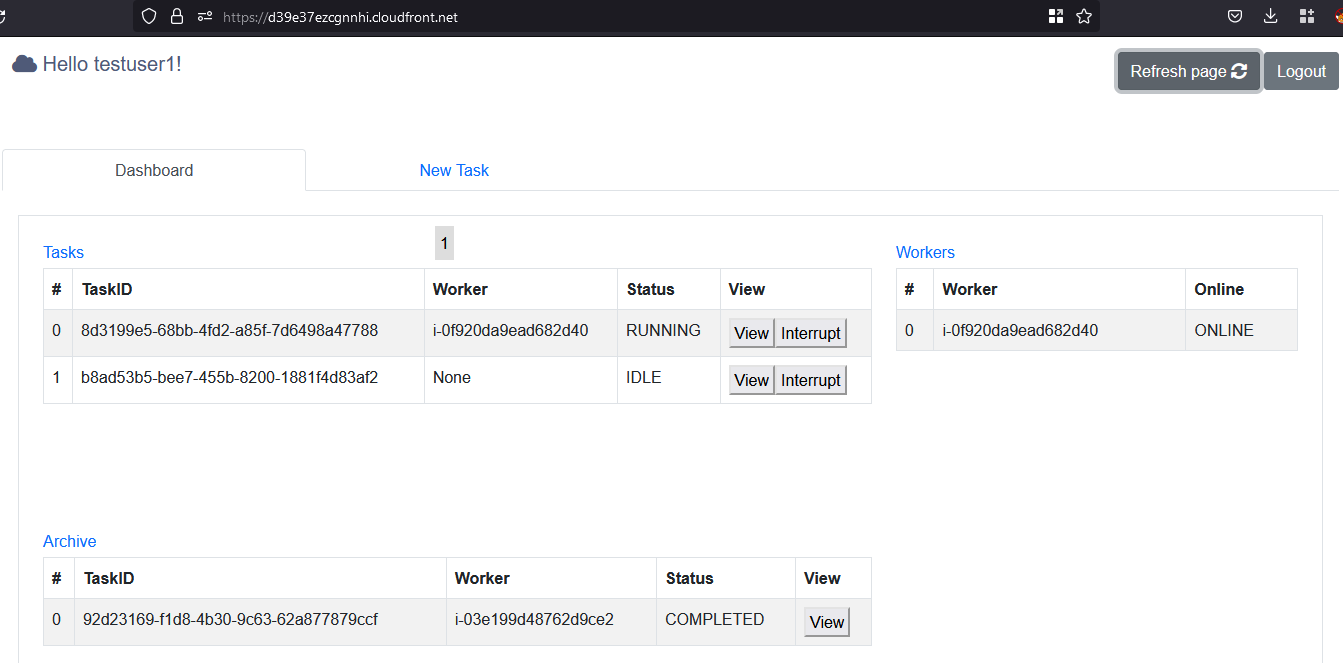
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…

[EXPERIMENTAL] Kubernetes Operator for Image Assurance

Security tools report parsers for Faradaysec.com

Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…

Exploit for CVE-2022-25173 targeting Jenkins Pipeline Groovy Plugin's CPS interpreter sandbox bypass, enabling arbitrary code execution within…

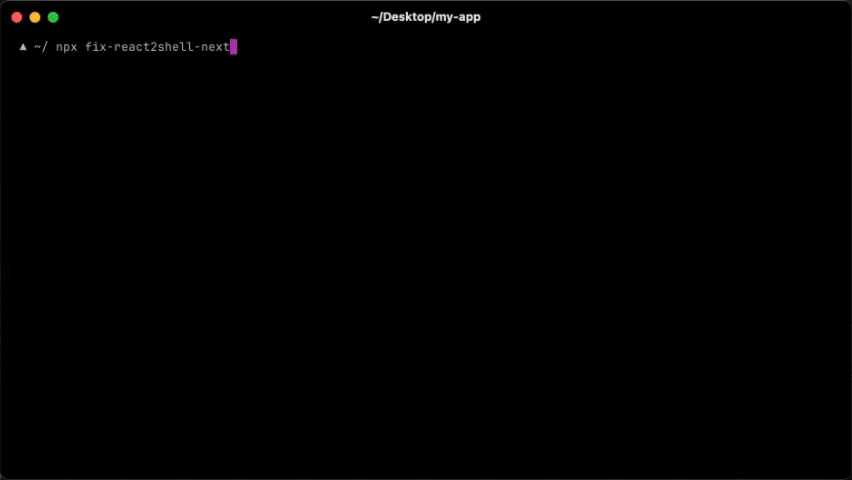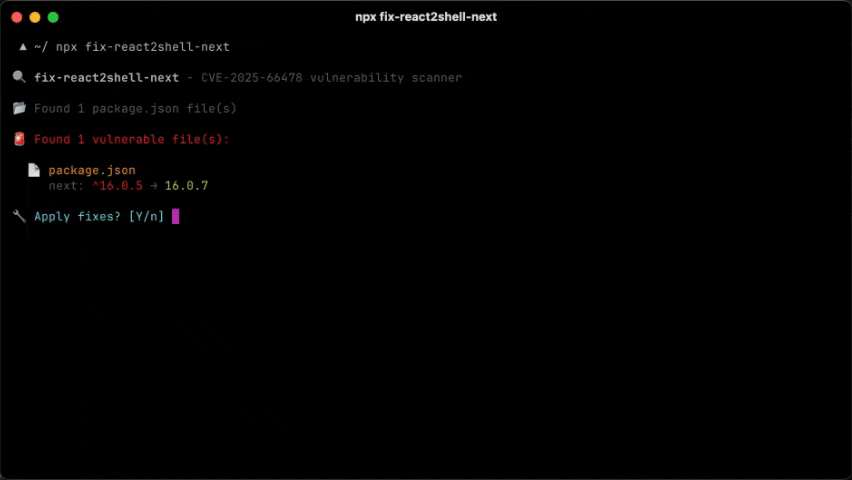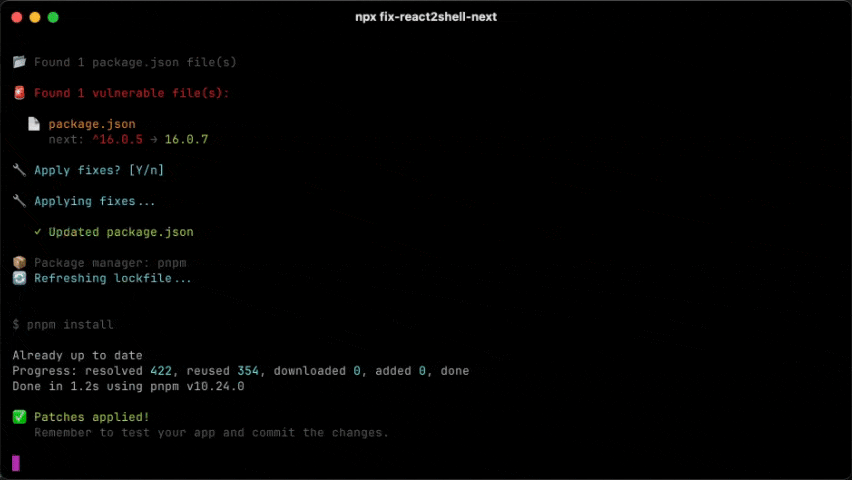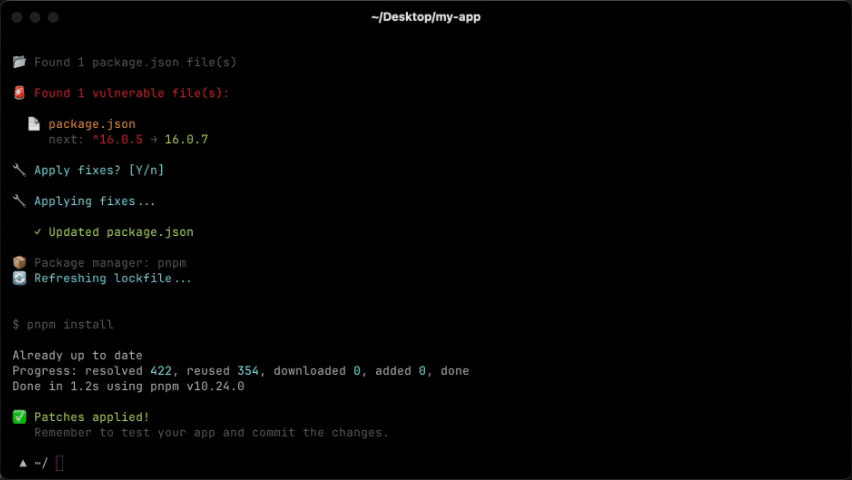
One command to fix CVE-2025-66478 (React 2 Shell RCE) in your Next.js / React RSC app.

A bash script to scan your server for React applications vulnerable to **CVE-2025-55182** — a critical remote code execution vulnerability (CVSS…

Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.

Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…

Scans selected files for patterns stated in rules. This is used in order to find secrets you may have accidentally written to a file. This scanner is…

This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode

Shell script and Ansible playbook to detect and remediate CVE-2024-3094 in xz-utils by checking package versions, upgrading or downgrading to a…

An anonymizer tool for replacing PII and similar data in dev/test databases copied from production