
o1js-scan
 auditinfra-io/o1js-scan
Dependency-free static analyzer for zk circuit soundness bugs in o1js/Mina zkApps and Noir circuits
code-analysiscryptographydefensive-tools+5
3
auditinfra-io/o1js-scanDependency-free static analyzer for zk circuit soundness bugs in o1js/Mina zkApps and Noir circuits
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 siyad01/agentbox
Open-source sandboxed runtime for AI agents — gVisor/Docker isolation, credential vault, immutable audit log. Built after CVE-2026-25253.
 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
 jbiniek/copy.fail-mitigation-mlm
Salt state to deploy a mitigation of the copy.fail vulnerability (CVE-2026-31431)
 gouldnicholas/cve-2026-4660-poc
PoC for CVE-2026-4660: arbitrary file read via git checkout in hashicorp/go-getter
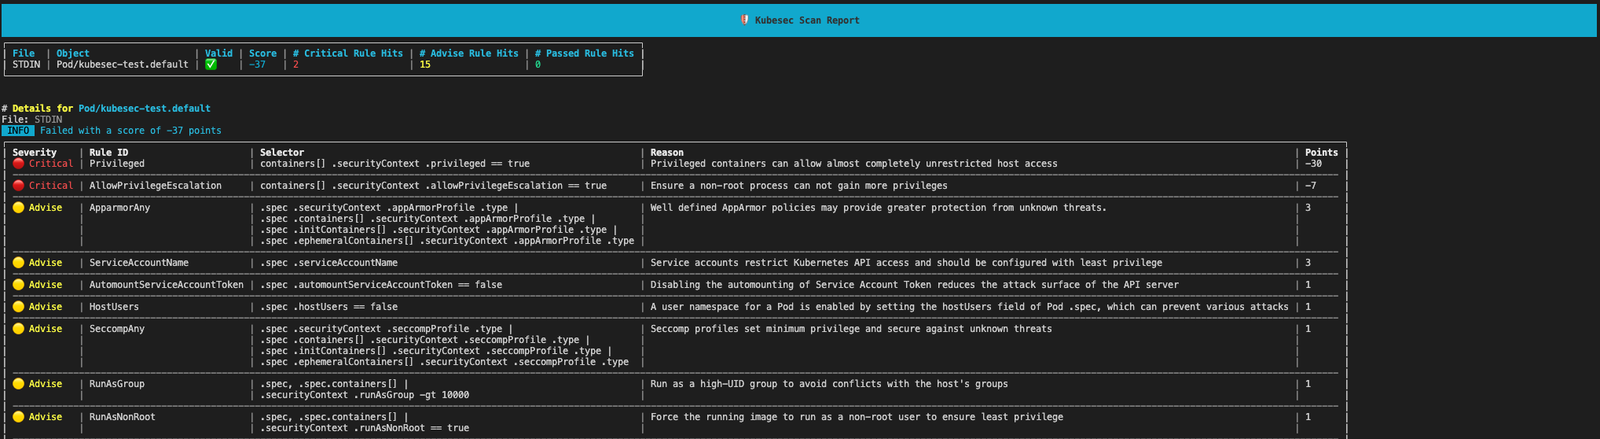 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
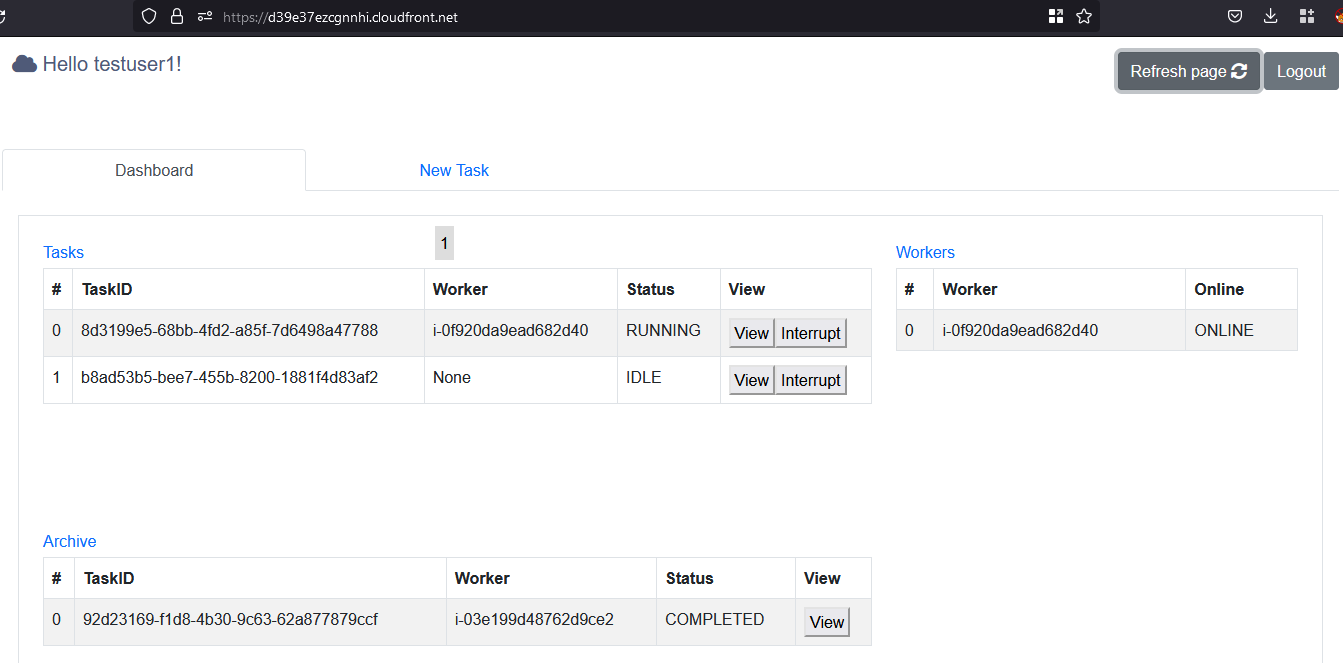 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
 aquasecurity/vex-repo-spec
VEX Repository Specification
 paveg/rails-activestorage-vips-audit
Agent skill that audits a Rails codebase for CVE-2026-66066 (KindaRails2Shell) — Active Storage + libvips arbitrary file read / RCE, checking Rails…

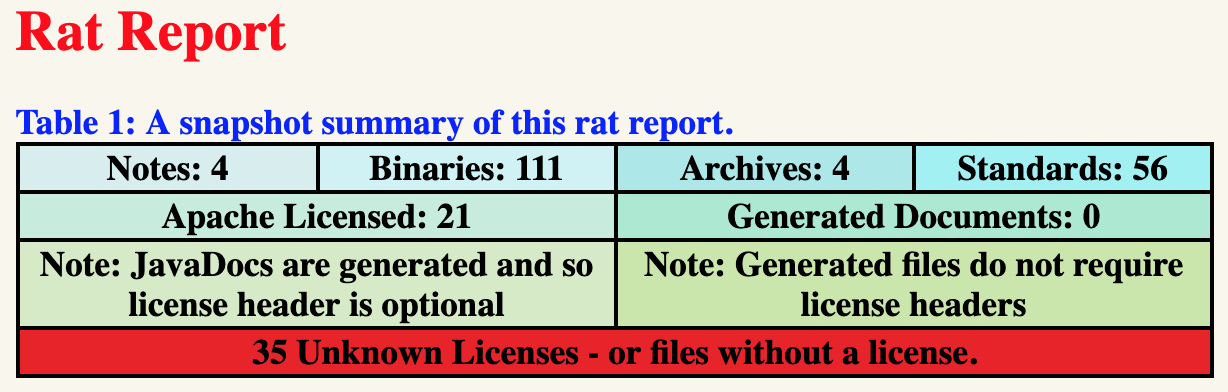 eskatos/creadur-rat-gradle
Apache RAT (Release Audit Tool) Gradle Plugin
 certbot/certbot
Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…
 sibersan/web-server-audit_cve-2026-42945
Trigger-aware web server CVE audit for nginx and Apache. Goes beyond version matching by checking whether the vulnerable code path is actually…
 shoucheng3/spring-cloud__spring-cloud-config_cve-2020-5410_2-1-8-release
Centralized configuration server for distributed systems with HTTP API, Git-backed storage, property encryption/decryption, and integration with…
 shoucheng3/spring-cloud__spring-cloud-config_cve-2020-5405_2-1-6-release
Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…
 trickyearlobe/inspec-log4j
An Inspec profile to check for Log4j CVE-2021-44228 and CVE-2021-45046