

cplt
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
ai-securitycommand-and-controlconfiguration-auditing+7
121
navikt/cpltSandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 philippeabraxas-jpg/responsible-alliance-protocol
Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 mrk336/from-foothold-to-domain-admin-weaponizing-cve-2025-54918-in-real-world-devops
Simulated exploitation and mitigation of CVE-2025-54918 (Windows NTLM flaw). Includes detection scripts, Ansible patching, and CI/CD hardening.…
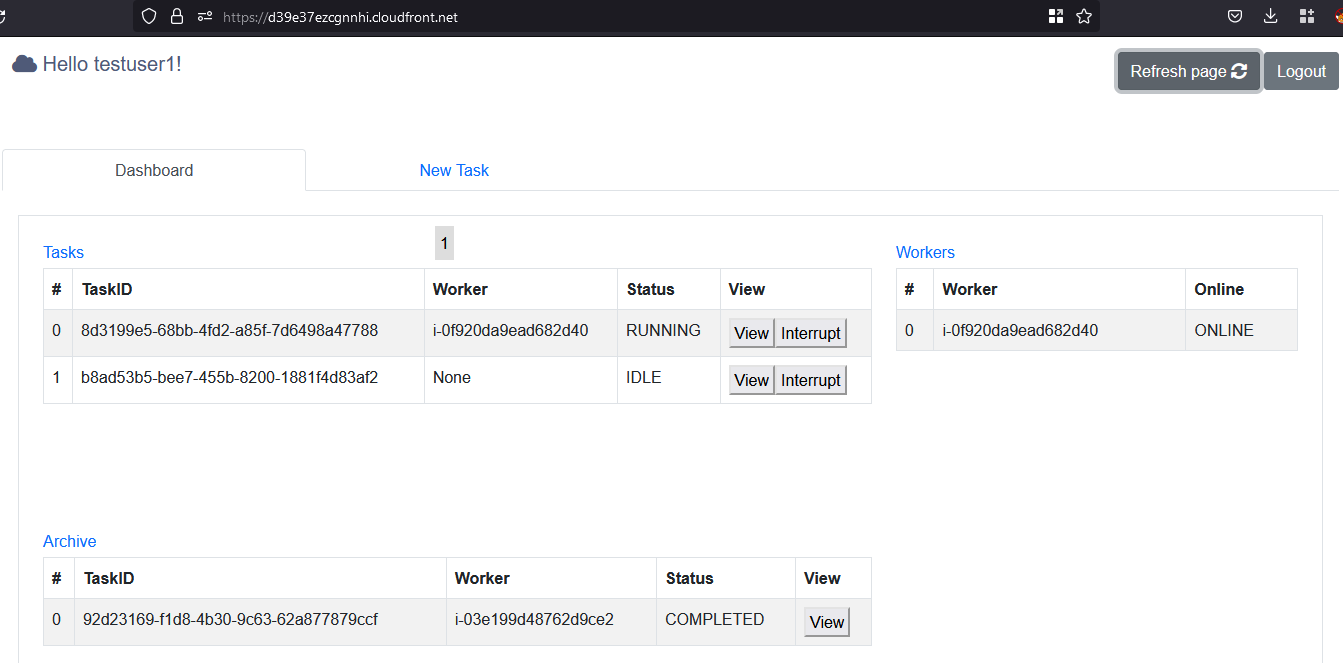 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
 wantasticapp/wantasticcore
AIO Cloud Managment Server
 danthegoodman1/netfence
Like Envoy xDS, but for eBPF filters
 teycir/apihunter
Async API security scanner in Rust for CORS, CSP, GraphQL, JWT, OpenAPI, and active API posture checks.
 kingsrule50/nessus-vulnerability-scanning-lab
Enterprise vulnerability management on Azure — Terraform-deployed Nessus scanner, credentialed scanning, CVE-2013-3900 remediation with verified…
 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
 c3rb3ru5d3d53c/signatures
Community Detection Signature Build and Distribution Pipeline for YARA, Suricata, Snort and Sigma
 arnaudluti/ps-cve-2021-44228
Static detection of vulnerable log4j librairies on Windows servers, members of an AD domain.
 punk-security/dnsreaper
Fast subdomain takeover scanner with 50+ signatures, supporting cloud provider integrations (AWS, Azure, Cloudflare) and CI/CD pipeline mode for…
 domain-protect/domain-protect
OWASP Domain Protect - prevent subdomain takeover
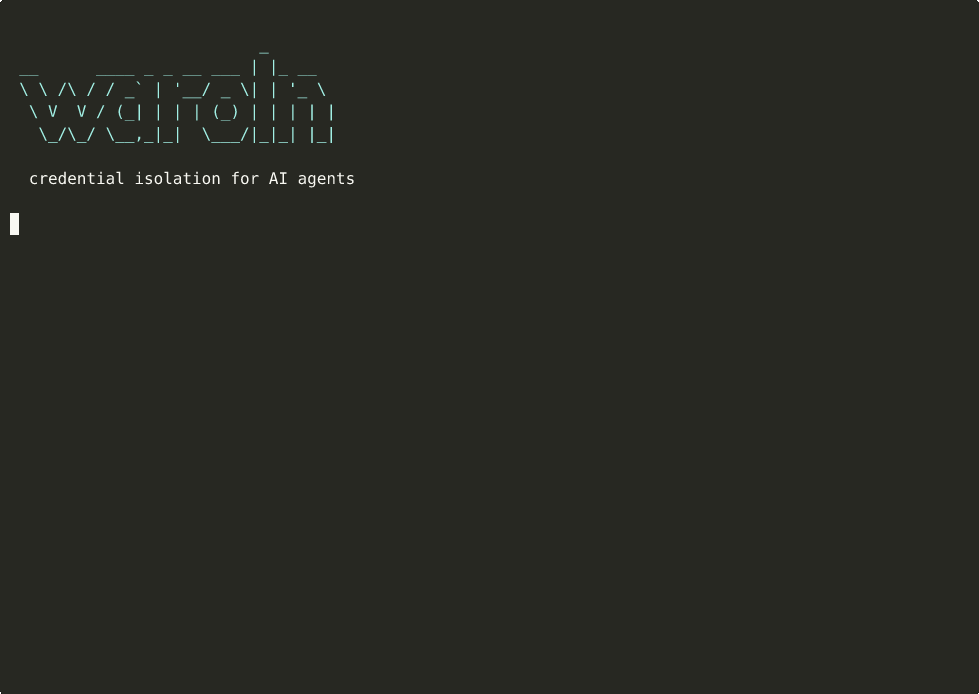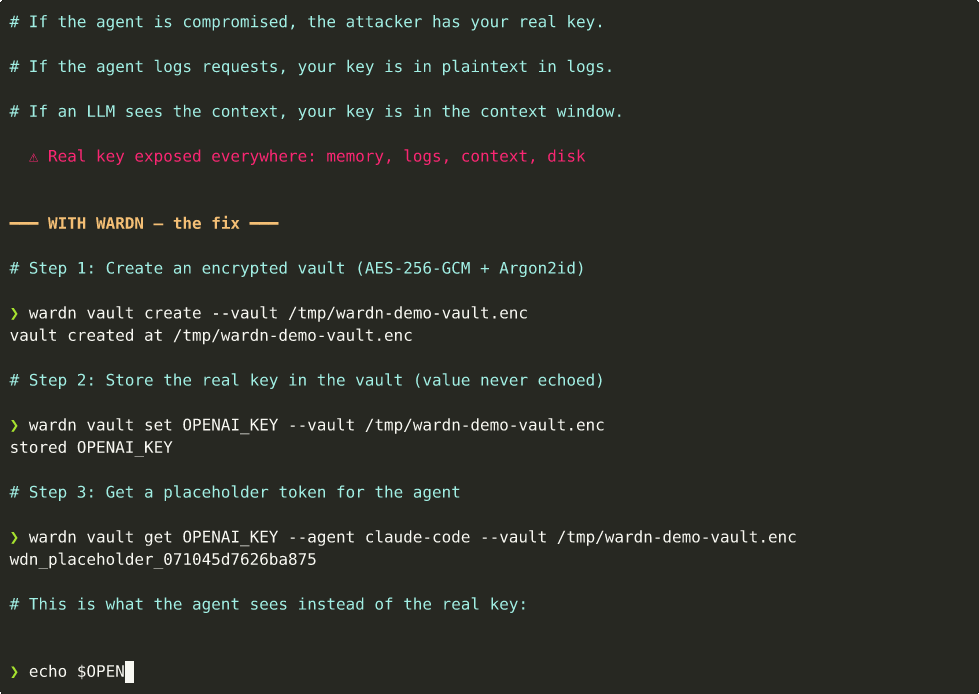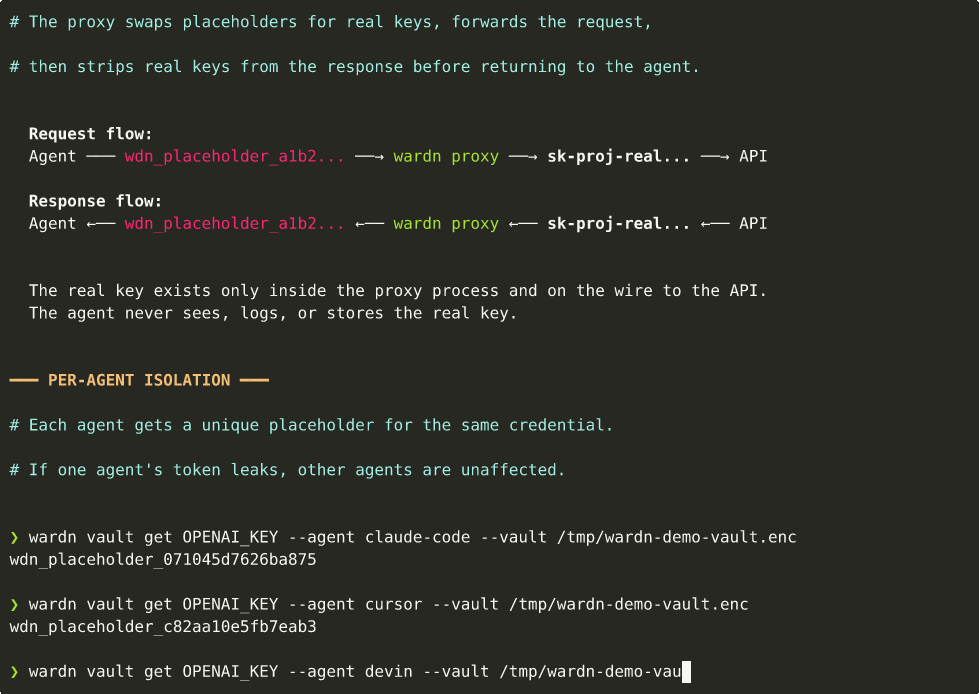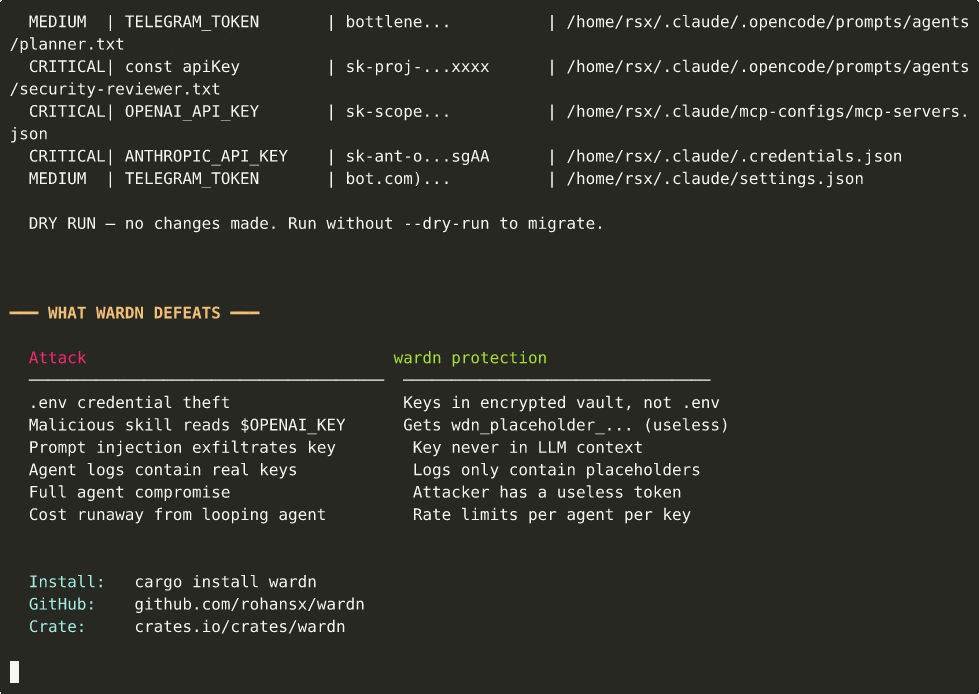 rohansx/wardn
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.
 shoucheng3/cov-int
XWiki Commons CVE-2023-31126 v14.10.3 for Coverity analysis
 pompelmi/pompelmi
ClamAV antivirus scanning for Node.js — scan file uploads with a single function call. Zero dependencies. Typed Symbol verdicts. Local or…