
airgap
 xtuc/airgap
Security for the modern age of AI: defend against bad AI agents and malicious npm packages
ai-securitycontainer-securitydefensive-tools+3
xtuc/airgapSecurity for the modern age of AI: defend against bad AI agents and malicious npm packages
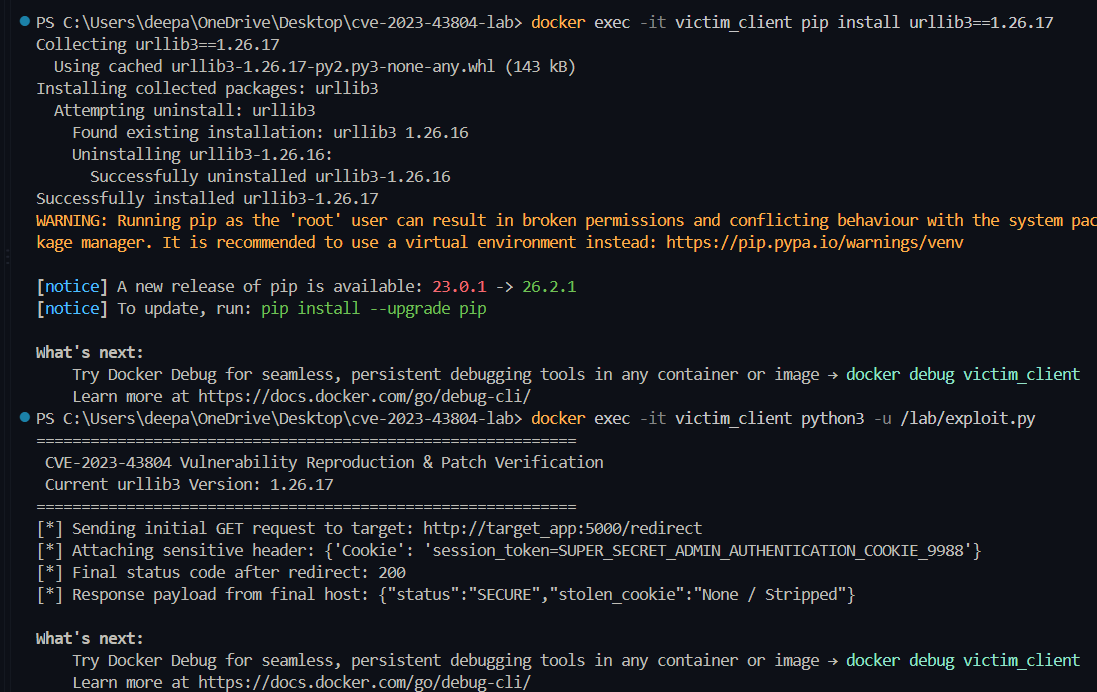 deepanshu-khurana/cve-2023-43804
Containerized three-tier lab reproducing CVE-2023-43804 urllib3 cookie leak via cross-origin redirects, with exploit script and patch verification.
 acharaf06/cve-2017-5638-attack-and-defense
Docker-based security lab demonstrating Apache Struts2 S2-045 (CVE-2017-5638) exploitation and defense, featuring vulnerable and patched applications…
 ahndrewalters/projectsecurity-homelab
Hands-on homelab simulating the Log4Shell (CVE-2021-44228) vulnerability. Deploy Docker containers to build a vulnerable target and attacker machine,…
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 ikarolaborda/cve2026-42926
Controlled NGINX HTTP/2 frame injection lab for CVE-2026-42926 patch validation and defensive research
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 gmh5225/disclosure-check
Tool to identify the best mechanisms for privately disclosing a security vulnerability for a package/project.
 graphenex/graphenex
Automated System Hardening Framework
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
 jp1337/easywall
Web interface for the nftables firewall on Linux, written in Go. The apply undoes itself after 120 seconds unless you confirm it — you cannot lock…
 aarif450/zapscape
Guest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 knqyf263/aqua-checksums
Monitors cryptographic integrity of container images, releases, and Git tags for supply chain security, verifying Sigstore cosign signatures with…
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 kubearmor/kubearmor
Runtime Security Enforcement System. Workload hardening/sandboxing and implementing least-permissive policies made easy leveraging LSMs (LSM-BPF,…
 cybereason-public/owlsm
Sigma Rules Engine inside the Linux Kernel using eBPF. Focusing on prevention capabilities