
EfiGuard
 mattiwatti/efiguard
Disable PatchGuard and Driver Signature Enforcement at boot time
binary-analysisdefensive-toolsexploitation+1
2.5k
mattiwatti/efiguardDisable PatchGuard and Driver Signature Enforcement at boot time
 dosx-dev/obfus.h
Macro-header for compile-time C obfuscation (tcc, win x86/x64)
 c3rb3ru5d3d53c/mwcfg
A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck
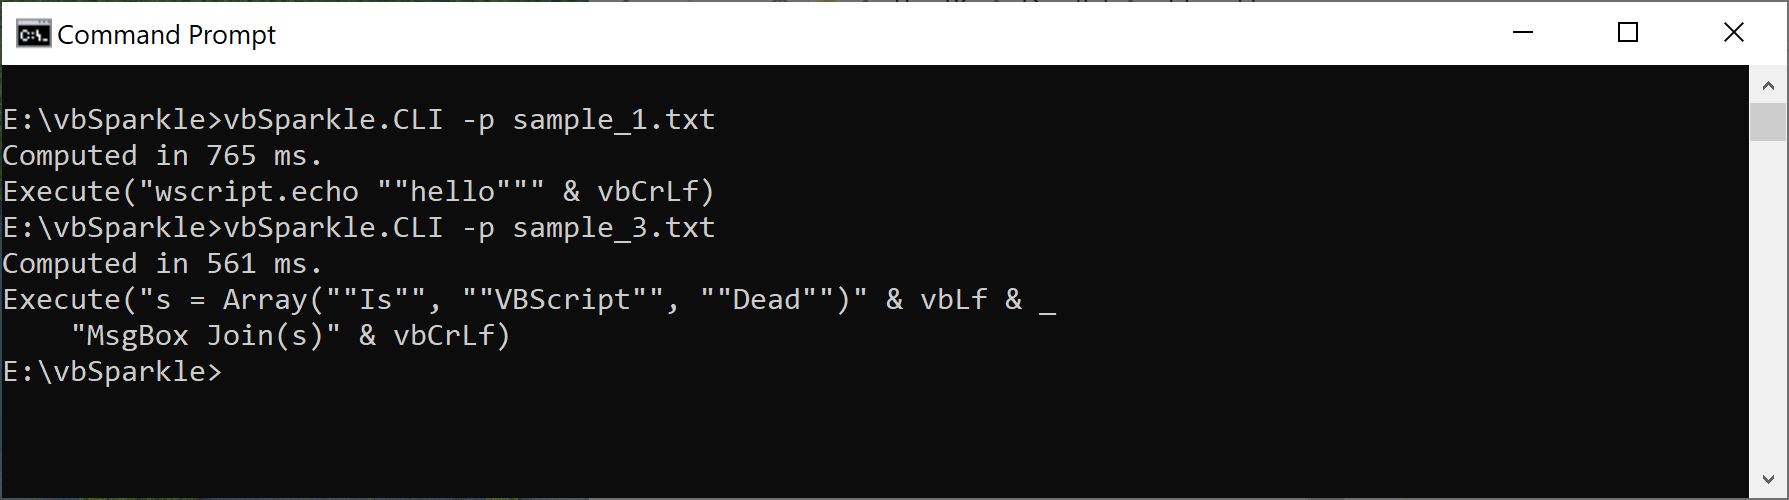 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
 gmh5225/anti_suspend
Protect process by shellcode
 gmh5225/deobf-arxan-deob-c
Simple C program to quickly deobfuscate windows executables protected with Arxan.
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 gmh5225/asm-obfuscator
Obfuscates x86-64 assembly with instruction injection, junk code, constant obfuscation, and runtime decryption to hinder reverse engineering and…
 javascript-obfuscator/javascript-obfuscator
Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…
 devianntsec/cve-2024-51324
Master's Thesis research on CVE-2024-51324 (BYOVD). Advanced exploit with 4 operational modes (SCANNER, LOADER, KILLER, CLEANUP), SHA-256 driver…
 lilify-jp/squre
🛡️ Open-source binary protection toolkit for Windows PE. Nanomite, VM protection, anti-debug, and more.
 jkornev/hidden
🇺🇦 Windows driver with usermode interface which can hide processes, file-system and registry objects, protect processes and etc
 dissectmalware/yaradbg-frontend
Web-based Yara rule debugger with an editor, live match evaluation, matched-string details, and rule dependency visualization for detection…
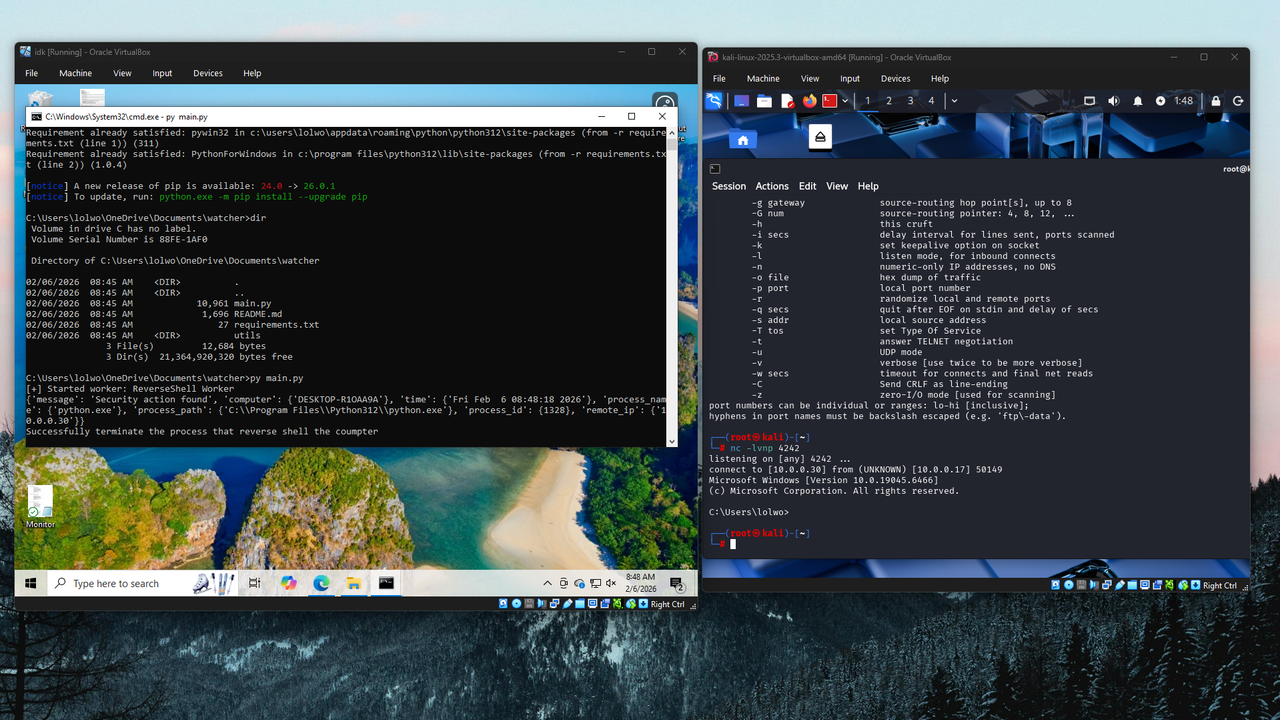 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
 lolbas-project/lolbas
Living Off The Land Binaries And Scripts - (LOLBins and LOLScripts)
 cisco-talos/clamav
Open-source antivirus engine for detecting trojans, viruses, and malware via signature-based scanning; includes a daemon, on-demand CLI, and…
 freedomofpress/dangerzone
Take potentially dangerous PDFs, office documents, or images and convert them to safe PDFs
 rabbitstack/fibratus
Security sensor for realtime threat detection and protection