
seccubus
 seccubus/seccubus
Easy automated vulnerability scanning, reporting and analysis
defensive-toolslog-analysisnetwork-mapping+5
seccubus/seccubusEasy automated vulnerability scanning, reporting and analysis
 taisa456/network-security-snort
Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
 korben00/no-gdid
Read, understand and silence the Windows GDID device identifier (the ID that tracked a hacker through a VPN). Verified on a real Win11 VM. Honest: it…
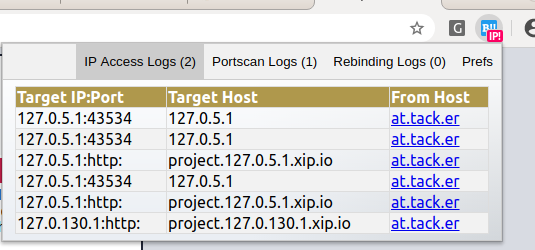 mindedsecurity/behave
Behave! A monitoring browser extension for pages acting as "bad boi"
 loresuso/psc
the ps utility, with an eBPF twist and container context
 blacksnufkin/invoke-dumpmdeconfig
PowerShell script to dump Microsoft Defender Config, protection history and Exploit Guard Protection History (no admin privileges required )
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
 mubix/find-wsus
Helps defenders find their WSUS configurations in the wake of CVE-2025-59287
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
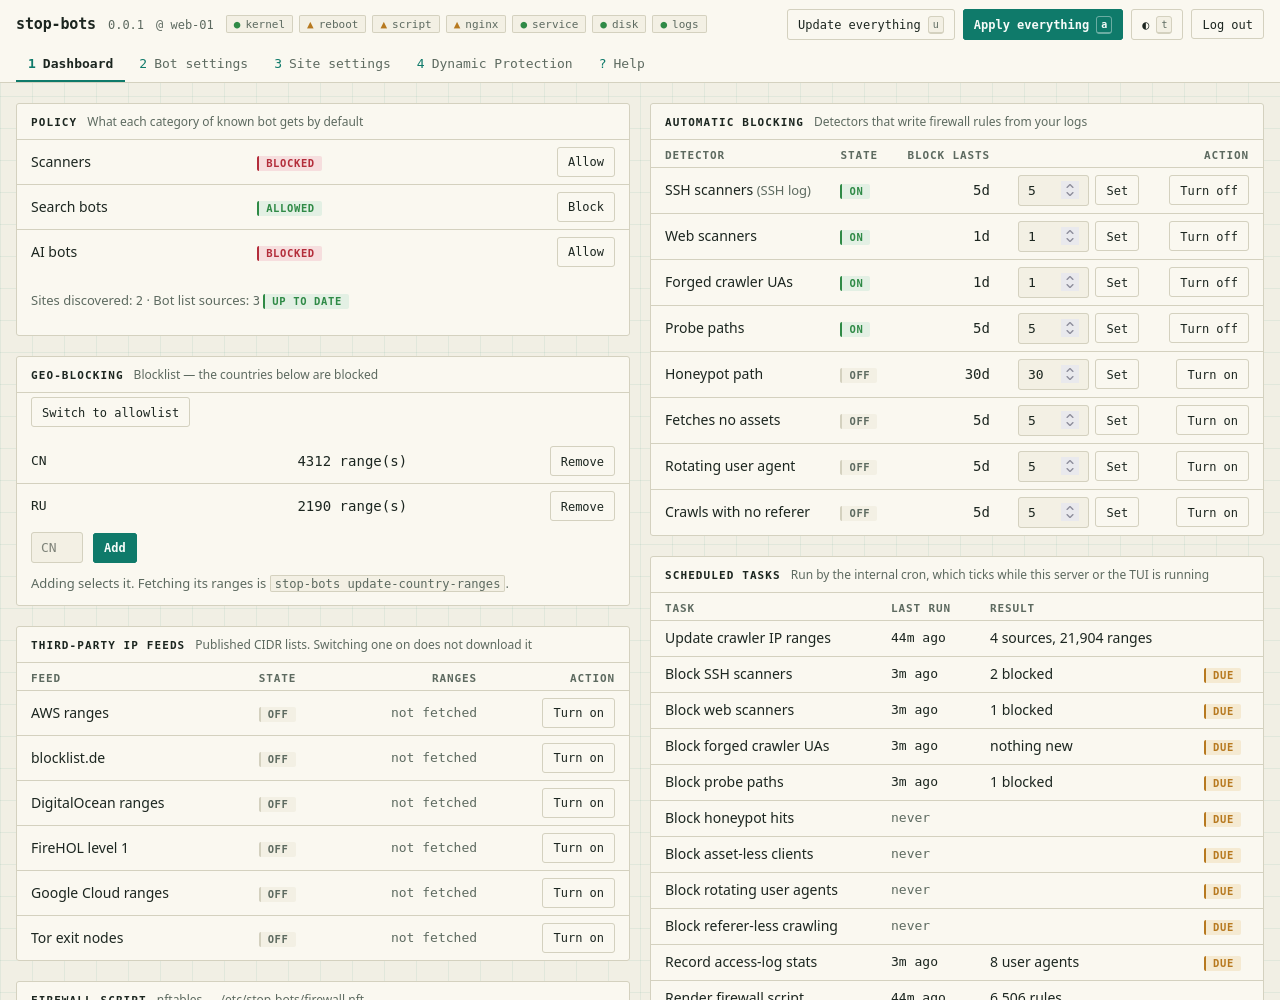 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 pbxqdown/portclue
Explain why a Linux TCP port may or may not be reachable
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 freeguy-6/dmz-security-monitoring-hardening
CY376 Blue Team project — pfSense DMZ, Suricata IDS/IPS, and automated host hardening against CVE-2014-6271
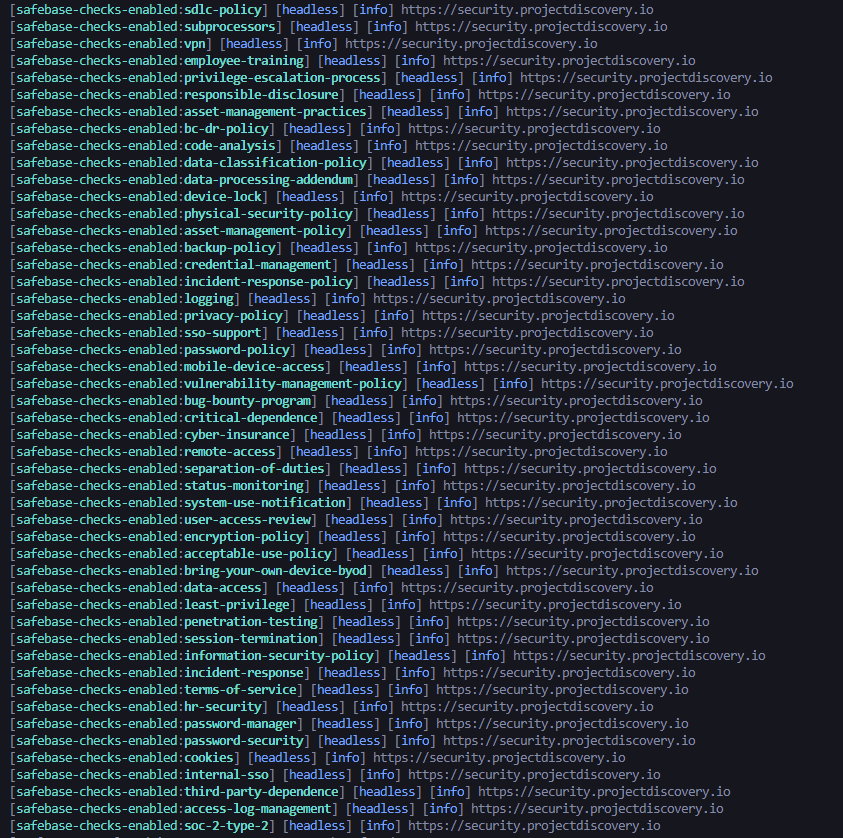 rxerium/internal-security-detect
The detection of internal security controls at a company
 sreejaputhan/cpanel-control-plane-exposure-check
Defensive exposure assessment tool for identifying externally accessible cPanel, WHM, and Webmail management interfaces related to CVE-2026-41940.
 hnytgl/cve-2026-34197
这是一个面向防守和内网排查的 Apache ActiveMQ Classic 暴露面检测工具,用于辅助评估 CVE-2026-34197 相关风险。