
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
146 results
attack_monitor preview

attack_monitor

GitHubyarox24/attack_monitor

Endpoint detection & Malware analysis software
defensive-toolsdynamic-analysis-sandboxingincident-response+1
234
6 years ago
HookTools preview

HookTools

GitHubgmh5225/hooktools

Basic injectable for analyzing the behavior of evasive malware
binary-analysisdebuggersdefensive-tools+3
2 years ago
fake-sandbox preview

fake-sandbox

GitHubnuclearphoenixx/fake-sandbox

👁‍🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.
anti-botdefensive-toolsids-ips-evasion+1
1421 year ago
SilkETW preview
Archived

SilkETW

GitHubmandiant/silketw

C# wrapper for ETW that serializes kernel and user-mode event data to JSON for threat hunting, malware analysis, and incident response, with Yara…
anomaly-detectiondefensive-toolsdigital-forensics+8
8523 years ago
mod_plaintext.py preview

mod_plaintext.py

GitHubjeremyngalloway/mod_plaintext.py

Archived copy of the mod_plaintext.py "Internet Chemotherapy" IoT worm payload, preserved with archival references for malware research and…
curated-resourcesdefensive-toolsmalware-analysis+2
688 years ago
hollows_hunter preview

hollows_hunter

GitHubhasherezade/hollows_hunter

Scans all running processes. Recognizes and dumps a variety of potentially malicious implants (replaced/implanted PEs, shellcodes, hooks, in-memory…
defensive-toolsforensicsincident-response+2
2.4k4 months ago
memhunter preview

memhunter

GitHubmarcosd4h/memhunter

Live hunting of code injection techniques
defensive-toolsincident-responsemalware-analysis+1
3857 years ago
FalconEye preview

FalconEye

GitHubrajiv2790/falconeye

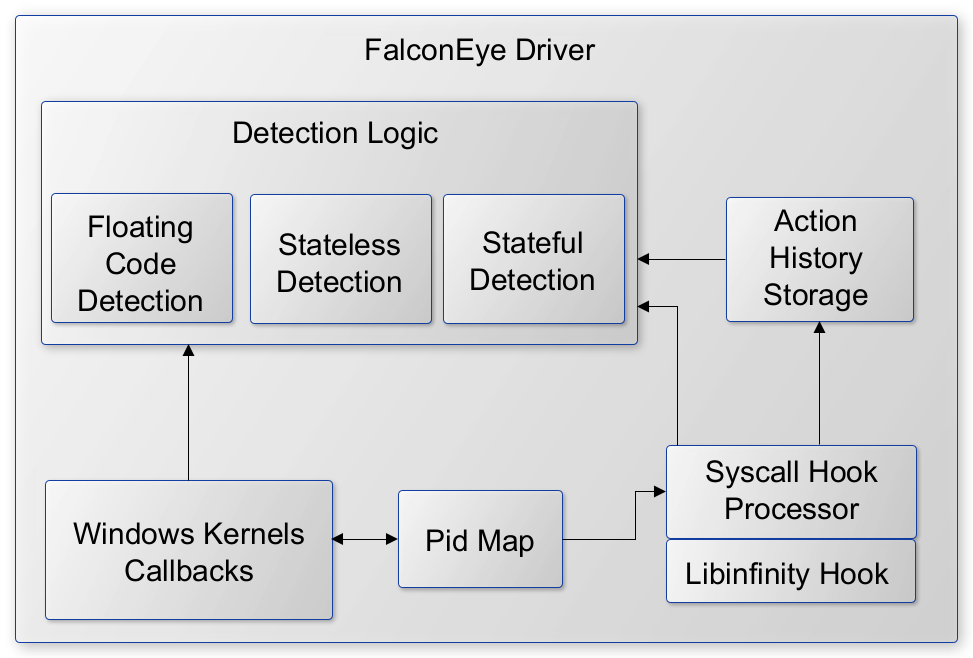
Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…
binary-analysisdefensive-toolsintrusion-detection+1
3095 years ago
kli-ex preview

kli-ex

GitHubgmh5225/kli-ex

Extended kernel lazy importer for Windows drivers that resolves APIs at runtime with encrypted, cached import names to hide kernel function usage…
binary-analysiscryptographydefensive-tools+4
343 years ago
yara-rules preview

yara-rules

GitHubdr4k0nia/yara-rules

A collection of my yara rules
defensive-toolsmalware-analysisthreat-intelligence
343 years ago
zombieguard preview

zombieguard

GitHubmdshoaibuddinchanda/zombieguard

ML-based detection of Zombie ZIP archive header evasion attacks (CVE-2026-0866)
binary-analysisdefensive-toolsmachine-learning+4
51 month ago
NeuPerm preview

NeuPerm

GitHubdanigil/neuperm

Zero-retraining sanitization that reorders permutation-equivalent neural network units to destroy malware embedded via weight-steganography attacks…
ai-securitydefensive-toolsmachine-learning+3
1 month ago
RAR-Anomaly-Inspector preview

RAR-Anomaly-Inspector

GitHubilhamrzr/rar-anomaly-inspector

Defensive PowerShell tool for static inspection of RAR archives and detection of CVE-2025-8088 path traversal anomalies.
defensive-toolsforensicsincident-response+3
19 months ago
GCTI preview
Archived

GCTI

GitHubchronicle/gcti

Detection signature repository providing YARA rules and threat-hunting content for identifying malware and malicious activity across enterprise…

defensive-toolsintrusion-detectionmalware-analysis+1
5542 years ago
KDU preview

KDU

GitHubhfiref0x/kdu

Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
binary-exploitationdefensive-toolsexploitation+8
2.8k1 month ago
RedTeamCCode preview

RedTeamCCode

GitHubmr-un1k0d3r/redteamccode

Red Team C code repo
binary-analysisdefensive-toolsmalware-analysis+1
5741 year ago
amun preview

amun

GitHubzeroq/amun

Amun Honeypot

defensive-toolsmalware-analysisnetwork-security+1
637 years ago
vbSparkle preview

vbSparkle

GitHubairbus-cert/vbsparkle

VBScript & VBA source-to-source deobfuscator with partial-evaluation

code-analysisdefensive-toolsmalware-analysis+2
814 years ago
Previous12…9Next