soc-investigation-powershell-edrfreeze

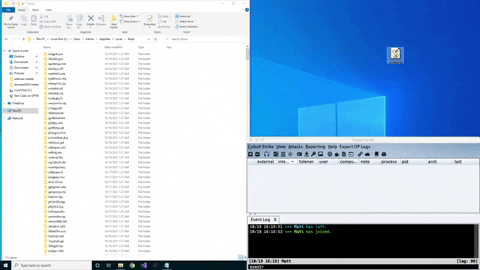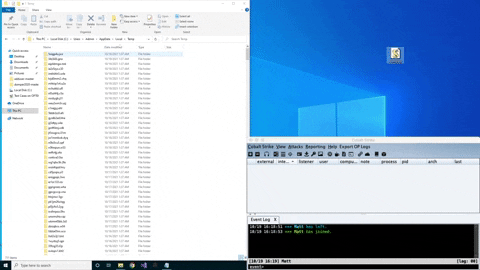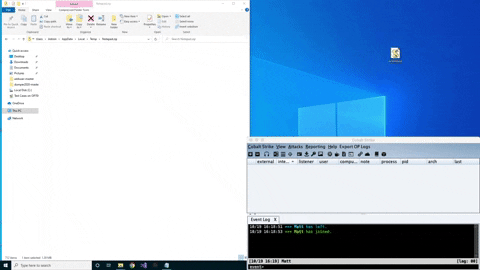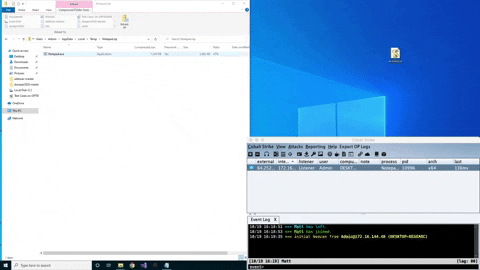
SOC investigation of CVE-2024-49138 exploitation alert involving PowerShell, EDRFreeze execution, and defense evasion behavior in a simulated…

SOC investigation of CVE-2024-49138 exploitation alert involving PowerShell, EDRFreeze execution, and defense evasion behavior in a simulated…

Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…

Dynamic Windows API resolver and unhooker that detects and restores hooked functions (IAT, EAT, inline patches) to invoke unmonitored system calls…

Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…

PowerShell Remote Download Cradle Generator & Obfuscator

XLL Phishing Tradecraft

Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.

LoadLibrary for offensive operations

A unique technique to execute binaries from a password protected zip

Tool for embedding payloads into JPG/PNG format images, allowing to perform certain actions when opening them.

POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs

Python-based simulated firewall to detect and block Spring4Shell (CVE-2022-22965) exploit attempts. This project filters HTTP requests by identifying…

A BYOSI (Bring-Your-Own-Script-Interpreter) Rapid Payload Deployment Toolkit

#PaperCut CVE-2026-81578 + CVE-2026-82078 Defense Toolkit 2 3 A **defensive** toolkit to check and understand exposure to the chained

🔥 XSS2Shell — CVE-2026-64638 Scanner & PoC Toolkit

Header-only Windows x64 indirect syscall library. Zero CRT, zero IAT, VEH anti-BP, AMSI/ETW bypass, W^X memory, per-call dynamic stubs.

Generate an obfuscated DLL that will disable AMSI & ETW