Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
19 results
MappedImagesDetector preview

MappedImagesDetector

GitHubadem-hosni/mappedimagesdetector

Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk

anomaly-detectionbinary-analysisdefensive-tools+4
1
10 months ago
Mangle preview
Archived

Mangle

GitHuboptiv/mangle

Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs

binary-analysisdefensive-toolsexploitation+6
1.2k3 years ago
CLR-Unhook preview

CLR-Unhook

GitHubhwbp/clr-unhook

Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…

defensive-toolsexploitationpayload-development+3
21710 months ago
SigFlip preview

SigFlip

GitHubmed0x2e/sigflip

SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.

binary-analysiscode-analysisdefensive-tools+5
1.3k3 years ago
RC4Decryption preview

RC4Decryption

GitHubweedhashpeddler/rc4decryption

Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…

binary-analysiscryptographydefensive-tools+6
371 month ago
ghostdebug preview

ghostdebug

GitHubvollragm/ghostdebug

Debugger utilizing stealth hooks to hide from debugger detection

binary-analysisdebuggersdefensive-tools+1
272 months ago
QuickAssist_UAC_Bypass preview

QuickAssist_UAC_Bypass

GitHubr41n3rzuf477/quickassist_uac_bypass

UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…

defensive-toolsexploitationpayload-development+4
2443 months ago
cve-2026-25676 preview

cve-2026-25676

GitHubnexxus67/cve-2026-25676

Research and proof-of-concept for CVE-2026-25676, a DLL search path hijacking vulnerability in M-Track Duo HD installer, including root cause…

binary-analysisdefensive-toolseducation+3
18 months ago
gluegate preview

gluegate

GitHubsbousseaden/gluegate

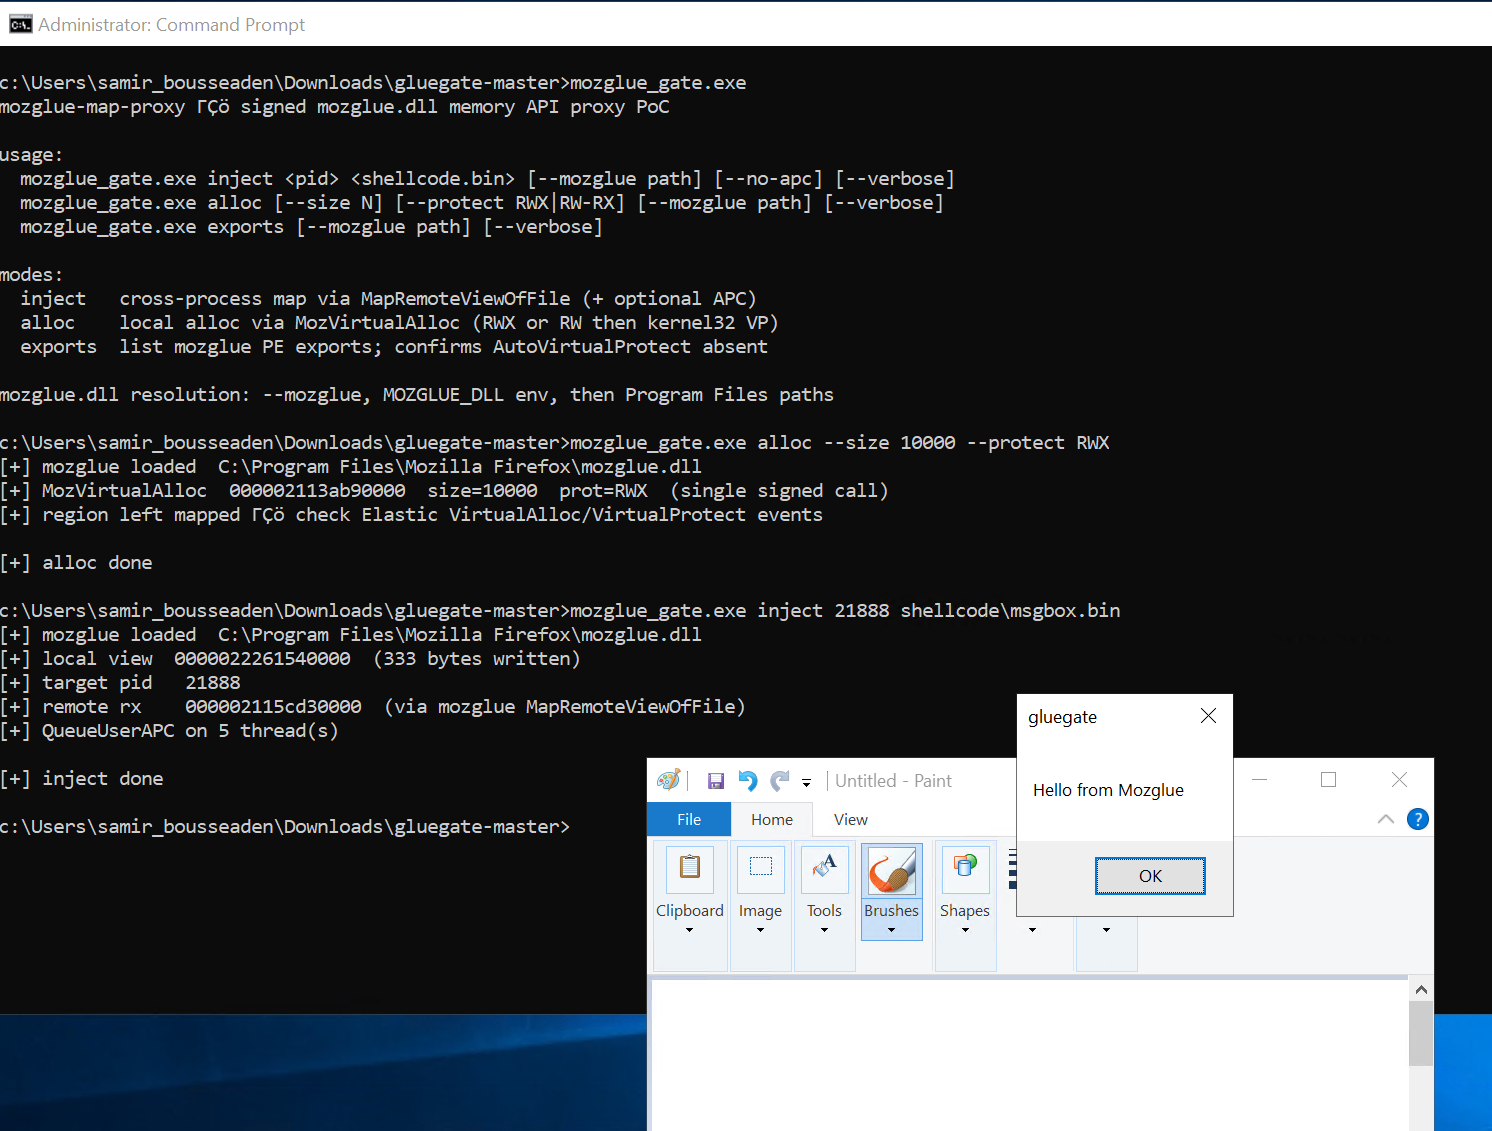
Memory API proxy via signed mozglue.dll

defensive-toolsids-ips-evasionmemory-forensics+2
394 months ago
uac-a-mola preview

uac-a-mola

GitHubtelefonica/uac-a-mola

Modular framework for Windows UAC bypass attacks and mitigation, featuring DLL hijacking, fileless execution, and real-time monitoring to detect and…

defensive-toolsexploit-frameworkspenetration-testing+1
1075 years ago
LightsOut preview

LightsOut

GitHubicyguider/lightsout

Generate an obfuscated DLL that will disable AMSI & ETW

defensive-toolsexploitationpayload-generation+1
3352 years ago
GoDefender preview
Archived

GoDefender

GitHubkiexitdispatcher/godefender

Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.

anti-botbinary-analysisdefensive-tools+3
85810 months ago
RCLocals preview

RCLocals

GitHubyjesus/rclocals

Linux startup analyzer

defensive-toolsforensicshash-analysis+4
661 year ago
DarkLoadLibrary preview

DarkLoadLibrary

GitHubbats3c/darkloadlibrary

LoadLibrary for offensive operations

binary-analysisdefensive-toolsexploitation+2
1.2k5 years ago
MagicSigner preview

MagicSigner

GitHubnamazso/magicsigner

Signtool for expired certificates

adversarial-attackauthentication-authorizationdefensive-tools+2
5243 years ago
FalconEye preview

FalconEye

GitHubrajiv2790/falconeye

Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…

binary-analysisdefensive-toolsintrusion-detection+1
3105 years ago
malware-analysis-fake-hwmonitor preview

malware-analysis-fake-hwmonitor

GitHubdmitry-matvienko/malware-analysis-fake-hwmonitor

Technical analysis, writeup, and YARA rules for a DLL Sideloading campaign disguised as HWMonitor

defensive-toolsdigital-forensicseducation+6
11 month ago
NativeMirror preview

NativeMirror

GitHubhabanada/nativemirror

Native Delphi implementation of PE-sieve functionality with a reusable library, CLI, and PE-sieve-compatible DLL for HollowsHunter integration.

binary-analysisdefensive-toolsdigital-forensics+4
58 days ago
Previous12Next