
YARA_Rules
 malgamy/yara_rules
Curated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
curated-resourcesdefensive-toolsincident-response+3
65
malgamy/yara_rulesCurated signature-rule collection for detecting and classifying malicious files via pattern matching, with CLI instructions for scanning files and…
 zephrfish/stompy
Timestomp Tool to flatten MAC times with a specific timestamp
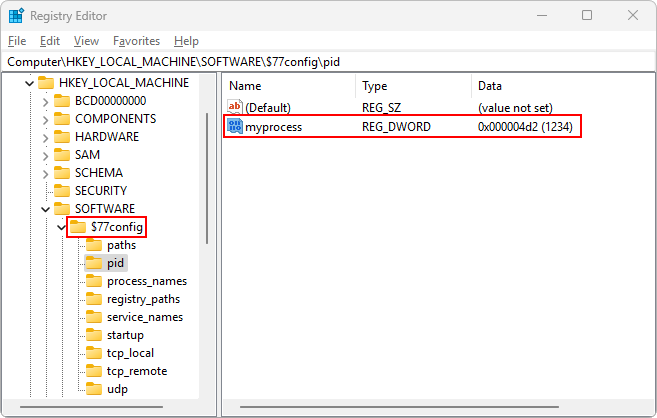 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 twosevenonet/edr-redir
Redirects EDR working folders using a Bind Filter (bindflt.sys) to bypass endpoint detection, corrupt EDR services, or replace with…
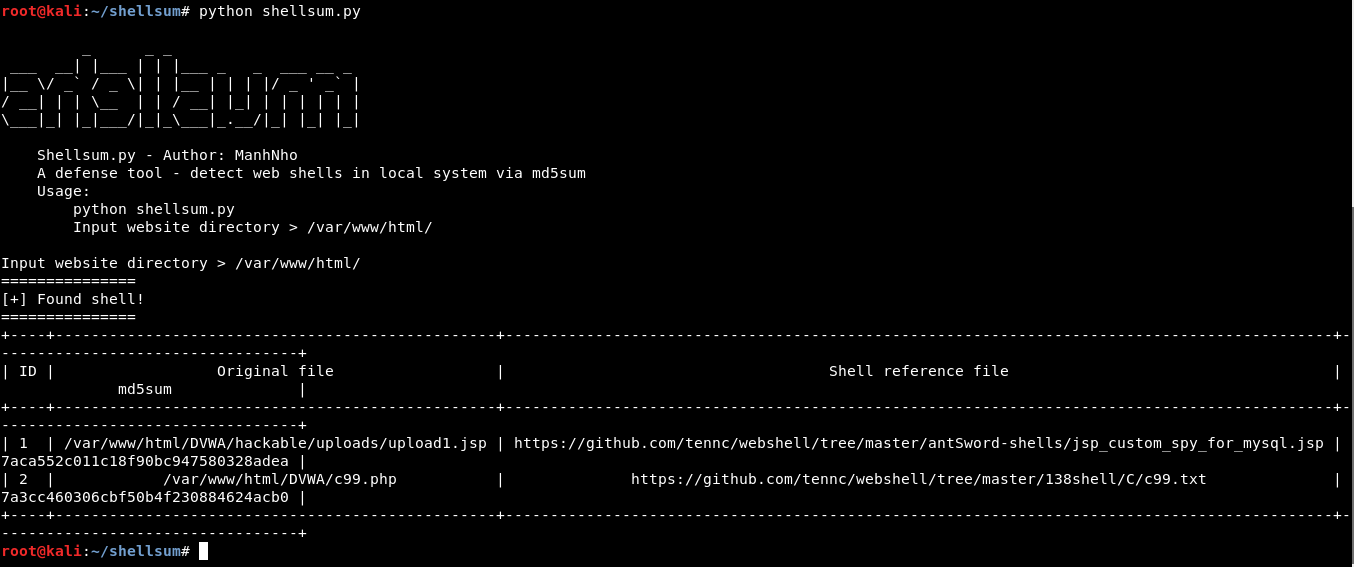 manhnho/shellsum
A defense tool - detect web shells in local directories via md5sum