
CVE-2022-30190
 ernestak/cve-2022-30190
Official guidance and workarounds for CVE-2022-30190, a remote code execution vulnerability in the Microsoft Support Diagnostic Tool (MSDT)…
defensive-toolseducationexploitation+3
ernestak/cve-2022-30190Official guidance and workarounds for CVE-2022-30190, a remote code execution vulnerability in the Microsoft Support Diagnostic Tool (MSDT)…
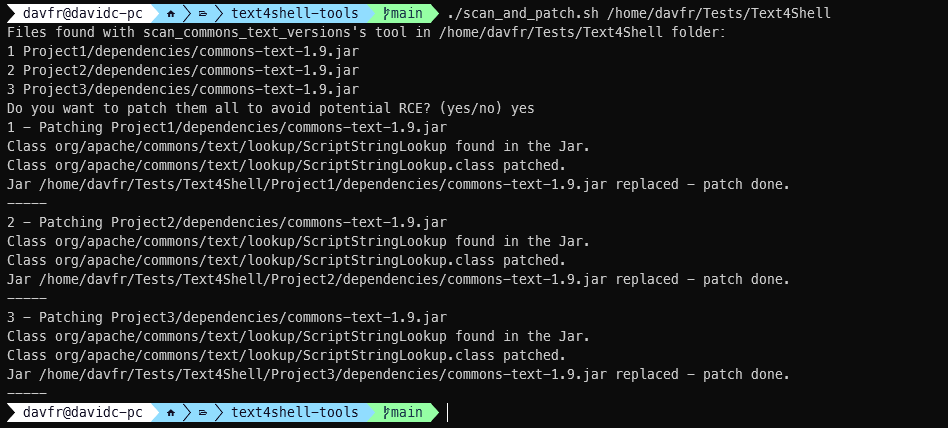 jfrog/text4shell-tools
Detect and patch vulnerable Apache Commons Text in Java JAR/WAR artifacts; fingerprint classes and scan bytecode for CVE-2022-42889 (Text4Shell) call…
 h4ckm310n/cve-2022-0847-ebpf
An eBPF program to detect attacks on CVE-2022-0847
 tiktb8/cve-2022-29072
Powershell to mitigate CVE-2022-29072
 fdjy1234/cve-2022-41404-dos-protection
Windows Apache Tomcat resource limits implementation guide for CVE-2022-41404 DoS vulnerability protection
 phantomiman/7-zip.chm-mitigation
7-Zip CVE-2022-29072 Mitigation - CHM file - This script detects if the .chm file exists and removes it.
 rouben/cve-2022-30190-nsis
An NSIS script that helps deploy and roll back the mitigation registry patch for CVE-2022-30190 as recommended by Microsoft
 jeffreybxu/five-nights-at-follina-s
A Fullstack Academy Cybersecurity project examining the full cycle of the Follina (CVE-2022-30190) vulnerability, from exploit to detection and…
 derco0n/mitigate-folina
Mitigates the "Folina"-ZeroDay (CVE-2022-30190)
 cyberdashy/cve-2022-30190
PowerShell script to mitigate CVE-2022-30190 by updating a registry DWORD key, designed for deployment via RMM tools like ConnectWise Automate.
 sentrium-security/follina-workaround-cve-2022-30190
PowerShell scripts to apply and restore Microsoft's registry-based workaround for CVE-2022-30190 (Follina) vulnerability, deployable via InTune for…
 jotaqc/cve-2022-30190_temporary_fix
These are two Python scripts compiled to easily and quickly apply temporary protection against the CVE-2022-30190 vulnerability (Follina)
 aur3ns/block-spring4shell
POC firewall with rules designed to detect and block Spring4Shell vulnerability (CVE-2022-22965) exploit
 jotaqc/cve-2022-30190_temporary_fix_source_code
These are the source codes of the Python scripts to apply the temporary protection against the CVE-2022-30190 vulnerability (Follina)
 cosmo121/follina-remediation
Removes the ability for MSDT to run, in response to CVE-2022-30190 (Follina)