
waf-fu
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
cloud-securitydefensive-toolsincident-response+6
2
confused-binary/waf-fuTerminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
 zephrfish/cve-2025-53770-scanner
ToolShell scanner - CVE-2025-53770 and detection information
 bardlaudian/cve-2024-37054
Proof-of-concept that poisons MLflow registered models via the REST API, embedding a malicious pickle to trigger RCE when the model is loaded.
 oscerd/cve-2026-80344
Runnable proof-of-concept reproducer for CVE-2026-80344 in Apache Camel camel-as2, demonstrating asynchronous MDN SSRF and credential disclosure with…
 oscerd/cve-2026-85243
Runnable Spring Boot and Quarkus proof-of-concept for CVE-2026-85243, demonstrating the Apache Camel camel-crypto-pgp integrity-verification…
 oscerd/cve-2026-101259
Runnable proof-of-concept reproducer for CVE-2026-101259, demonstrating error-message disclosure in Apache Camel camel-coap consumers on Spring Boot…
 oscerd/cve-2026-95664
Runnable Spring Boot and Quarkus reproducer for CVE-2026-95664, demonstrating Simple expression injection via the CamelAwsS3Key header in…
 oscerd/cve-2026-95628
Runnable proof-of-concept reproducer for CVE-2026-95628, an absolute-path validation gap in Apache Camel camel-docling, with Spring Boot and Quarkus…
 oscerd/cve-2026-95629
Runnable proof-of-concept reproducer for CVE-2026-95629, a path-traversal flaw in Apache Camel camel-docling where the output-path header reaches…
 oscerd/cve-2026-90885
Runnable proof-of-concept reproducer for CVE-2026-90885, an XXE (CWE-611) in Apache Camel camel-saxon XQuery, with Spring Boot and Quarkus builds and…
 arpsyndicate/vedas-signatures
VEDAS-Driven Autonomous Generation + Community Contributions of Suricata & Nuclei Rules for over 15k CVEs
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 albinowax/activescanplusplus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 portswigger/active-scan-plus-plus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…
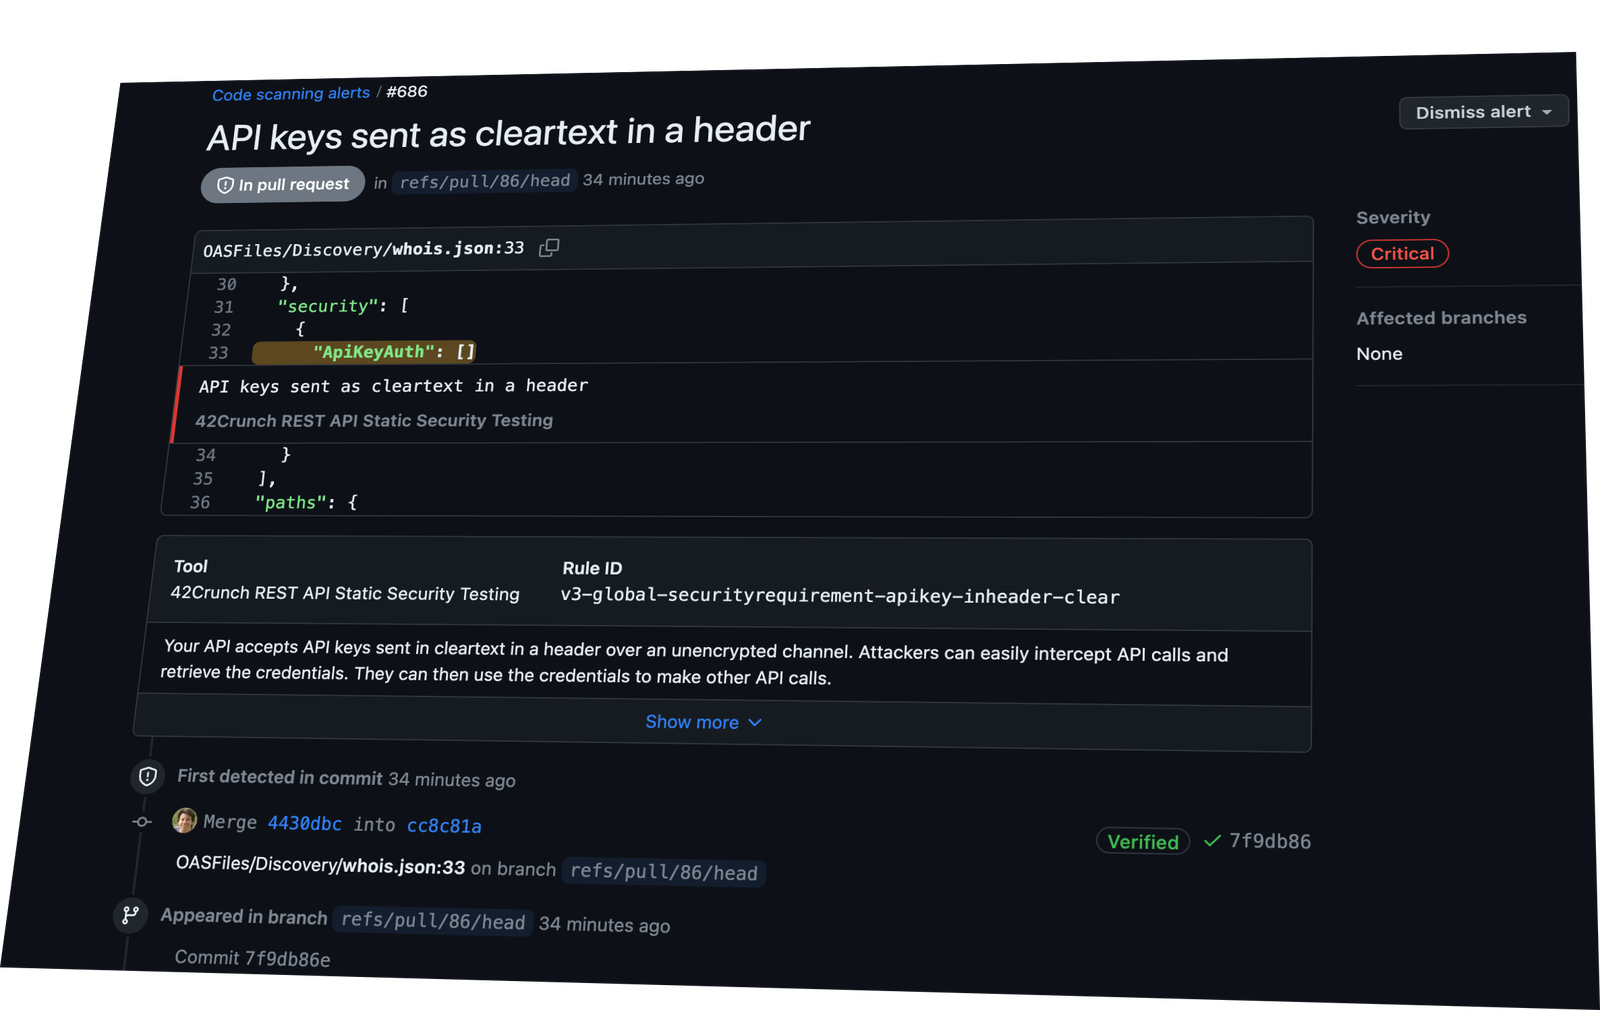 42crunch/api-security-audit-action
Automates static API security auditing of OpenAPI contracts in CI/CD, running 300+ checks for authentication, authorization, and data constraints,…
 dragonjar/burpia
Extensión de Burp Suite que incorpora detección pasiva de vulnerabilidades mediante inteligencia artificial.