
threatest
 datadog/threatest
CLI and Go framework for end-to-end testing of threat detection rules. Detonates attack techniques and verifies alerts in security platforms like…
defensive-toolspenetration-testingred-teaming
datadog/threatestCLI and Go framework for end-to-end testing of threat detection rules. Detonates attack techniques and verifies alerts in security platforms like…
 olafhartong/bamboozledr
A comprehensive ETW (Event Tracing for Windows) event generation tool designed for testing and research purposes.
 robrankin/cve-2021-44228-waf-tests
Testing WAF protection against CVE-2021-44228 Log4Shell
 shutdownrepo/dcshadow
Python alternative to Mimikatz lsadump::dcshadow
 wavestone-cdt/edrsandblast
Weaponizes vulnerable signed drivers to bypass EDR kernel callbacks, object callbacks, ETW TI provider, and userland hooks for LSASS memory dumping…
 jxy-s/herpaderping
Process Herpaderping proof of concept, tool, and technical deep dive. Process Herpaderping bypasses security products by obscuring the intentions of…
 rythmstick/amsitrigger
The Hunt for Malicious Strings
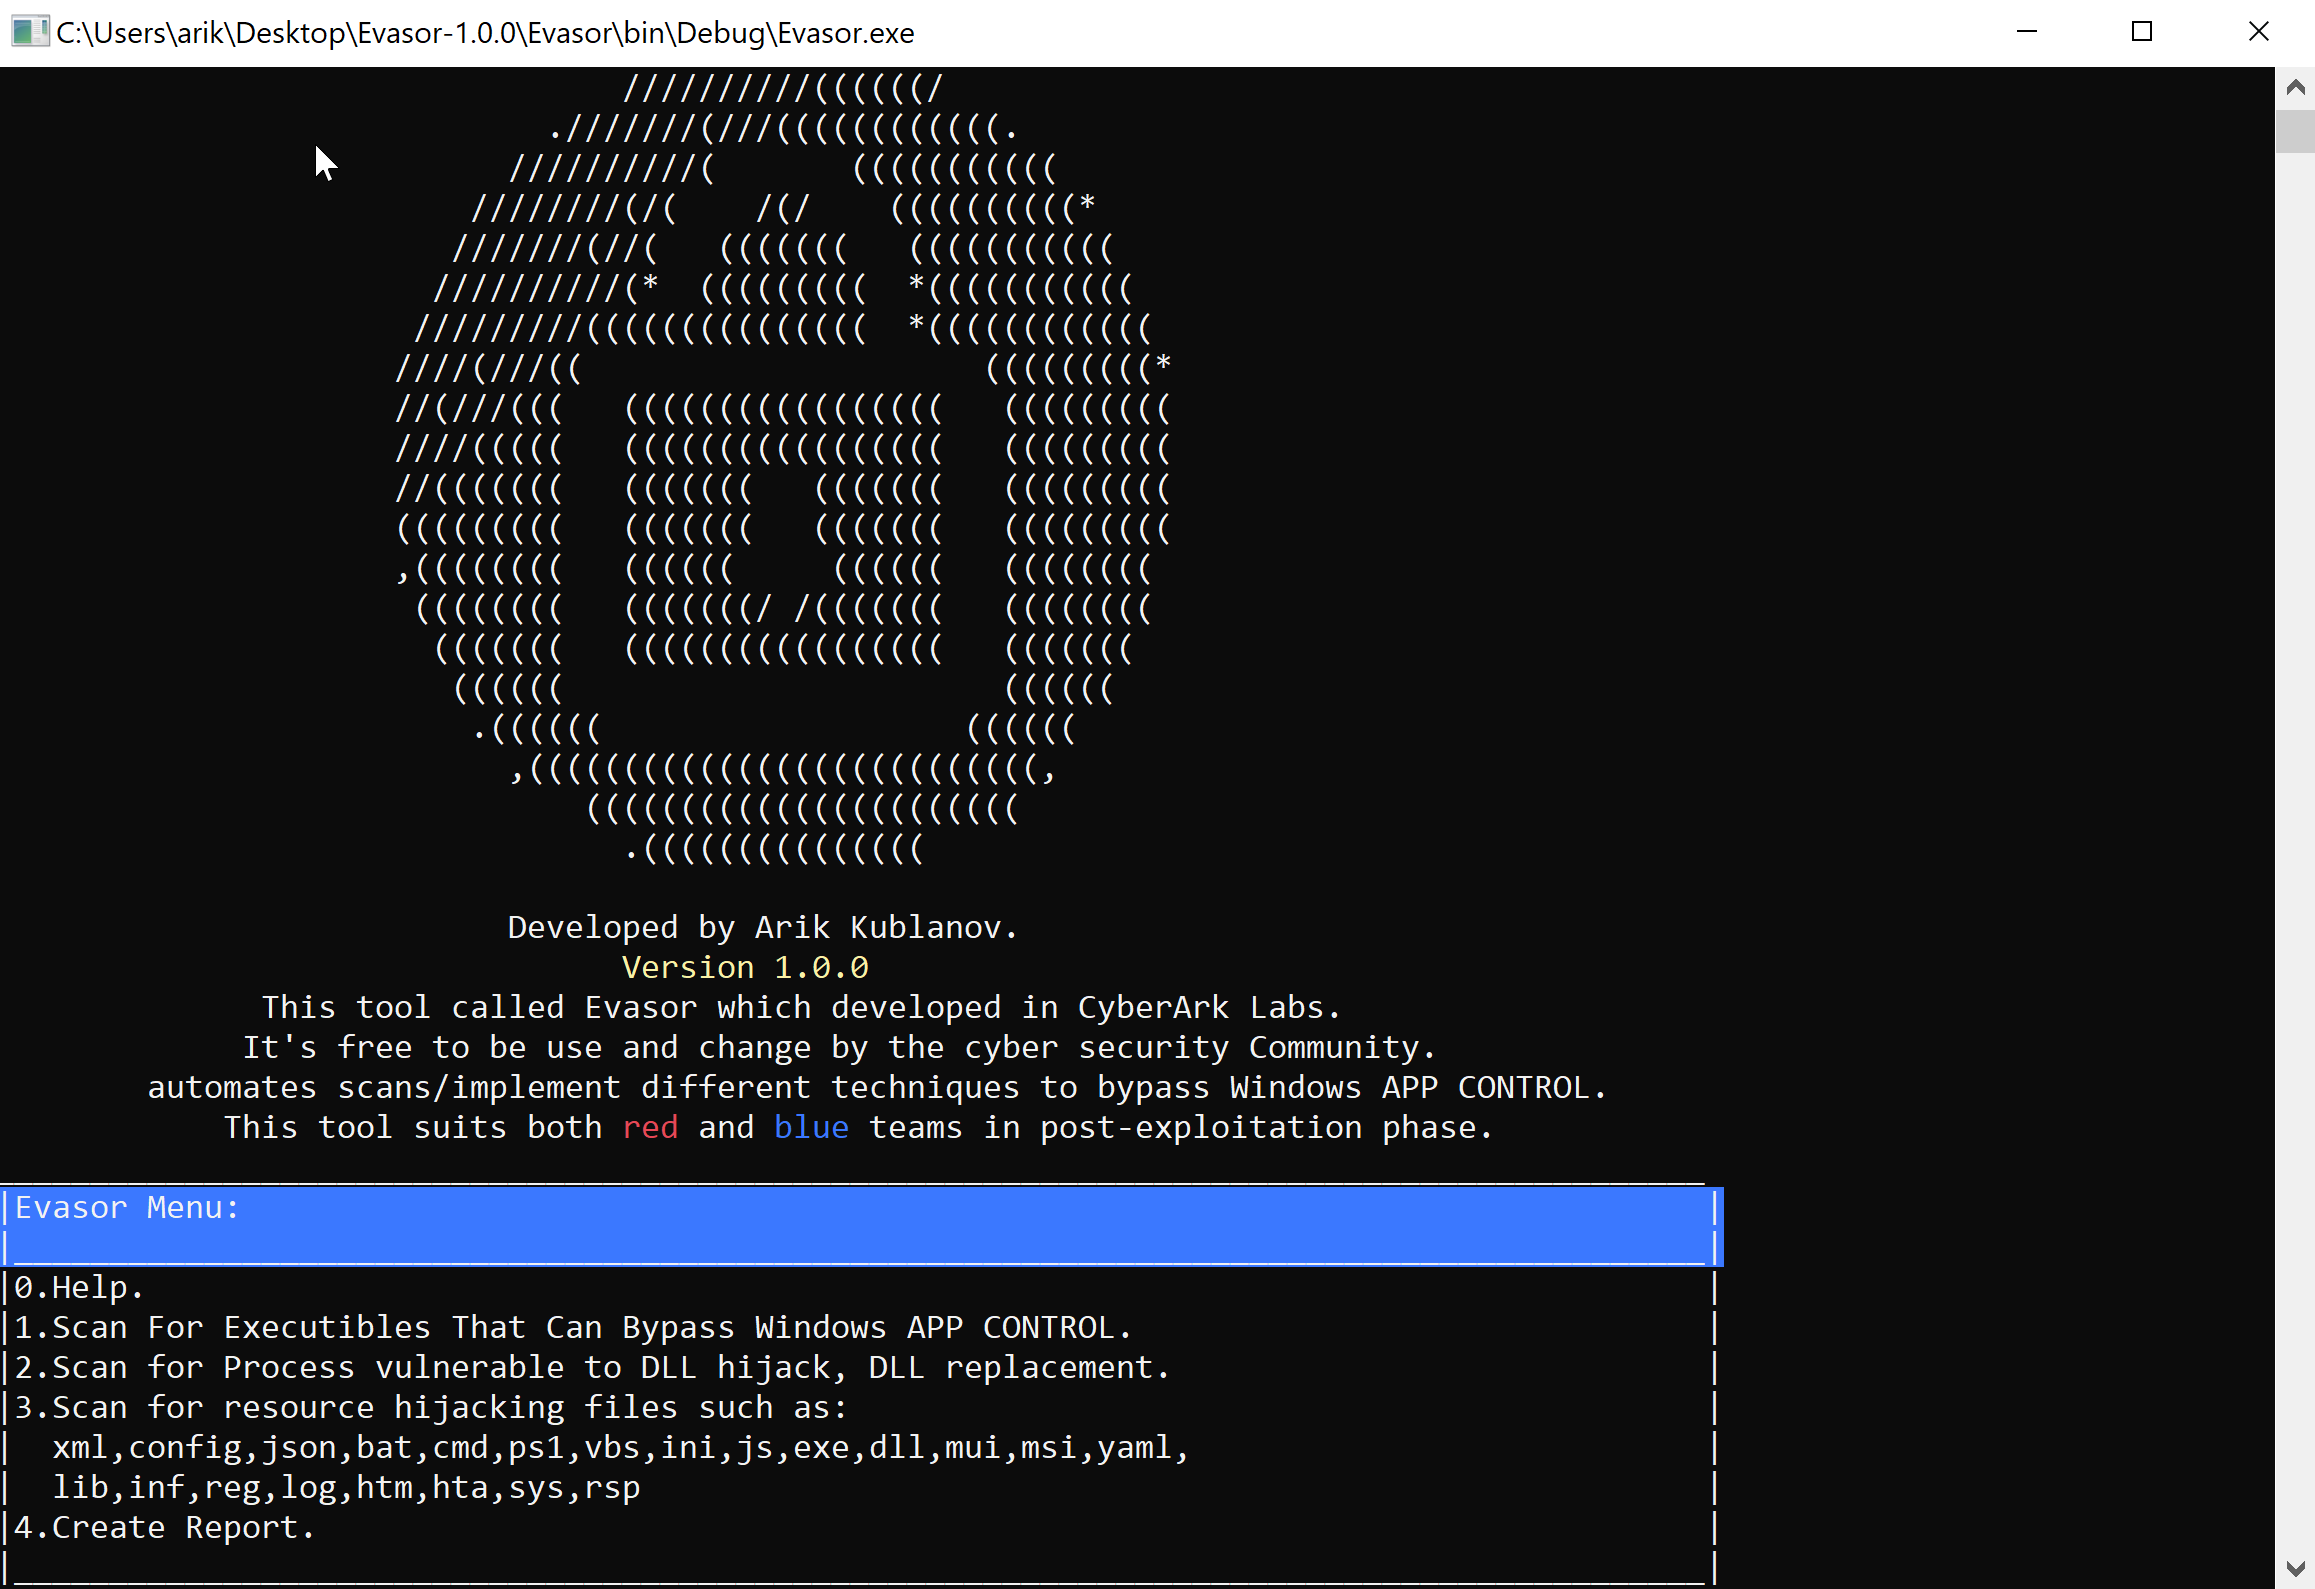 cyberark/evasor
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
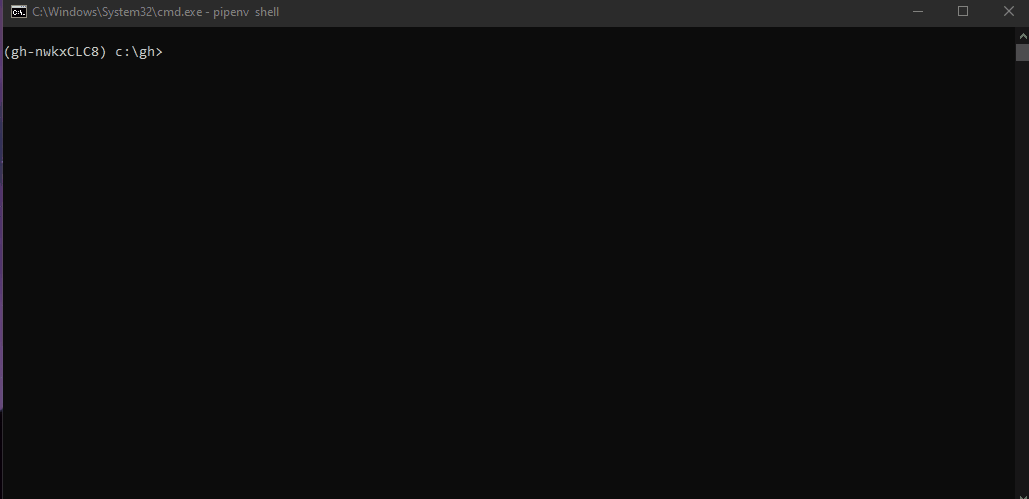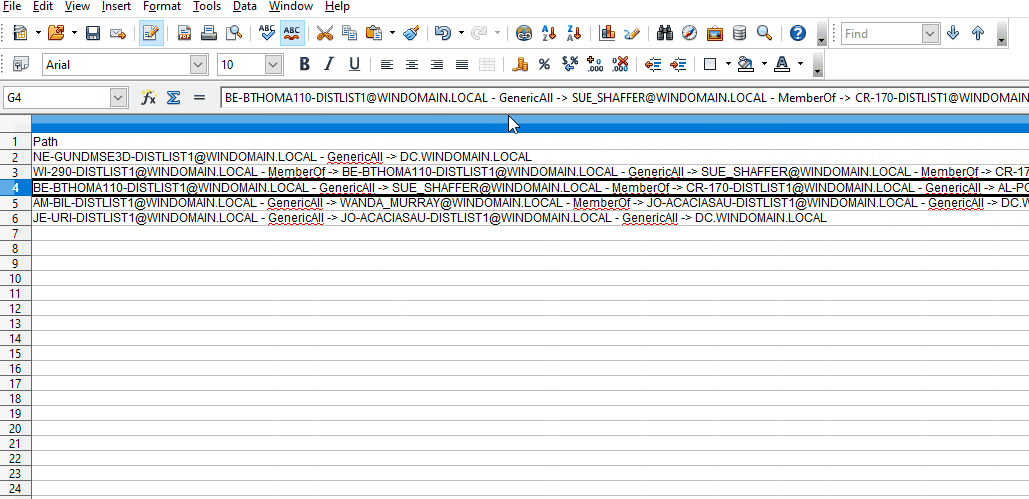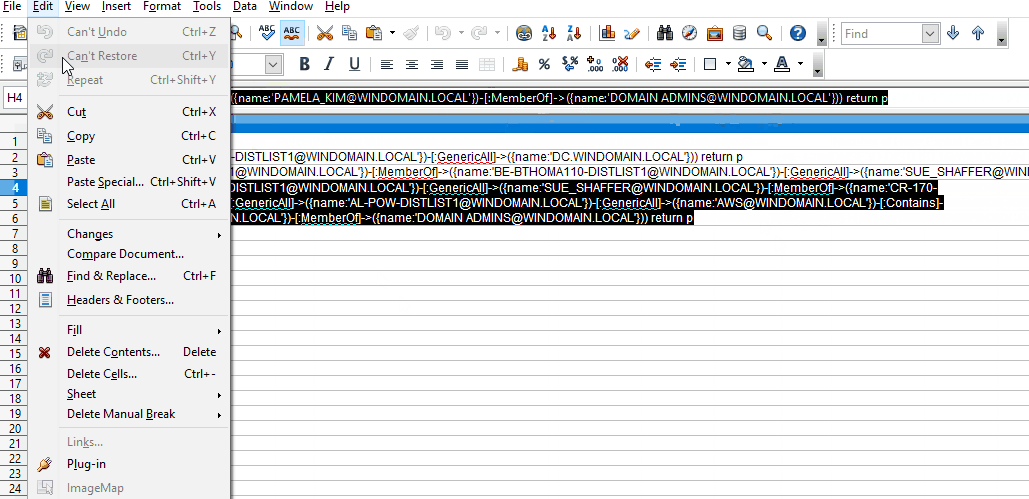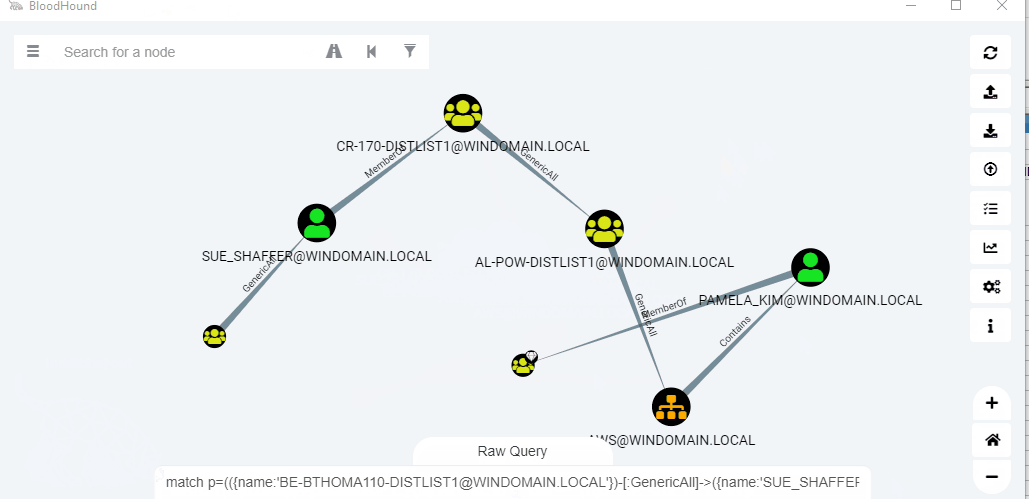 idnahacks/goodhound
Uses Sharphound, Bloodhound and Neo4j to produce an actionable list of attack paths for targeted remediation.
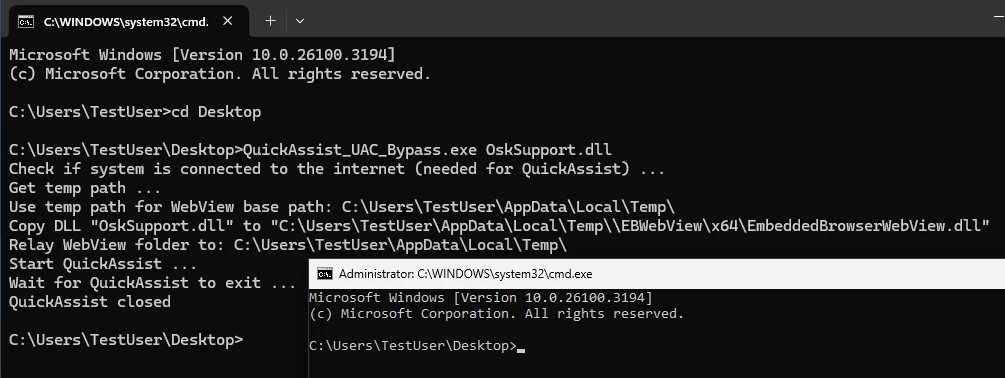 r41n3rzuf477/quickassist_uac_bypass
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…
 redcanaryco/atomictestharnesses
Public Repo for Atomic Test Harness
 magisterquis/sshhipot
High-interaction MitM SSH honeypot
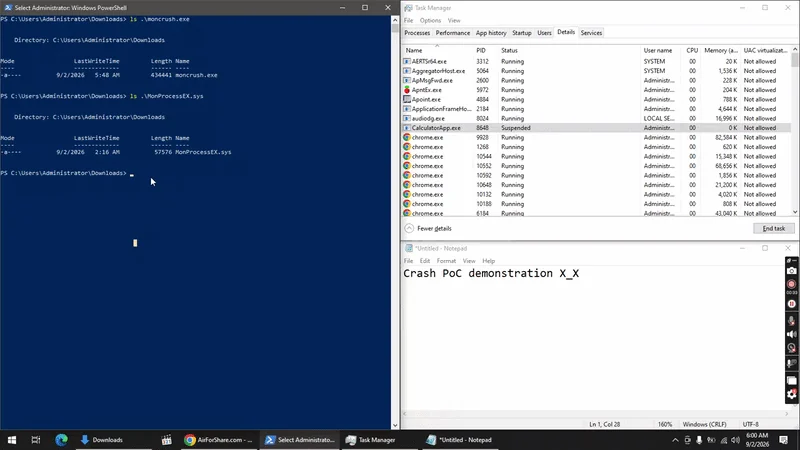 deathshotxd/0xm0ncrush
Kernel-mode process terminator using a signed BYOVD driver. Works on all Windows 10/11. No offsets, no PDB. Rust.
 hwbp/clr-unhook
Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…
 thannikudam/topazterminator
C-based tool exploiting the vulnerable wsftprm.sys kernel driver to terminate protected EDR/AV processes on Windows, including PPL processes, via…
 cedowens/macshellswift
Proof of concept MacOS post exploitation tool written in Swift. Designed as a POC for blue teams to build macOS detections. Author: Cedric Owens
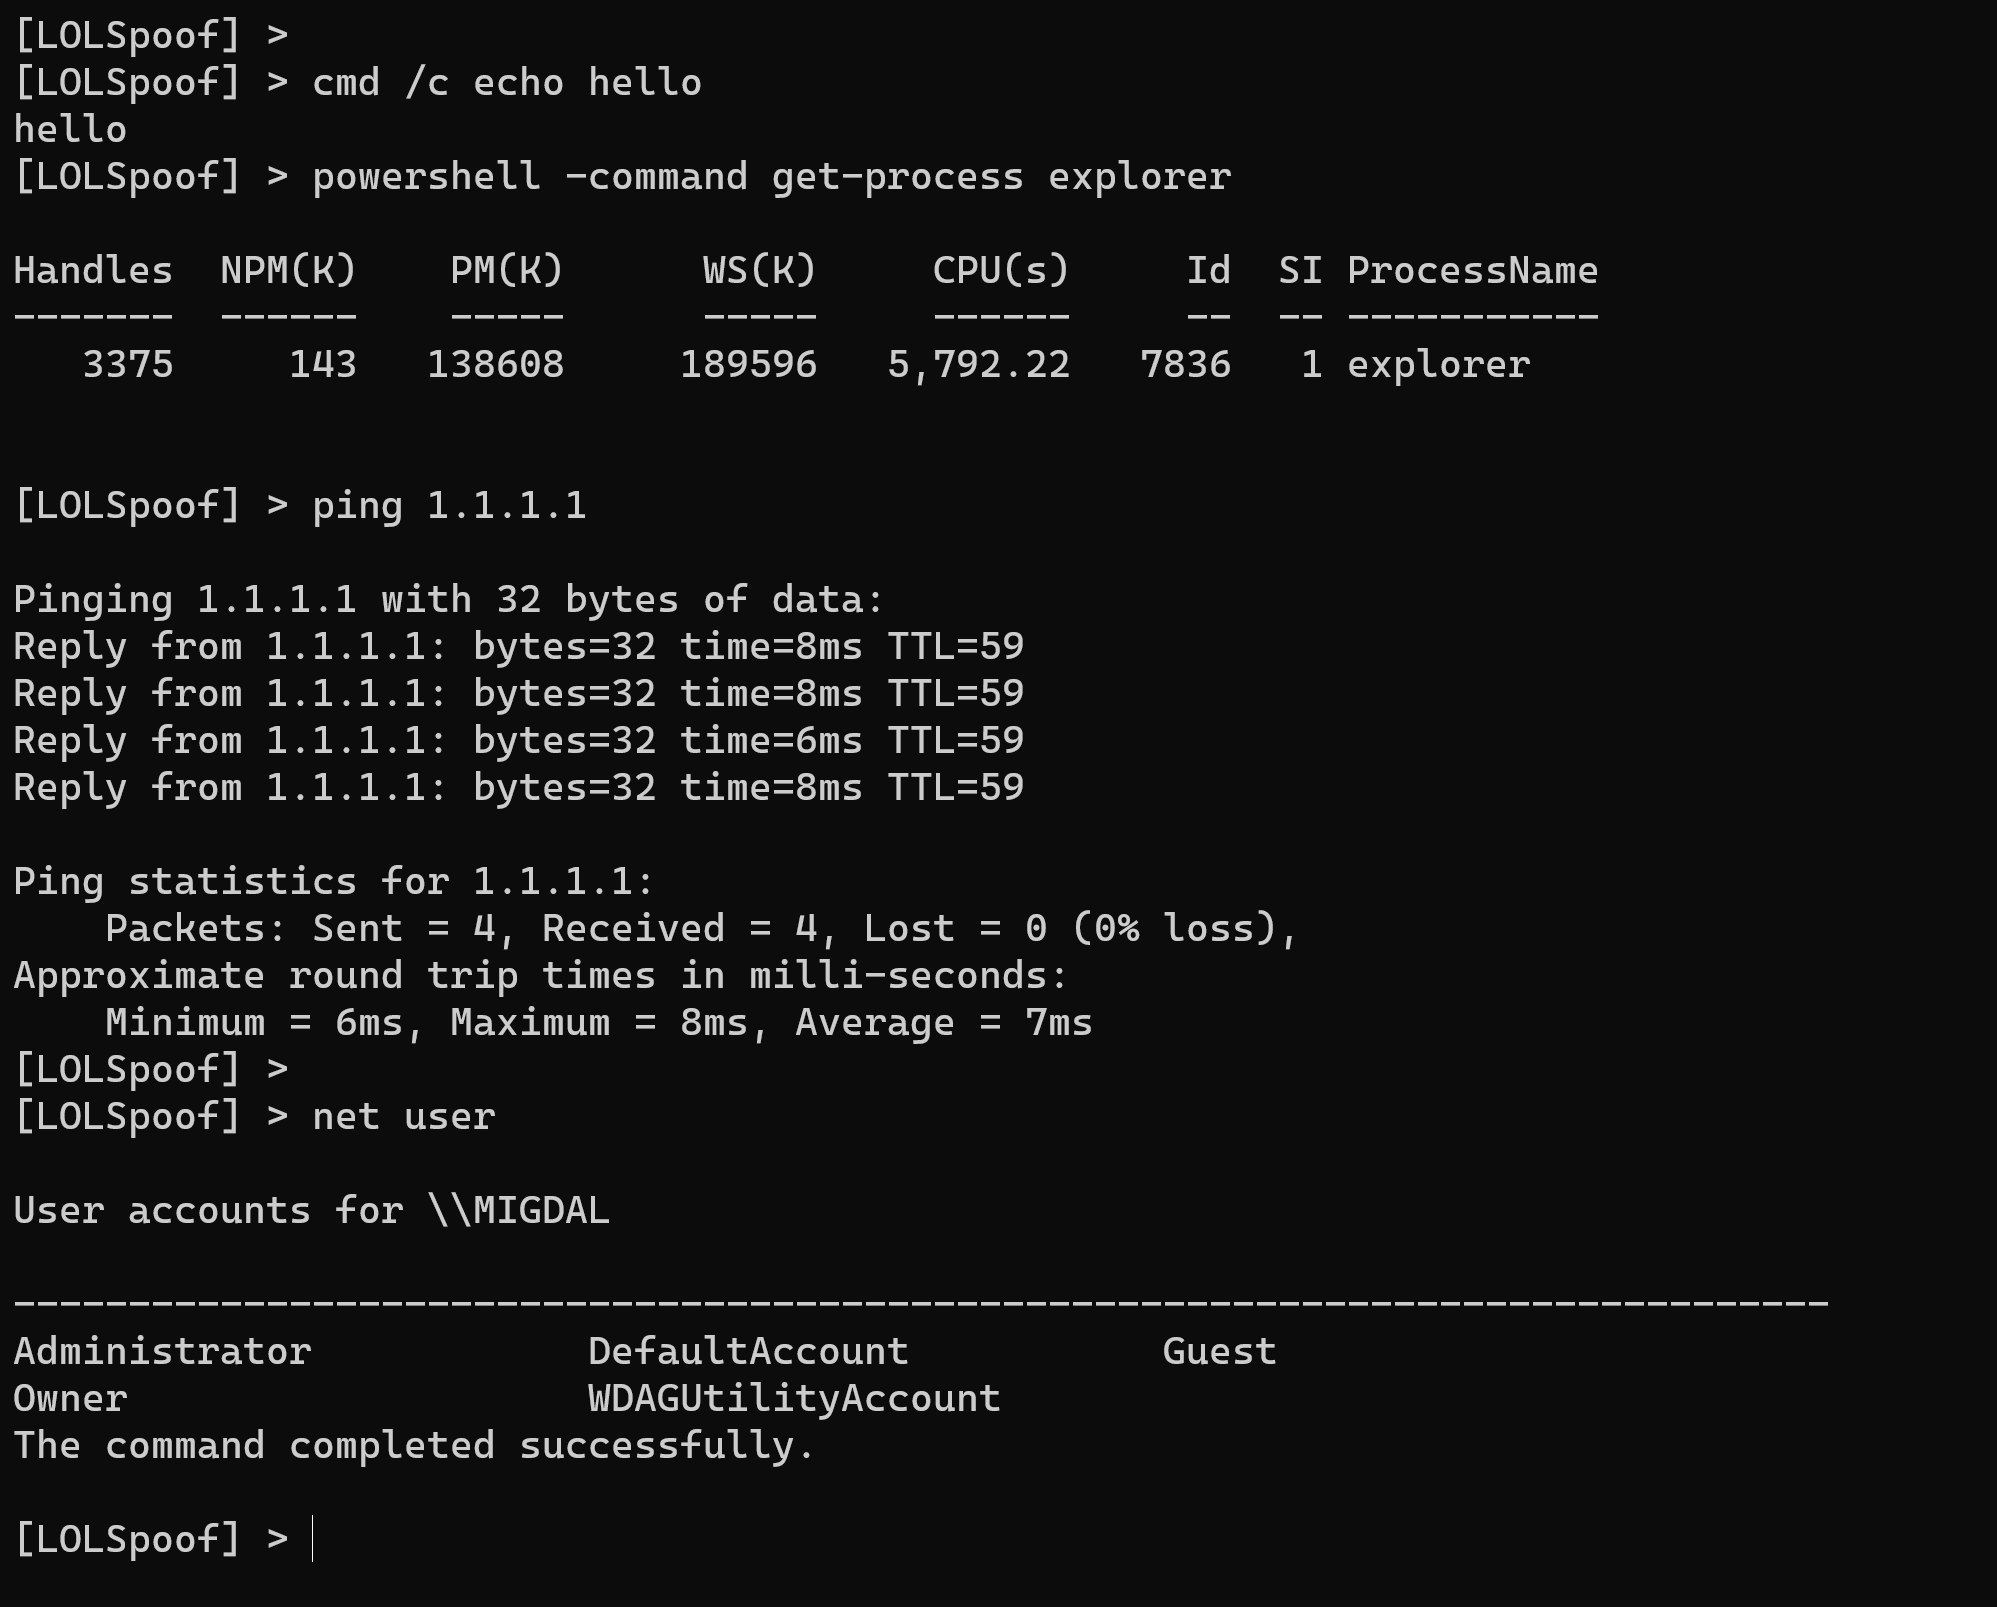 itaymigdal/lolspoof
An interactive shell to spoof some LOLBins command line
 flangvik/sharpapplocker
C# port of the Get-AppLockerPolicy PS cmdlet