
dcshadow
 shutdownrepo/dcshadow
Python alternative to Mimikatz lsadump::dcshadow
defensive-toolspenetration-testingpersistence-mechanisms+2
1611 year ago
shutdownrepo/dcshadowPython alternative to Mimikatz lsadump::dcshadow
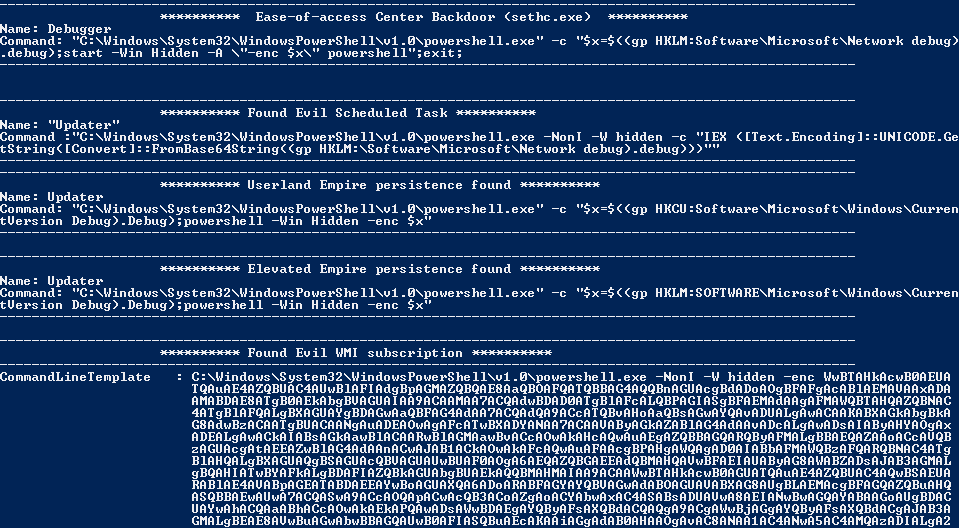 n00py/norknork
Powershell Empire Persistence finder
 lockness-ko/xz-vulnerable-honeypot
An ssh honeypot with the XZ backdoor. CVE-2024-3094
 chaitin/mimicry
Active deception tool that transparently migrates attackers from real targets to honeypots during exploitation and post-exploitation, supporting…
 last-byte/persistencesniper
Powershell module that can be used by Blue Teams, Incident Responders and System Administrators to hunt persistences implanted in Windows machines.…
 wgpsec/createhiddenaccount
A tool for creating hidden accounts using the registry || 一个使用注册表创建隐藏帐户的工具
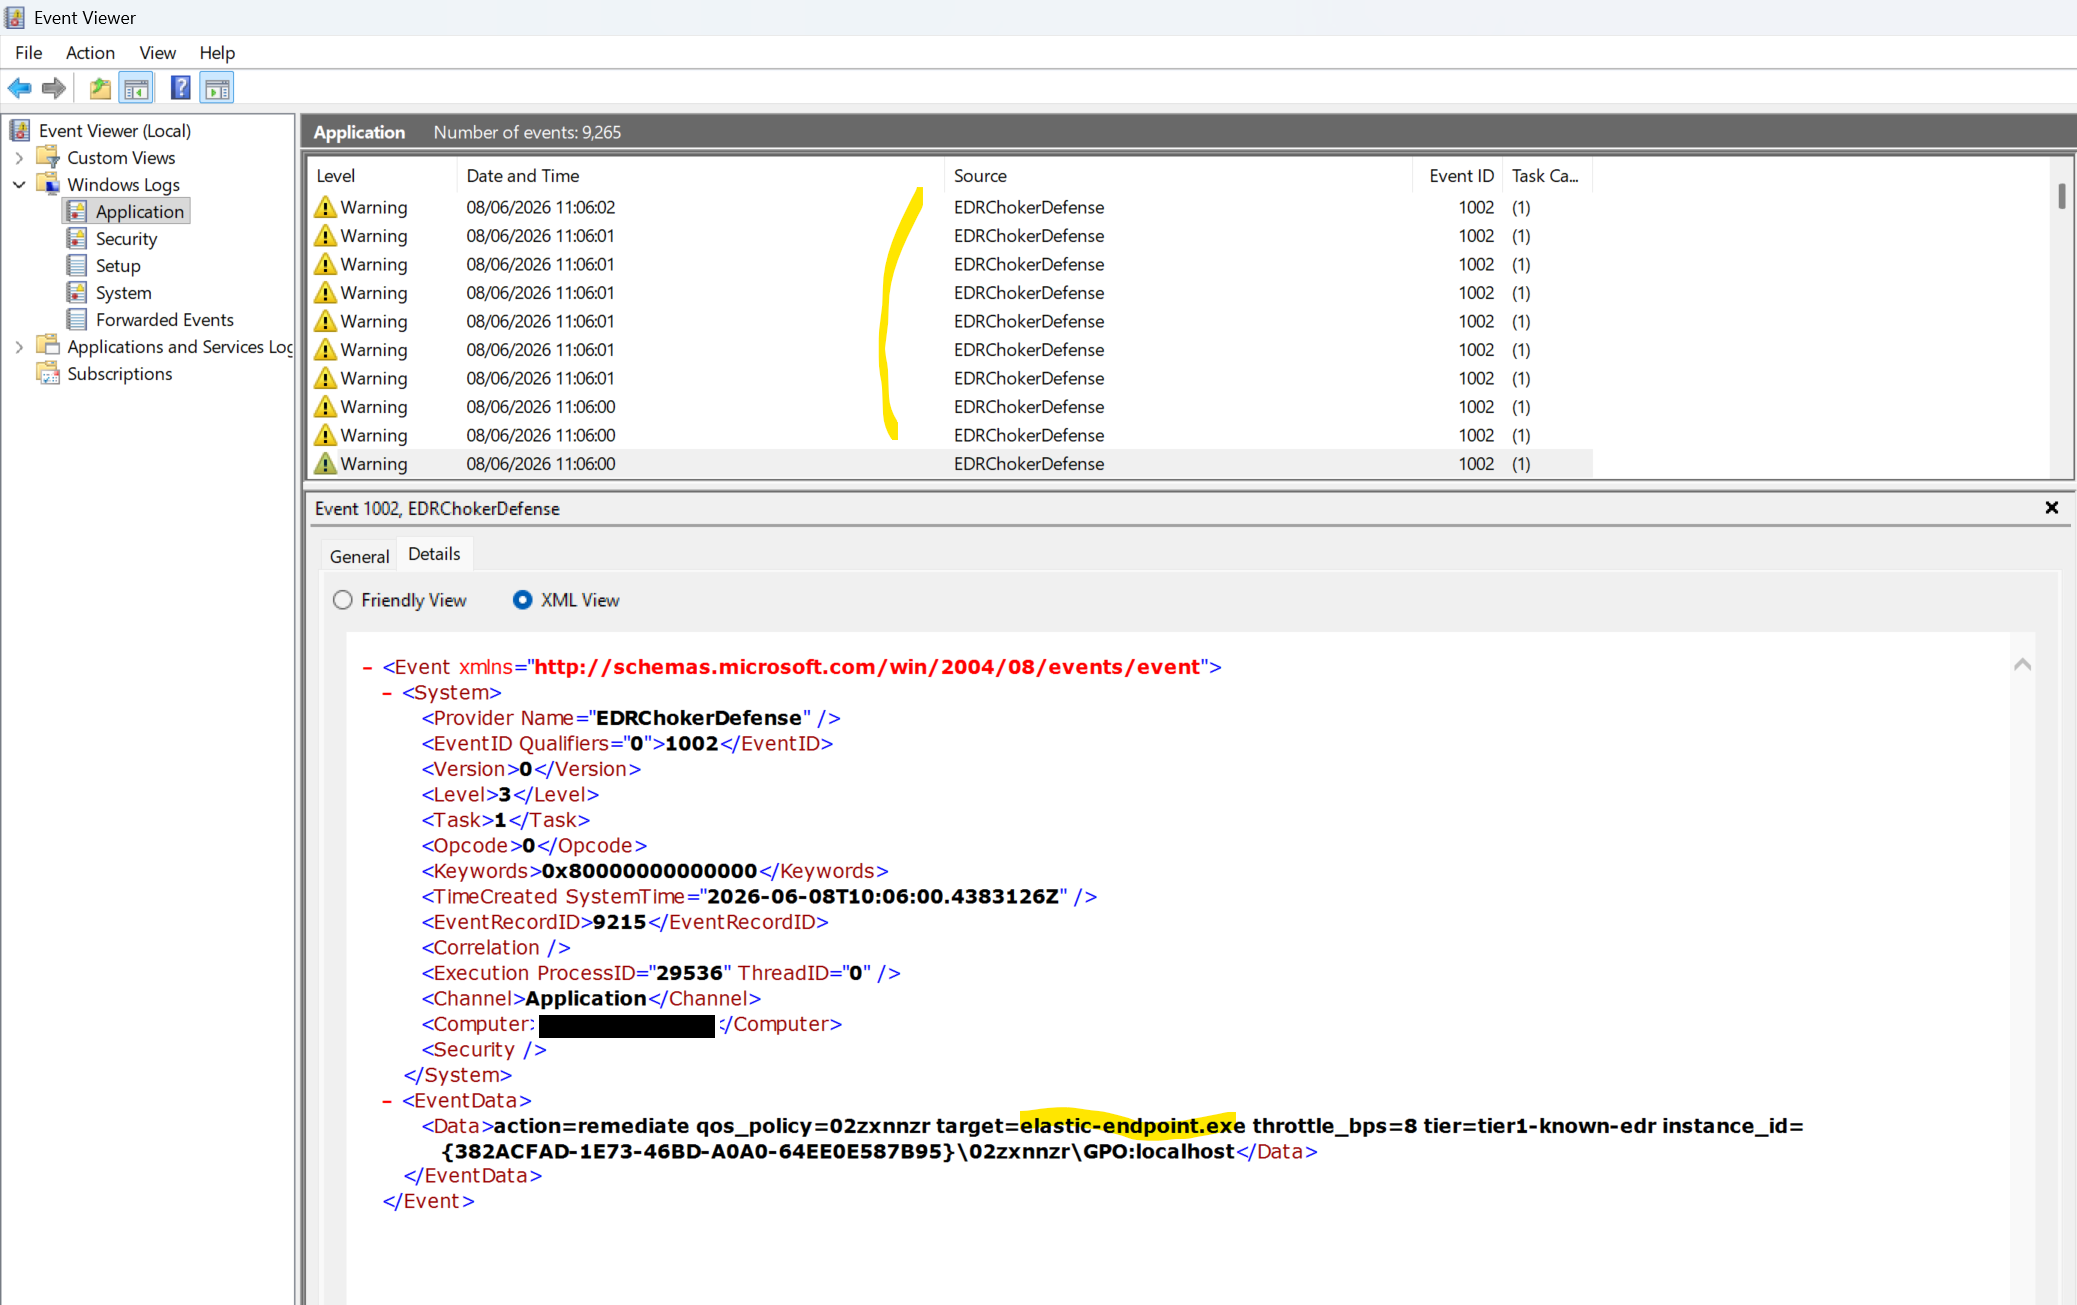 sbousseaden/edrunchoker
EDRUnChoker - fileless WMI defense that removes EDRChoker QoS throttling policies
 gmh5225/dse-patcher
Windows tool that disables Driver Signature Enforcement by patching kernel variables, allowing unsigned drivers to load for testing and research.
 gmh5225/driver-hide-file
choose and hide windows files/path from kernel space using this driver

 mr-r3b00t/cve-2021-44228
PowerShell-based backdoor detection tool for VMware Horizon connection servers, targeting CVE-2021-44228. Includes canary with optional submission…
 alex66366/odpure
Black-box input-stage purification defense that neutralizes backdoor attacks on object detectors via corruption, diffusion reconstruction, and DBSCAN…
 taisa456/network-security-snort
Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…
 corelight/redxor
Detection of Linux Malware C2 RedXOR - demonstration