
Zirconium
 byinarie/zirconium
Tool to search for IOCs related to HAFNIUM: CVE-2021-26855 CVE-2021-26857 CVE-2021-26858 CVE-2021-27065
defensive-toolsdigital-forensicsincident-response+3
2
byinarie/zirconiumTool to search for IOCs related to HAFNIUM: CVE-2021-26855 CVE-2021-26857 CVE-2021-26858 CVE-2021-27065
 cropnet/ni8mare
Comprehensive vulnerability detection tool for n8n workflow automation instances. Detects the critical CVE-2026-21858 vulnerability (CVSS 10.0)…
 shizuku198411/cve-2026-0300
Non-destructive exposure survey tool for assessing PAN-OS User-ID Authentication Portal surfaces related to CVE-2026-0300, performing safe HTTP(S)…
 sreejaputhan/cpanel-control-plane-exposure-check
Defensive exposure assessment tool for identifying externally accessible cPanel, WHM, and Webmail management interfaces related to CVE-2026-41940.
 ilhamrzr/rar-anomaly-inspector
Defensive PowerShell tool for static inspection of RAR archives and detection of CVE-2025-8088 path traversal anomalies.
 nrnw/cve-2026-24061-gnu-inetutils-telnet-detector
A passive detection tool for identifying potential exposure to CVE-2026-24061 in GNU inetutils telnet installations
 laachy/cve-2024-39930-ptrace-detection-mitigation
Rust-based tool to detect and mitigate CVE-2024-39930 ptrace exploitation, providing binary-level analysis and defensive countermeasures for Linux…
 ernestak/cve-2022-30190
Official guidance and workarounds for CVE-2022-30190, a remote code execution vulnerability in the Microsoft Support Diagnostic Tool (MSDT)…
 ml-k-eng/cve-2023-38831-exploit-and-detection
This repository has both an attack detection tool and a Proof-of-Concept (PoC) Python script for the WinRAR CVE-2023-38831 vulnerability.
 runzeroinc/sshamble
Research tool that scans SSH services for authentication bypasses, timing leaks, weak keys, and post-session exposures, with JSON output and analysis.
 spinfosecurity/rail-ot-protector
Rail-OT-Protector (ROP) — free, open-source cybersecurity scanning tool for rail and transit OT/SCADA networks. PowerShell + Bash scanners for…
 ull0a/bdapiutil-bydov
C++ Windows research tool for studying the BdApiUtil64.sys vulnerable driver and CVE-2024-51324
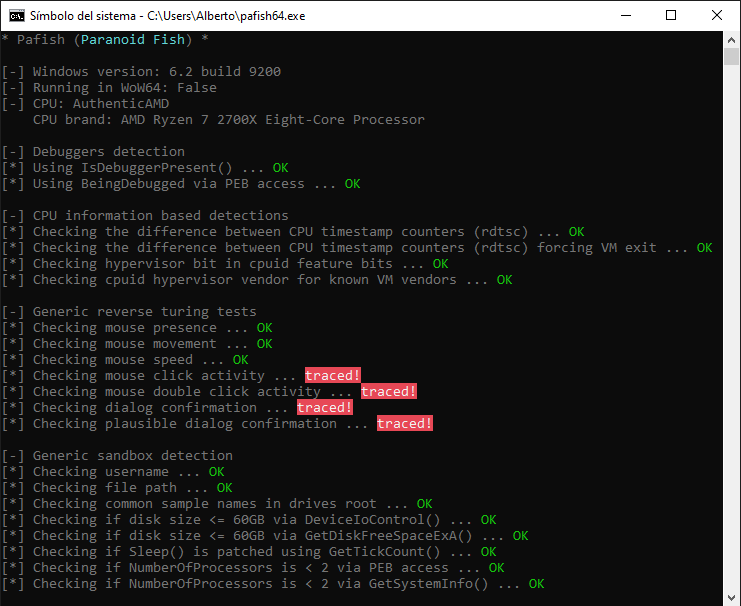 a0rtega/pafish
Pafish is a testing tool that uses different techniques to detect virtual machines and malware analysis environments in the same way that malware…
 gmh5225/dse-patcher
Windows tool that disables Driver Signature Enforcement by patching kernel variables, allowing unsigned drivers to load for testing and research.
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 gamingwithevets/msdt-disable
MSDT protocol disabler (CVE-2022-30190 patch tool)
 wavestone-cdt/edrsandblast
Weaponizes vulnerable signed drivers to bypass EDR kernel callbacks, object callbacks, ETW TI provider, and userland hooks for LSASS memory dumping…
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.