
Z-Jail
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
binary-analysiscontainer-securityctf+7
74
division-36/z-jailA lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
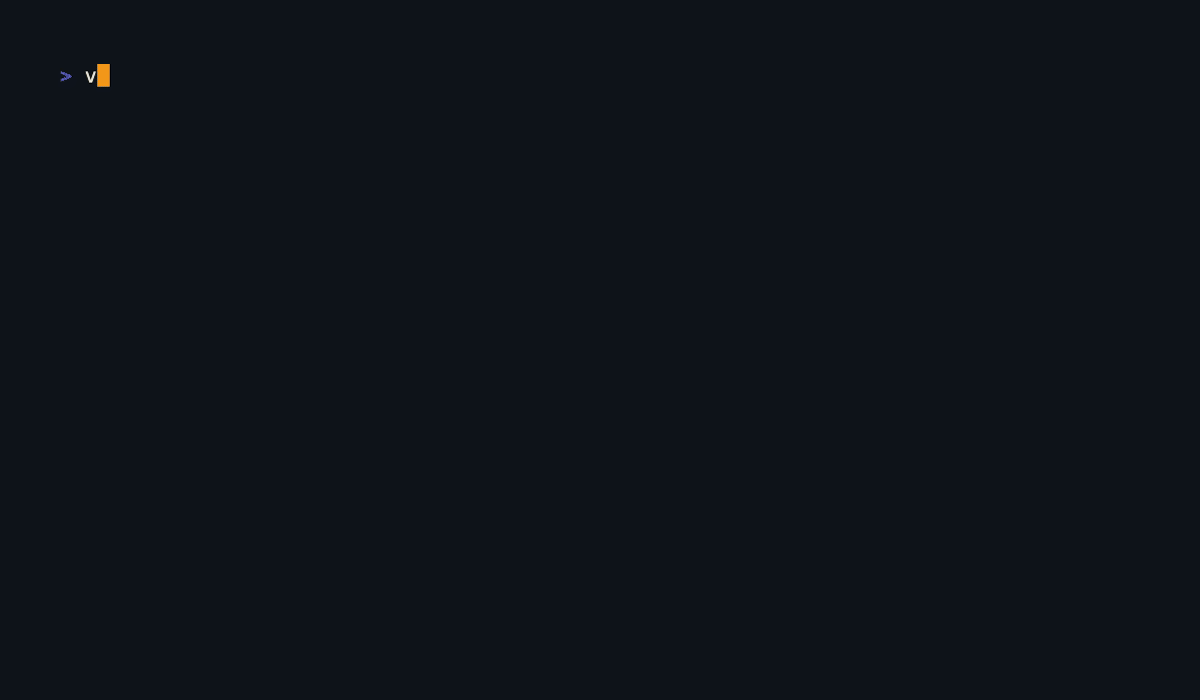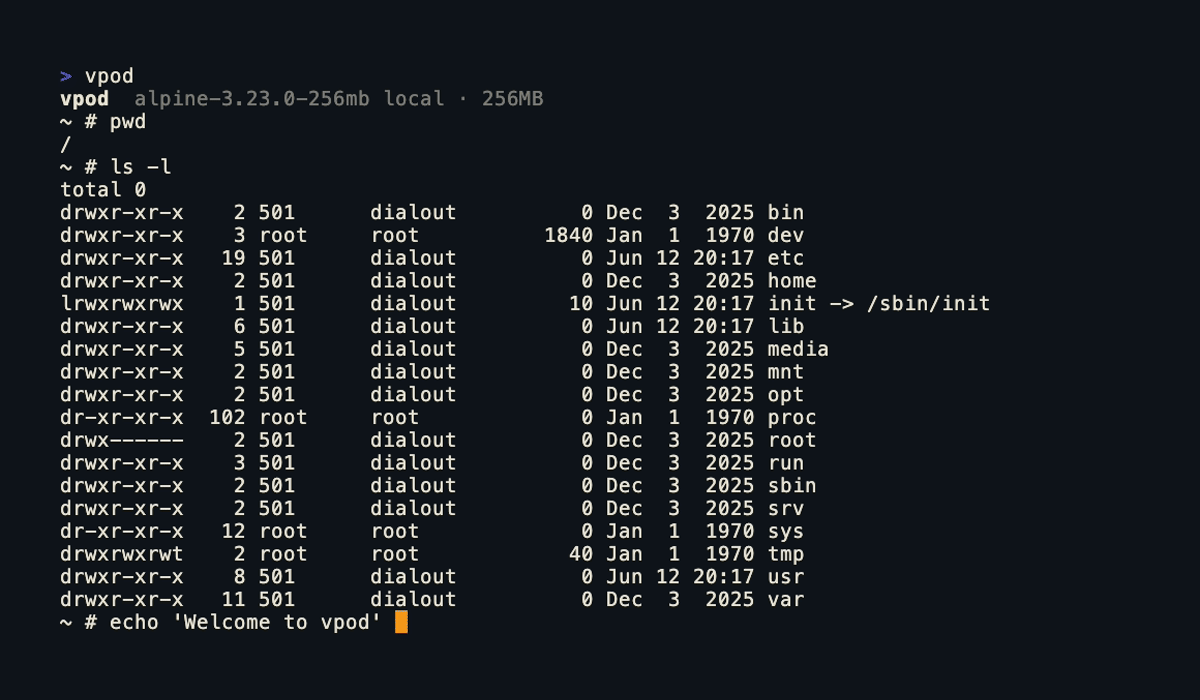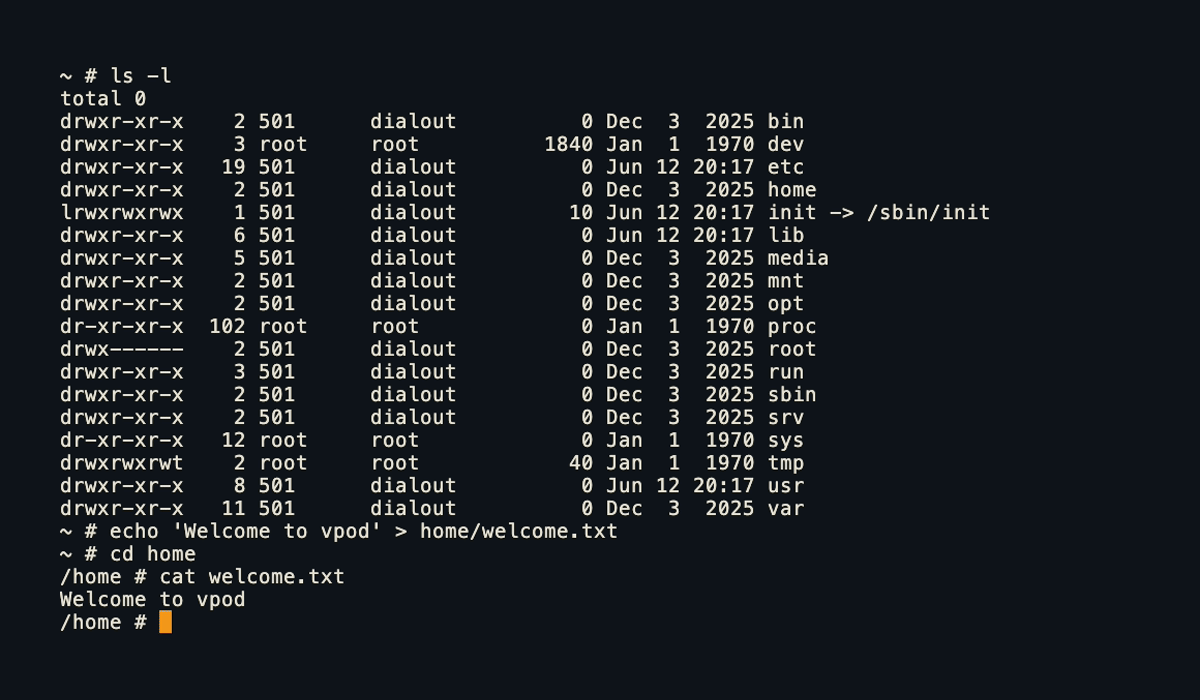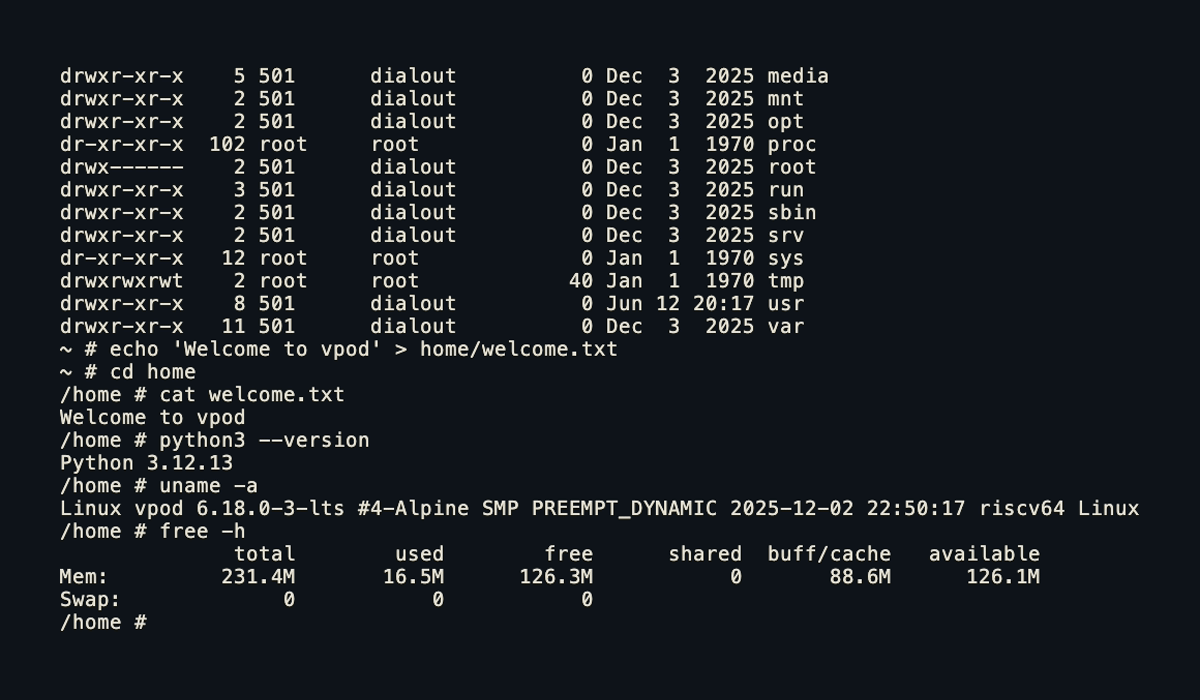 capsulerun/vpod
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
 airbus-cert/dirtypipe-ebpf_detection
An eBPF detection program for CVE-2022-0847
 cozystack/copy-fail-blocker
BPF-LSM mitigation for CVE-2026-31431 (Copy Fail) — denies AF_ALG socket creation cluster-wide
 xtuc/airgap
Security for the modern age of AI: defend against bad AI agents and malicious npm packages
 mc493/linux-kernel-zero-day-mitigation-zero-downtime-kernel-defense-
Zero-downtime Linux kernel zero-day defense case study. For the automated CLI and dual-witness notary framework, see mc493/kshield.
 douglasmun/pagecache-lpe-containment-kit
Educational, defensive kit for two Linux page-cache-corruption LPEs (DirtyClone CVE-2026-43503, pedit COW CVE-2026-46331): hardening, detection,…
 mrunalp/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) - zero-reboot remediation for OpenShift 4
 ahndrewalters/projectsecurity-homelab
Hands-on homelab simulating the Log4Shell (CVE-2021-44228) vulnerability. Deploy Docker containers to build a vulnerable target and attacker machine,…
 detect-defenselab/cve-2026-31431-detection-defense
Research and detection guidance for CVE-2026-31431, an io_uring-based bypass of syscall monitoring. Provides detection rules for Tetragon, Falco, and…
 gmh5225/llm-guard-service
A service to provide protection against prompt injection, jailbreak attacks, and harmful content when interacting with AI services..
 snyk/leaky-vessels-dynamic-detector
eBPF-based runtime detector for container breakout vulnerabilities in runc and Docker, monitoring syscalls and Docker daemon calls to detect…
 nsrg-fmlorg/kpatch-alma-cve-2026-99999
kpatch livepatch build for CVE-2026-99999 on AlmaLinux 8/9 GA kernels
 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.
 cybereason-public/owlsm
Sigma Rules Engine inside the Linux Kernel using eBPF. Focusing on prevention capabilities
 shambhavim18/cve-2019-15107-lab
Docker-based lab demonstrating CVE-2019-15107, the Webmin unauthenticated RCE, covering deployment, exploitation, detection, and remediation.
 spanwich/sel4-ics-gateway-demo
Defensive security demo: seL4 microkernel gateway protecting vulnerable ICS from CVE-2019-14462
 kubearmor/kubearmor
Runtime Security Enforcement System. Workload hardening/sandboxing and implementing least-permissive policies made easy leveraging LSMs (LSM-BPF,…