

libprocesshider
 gianlucaborello/libprocesshider
LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
defensive-toolsinformation-gatheringmalware-analysis+4
1.1k
gianlucaborello/libprocesshiderLD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
 tylous/zipexec
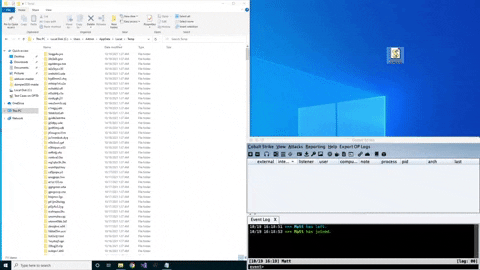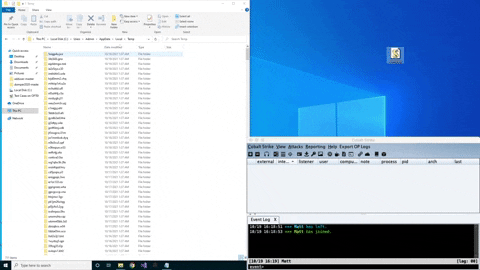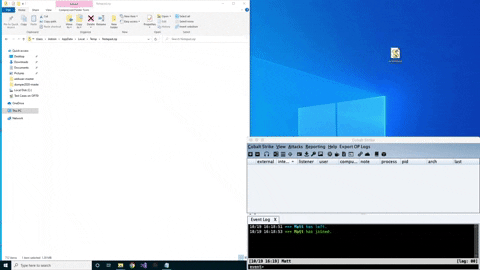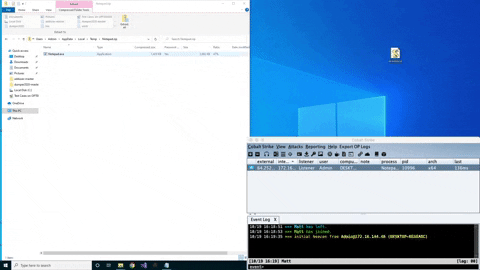
A unique technique to execute binaries from a password protected zip
 volexity/threat-intel
Signatures and IoCs from public Volexity blog posts.
 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
 mohuihui/antispy
AntiSpy is a free but powerful anti virus and rootkits toolkit.It offers you the ability with the highest privileges that can detect,analyze and…
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
 cyberdefenders/detectionlabelk
DetectionLabELK is a fork from DetectionLab with ELK stack instead of Splunk.
 tyeurada/edrevasionworkshop
Workshop materials for “Step-by-Step Malware Development: Evading EDR from Loaders to the Kernel” presented at DEF CON 34 and BSidesLV 2026. Covers…
 malwaretech/edr-preloader
An EDR bypass that prevents EDRs from hooking or loading DLLs into our process by hijacking the AppVerifier layer
 cryptolok/ghostinthenet
Ultimate Network Stealther that makes Linux a Ghost In The Net and protects from MITM/DOS/scan
 d4rksystem/vmwarecloak
A PowerShell script that attempts to help malware analysts hide their VMware Windows VM's from malware that may be trying to evade analysis.
 d4rksystem/vboxcloak
A PowerShell script that attempts to help malware analysts hide their Windows VirtualBox Windows VM's from malware that may be trying to evade…
 corretto/hotpatch-for-apache-log4j2
An agent to hotpatch the log4j RCE from CVE-2021-44228.
 robertdavidgraham/isowall
This is a mini-firewall that completely isolates a target device from the local network.
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
 andrewmichaelsmith/bluepot
Java-based Bluetooth honeypot that captures and stores malware from BlueBugging and BlueSnarfing attacks, with a GUI for monitoring and log analysis.
 the-dfir-report/sigma-rules
Rules generated from our investigations.
 eclecticiq/opentaxii
TAXII server implementation in Python from EclecticIQ