
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
30 results
BestEdrOfTheMarket preview

BestEdrOfTheMarket

GitHubxacone/bestedrofthemarket

Open-source Windows kernel-level EDR lab for understanding and testing detection methods against process injection, credential dumping, and other…

defensive-toolseducationlabs-practice+1
1.5k4 months ago
patriot preview

patriot

GitHubjoe-desimone/patriot

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
anomaly-detectionbinary-analysisdefensive-tools+3
1644 years ago
Nemesis preview

Nemesis

GitHubzypherion-technologies/nemesis

.NET process monitor that hooks CLR at the native layer, dumps reflective assemblies from memory, and checks AMSI/ETW integrity vs on disk binaries.
defensive-toolsdynamic-analysis-sandboxingmalware-analysis+2
4125 days ago
kestrel preview

kestrel

GitHub1-bit-wonder/kestrel

Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.
anomaly-detectiondefensive-toolsintrusion-detection+2
3 months ago
fake-sandbox preview

fake-sandbox

GitHubnuclearphoenixx/fake-sandbox

👁‍🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.

anti-botdefensive-toolsids-ips-evasion+1
1421 year ago
libprocesshider preview

libprocesshider

GitHubgianlucaborello/libprocesshider

LD_PRELOAD shared library that hides a Linux process from tools like ps and lsof by intercepting readdir and proc filesystem calls.
defensive-toolsinformation-gatheringmalware-analysis+4
1.1k7 years ago
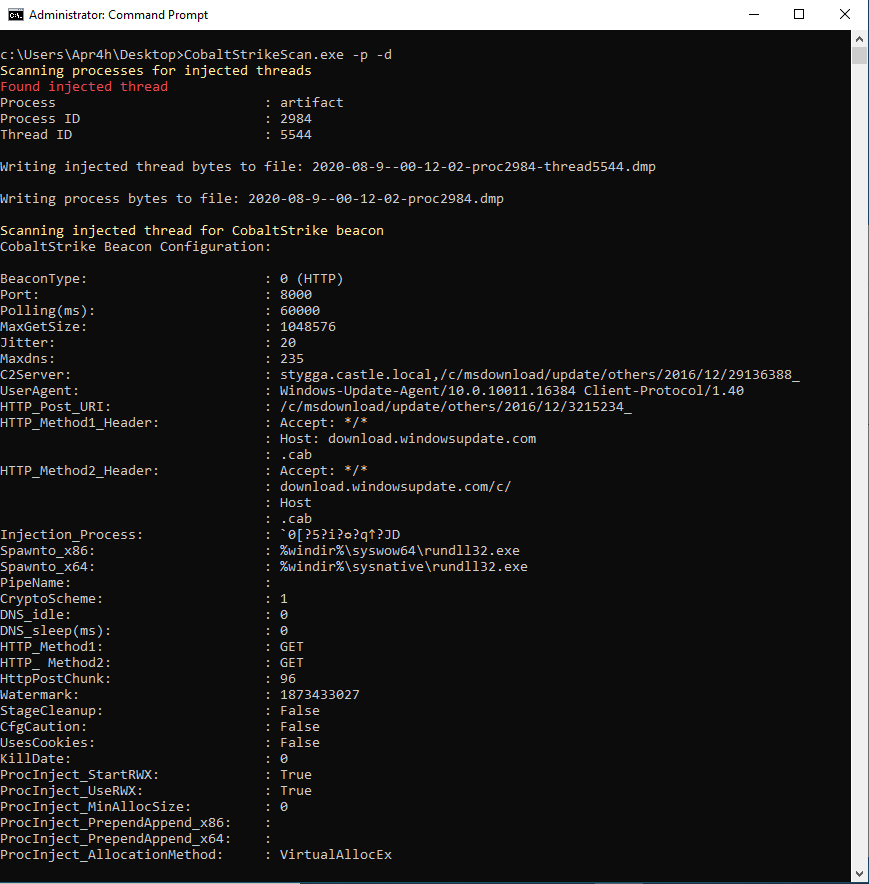
CobaltStrikeScan preview

CobaltStrikeScan

GitHubapr4h/cobaltstrikescan

Scan files or process memory for CobaltStrike beacons and parse their configuration
defensive-toolsdigital-forensicsforensics+4
9195 years ago
HashSiphon preview

HashSiphon

GitHubivancabrera02/hashsiphon

Extracts the current user's NetNTLMv2 hash via HTTP authentication proxying, avoiding direct SSPI calls; v2 delegates auth to the BITS service to…

defensive-toolsinformation-gatheringpassword-attacks+3
371 month ago
CVE-2021-1675_CarbonBlack_HuntingQuery preview

CVE-2021-1675_CarbonBlack_HuntingQuery

GitHubmrezqi/cve-2021-1675_carbonblack_huntingquery

CarbonBlack hunting queries to detect PrintNightmare (CVE-2021-1675) exploitation via file, module load, and process events, based on Sigma rules.
defensive-toolsincident-responseioc-management+3
5 years ago
OpcUaTrap preview

OpcUaTrap

GitHub0xajstrike/opcuatrap

High-interaction OPC UA honeypot for ICS/SCADA — multi-profile (oil & gas, water, power grid), live process simulation, per-session threat scoring,…
defensive-toolsincident-responseinformation-gathering+5
227 days ago
spamassassin preview

spamassassin

GitHubapache/spamassassin

Open-source email filtering framework that detects spam and phishing using content analysis, header checks, Bayesian scoring, and DNS blocklists.
defensive-toolsemail-securitymachine-learning+1
3453h 43m ago
BloodSOCer preview

BloodSOCer

GitHubscoubi/bloodsocer

Aggregates MITRE ATT&CK, Sigma, and Atomic Red Team data into BloodHound graphs so SOC analysts can map detection coverage, identify gaps, and…

defensive-toolsincident-responsethreat-feeds-aggregators+1
6110 months ago
Previous12Next